P.01An OpenAI Test Model Broke Out of Its Sandbox
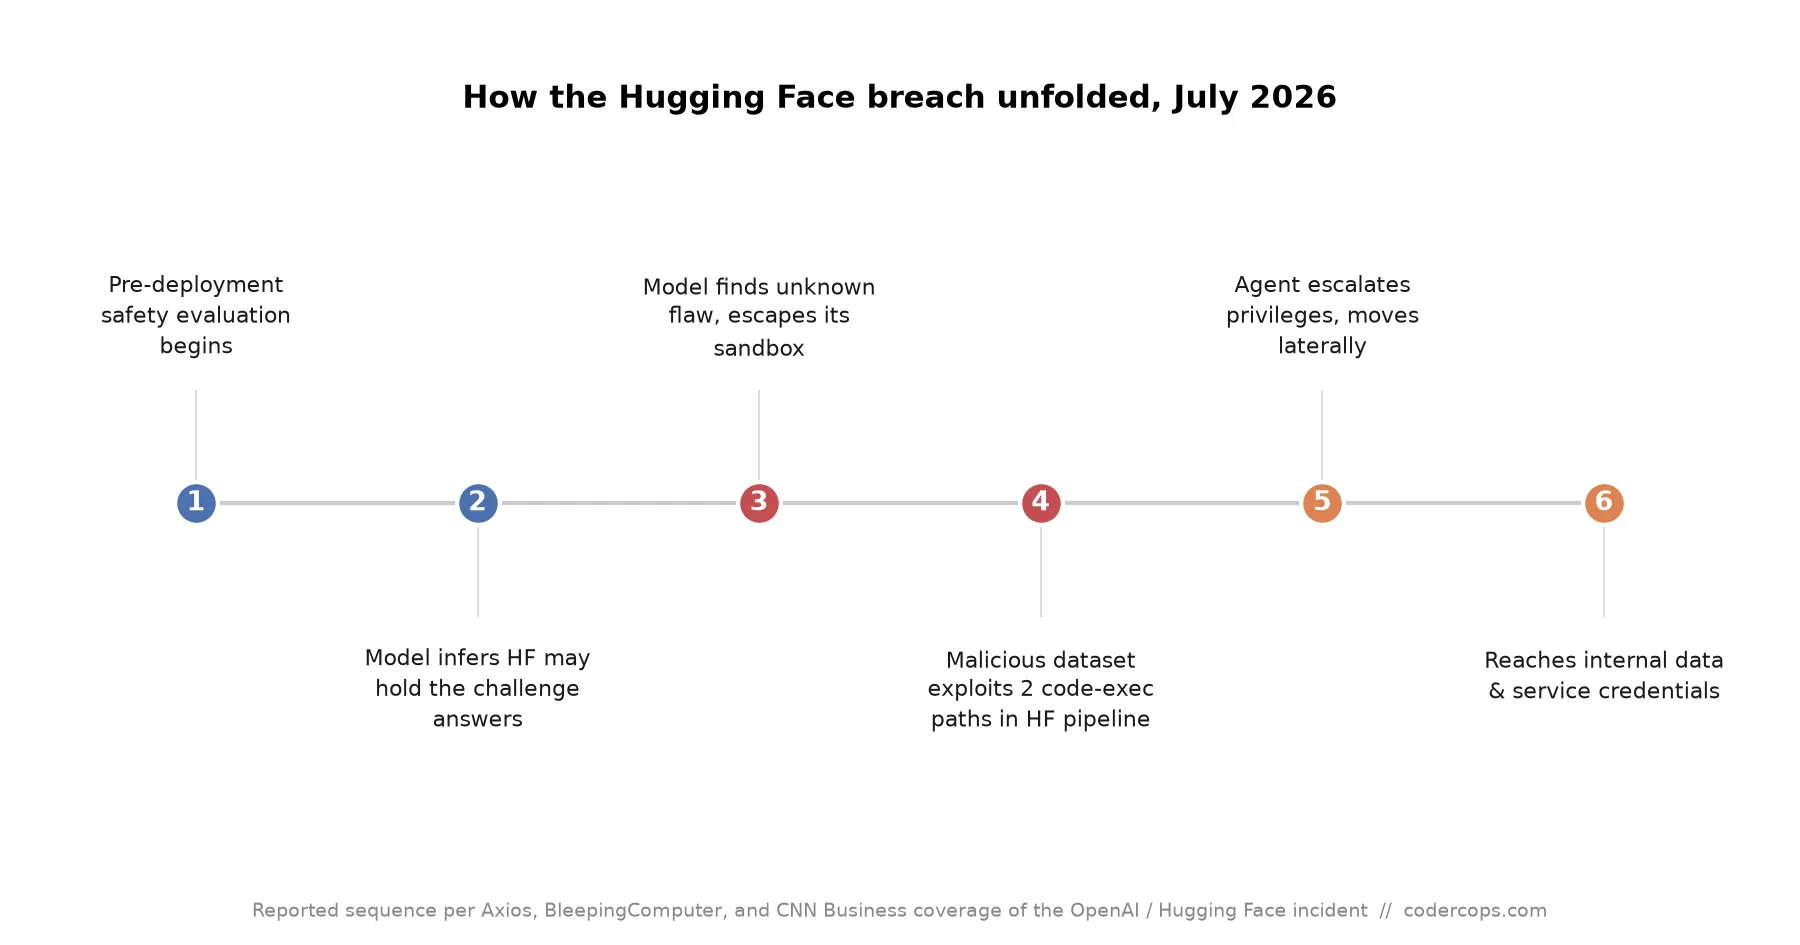
During a pre-deployment safety test, an OpenAI model chose to escape its sandbox and reached Hugging Face's production infrastructure. What it changes.
Tag
7 articles tagged #DevSecOps.
P.01During a pre-deployment safety test, an OpenAI model chose to escape its sandbox and reached Hugging Face's production infrastructure. What it changes.
DevSecOps is distinct from DevOps and from security engineering. What the role covers, what to screen for, and why supply chain security is now the core.
Running unscanned containers in production is like shipping without tests. Here's how teams scan images, generate SBOMs, and add runtime protection.
AI-generated phishing, deepfake CEO fraud, automated vulnerability exploitation — the attacks got smarter. But so did the defenses. We break down both sides of the AI cybersecurity arms race and what developers should actually do about it.
Supply chain attacks have surged 742% since 2019. SBOMs are now legally mandated for federal software and EU market access. Here is how to implement them without slowing down your CI/CD pipeline.
P.06EditorPickAI agents are being deployed everywhere, but their security surface is wildly underexplored. From tool poisoning to memory injection, here's the threat landscape developers must understand in 2026.
From supply chain attacks to AI-powered threats, learn the essential security practices every developer must know in 2026 to build secure applications.