P.01Hardening npm Against the Next Supply Chain Worm
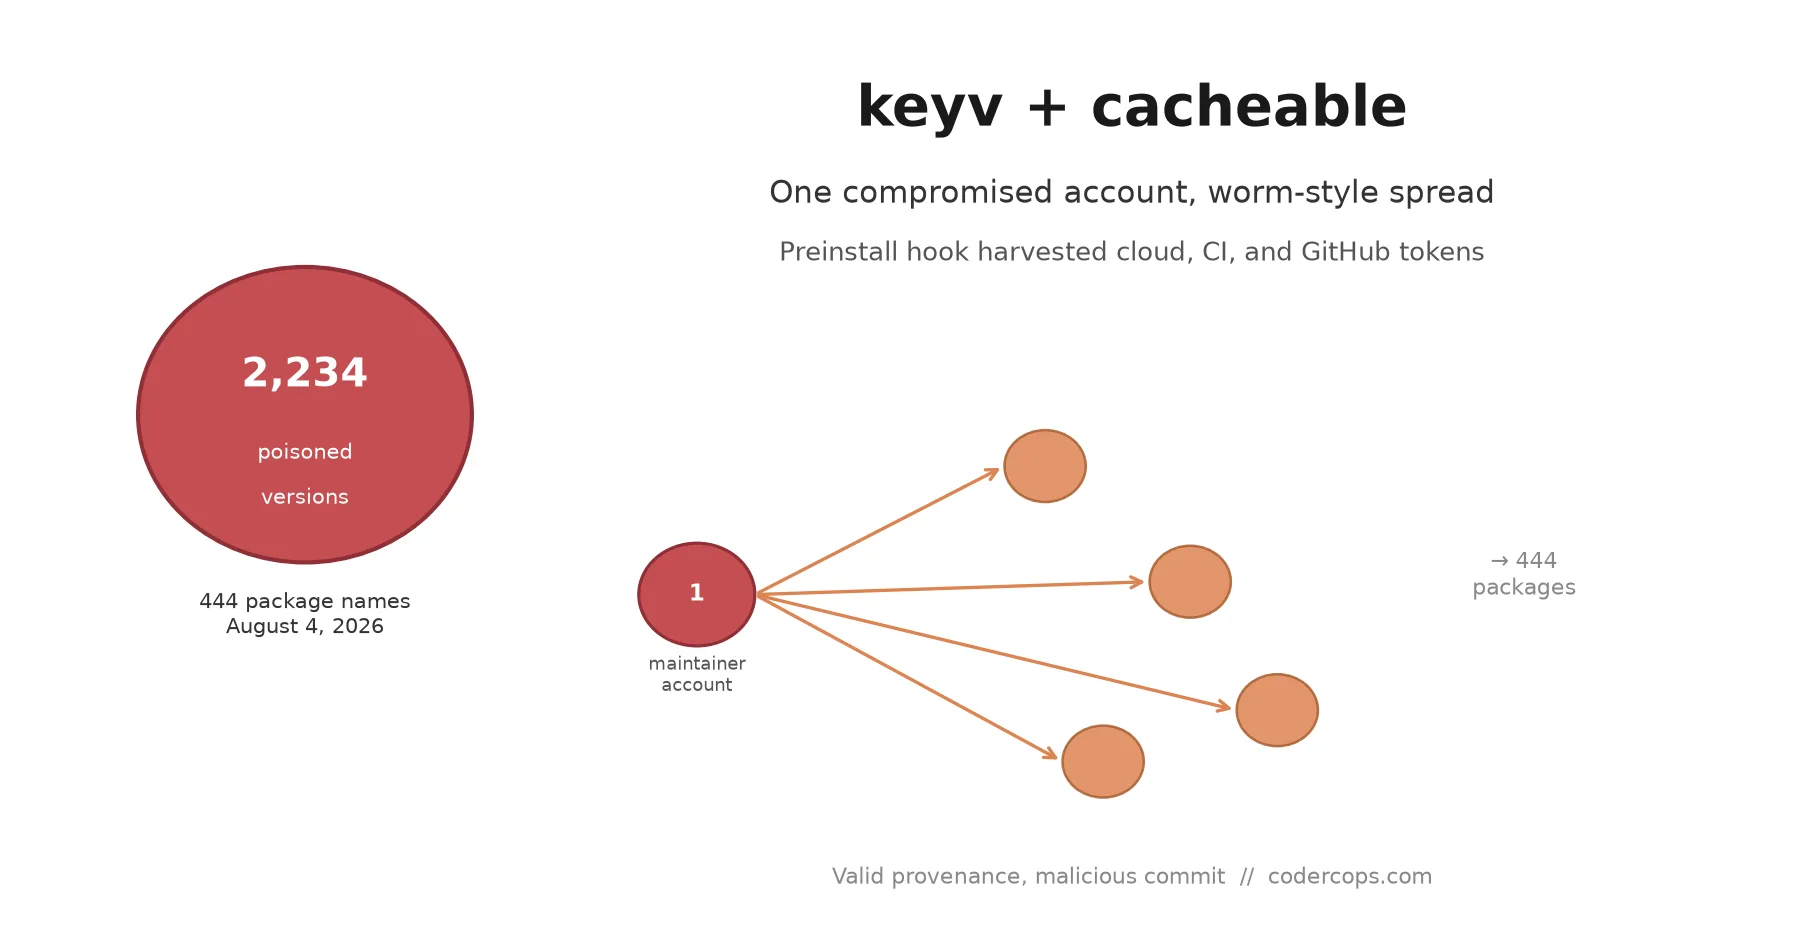
The keyv attack poisoned 2,234 package versions in a day, and it won't be the last. The checklist for install scripts, provenance, lockfiles, and CI tokens.
Tag
11 articles tagged #npm.
P.01The keyv attack poisoned 2,234 package versions in a day, and it won't be the last. The checklist for install scripts, provenance, lockfiles, and CI tokens.
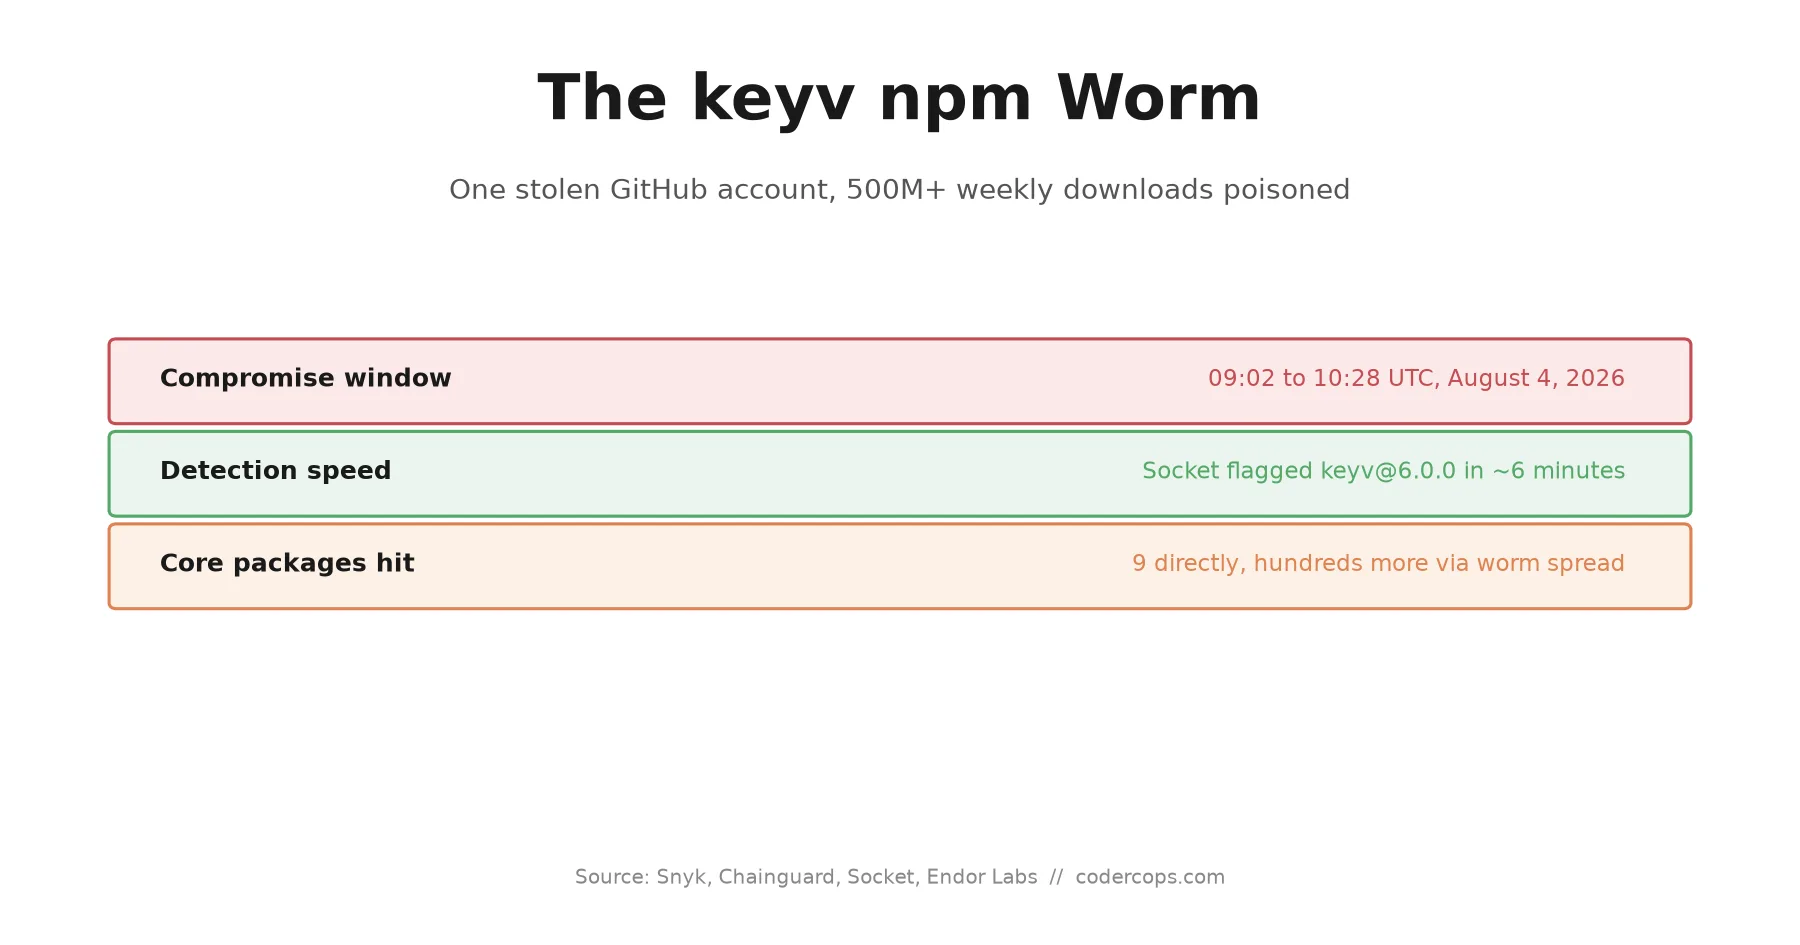
P.02A compromised maintainer account turned keyv and cacheable into a self-propagating npm worm that stole cloud, CI, and GitHub credentials. How to check.
P.03A compromised maintainer account pushed malware into keyv, cacheable, and seven other npm packages. Socket caught it in six minutes. How the worm worked.
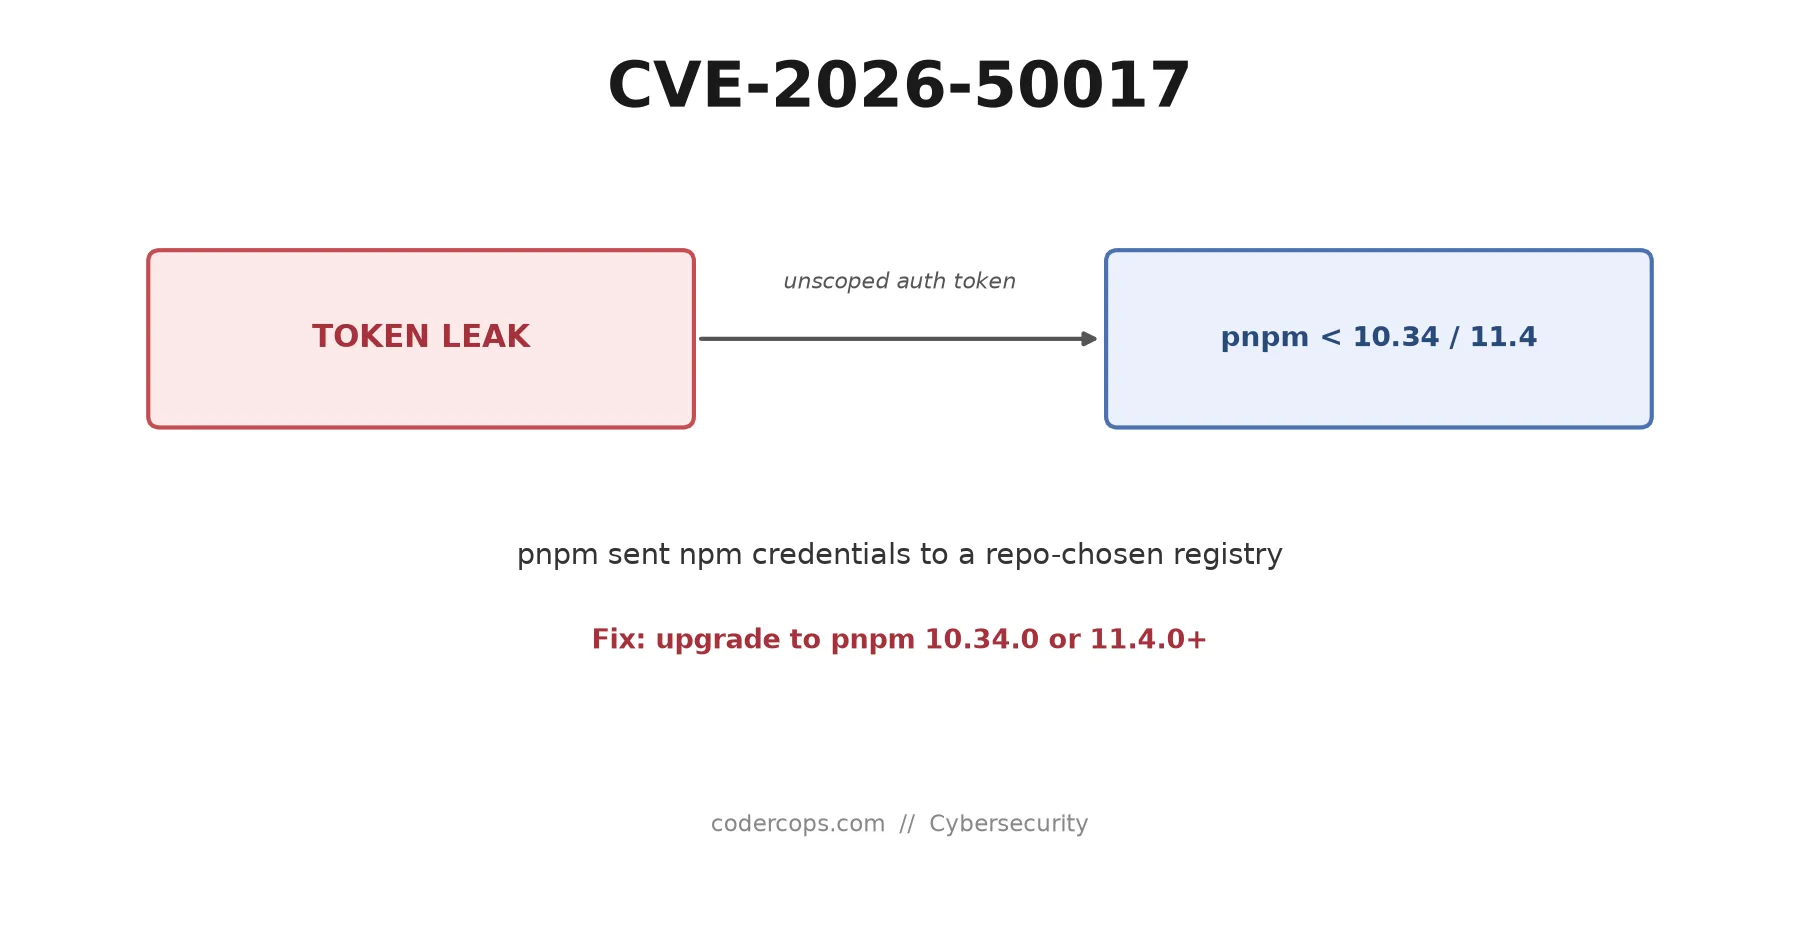
P.04pnpm before 10.34.0 and 11.4.0 could send your unscoped npm token to whatever registry a repo's .npmrc named. How it works, and how to check and fix.
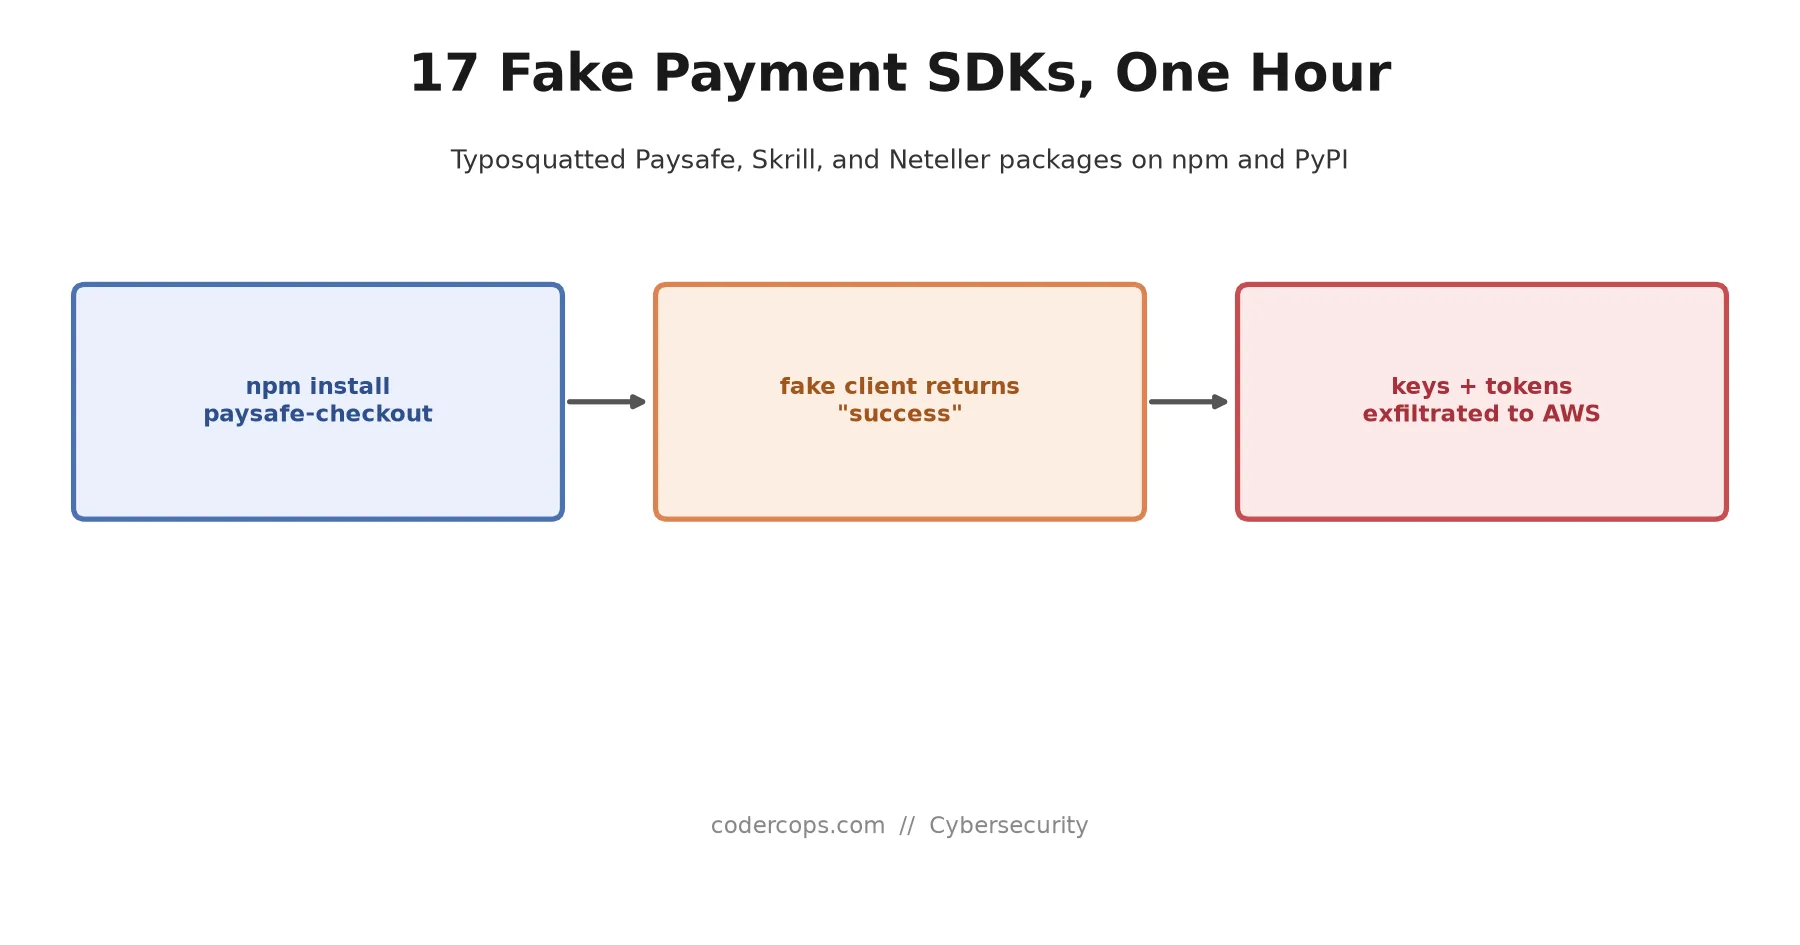
P.05Seventeen packages published July 7 impersonated real payment SDKs, returned fake success responses, and quietly exfiltrated API keys and cloud credentials.
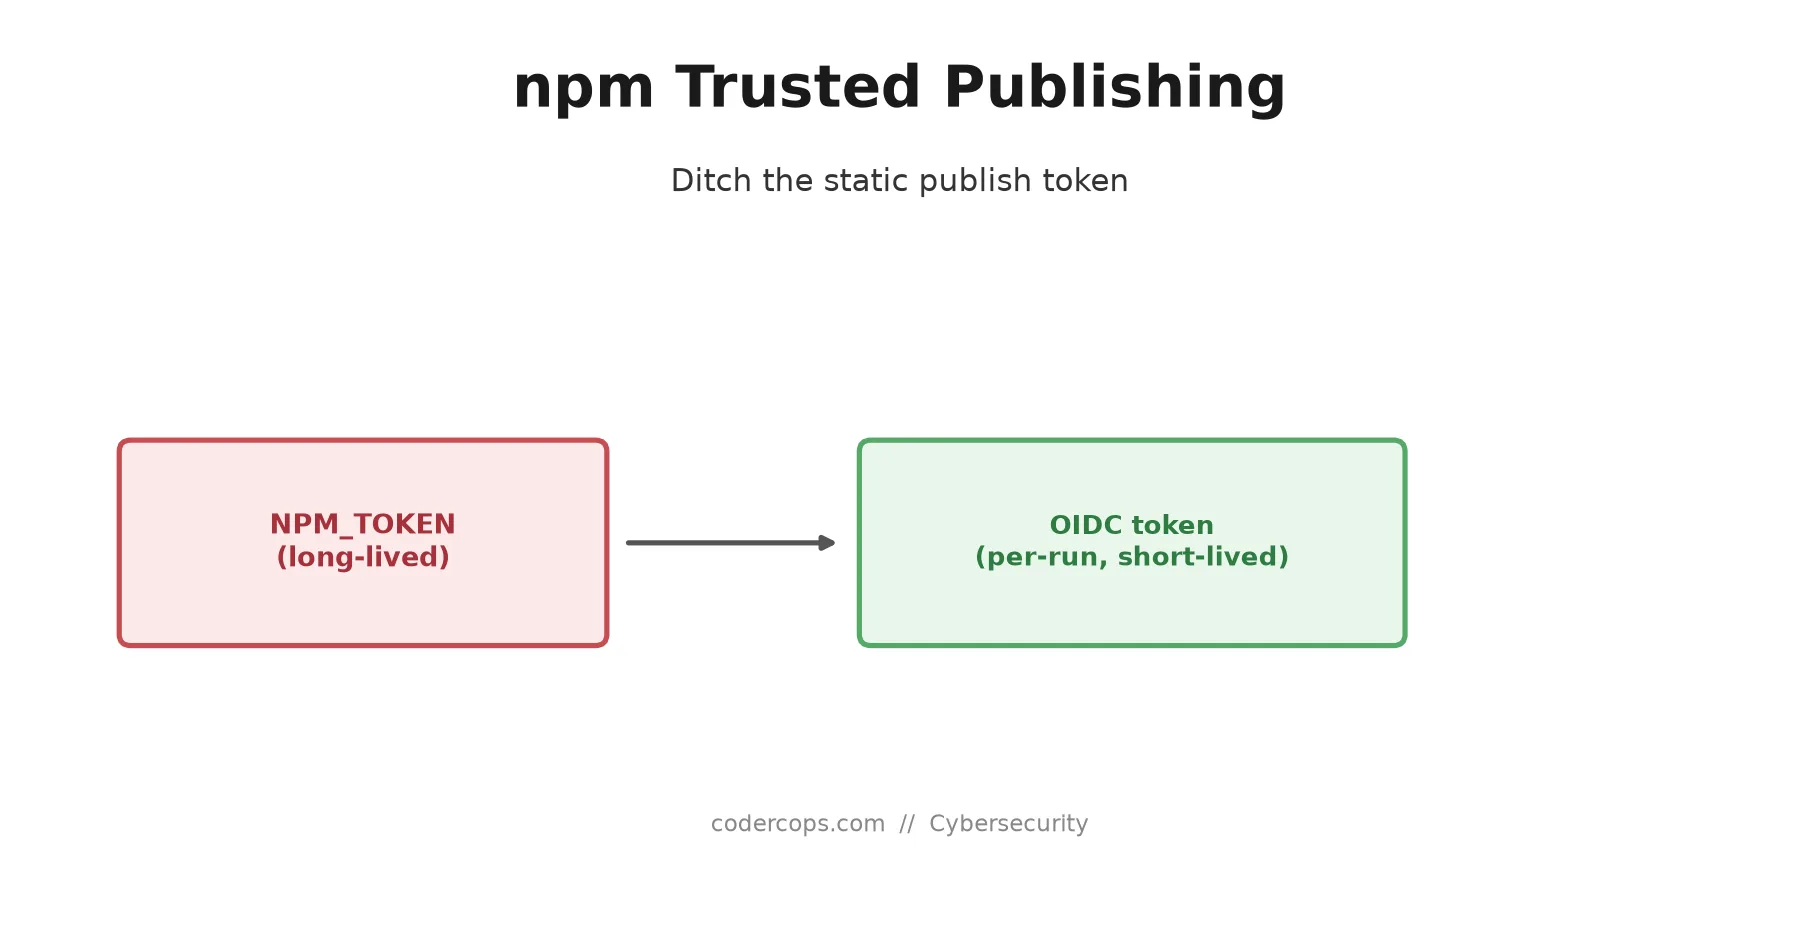
P.06Trusted publishing lets GitHub Actions and GitLab CI publish via short-lived OIDC tokens instead of a stored npm token. The setup, and the May 2026 change.
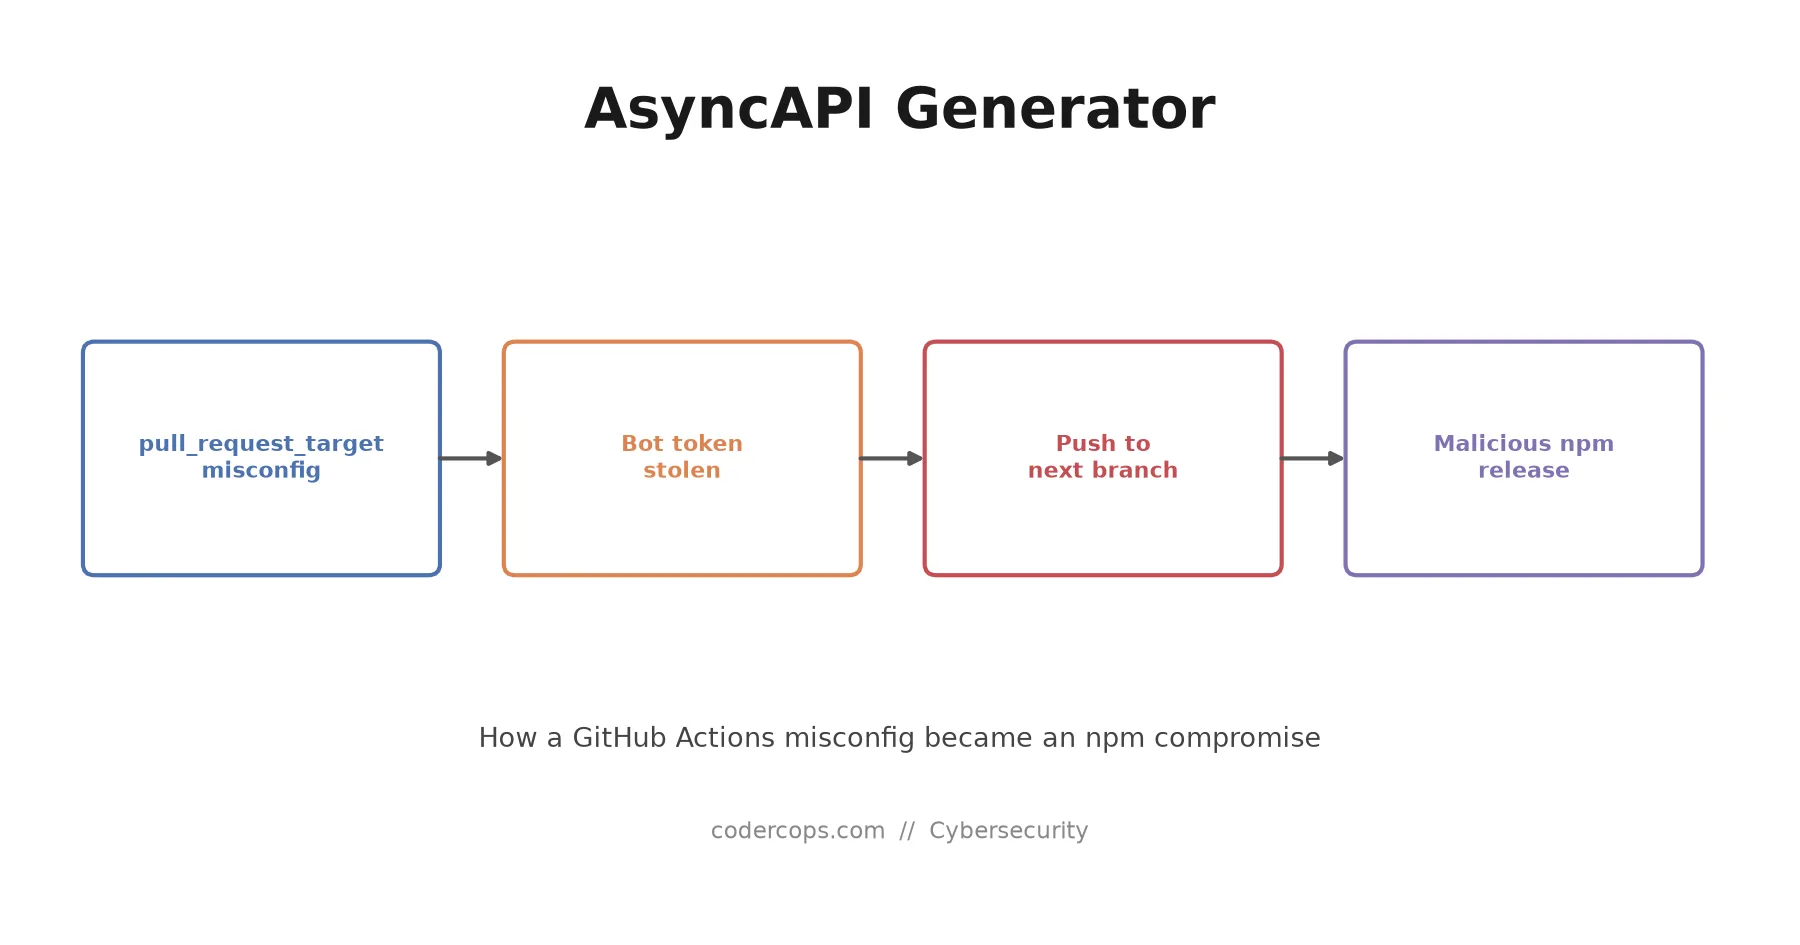
P.07A GitHub Actions misconfiguration let an attacker open dozens of PRs, steal a privileged bot token, and push a malicious @asyncapi/generator release.
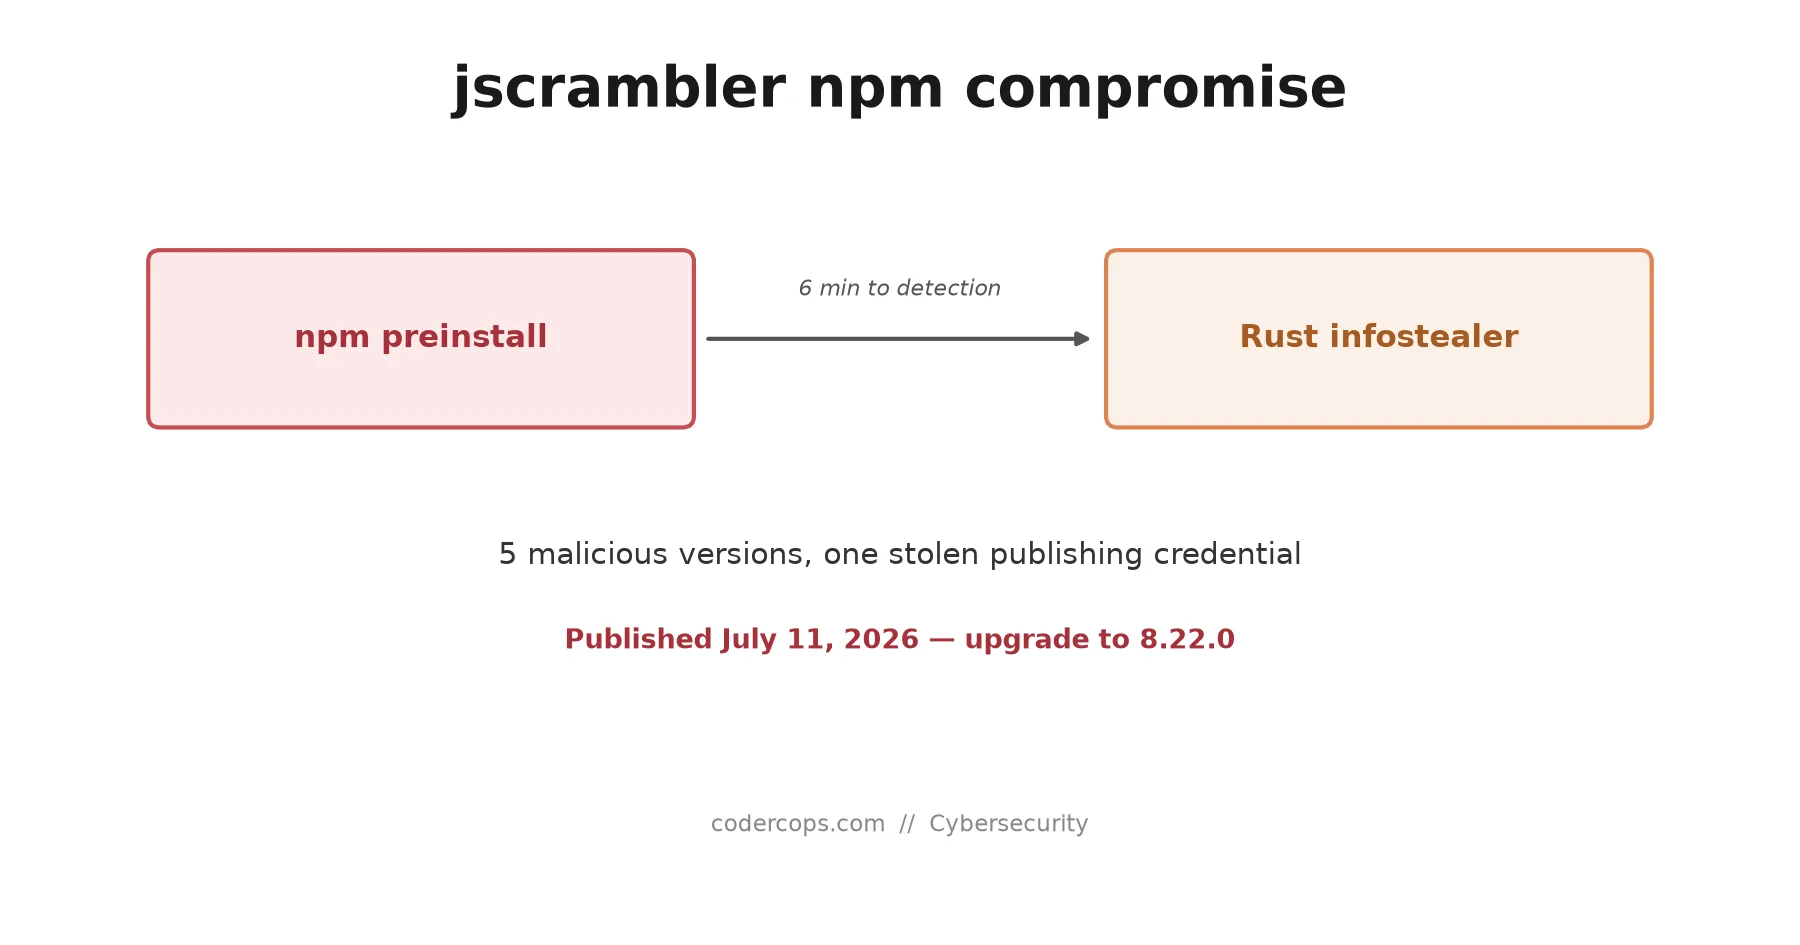
P.08Attackers used a stolen credential to push five malicious jscrambler versions, each carrying a 7.8MB cross-platform infostealer. What it stole, and how to check.
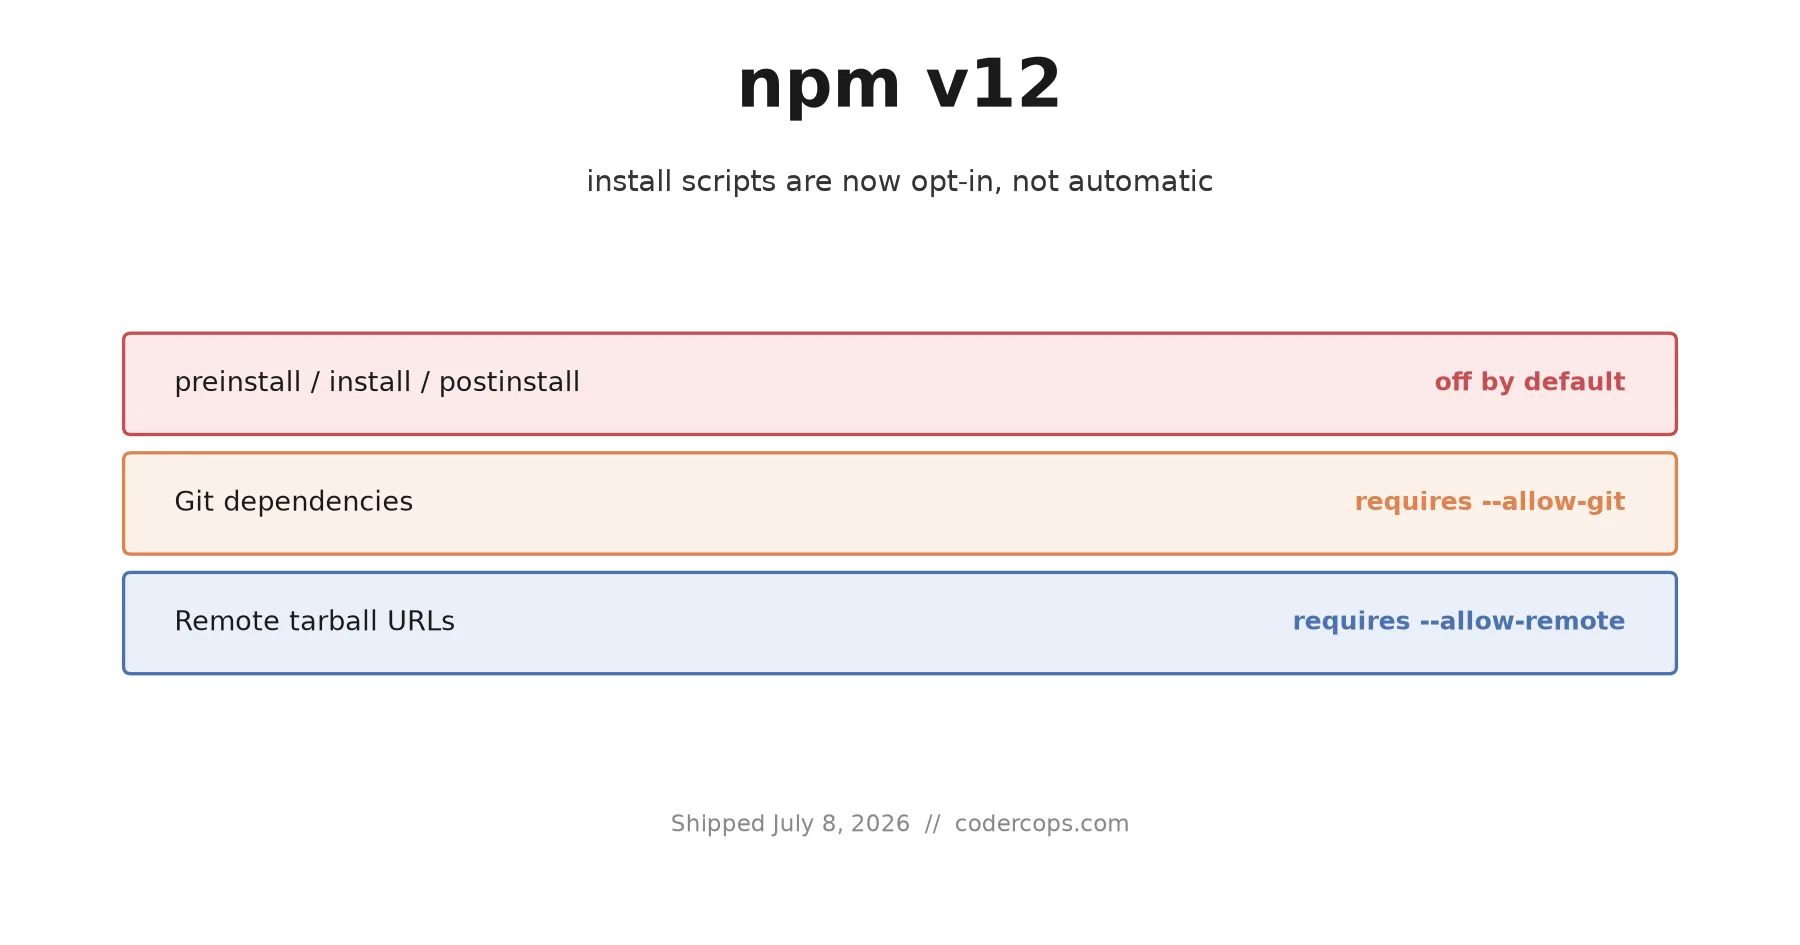
P.09npm v12 blocks preinstall, install, and postinstall scripts, Git dependencies, and remote tarballs unless allowed. What breaks, and how to migrate.
P.10TanStack (42 packages) and React Native Aria (17) were hit weeks apart with different entry points and payloads. What each teaches about dependencies.
Our curated list of npm packages that make it into every CODERCOPS project. Each one battle-tested across 30+ production apps with alternatives we considered.