P.01Cl0p Breached 40+ Firms Through PTC Windchill
One unauthenticated RCE in PTC Windchill and FlexPLM let Cl0p quietly take data from Shell, Philips, and GE. How CVE-2026-12569 works, and what to check.
Tag
9 articles tagged #Supply Chain.
P.01One unauthenticated RCE in PTC Windchill and FlexPLM let Cl0p quietly take data from Shell, Philips, and GE. How CVE-2026-12569 works, and what to check.
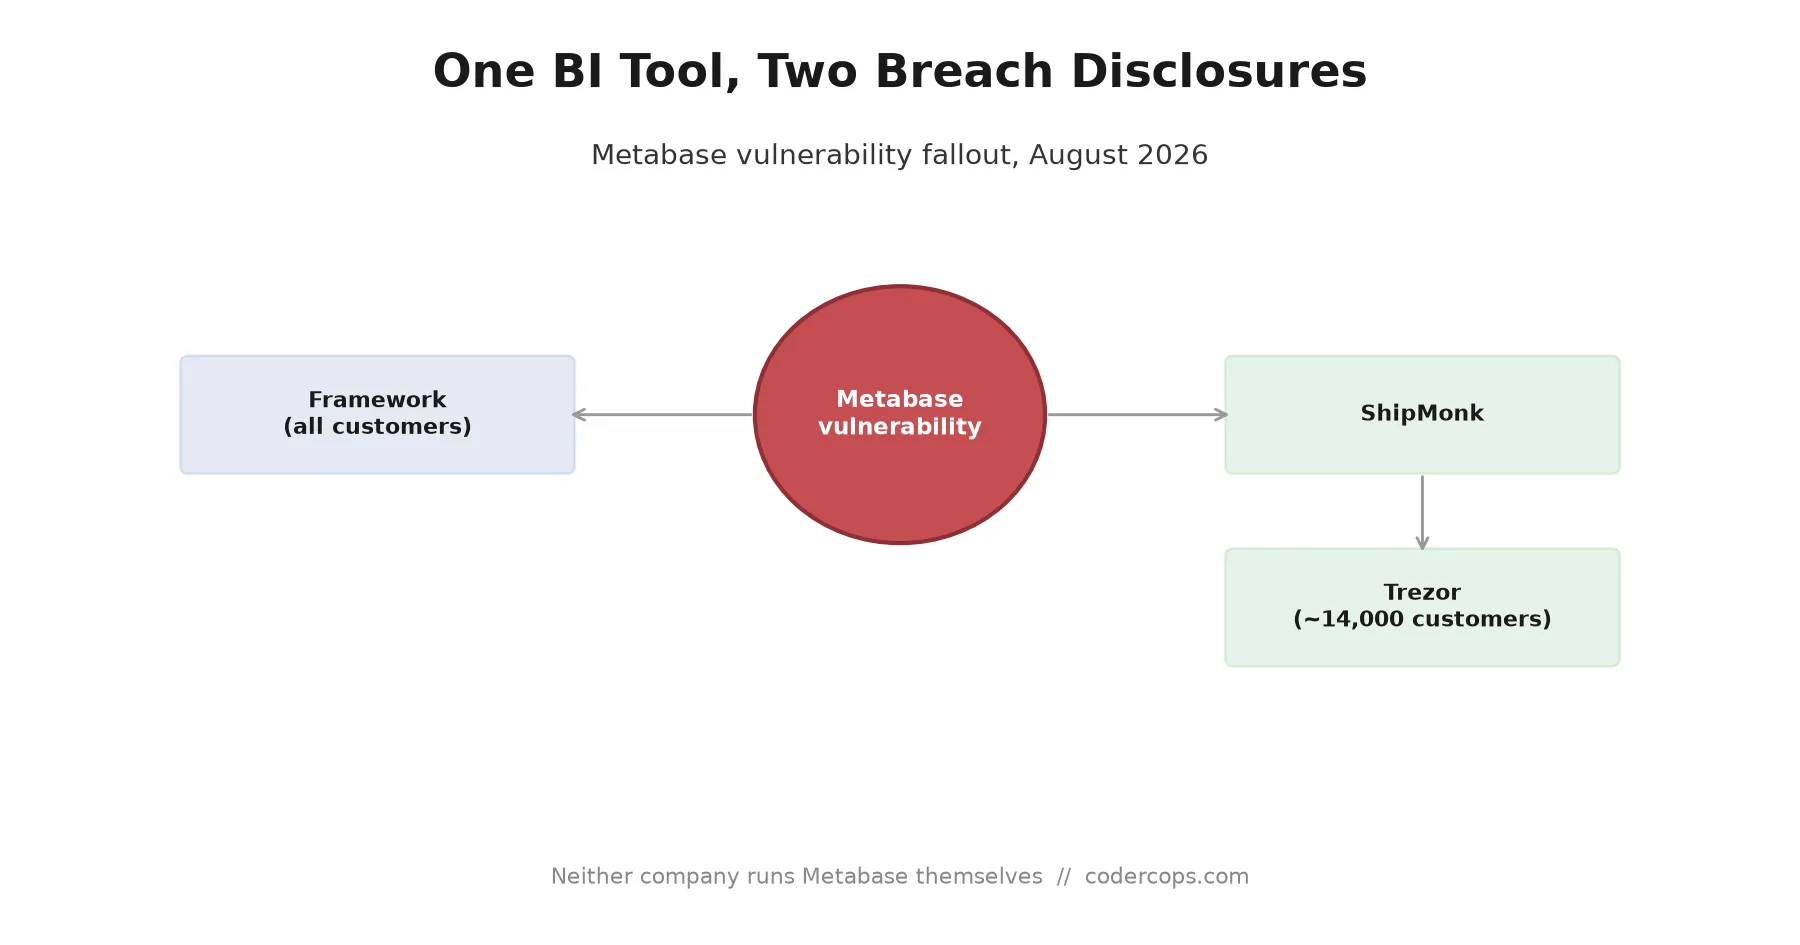
P.02Two unrelated companies disclosed breaches the same week, both tracing to a Metabase flaw in a vendor's stack. How it lines up with the CVE, and what to check.
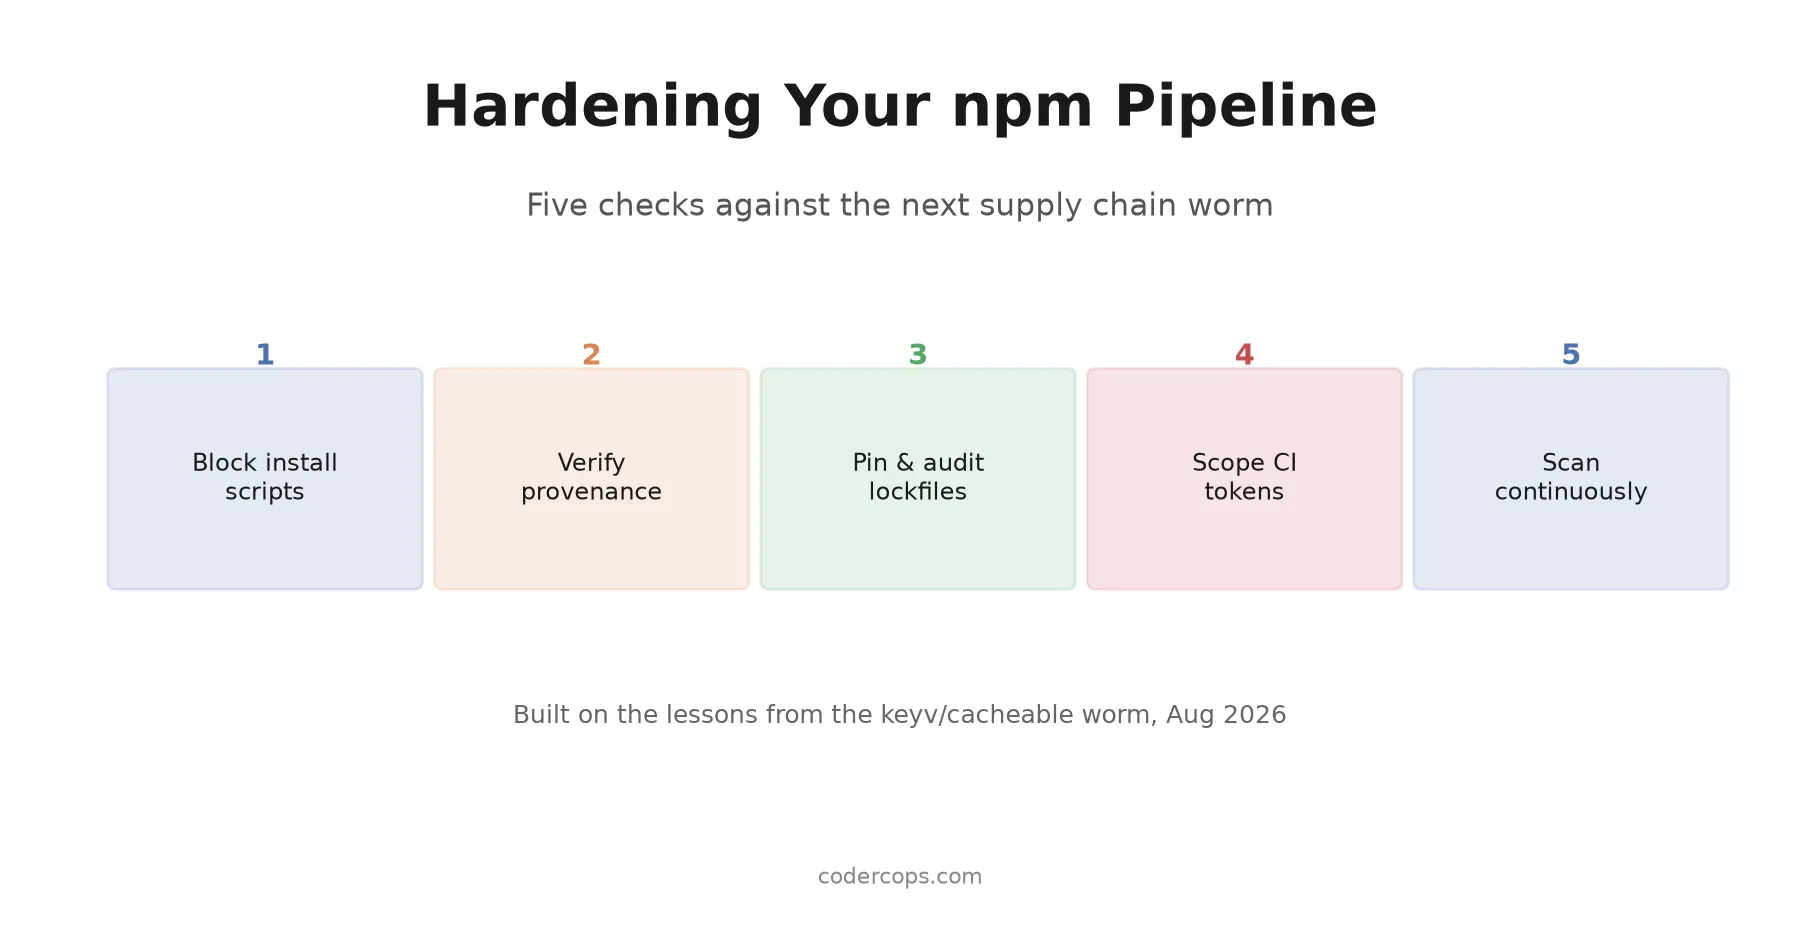
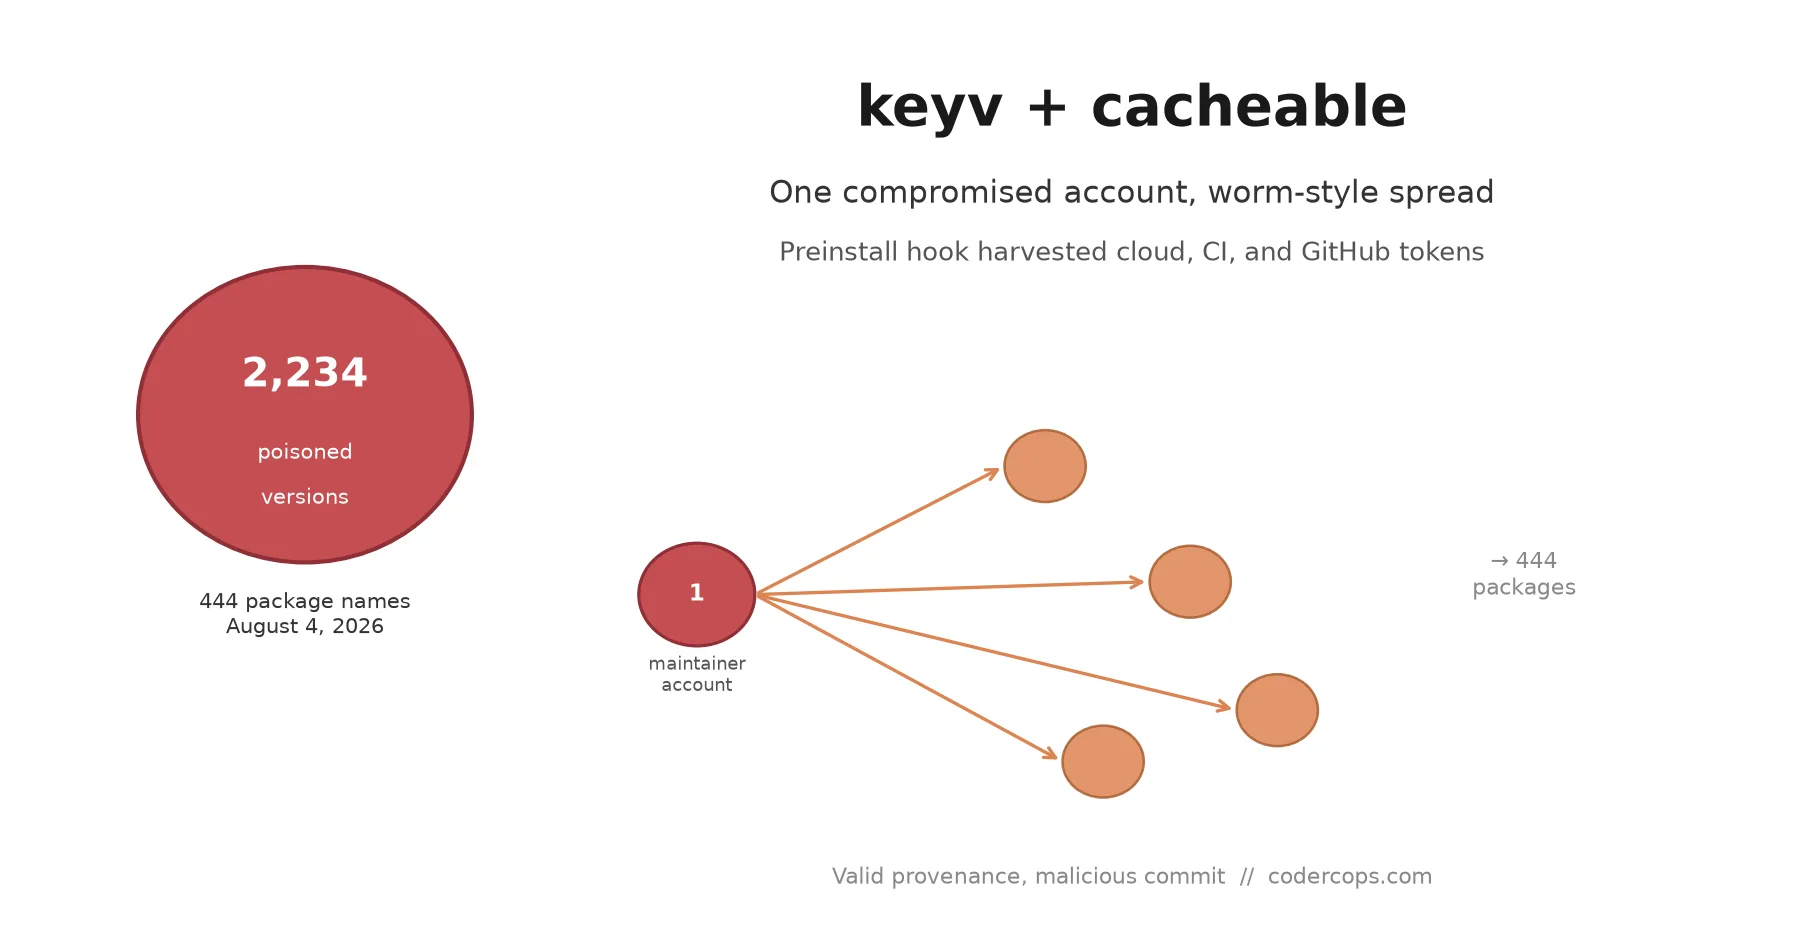
P.03The keyv attack poisoned 2,234 package versions in a day, and it won't be the last. The checklist for install scripts, provenance, lockfiles, and CI tokens.
P.04A compromised maintainer account turned keyv and cacheable into a self-propagating npm worm that stole cloud, CI, and GitHub credentials. How to check.
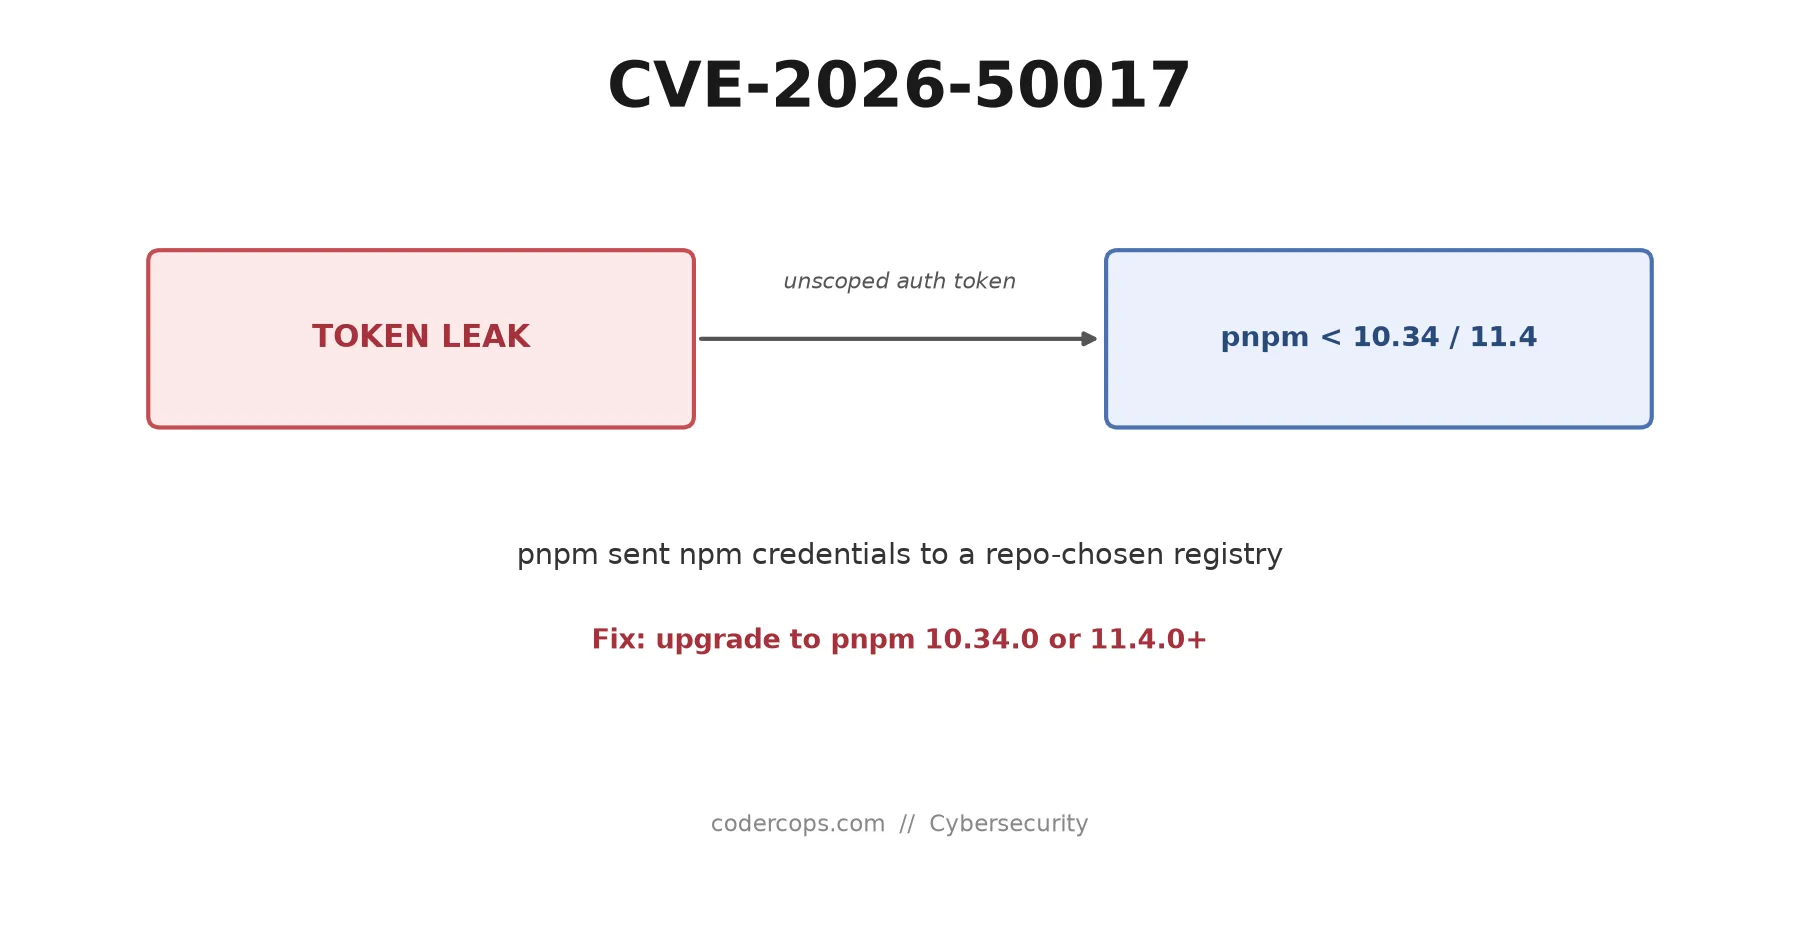
P.05pnpm before 10.34.0 and 11.4.0 could send your unscoped npm token to whatever registry a repo's .npmrc named. How it works, and how to check and fix.
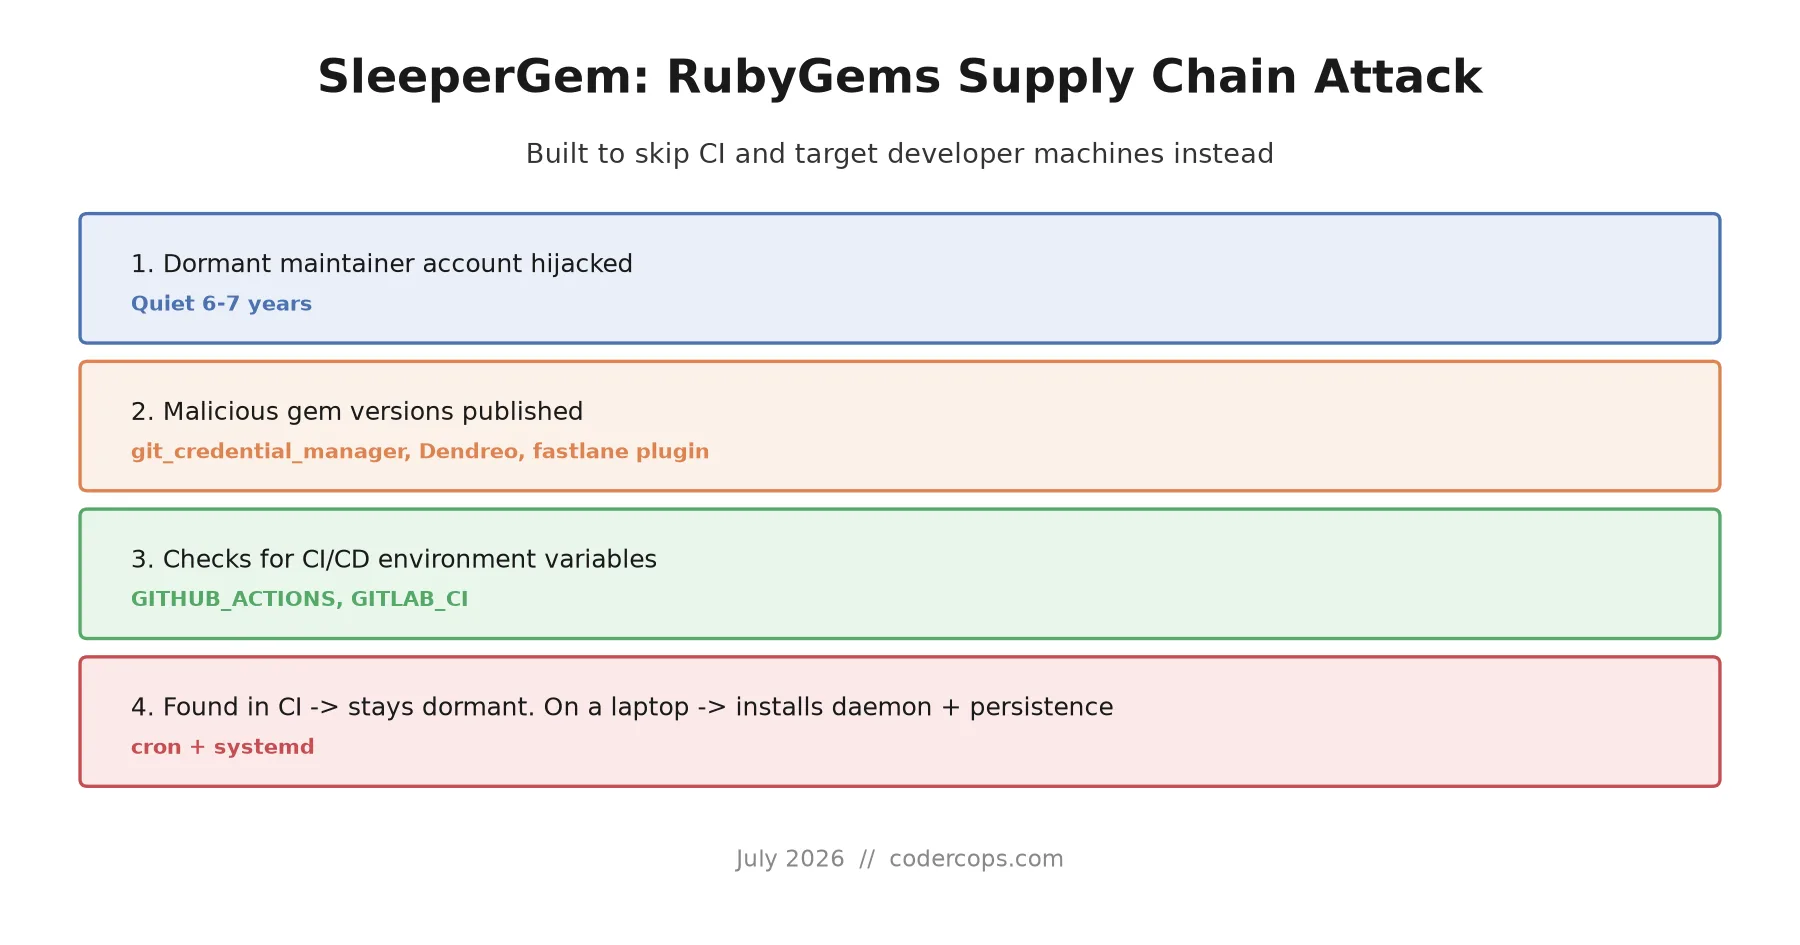
P.06Three malicious gems from a hijacked, six-year-dormant account check for CI variables and refuse to run there, targeting laptops. How to check your locks.
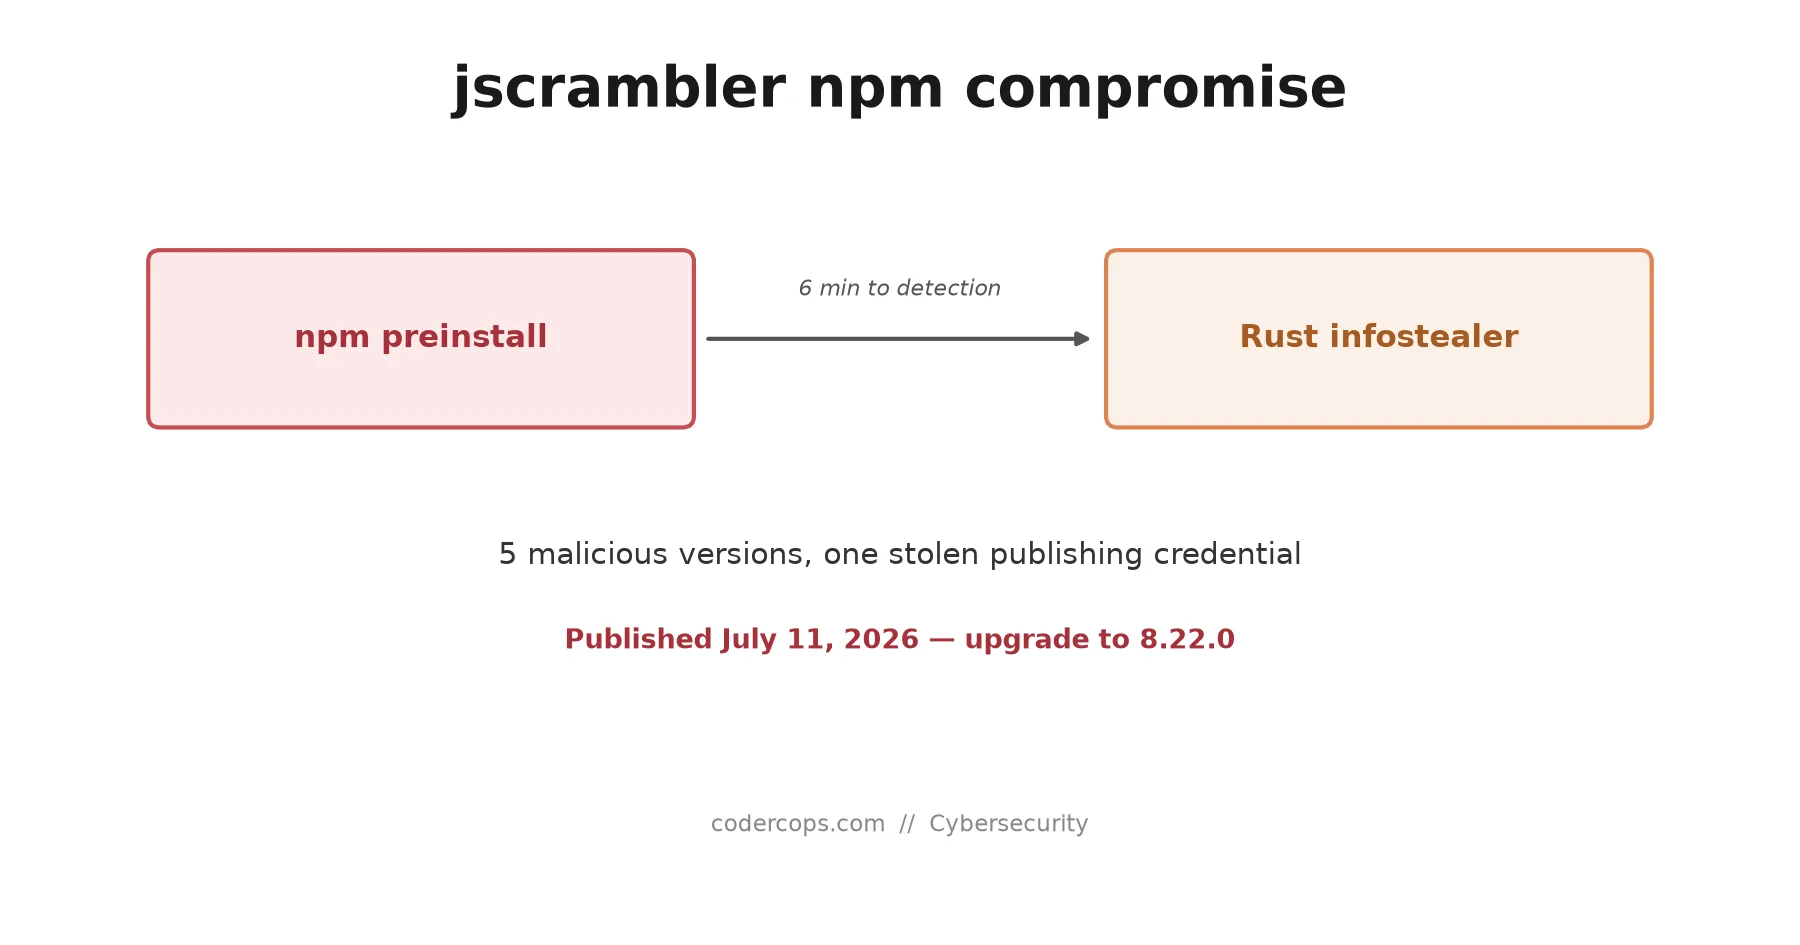
P.07Attackers used a stolen credential to push five malicious jscrambler versions, each carrying a 7.8MB cross-platform infostealer. What it stole, and how to check.
Strip away the crypto speculation and NFT mania. What is left of Web3 in 2026? Turns out, quite a lot — supply chain tracking, digital identity, smart contracts, and decentralized storage are quietly solving real problems.
Supply chain attacks have surged 742% since 2019. SBOMs are now legally mandated for federal software and EU market access. Here is how to implement them without slowing down your CI/CD pipeline.