P.01CSRF Protection in 2026: SameSite, Tokens, Origin Checks
SameSite cookies stop most CSRF, but not all. Learn when you still need tokens and Origin checks, with working Express code and a test you can run.
Tag
6 articles tagged #Authentication.
P.01SameSite cookies stop most CSRF, but not all. Learn when you still need tokens and Origin checks, with working Express code and a test you can run.
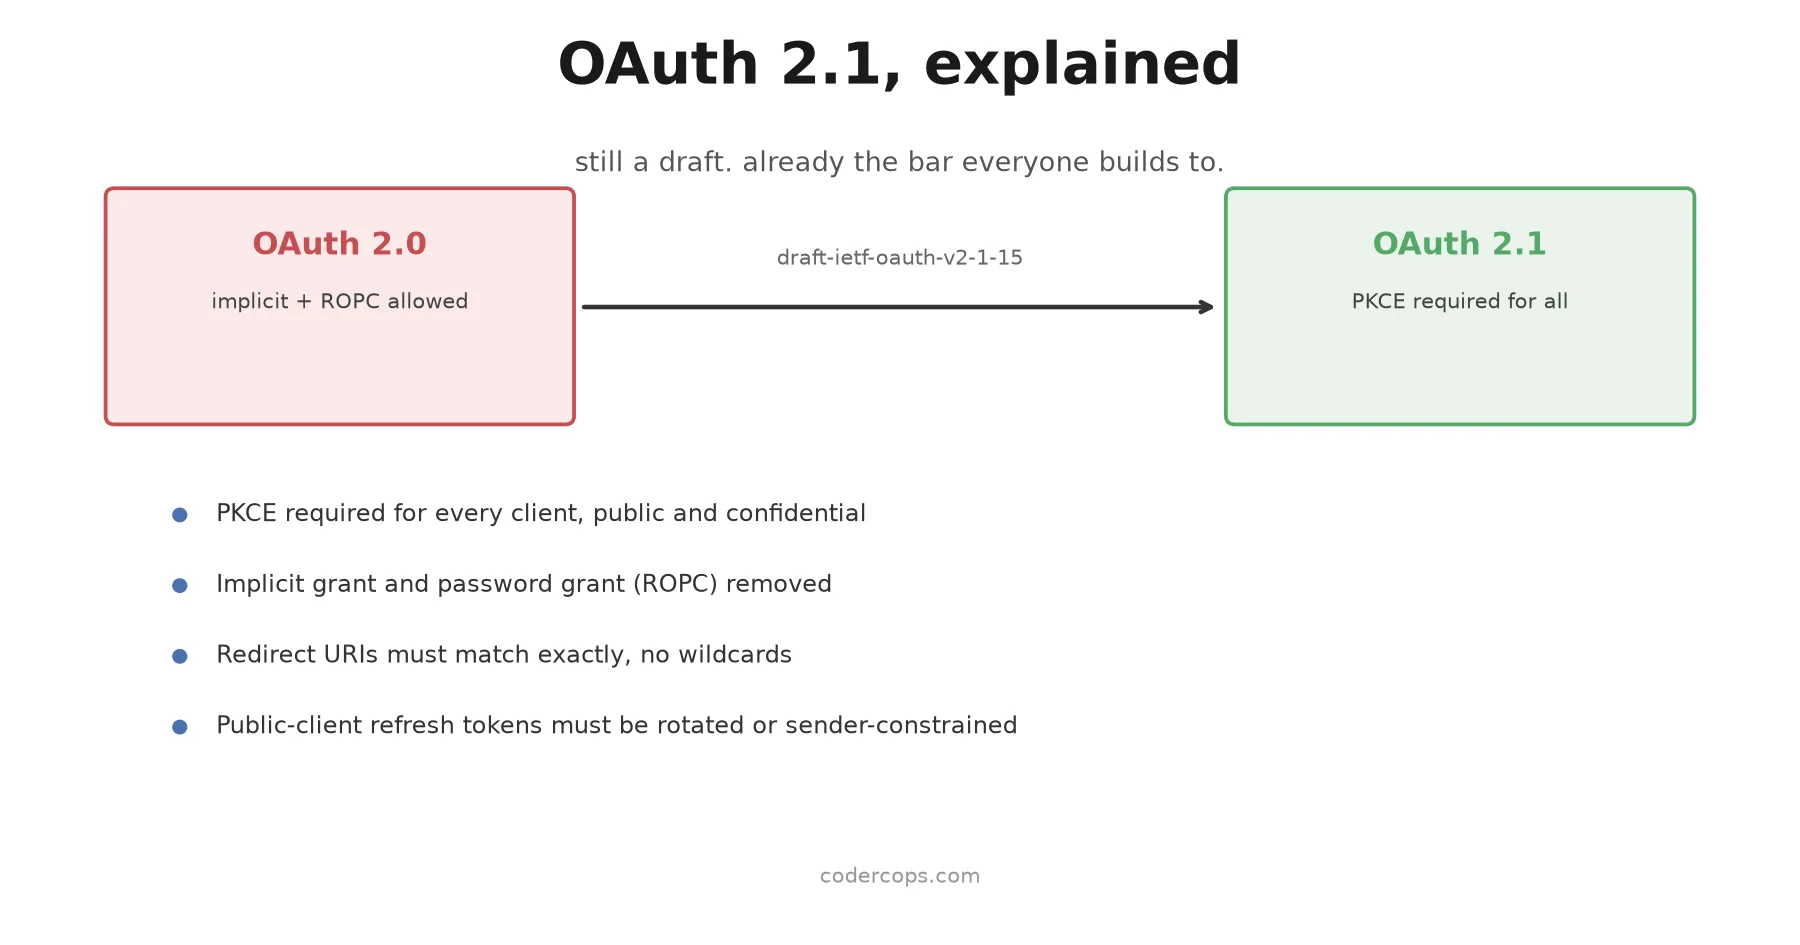
P.02OAuth 2.1 is still an IETF draft, but most providers enforce it already. What changed from 2.0, plus a checklist for auditing your own implementation.
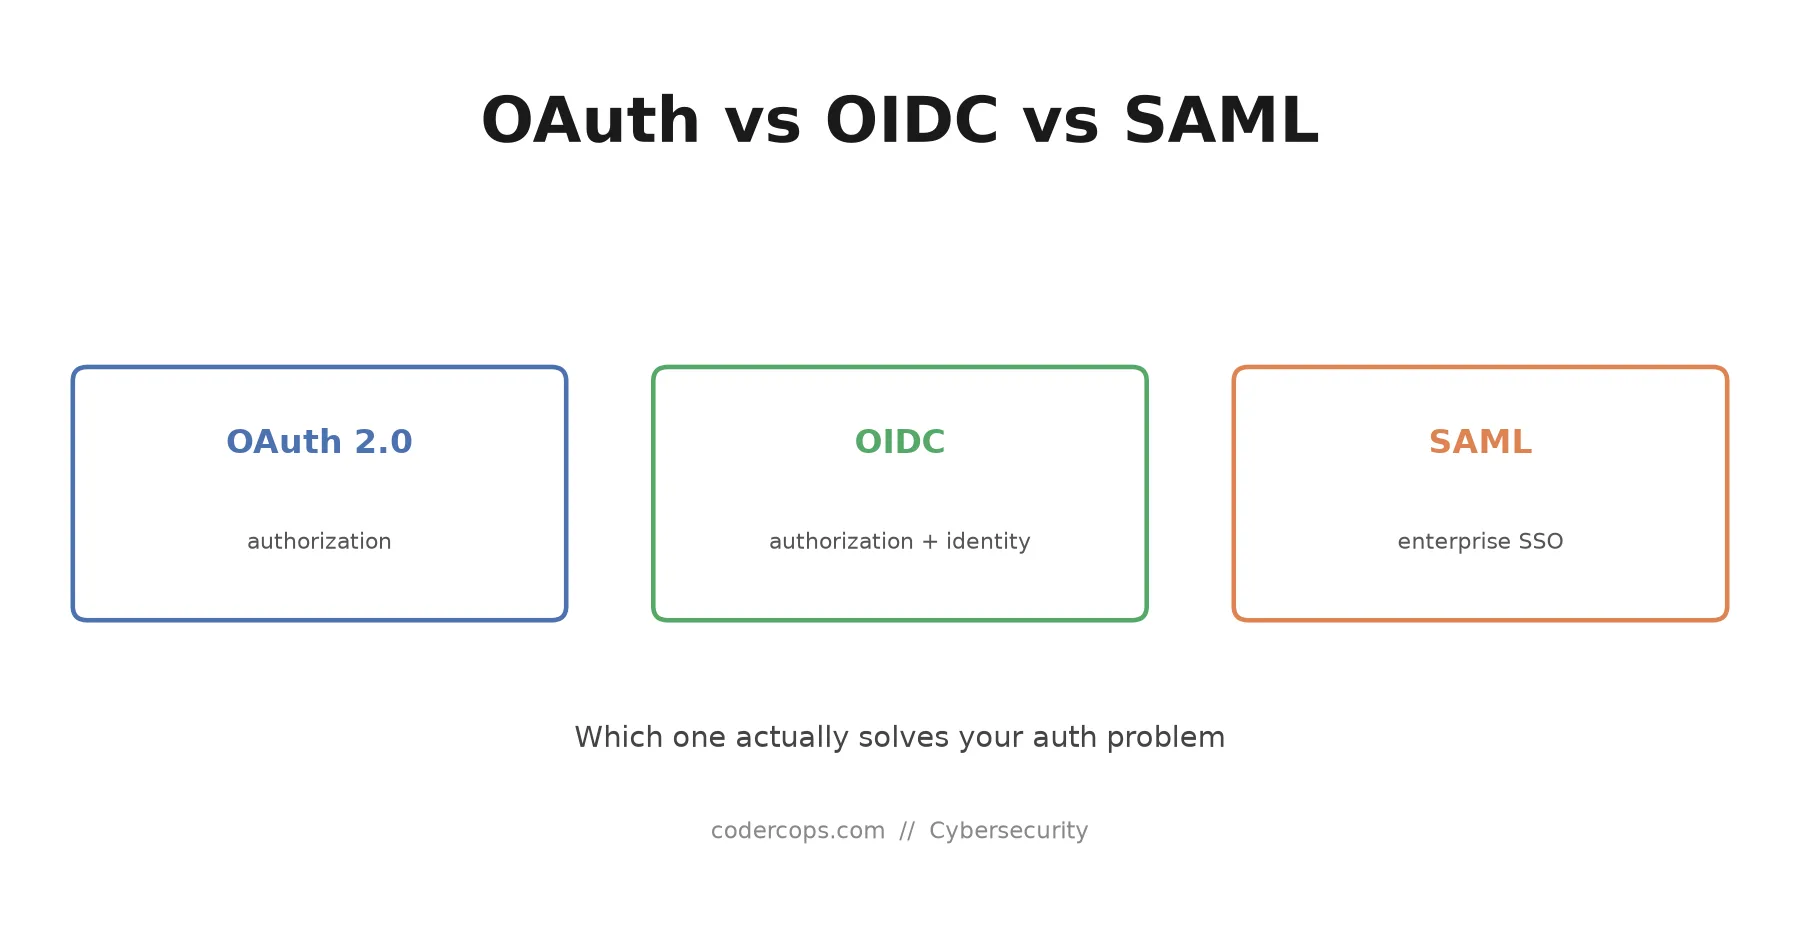
P.03OAuth handles authorization, OIDC adds identity on top, and SAML is the older enterprise SSO standard still running much of the corporate world. How to pick.
Three real authentication options for Next.js apps, with different trade-offs on control, cost, and setup time. Here's what each one actually involves.
The implicit flow is dead and tutorials still teach it. How authorization code flow with PKCE works, where tokens belong, and where SPA auth goes wrong.
Passkeys are mainstream now, with native support from Apple, Google, and Microsoft. Here's what WebAuthn looks like in real code, and when to use it.