P.01CVE-2026-44477: CloudNativePG's Superuser Escalation Bug
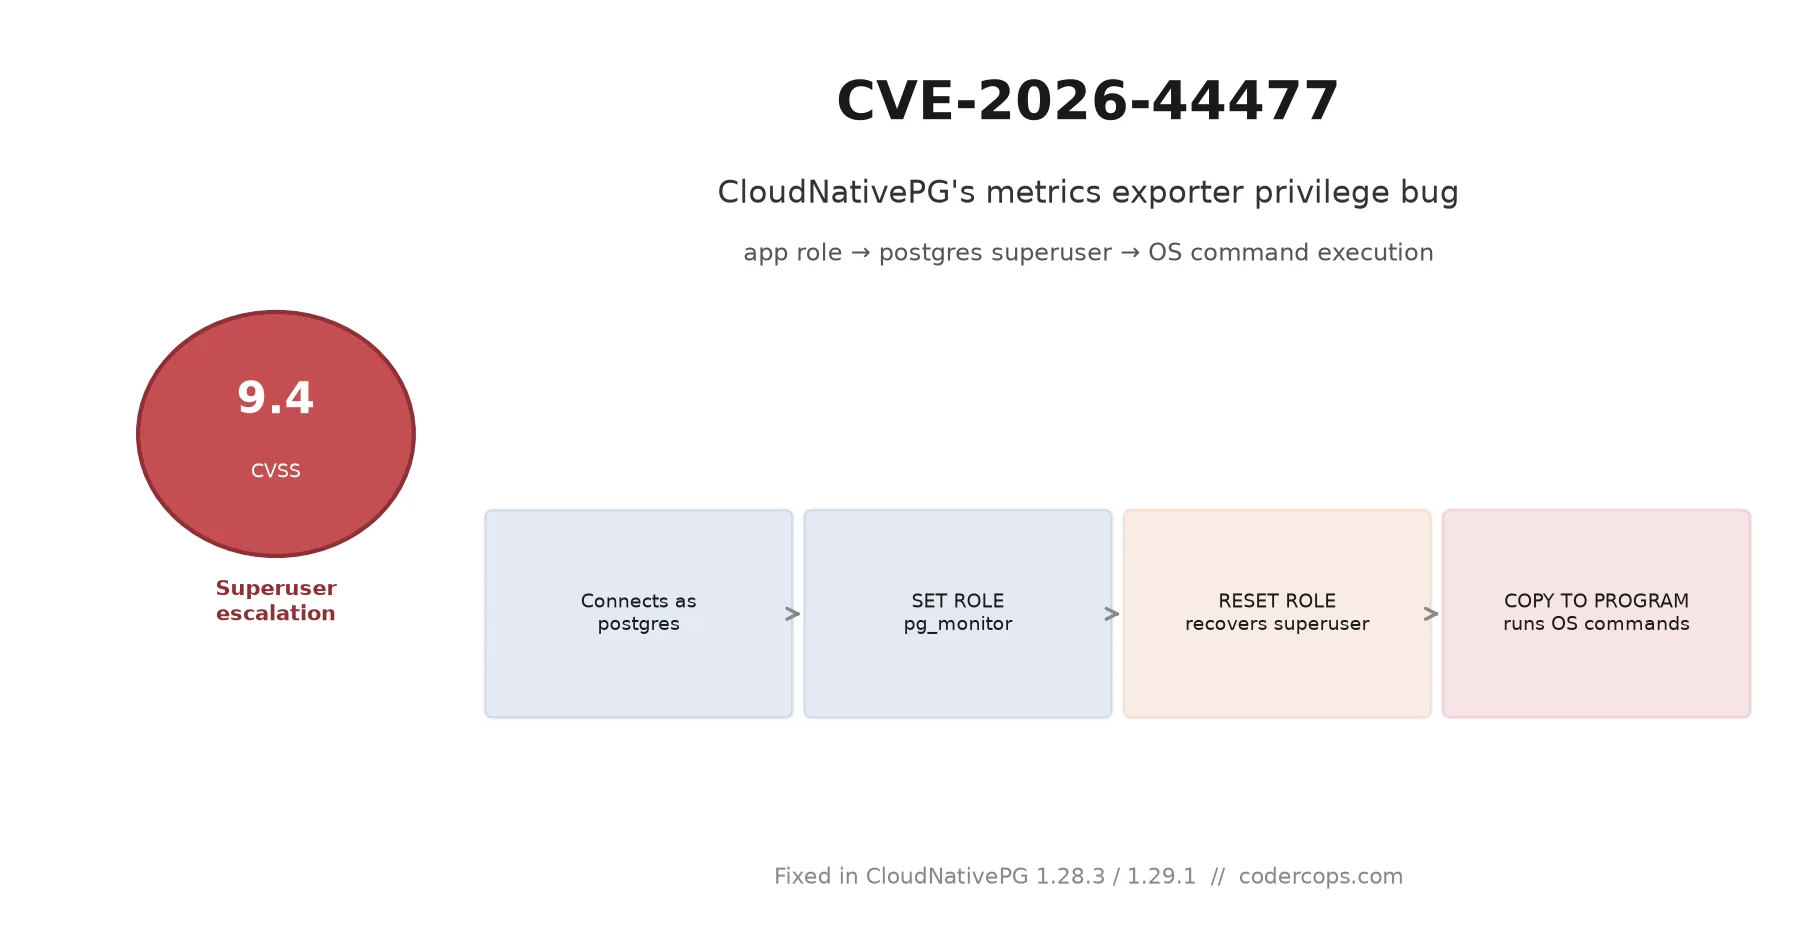
CVE-2026-44477 lets any database owner escalate to postgres superuser and run OS commands in CloudNativePG. Here is who is affected and how to patch.
Tag
10 articles tagged #Kubernetes.
P.01CVE-2026-44477 lets any database owner escalate to postgres superuser and run OS commands in CloudNativePG. Here is who is affected and how to patch.
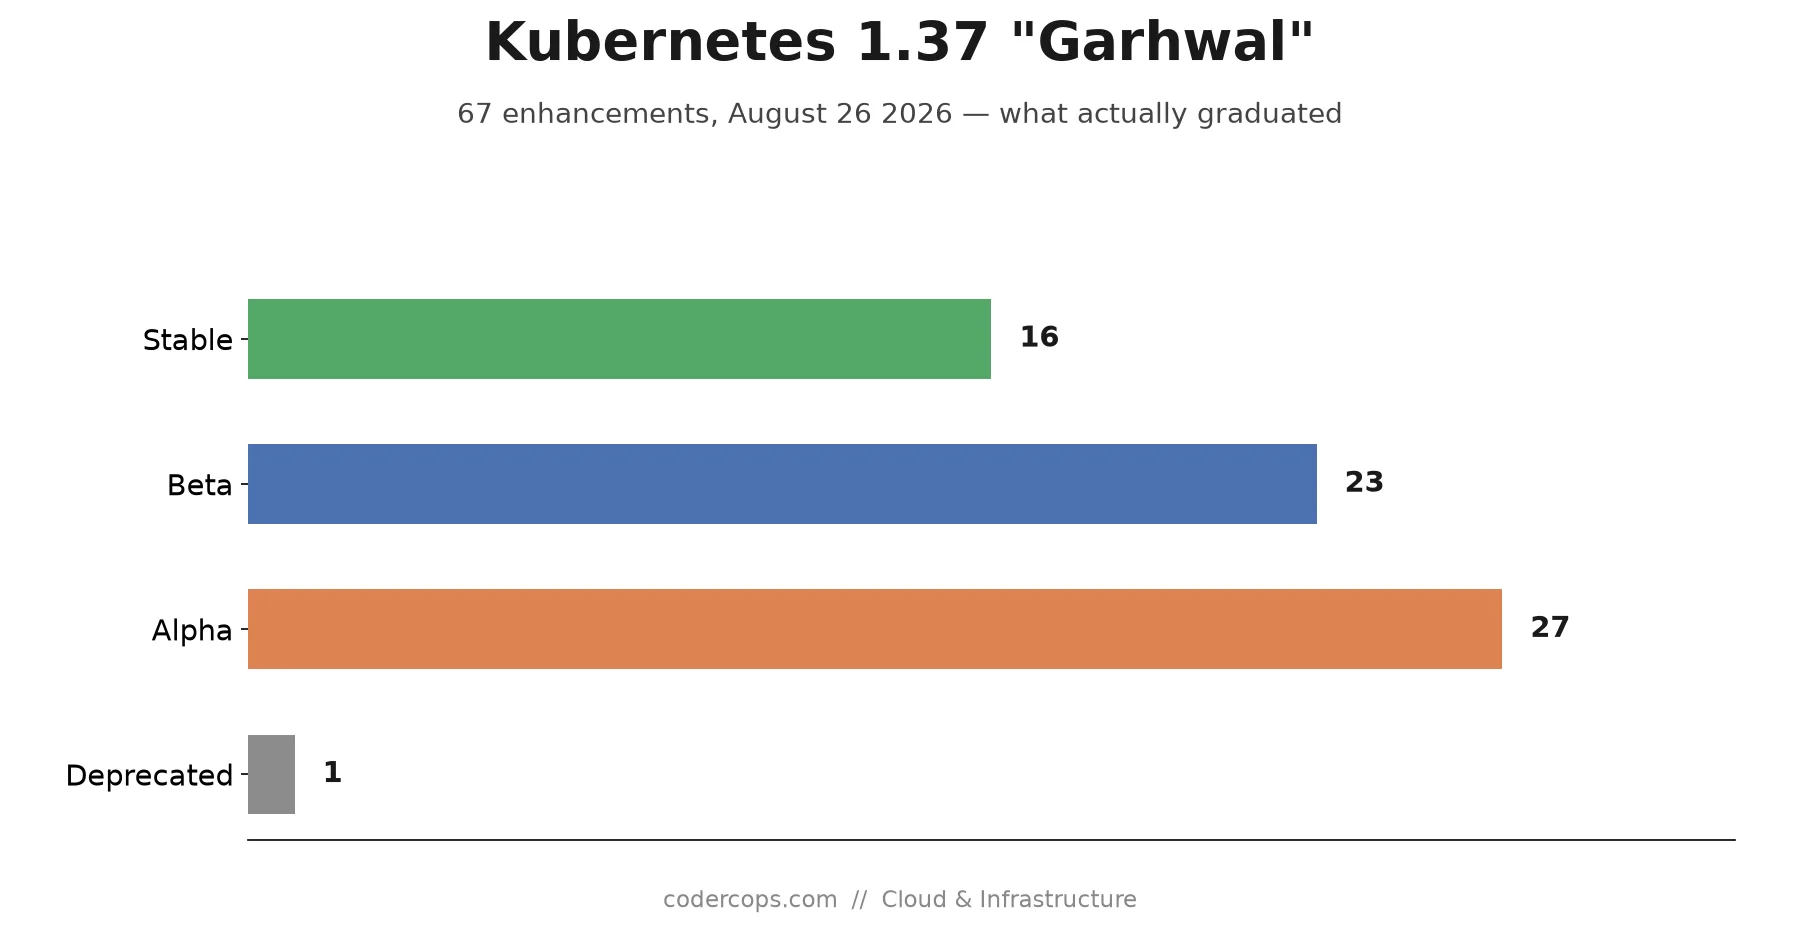
P.02Kubernetes 1.37 shipped August 26 with 67 enhancements. What actually graduated to stable, what's worth testing in beta, and what to leave alone for now.
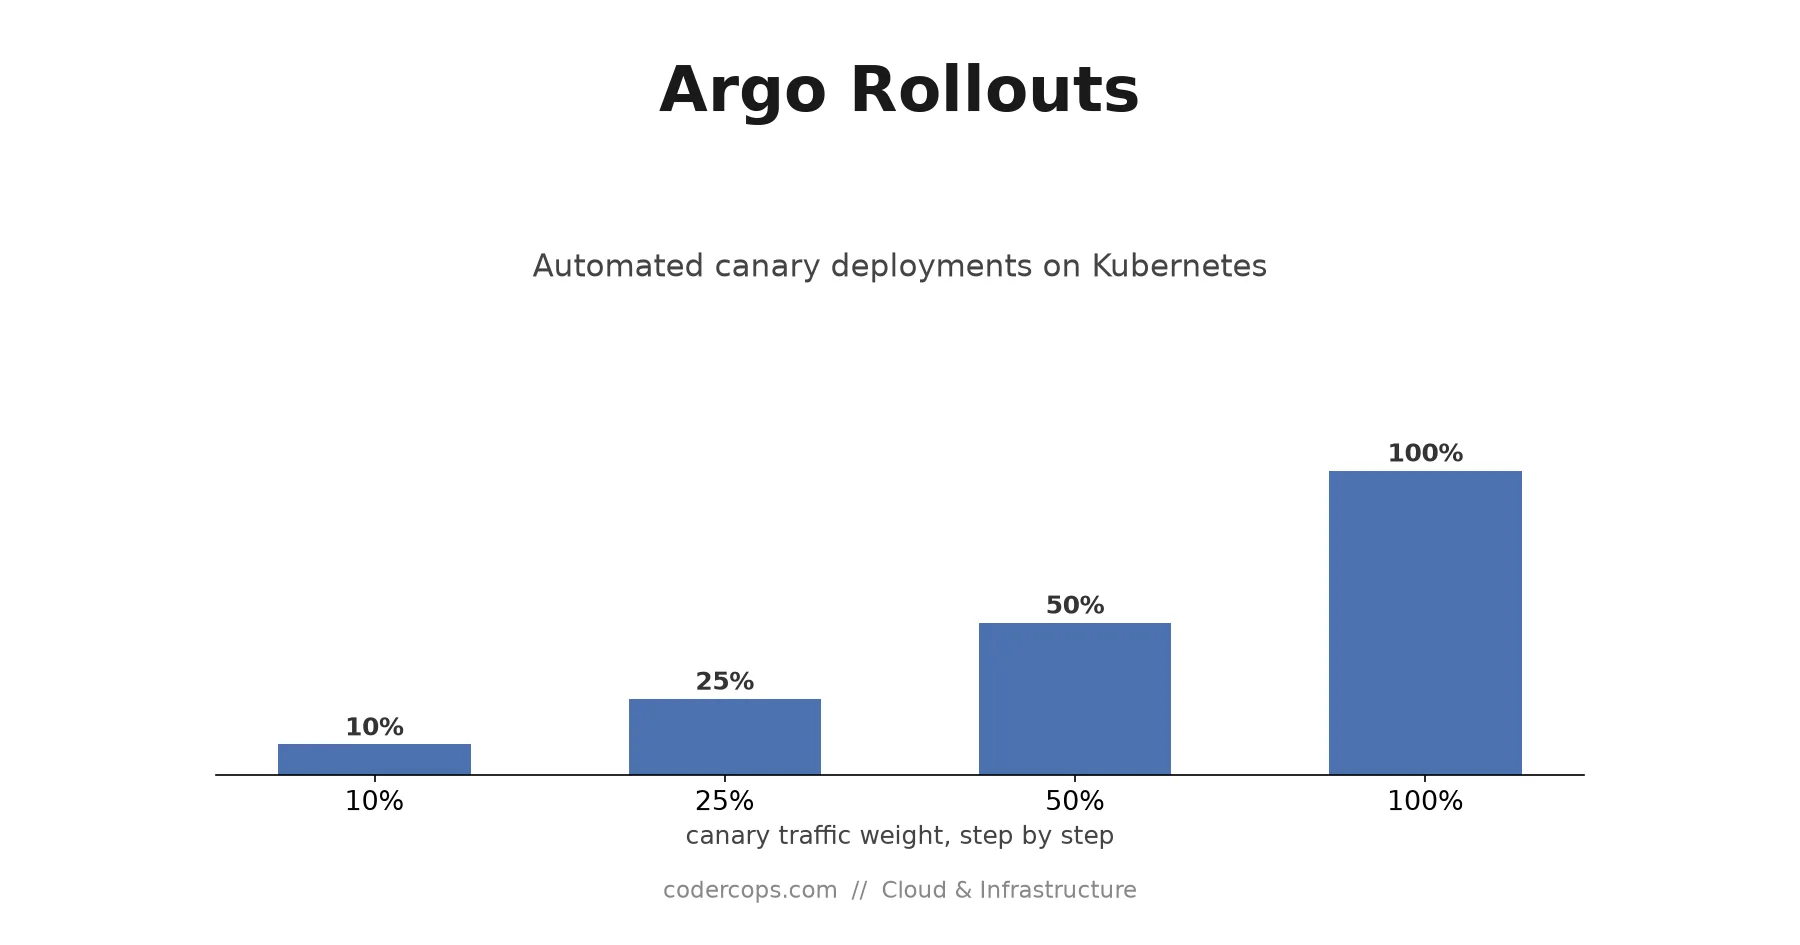
P.03Argo Rollouts replaces a Deployment with a controller that shifts traffic gradually and rolls back on bad metrics. Real manifests, plain Deployment to canary.
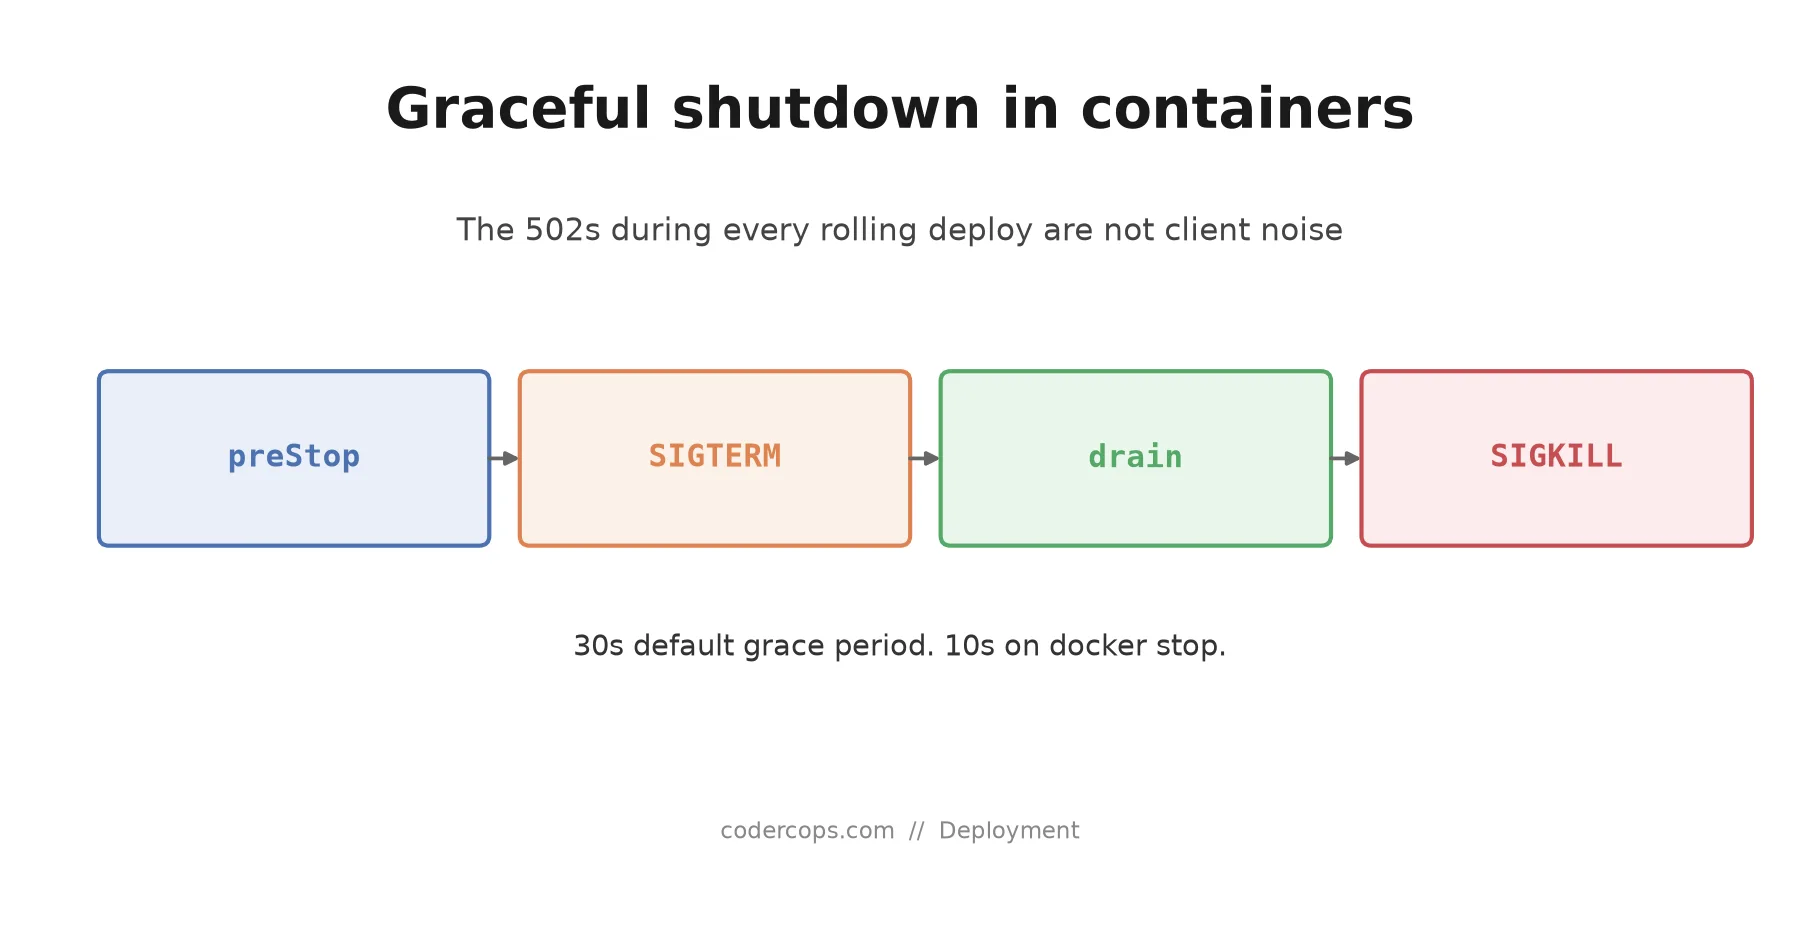
P.04Every rolling deploy drops a few requests and the errors look like client noise. The shutdown sequence, the race behind it, and the code that fixes it.
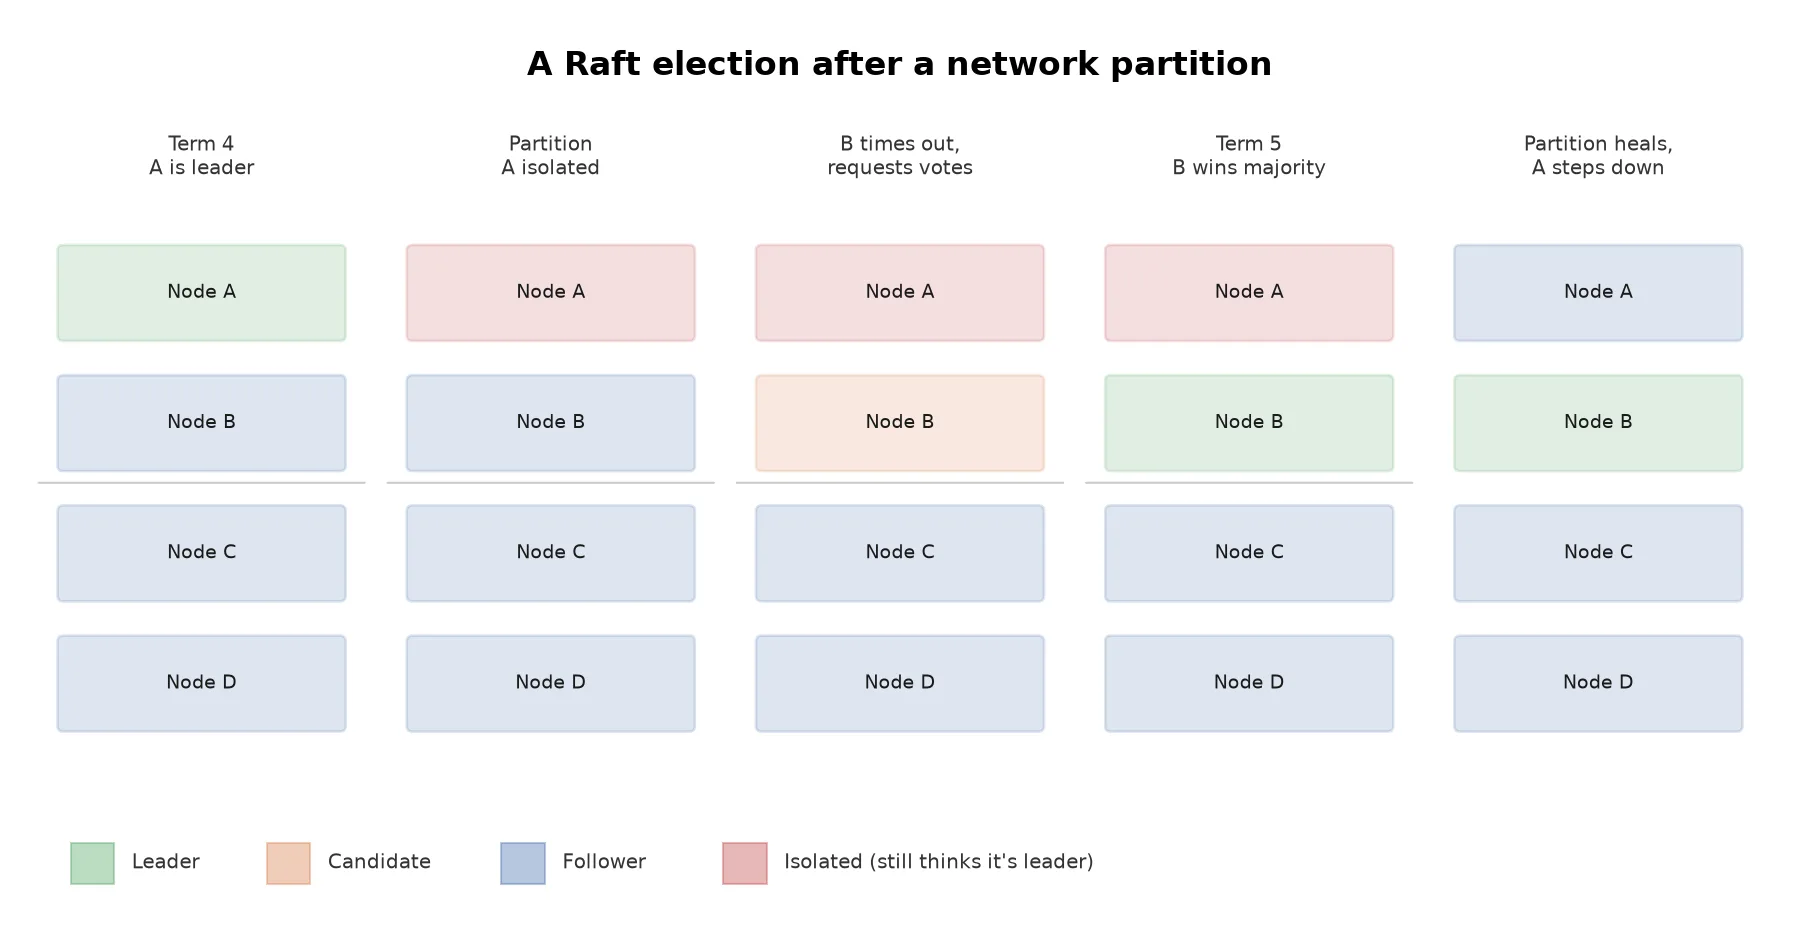
P.05Run three copies of a service and only one should do certain jobs. How leader election works, from Raft's term voting to the etcd lease pattern teams use.
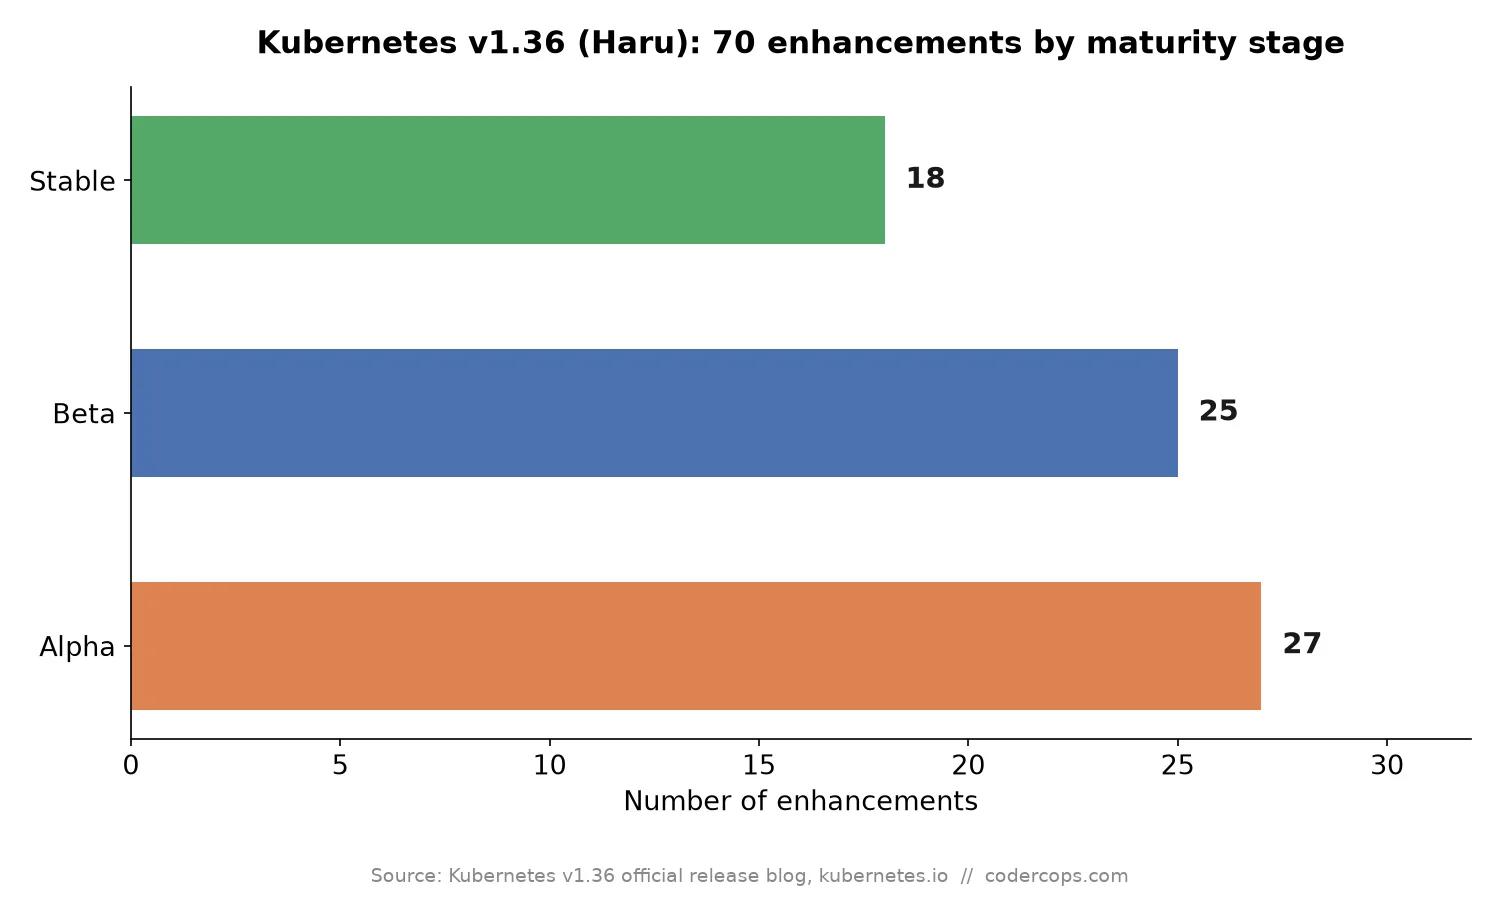
P.06Kubernetes 1.36 shipped 70 enhancements with no headline rewrite, just years of work reaching stable. What changes for platform teams, and what to skip.
HPA scales on CPU and memory. But most production workloads don't scale well on those signals. KEDA, VPA, and Goldilocks fill the gaps that HPA leaves open.
Service meshes promise secure, observable microservice communication. But most teams that adopt one do so before they need it. Here is how to decide, and what each option actually costs you.
Deploy WebAssembly workloads on Kubernetes using SpinKube: cluster setup, Spin deployment, autoscaling, monitoring, and a production readiness checklist.
Everyone says go cloud-native. But what does that actually mean in 2026? We break down microservices, serverless, and containers — and why most teams should start simpler than they think.