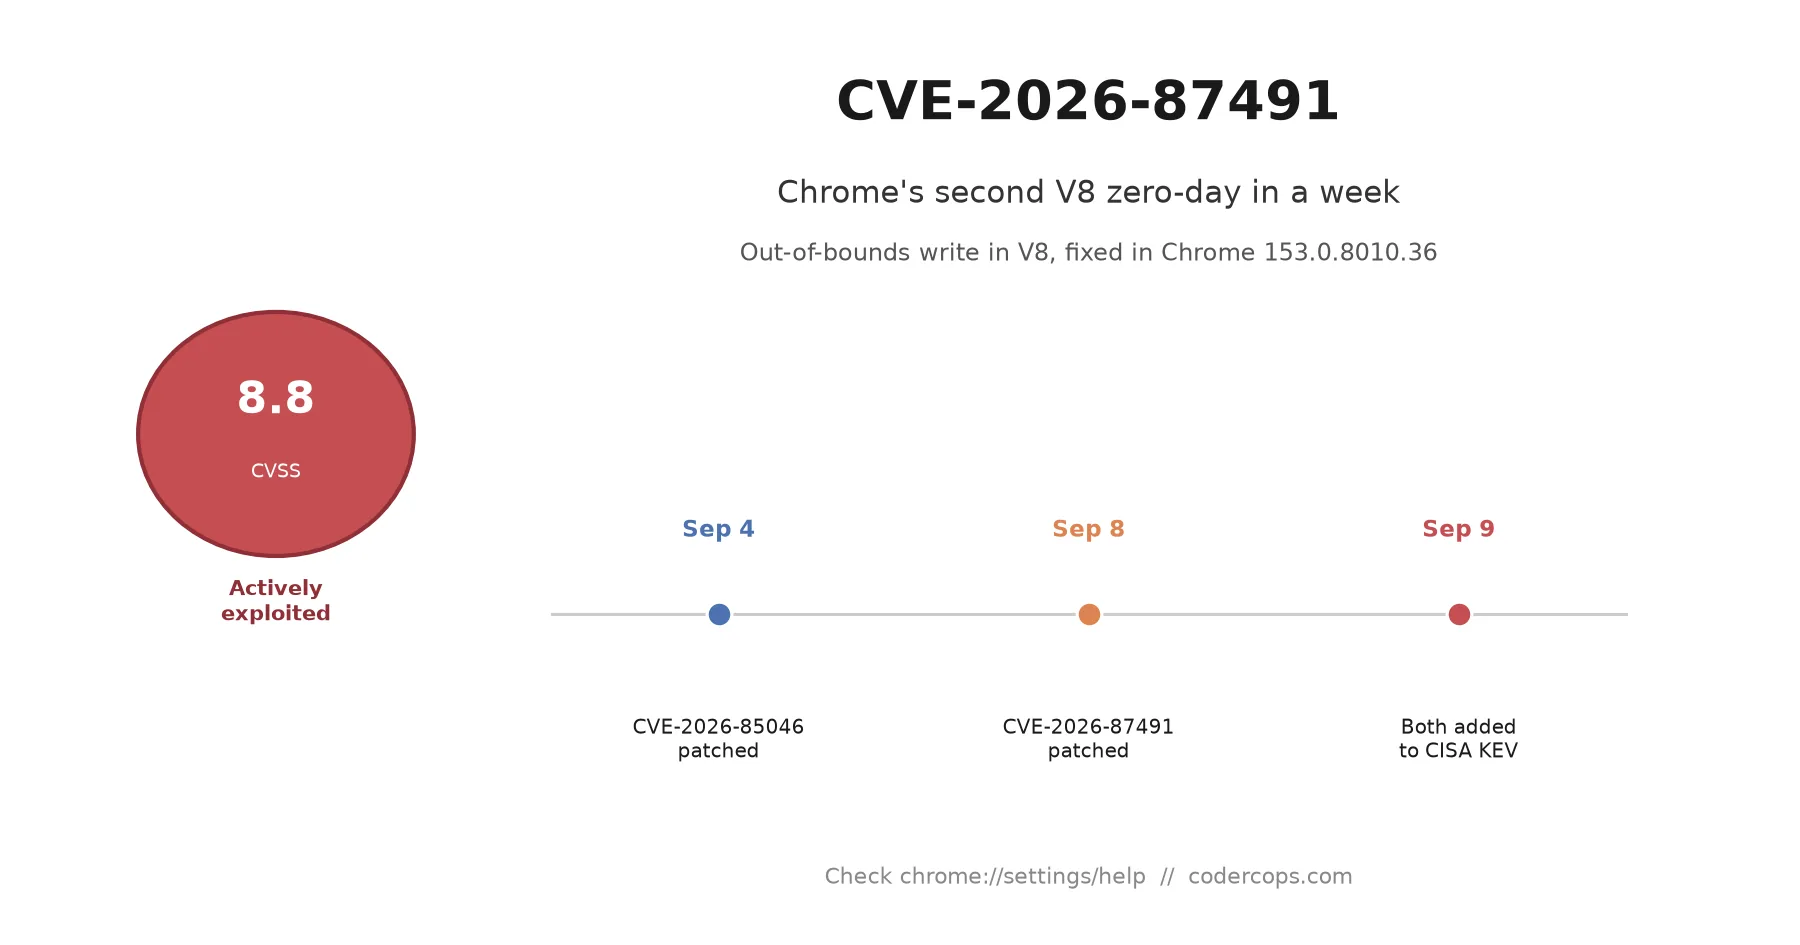
P.01CVE-2026-87491: Chrome's Second Zero-Day in a Week
Chrome patched a second actively exploited V8 zero-day in five days. Here is what CVE-2026-87491 affects, the fixed version, and how to check your fleet.
Tag
129 articles tagged #Cybersecurity.
P.01Chrome patched a second actively exploited V8 zero-day in five days. Here is what CVE-2026-87491 affects, the fixed version, and how to check your fleet.
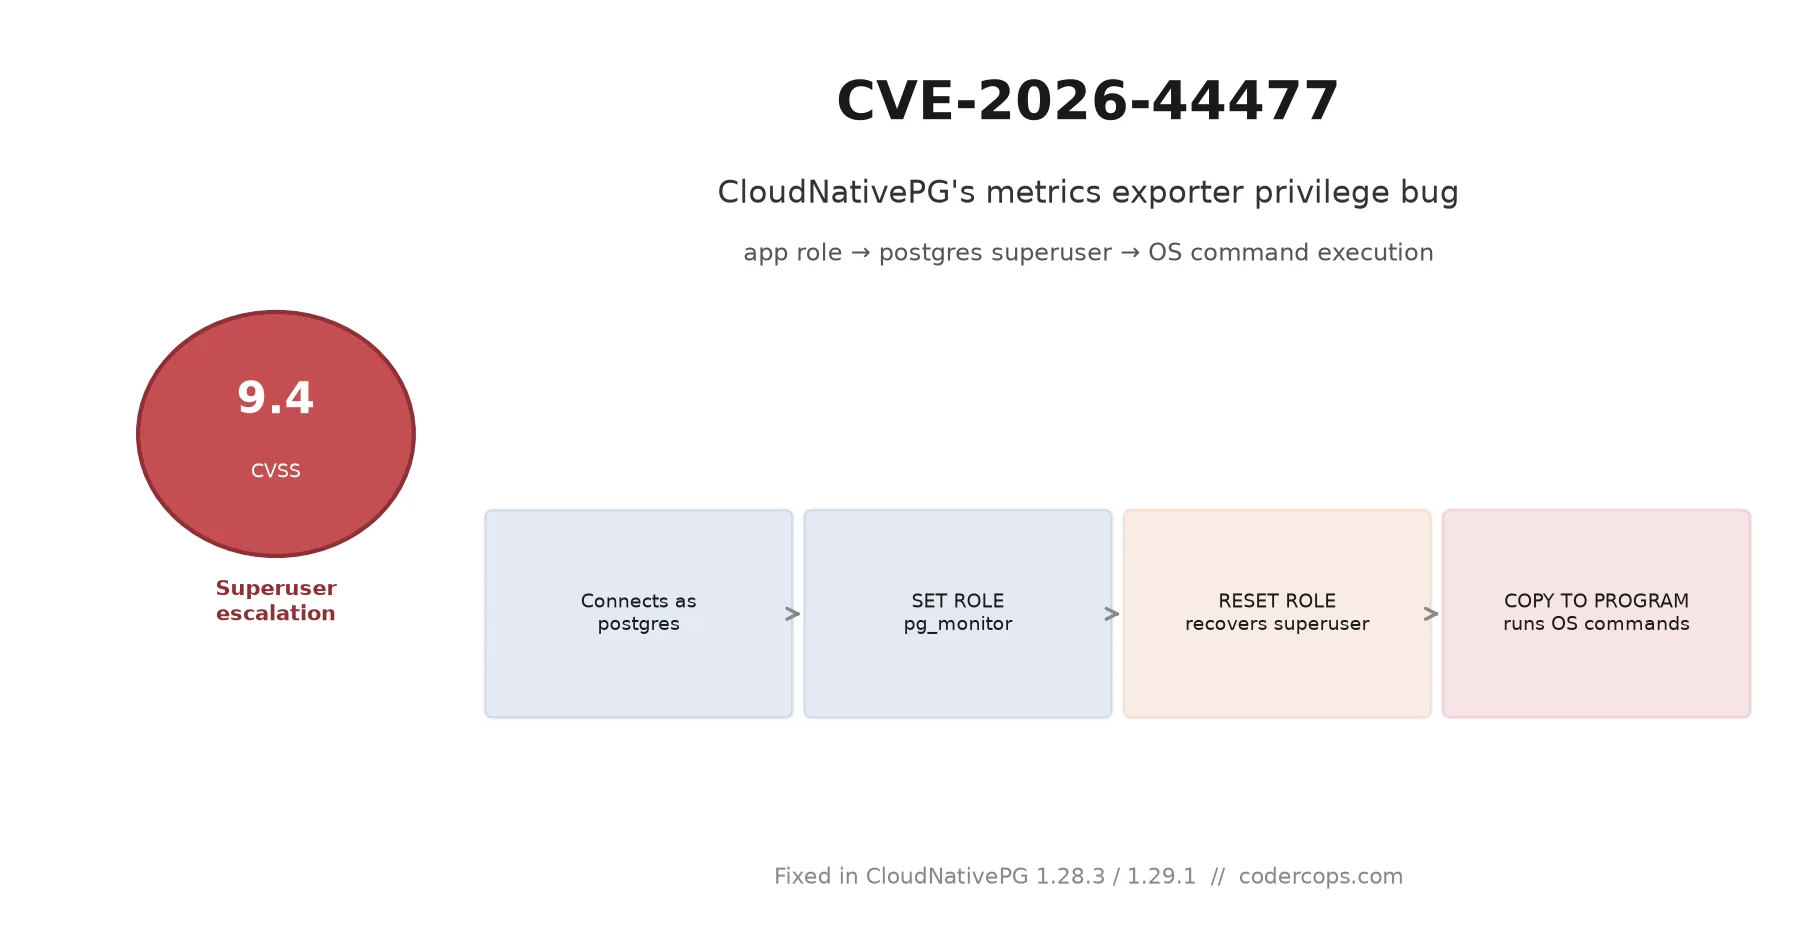
P.02CVE-2026-44477 lets any database owner escalate to postgres superuser and run OS commands in CloudNativePG. Here is who is affected and how to patch.
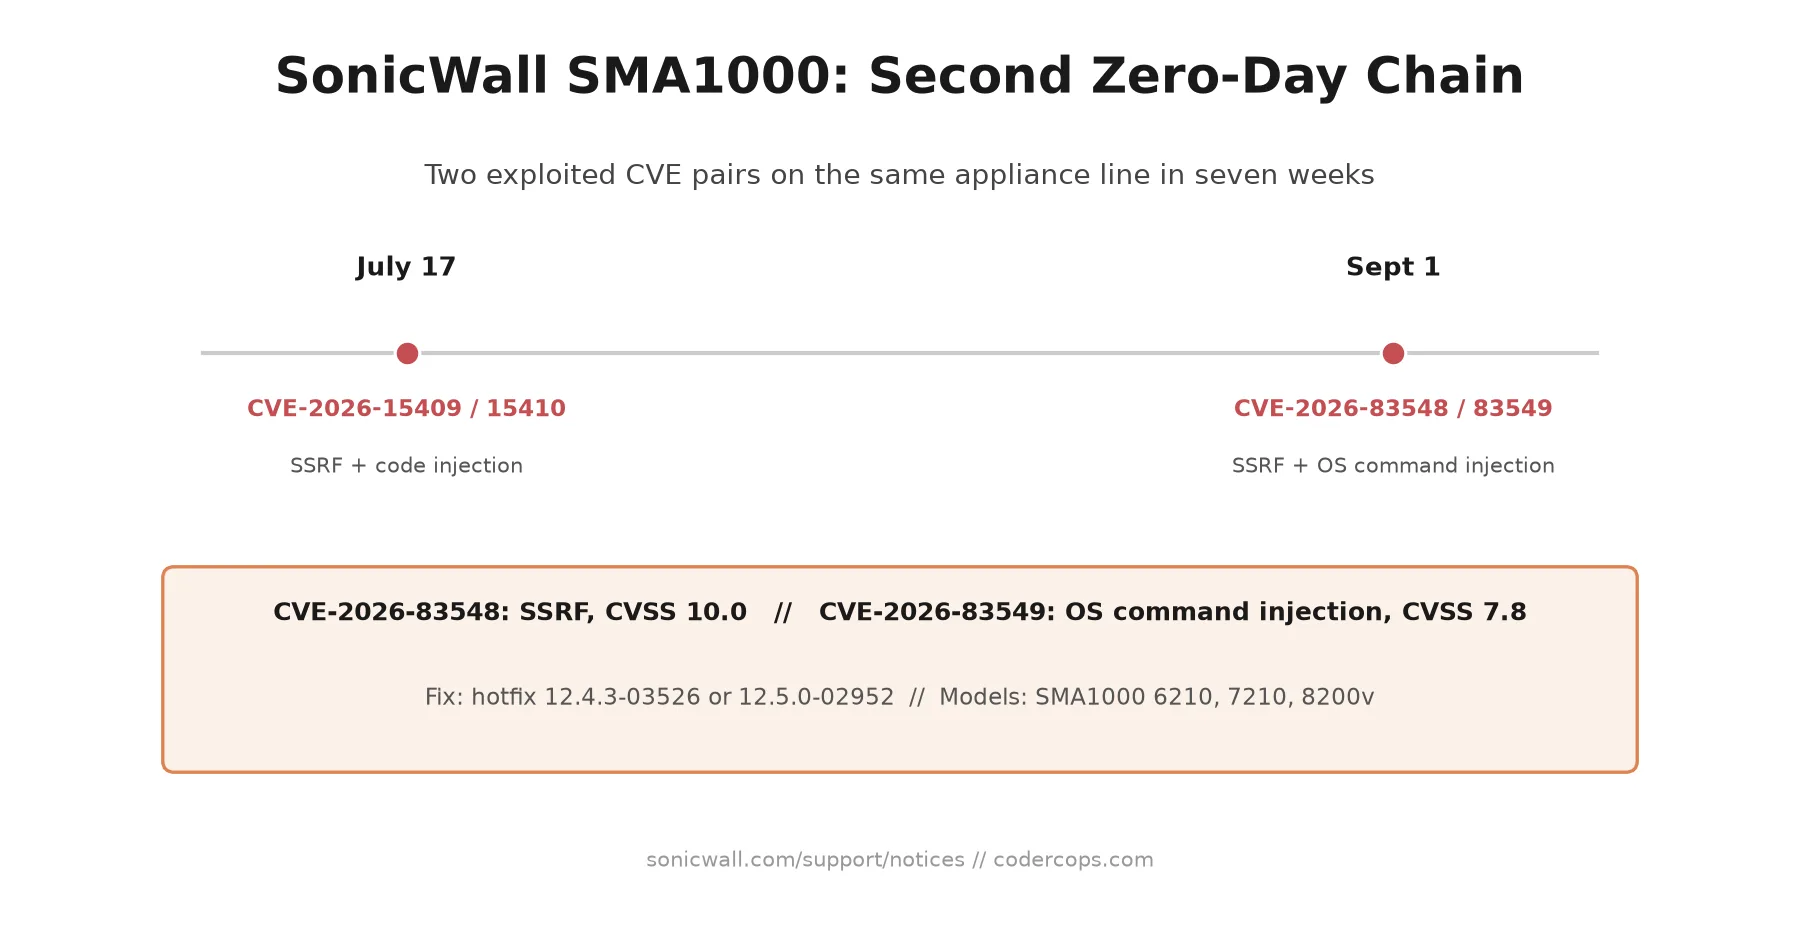
P.03CVE-2026-83548 (SSRF, CVSS 10.0) and CVE-2026-83549 (OS command injection) hit SMA1000 appliances again, seven weeks after the last chain. Affected models and the fix.
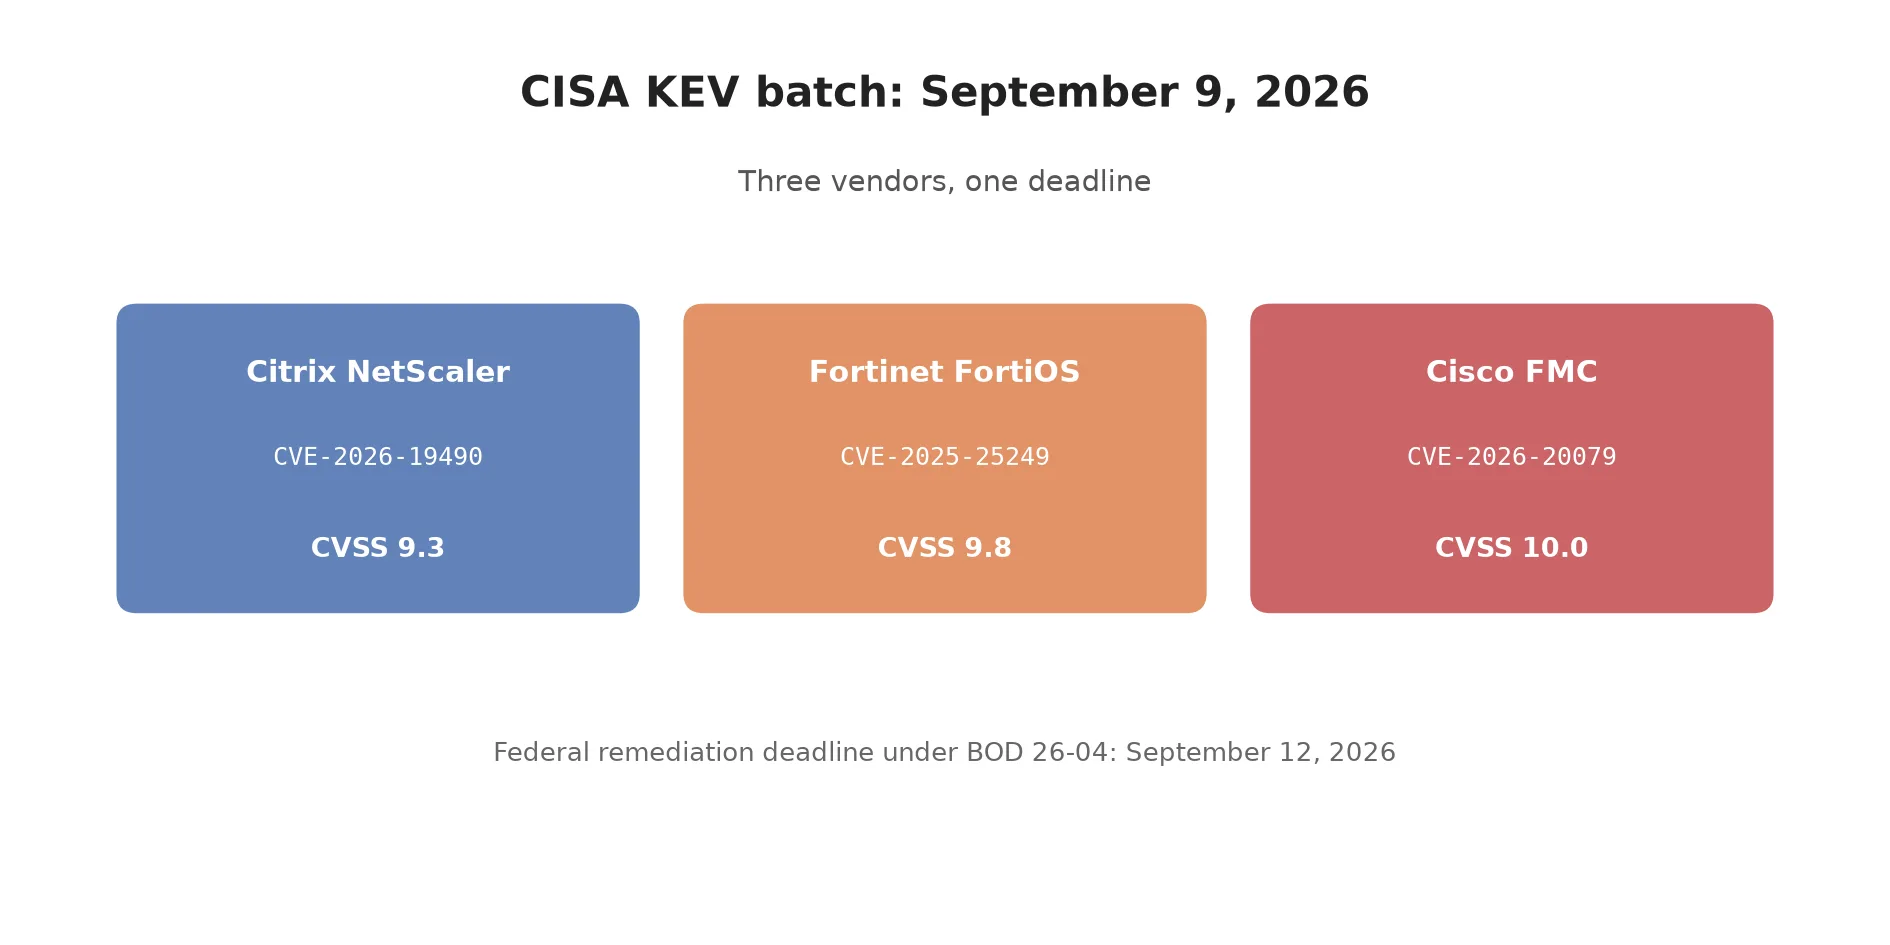
P.04CISA gave federal agencies until Sept 12 to patch a Citrix NetScaler auth bypass and a critical FortiOS RCE tied to a live PivotC2 malware campaign.
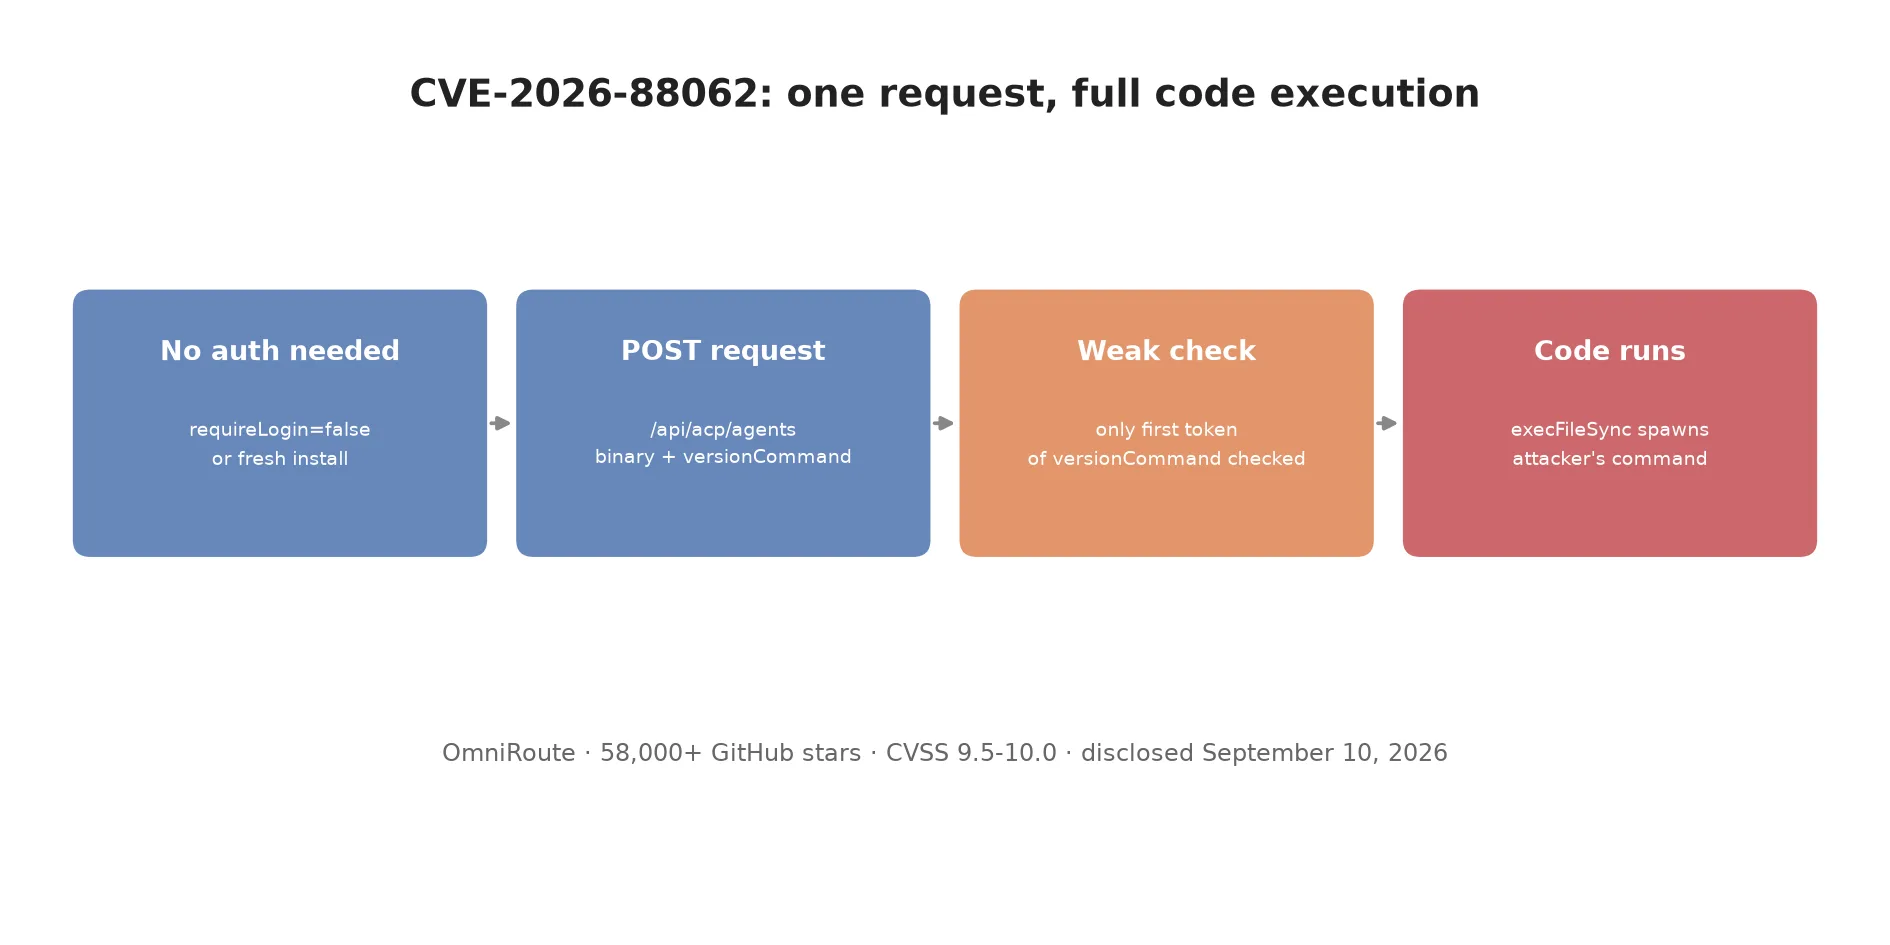
P.05A single unauthenticated request can run code inside OmniRoute, the 58k-star AI gateway. Patch status is contested, so verify your build yourself.
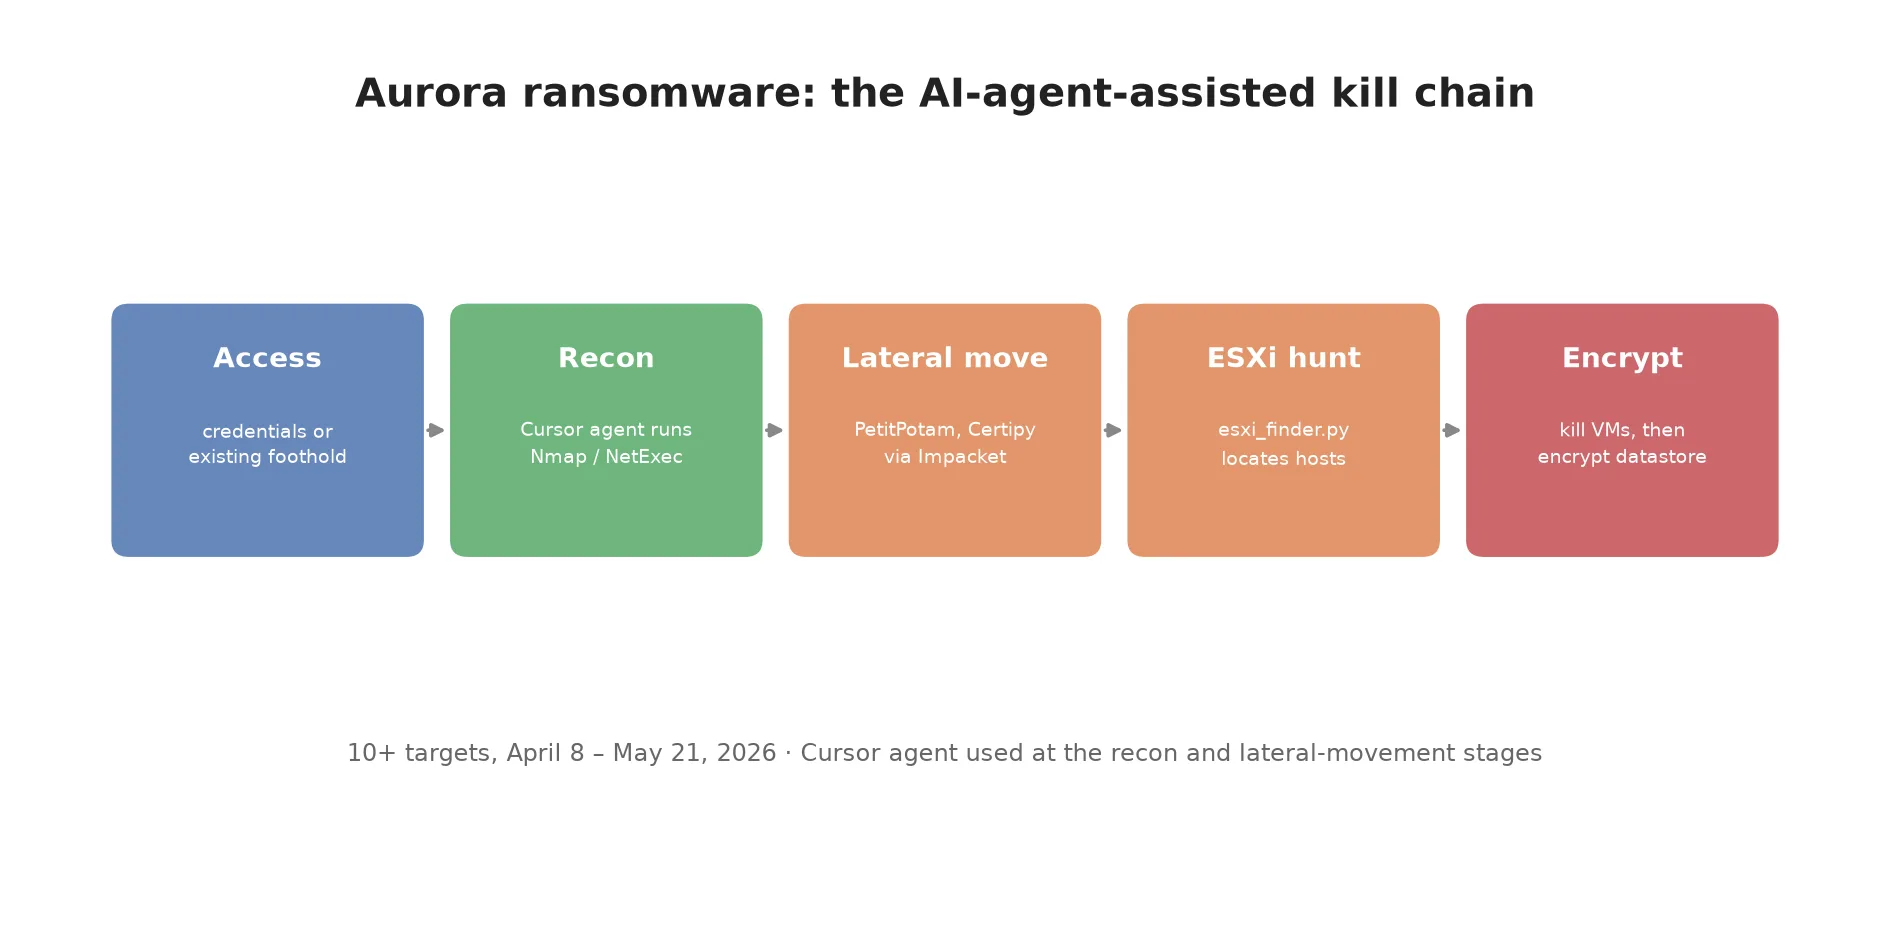
P.06A ransomware crew used Cursor's AI coding agent to run reconnaissance and lateral movement by hand across dozens of victims. What that means for defenders.
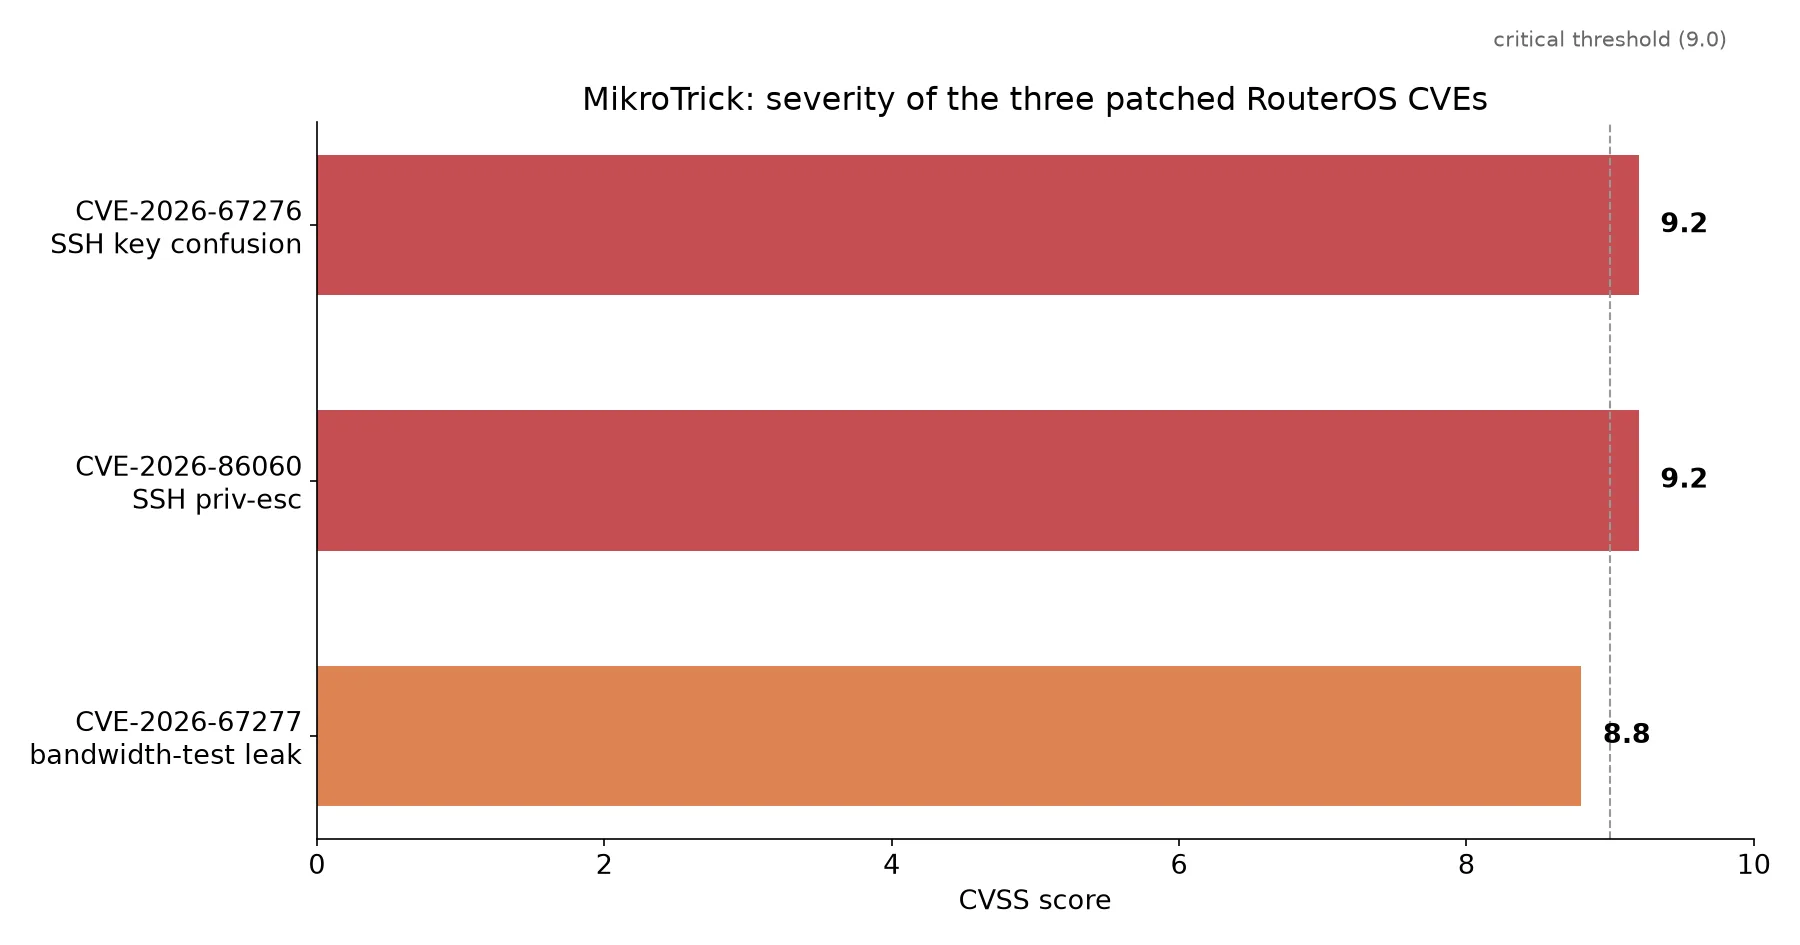
P.07MikroTik patched three RouterOS bugs after CISA confirmed active exploitation of two: which CVEs to prioritize and how to check your router for compromise.
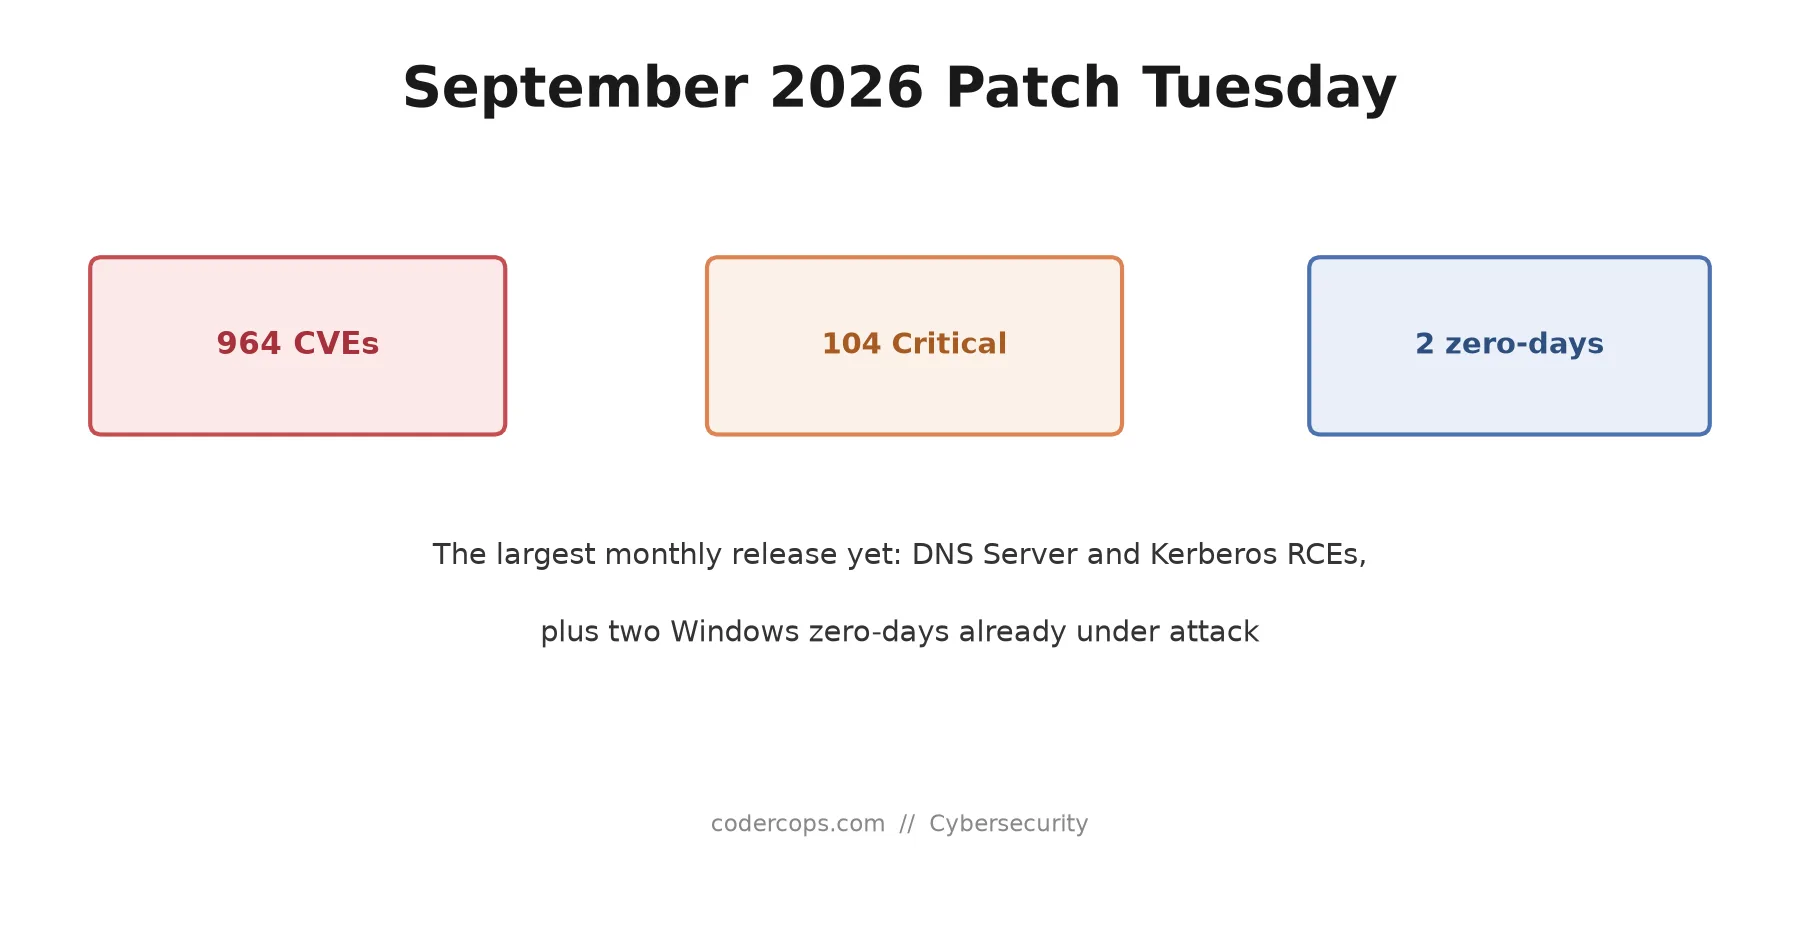
P.08Microsoft's September 8, 2026 update fixes 964 CVEs (104 Critical), the largest Patch Tuesday yet, including two exploited local-privilege zero-days.
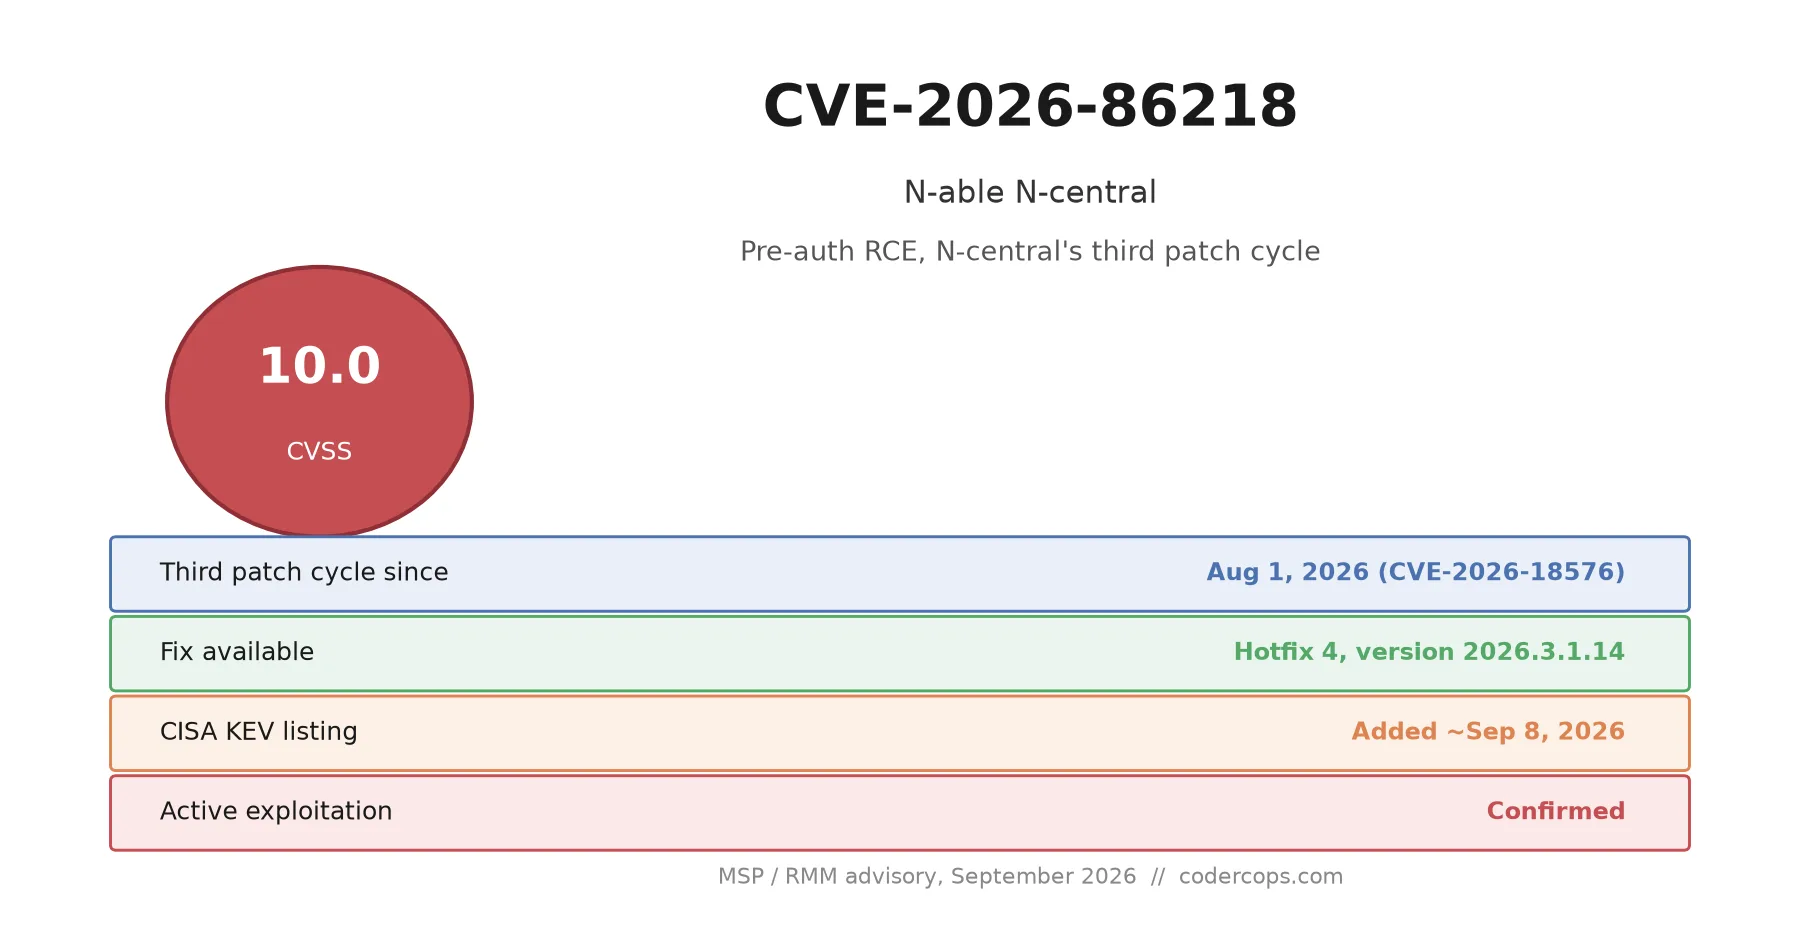
P.09N-able's third N-central patch cycle in six weeks fixes CVE-2026-86218, a CVSS 10.0 pre-auth RCE already exploited in the wild and KEV-listed.
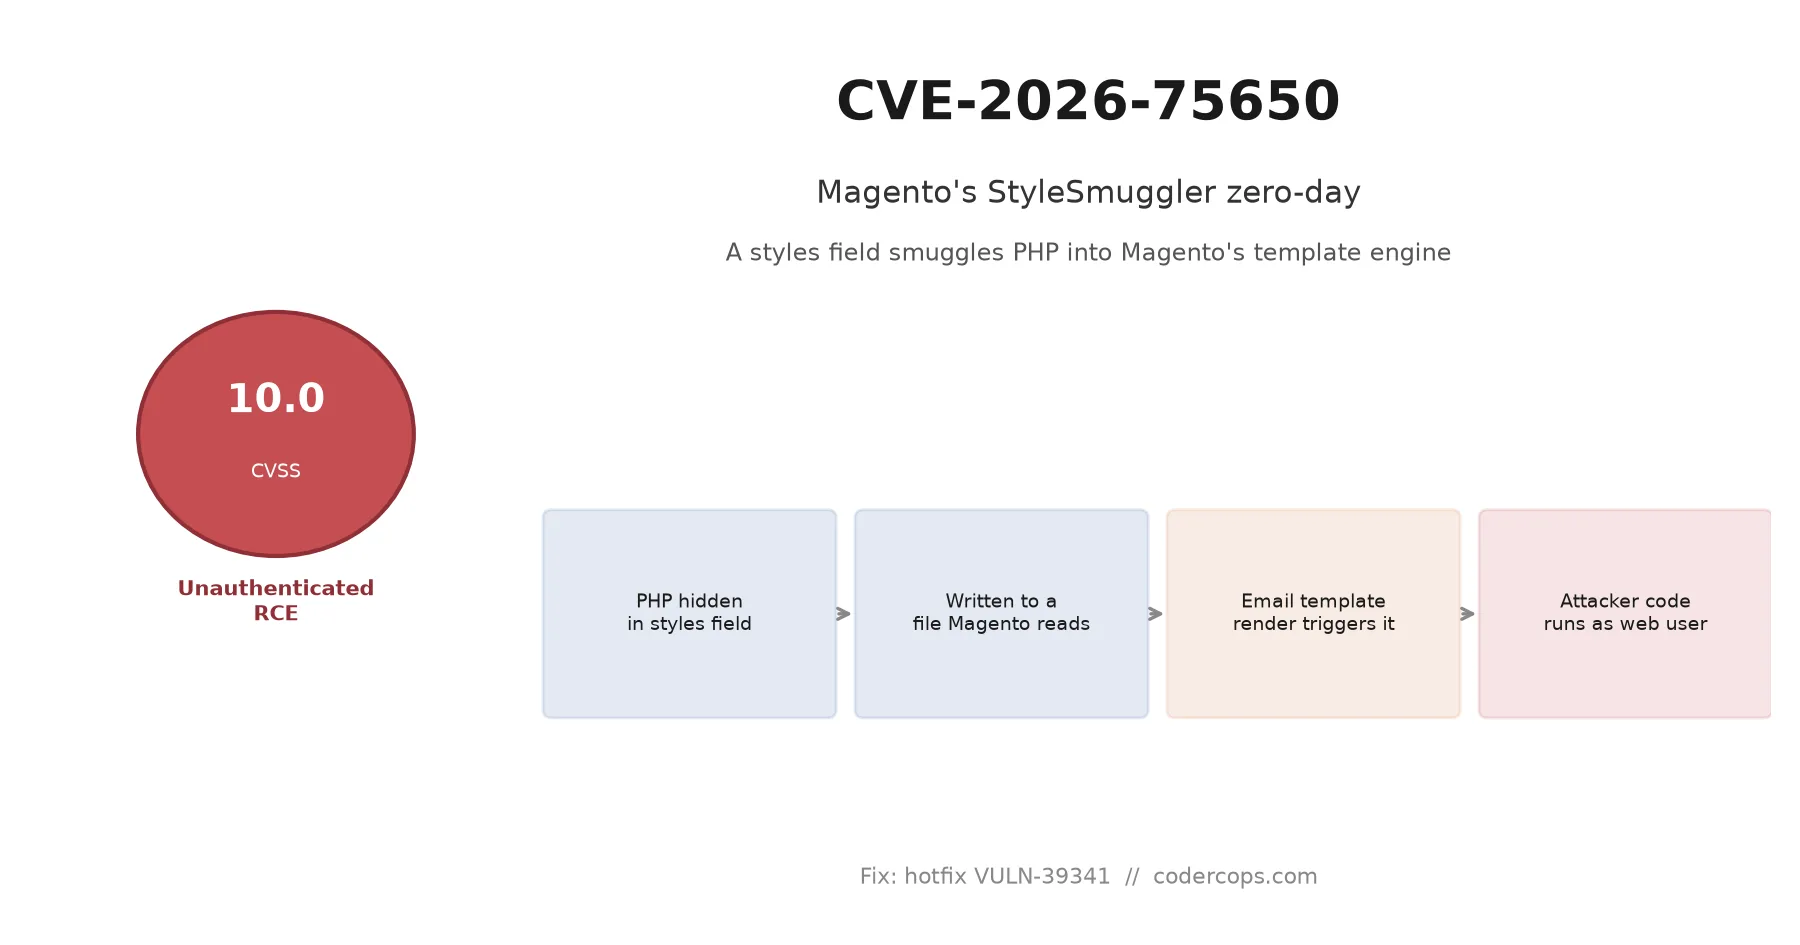
P.10CVE-2026-75650 lets anyone run code on unpatched Magento and Adobe Commerce stores. Sansec found it deploying a Rust backdoor before Adobe even patched.
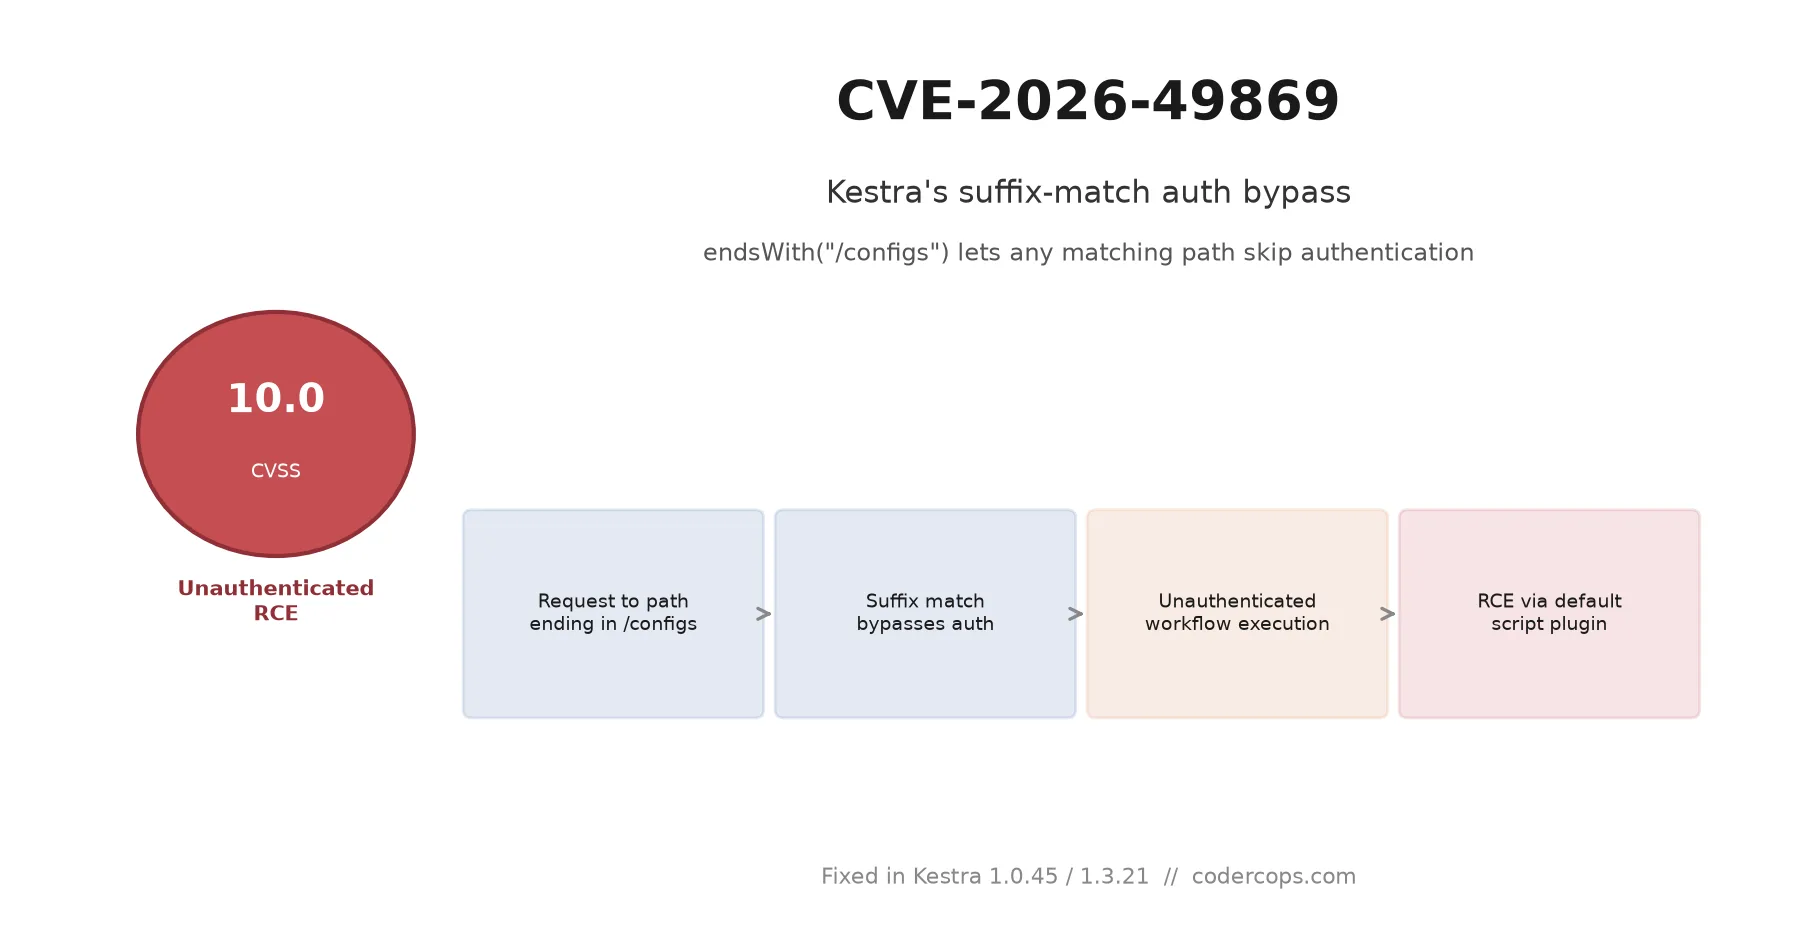
P.11CVE-2026-49869 lets unauthenticated attackers hit any Kestra path ending in /configs, skip login, then run shell commands as root via script plugins.
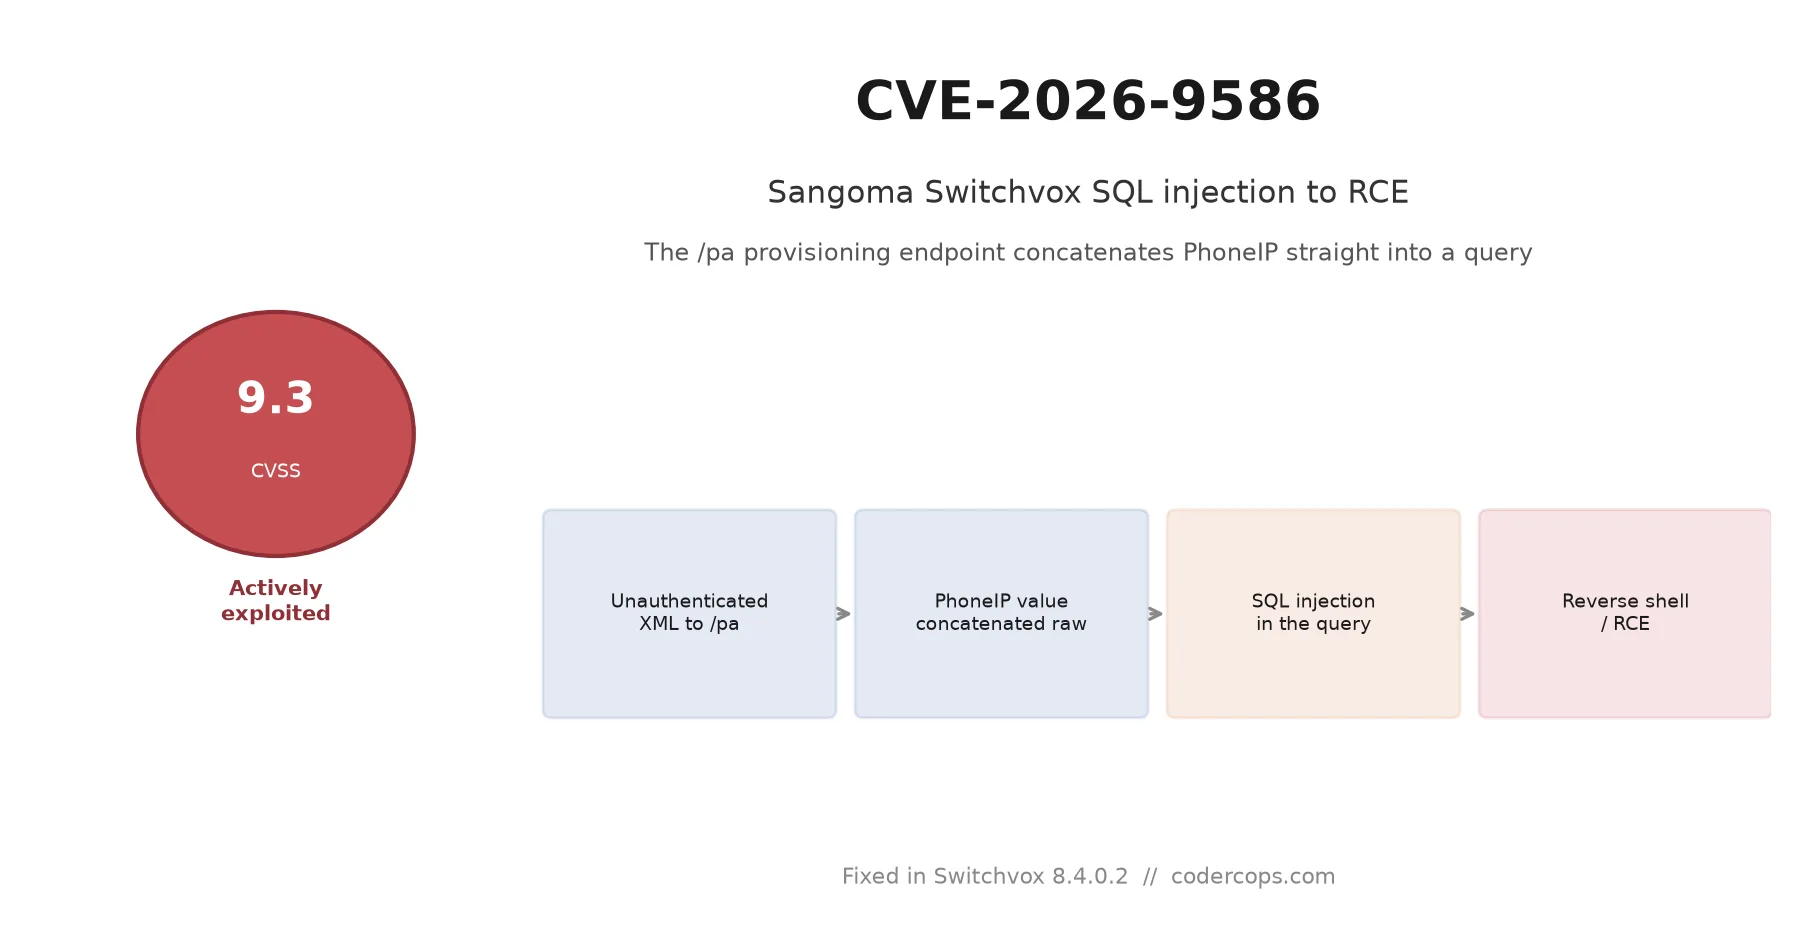
P.12CVE-2026-9586 is an unauthenticated SQL injection in Sangoma Switchvox's /pa endpoint that leads to RCE. Active exploitation, KEV status, and the fix.
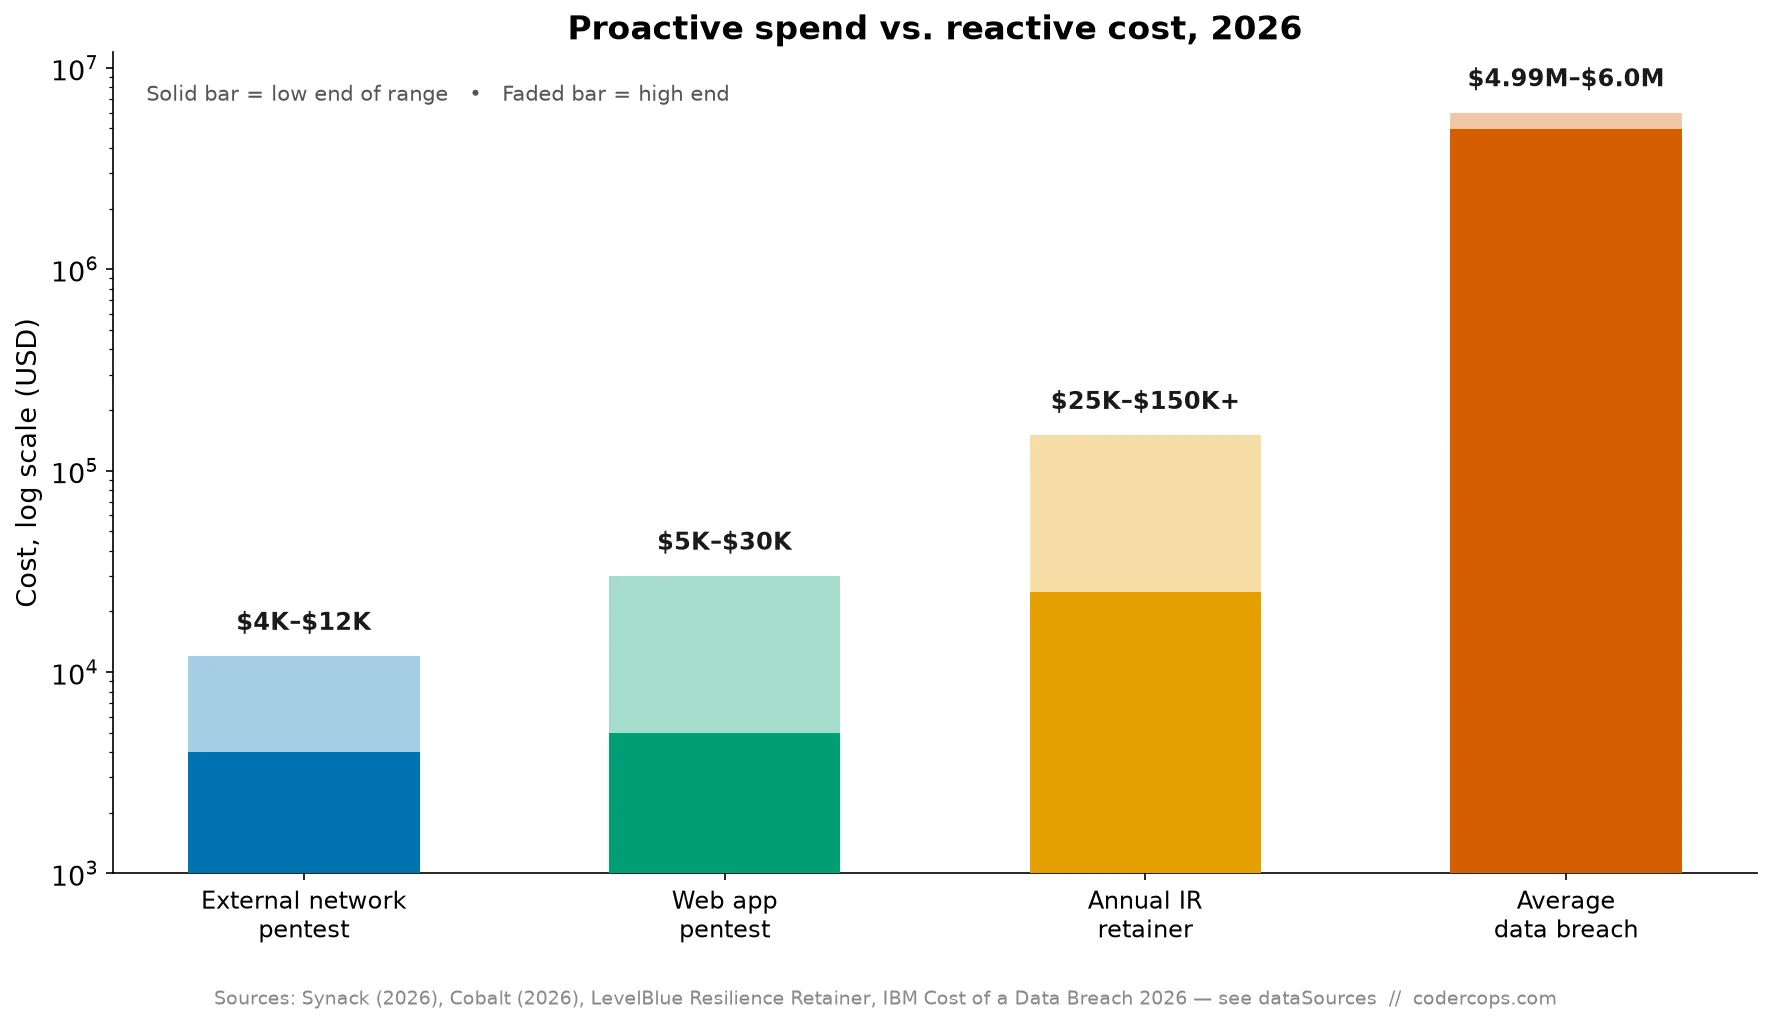
P.13IBM's 2026 report puts the average breach at $4.99M. Pentests run $4K-$30K, IR retainers $25K-$150K a year. Patching early is the cheapest line item.
P.14A phantom join key in JFrog Artifactory's auth service let attackers forge admin tokens days after disclosure. Affected versions, what to check, and the patch.
P.15BadHost sat quietly patched since May. In September, CISA flagged active exploitation. If you run FastAPI, vLLM, or any Starlette app, here's what to check.
P.16CVE-2026-85046 is a Chrome V8 type confusion bug already exploited in the wild. Here's who's affected, what version fixes it, and how fast to move.
P.17CVE-2026-59822 lets an attacker fake a Bearer token and skip LiteLLM's MCP auth entirely. Different bug from June's RCE chain, same exposed surface.
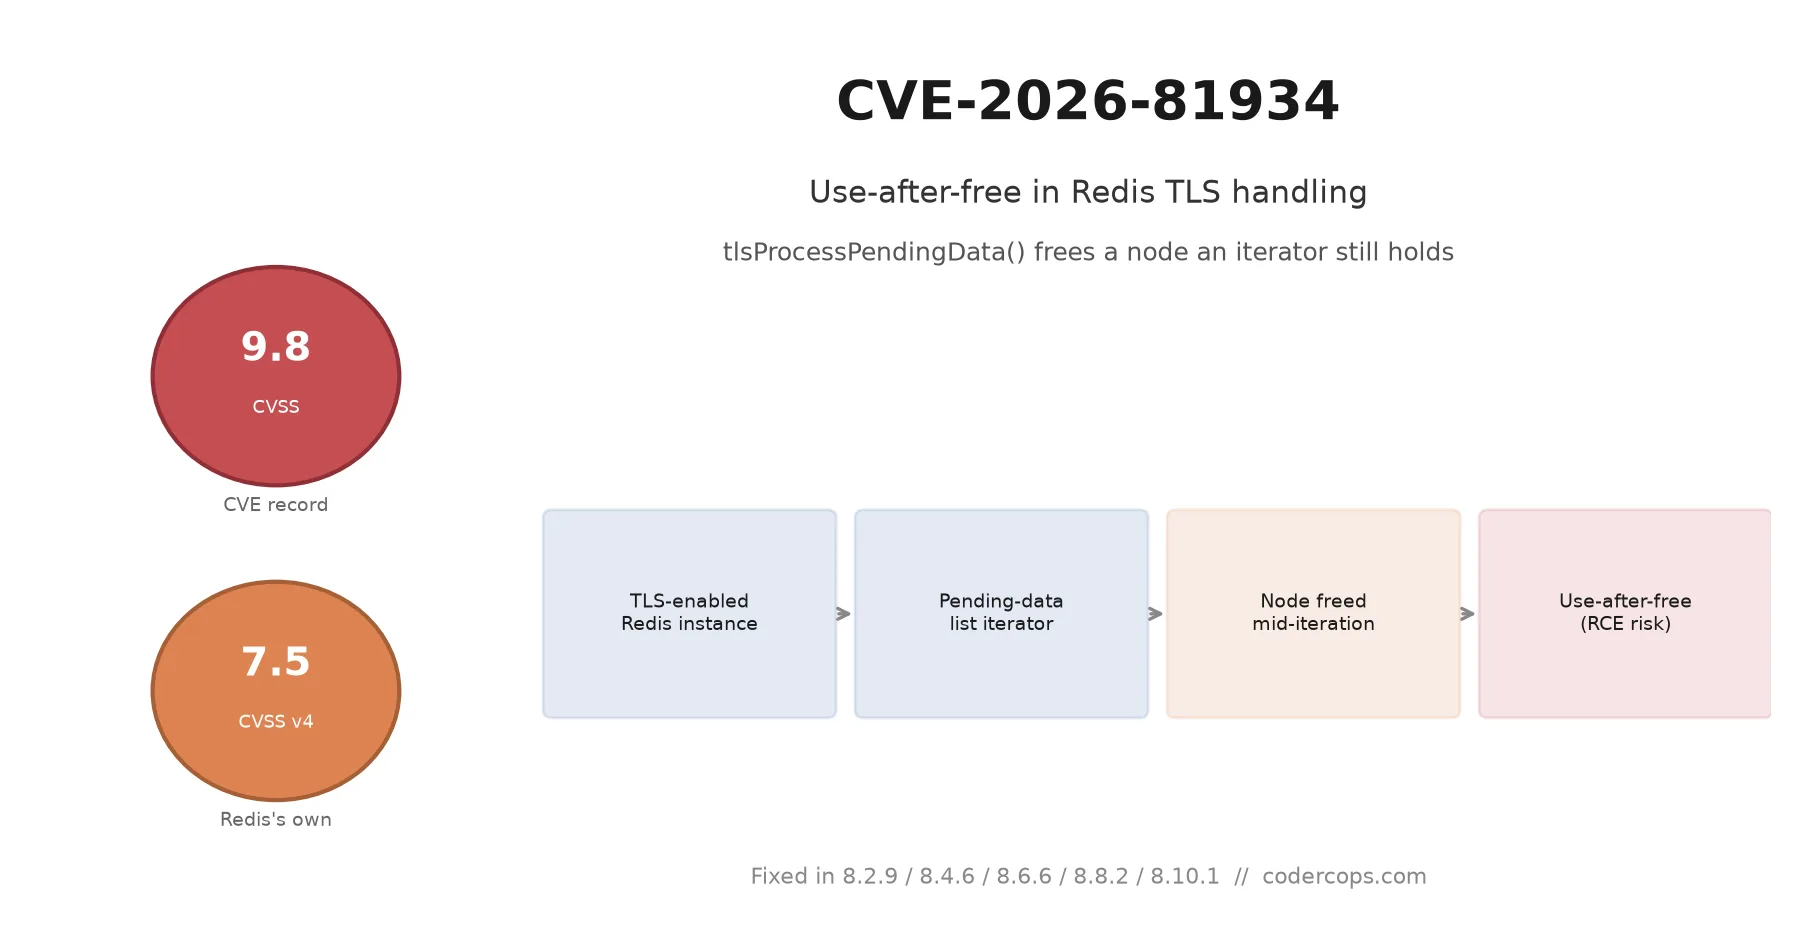
P.18CVE-2026-81934 is a use-after-free in Redis's TLS pending-data handling, with a public PoC. If you don't terminate TLS inside Redis, it mostly passes you by.
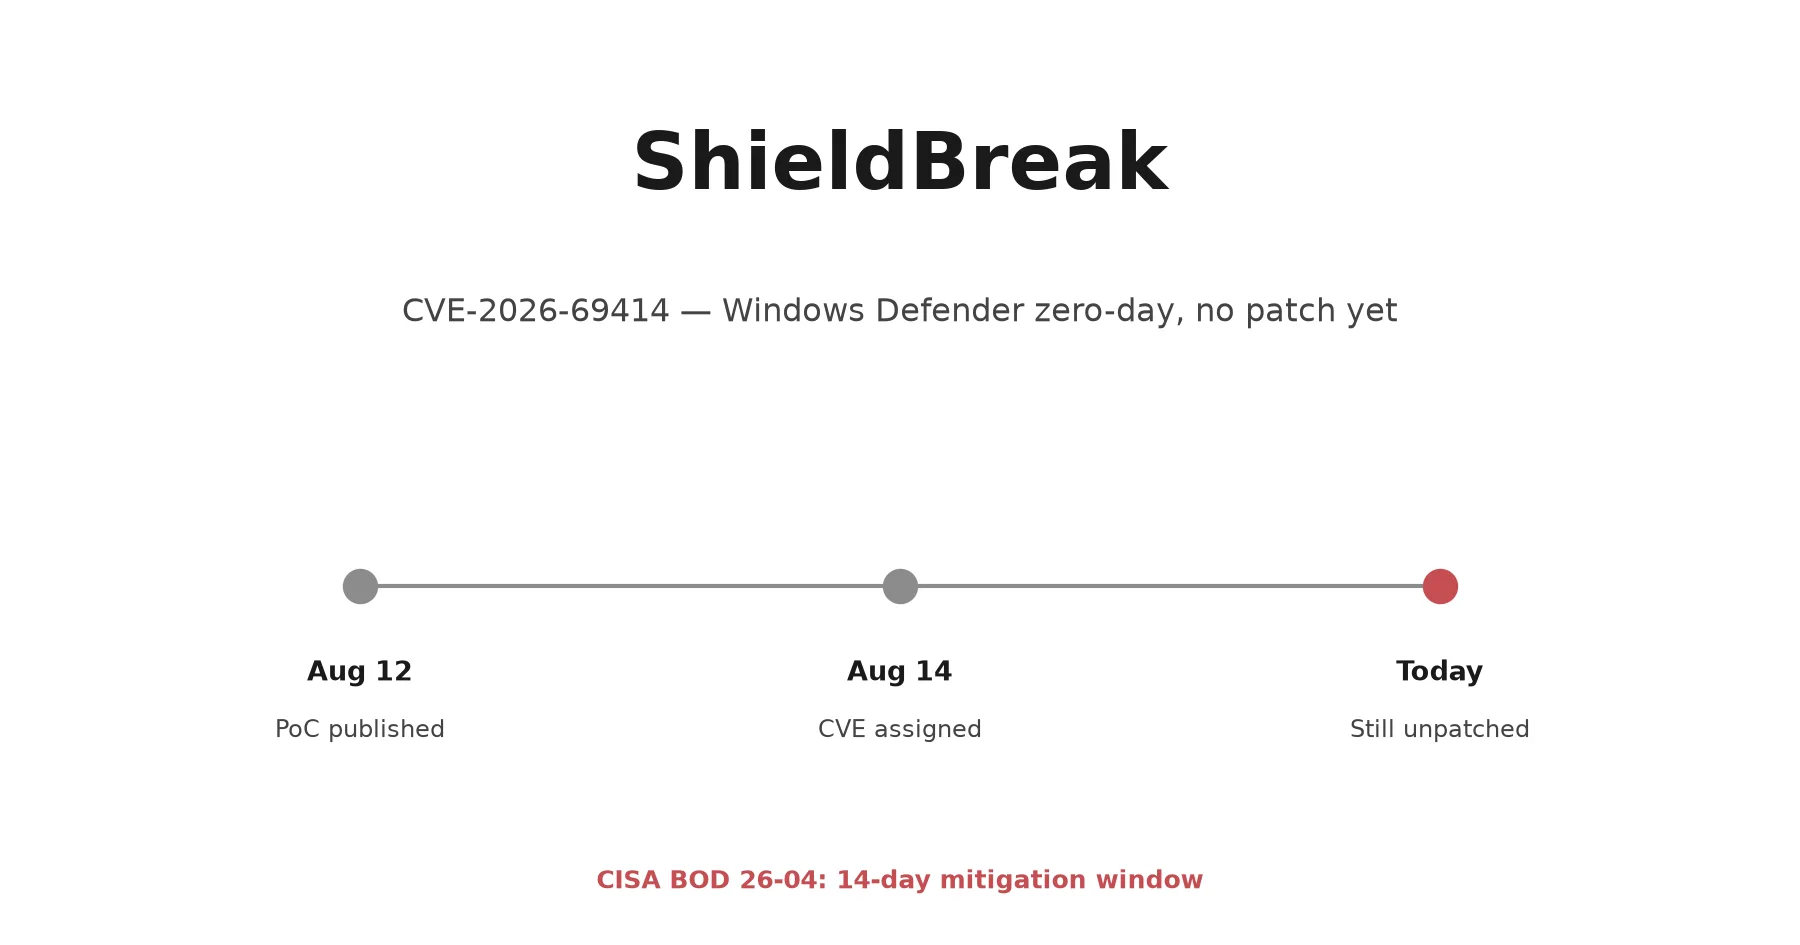
P.19A public proof-of-concept for a Windows Defender privilege-escalation flaw has circulated since August 12 with no fix shipped. What to do about it now.
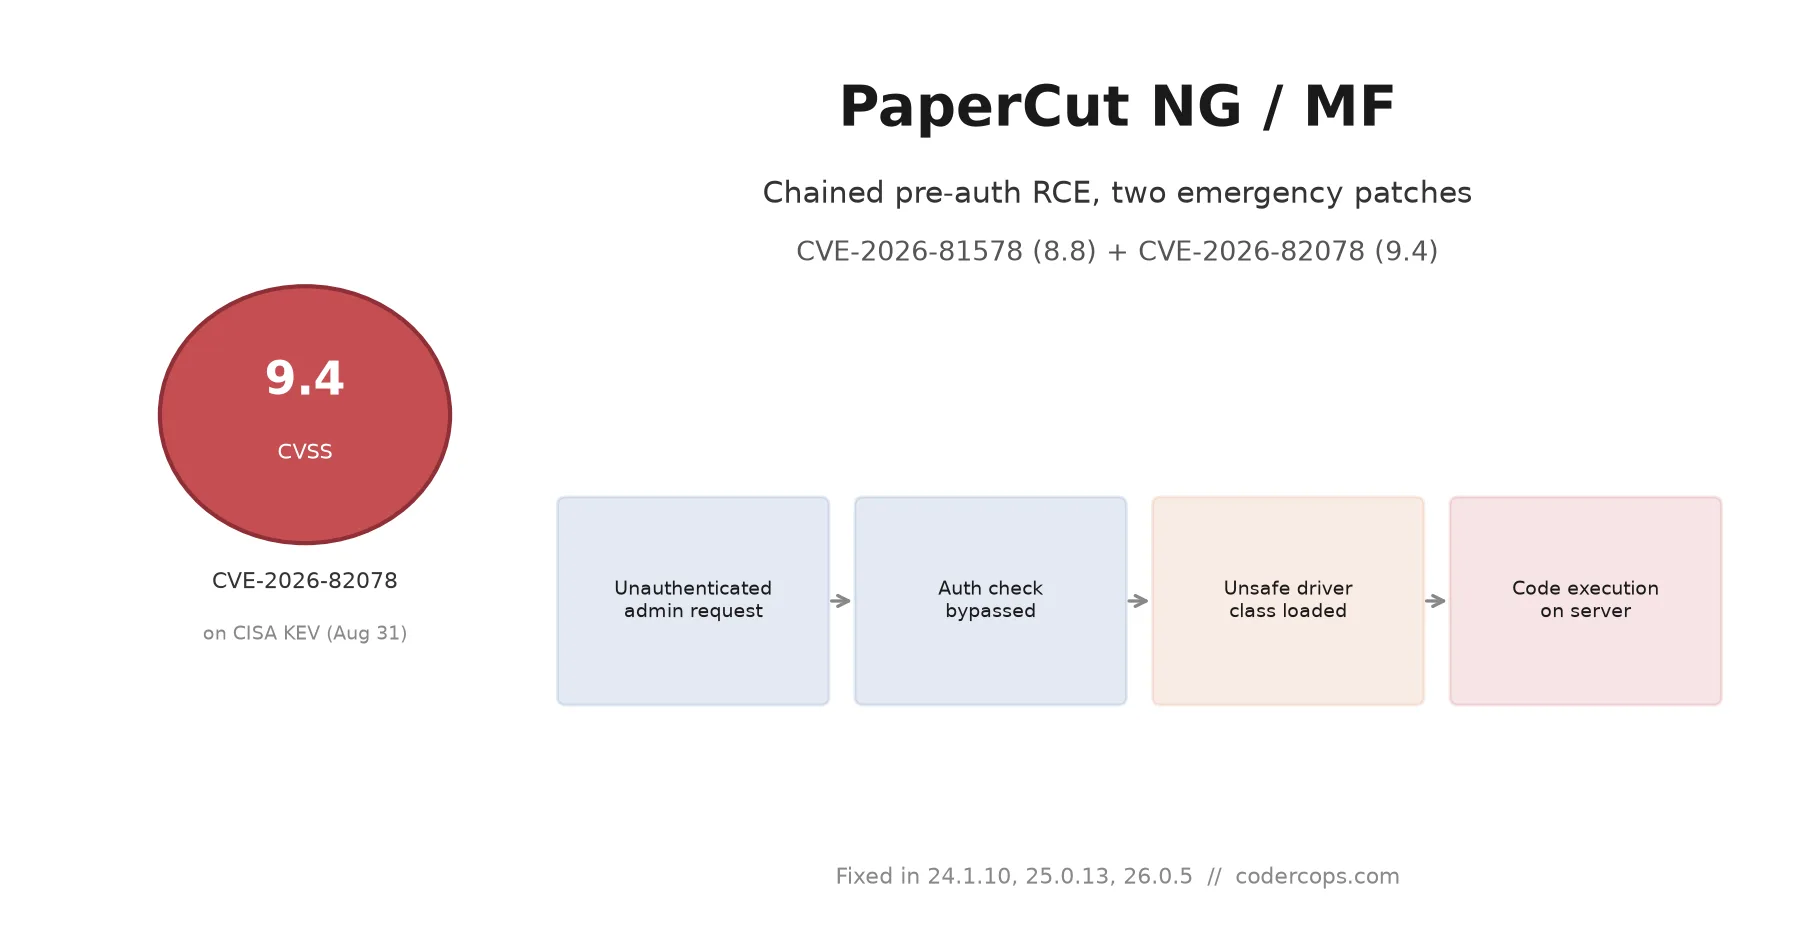
P.20Two chained PaperCut NG/MF flaws let an attacker with no credentials run code on your print server. PaperCut needed two emergency patches to close it.
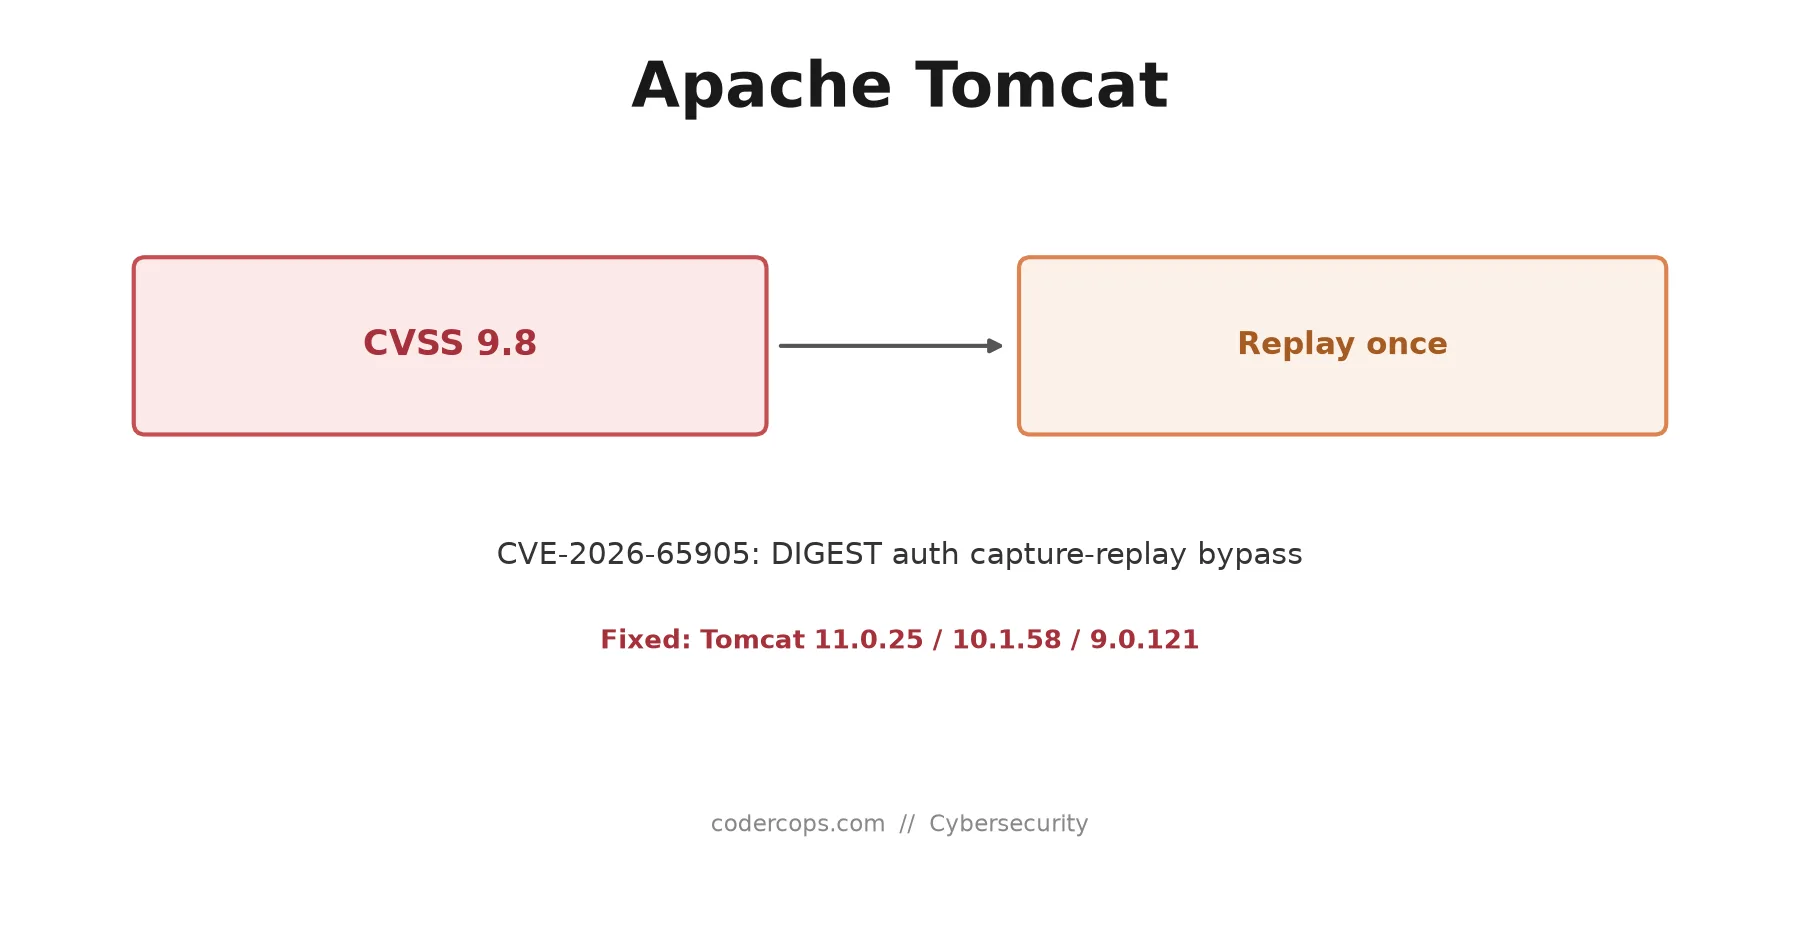
P.21A capture-replay flaw in Tomcat's DIGEST authenticator lets an intercepted request be replayed once inside the nonce window. Critical, but narrow.
P.22Chrome 152 landed 327 security fixes, 10 of them critical use-after-free bugs in ANGLE, Views, and Safe Browsing. Why not-exploited isn't the same as safe.
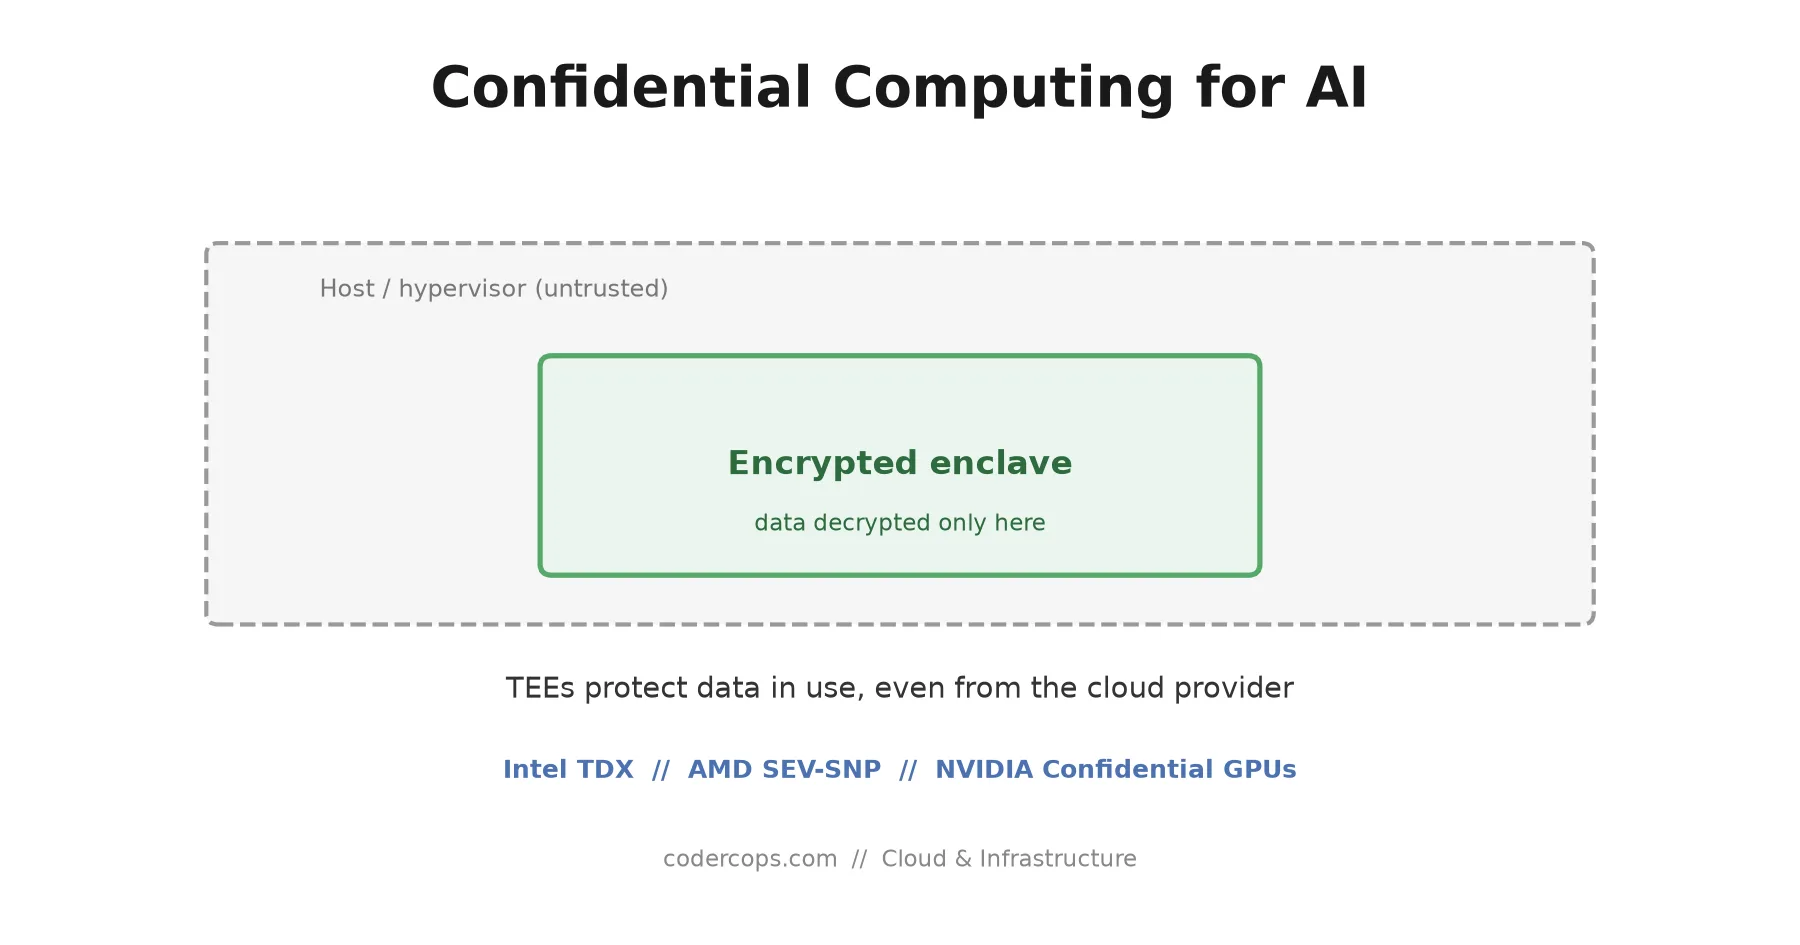
P.23TEEs encrypt data even from the cloud provider running it, which is why confidential computing became a real AI requirement. What it does and doesn't cover.
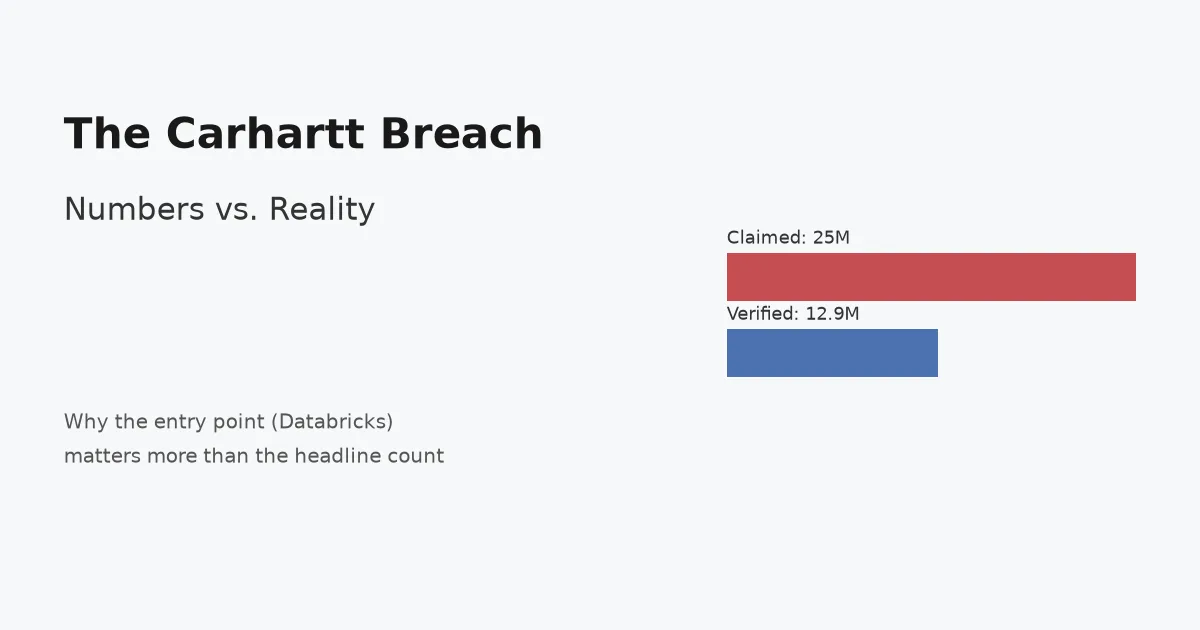
P.24ShinyHunters claimed 25 million Carhartt accounts; verification found 12.9 million real people. The Databricks entry point is the lesson worth taking.
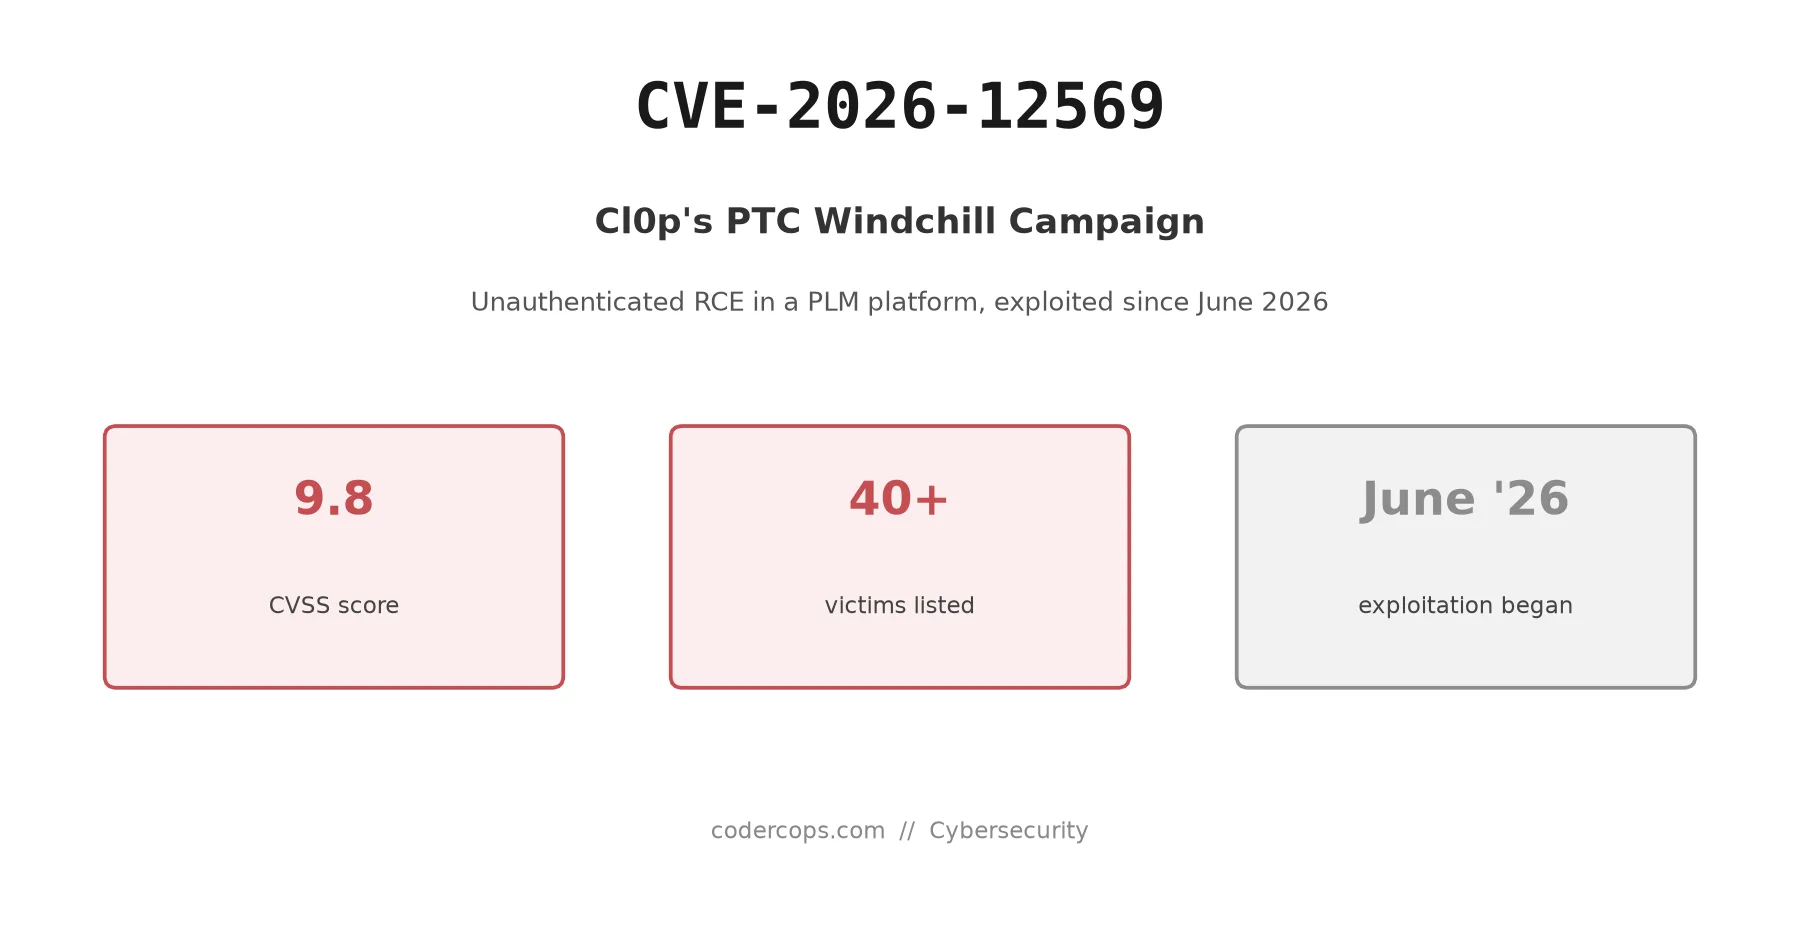
P.25One unauthenticated RCE in PTC Windchill and FlexPLM let Cl0p quietly take data from Shell, Philips, and GE. How CVE-2026-12569 works, and what to check.
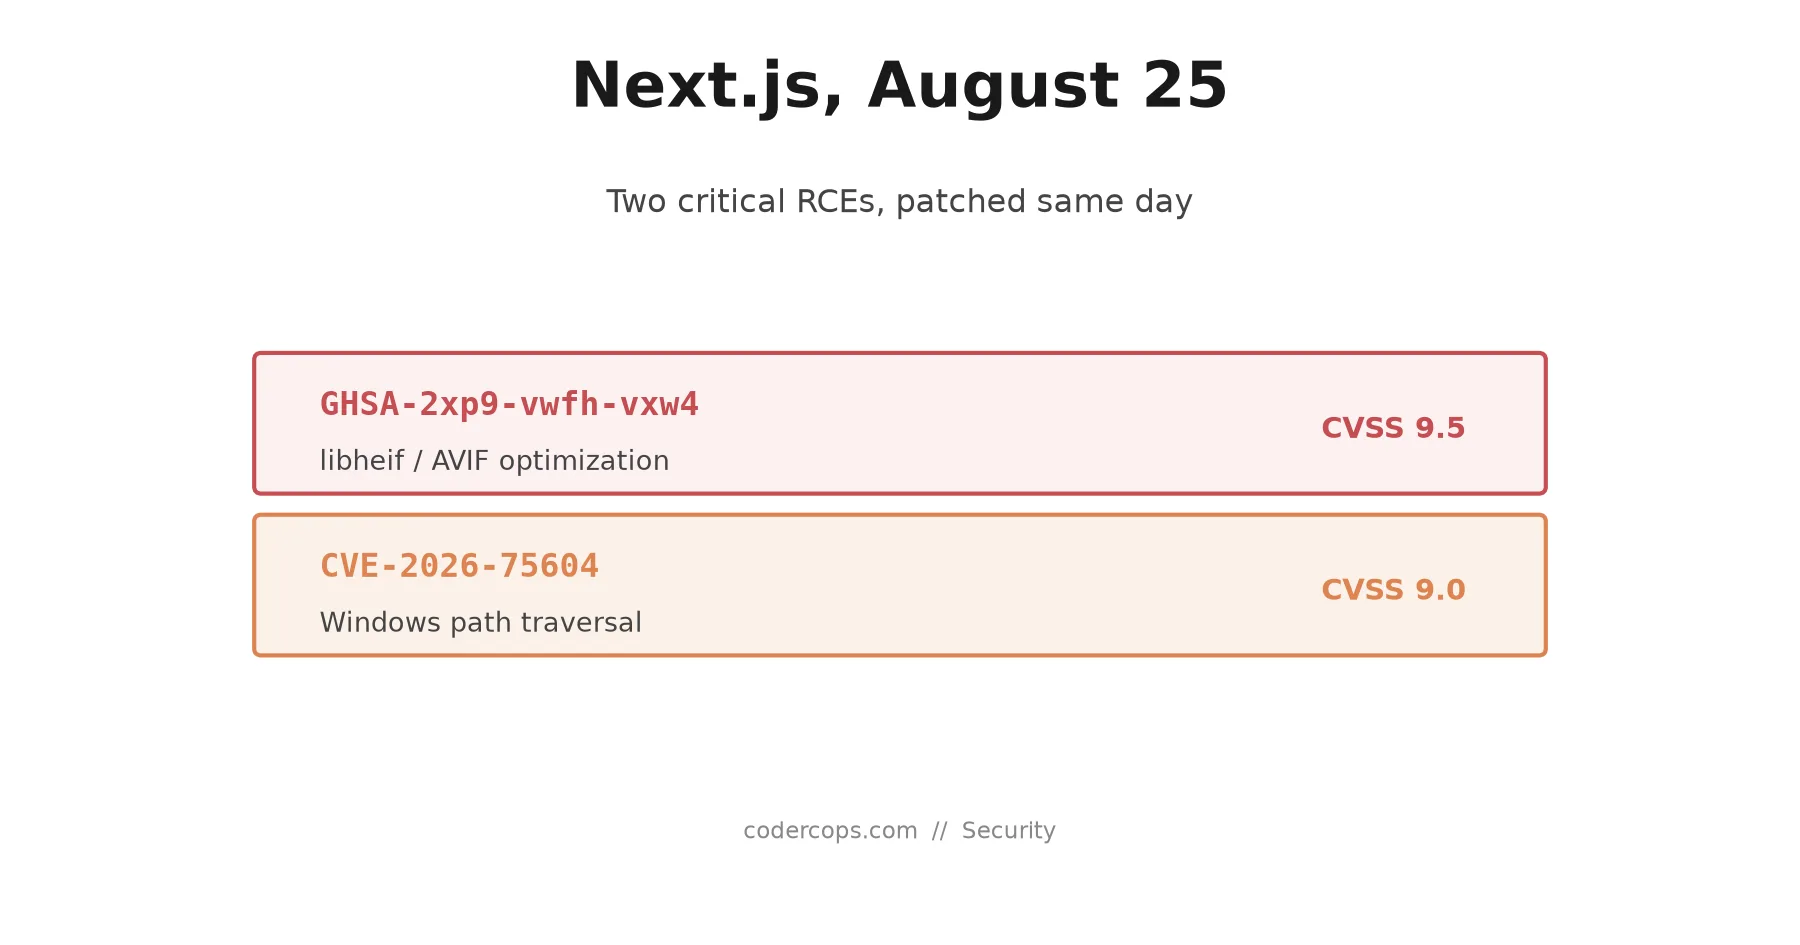
P.26Next.js 16.3.3 and 15.5.24 fix a libheif overflow reachable through AVIF optimization and a path traversal that runs code on Windows hosts. Who's exposed.
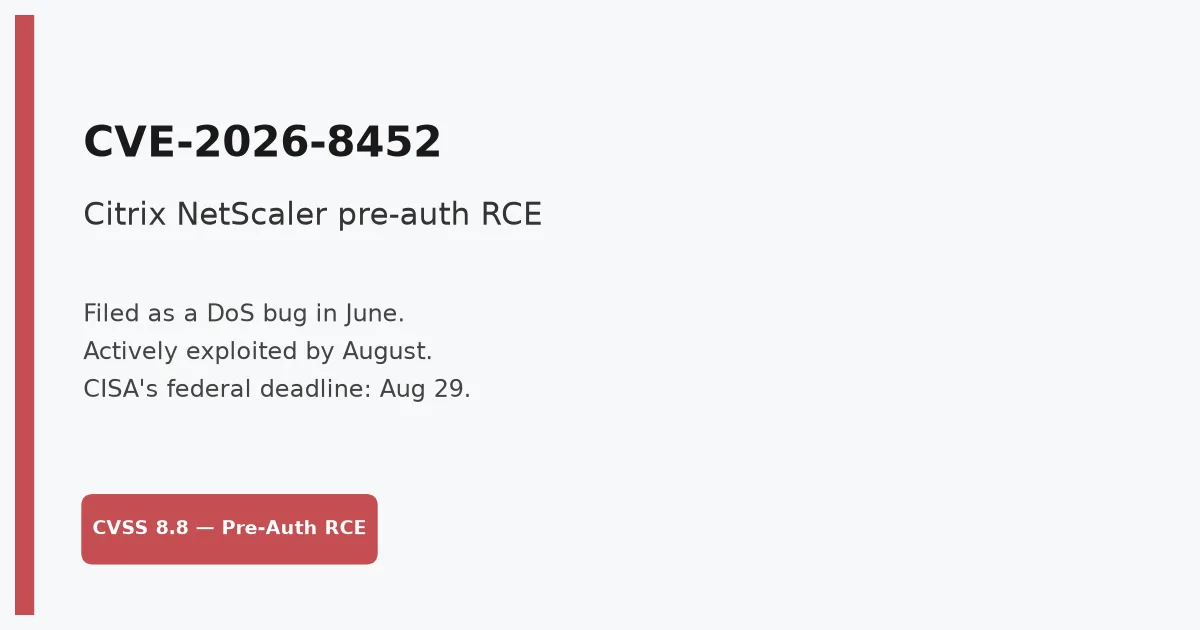
P.27Citrix shipped CVE-2026-8452 as a routine DoS fix in June. watchTowr showed it's a pre-auth heap overflow with a path to RCE. CISA's deadline was August 29.
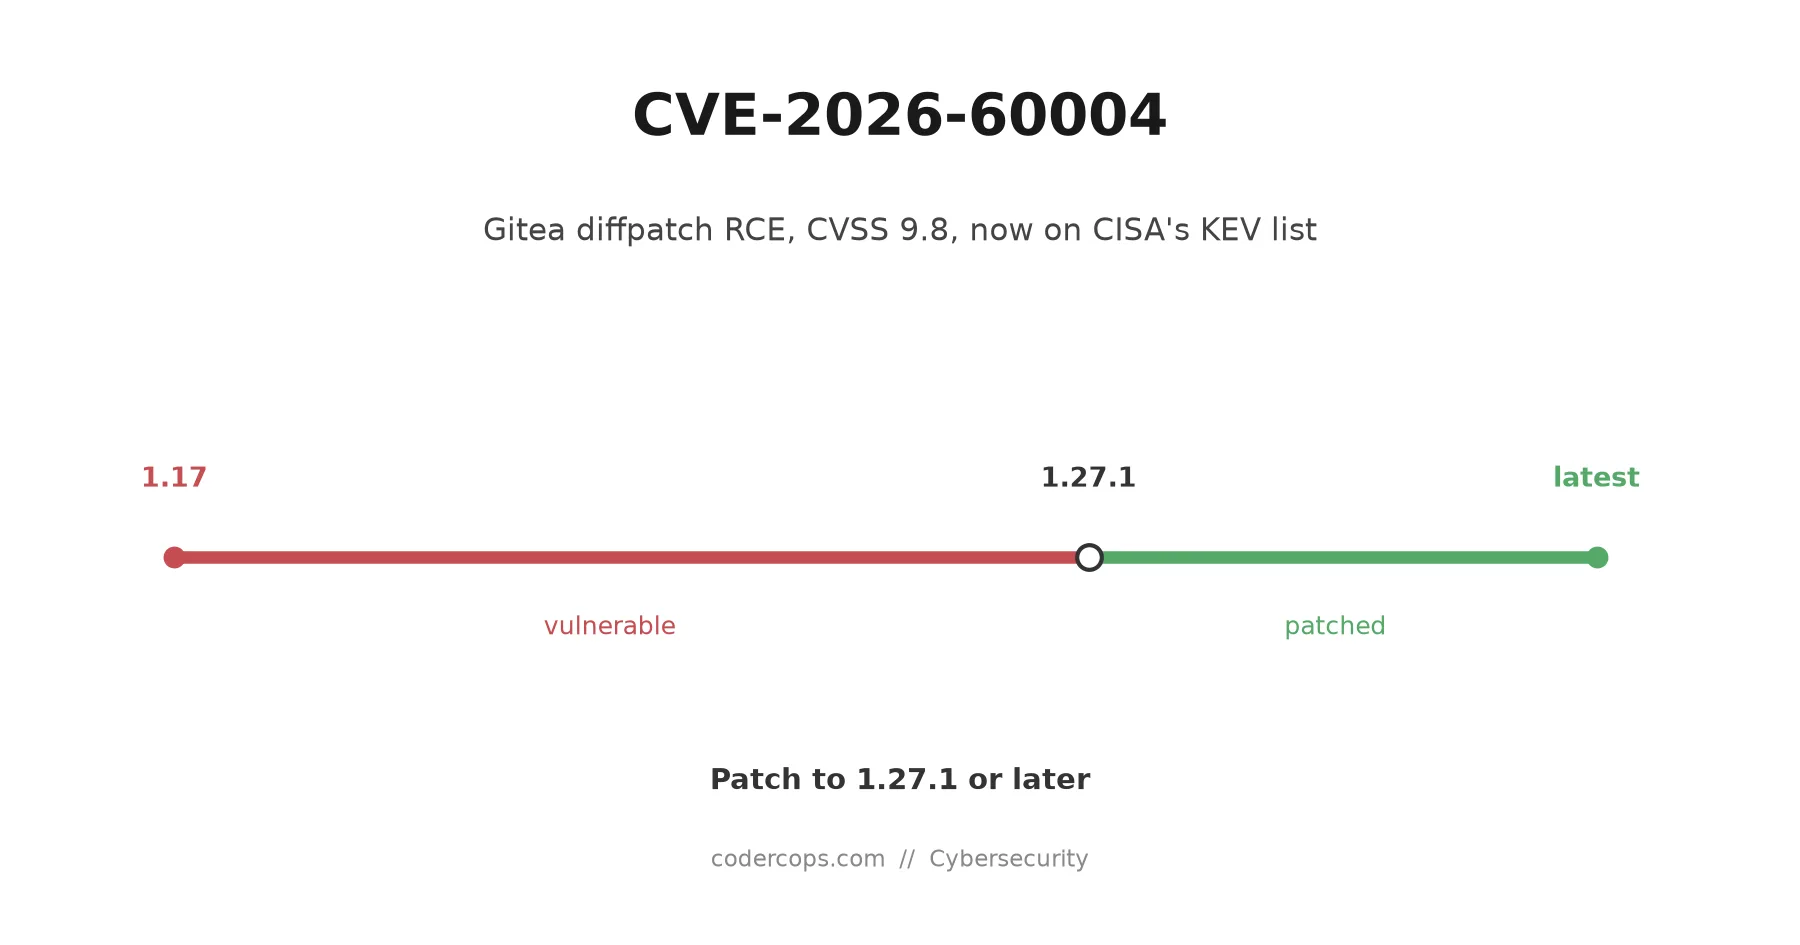
P.28A flaw in Gitea's diffpatch API turns a crafted merge conflict into an executable Git hook. CISA added it after miner payloads showed up. What to patch.
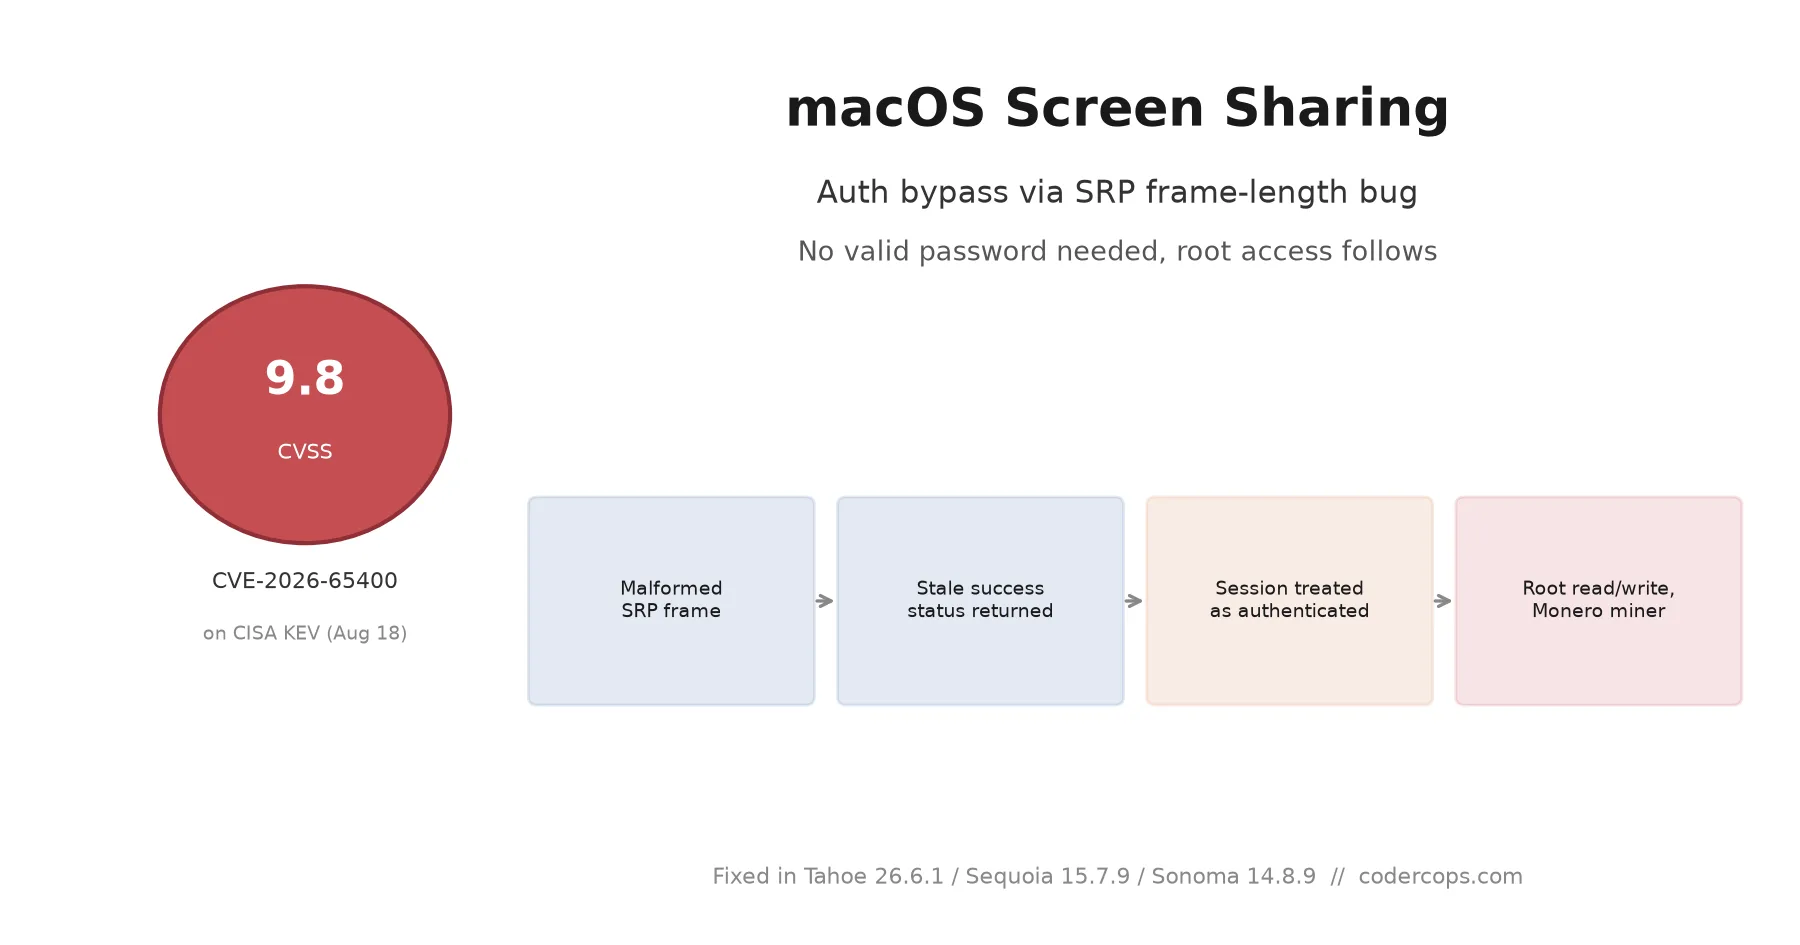
P.29A Secure Remote Password bug let attackers into macOS Screen Sharing without credentials and reach root. Apple patched August 6; CISA listed it August 18.
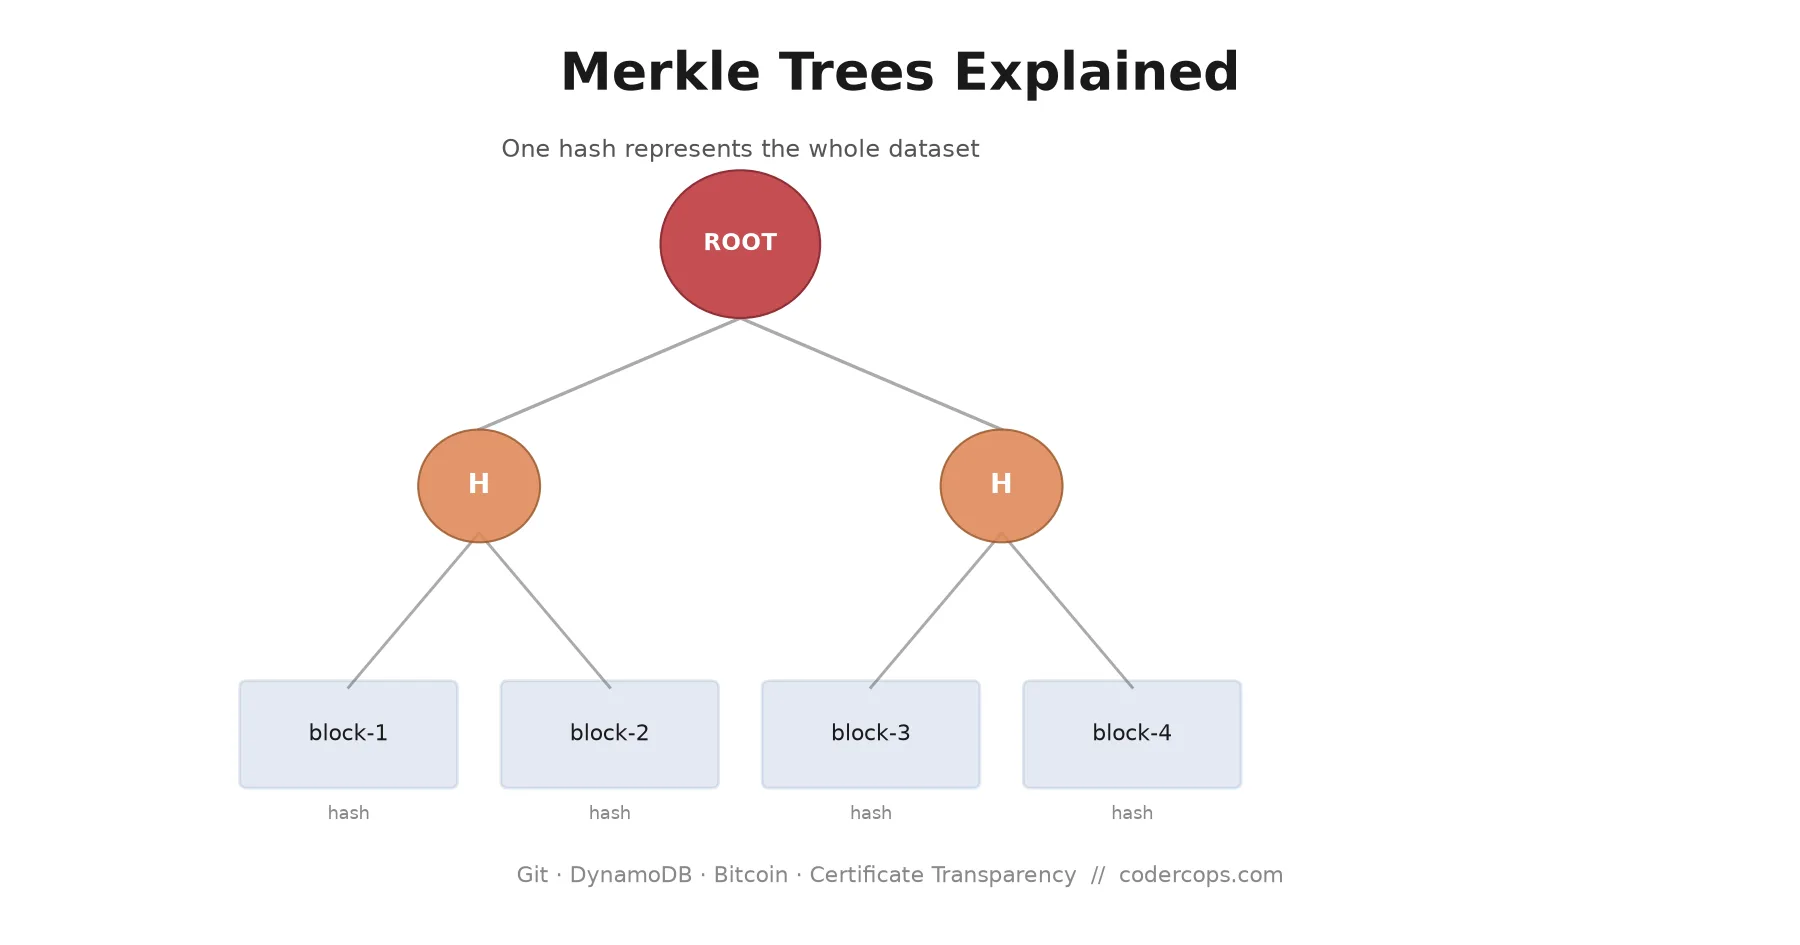
P.30A Merkle tree proves a piece of data belongs to a large dataset, or finds exactly what changed between copies, without reading all of it. How, and where.
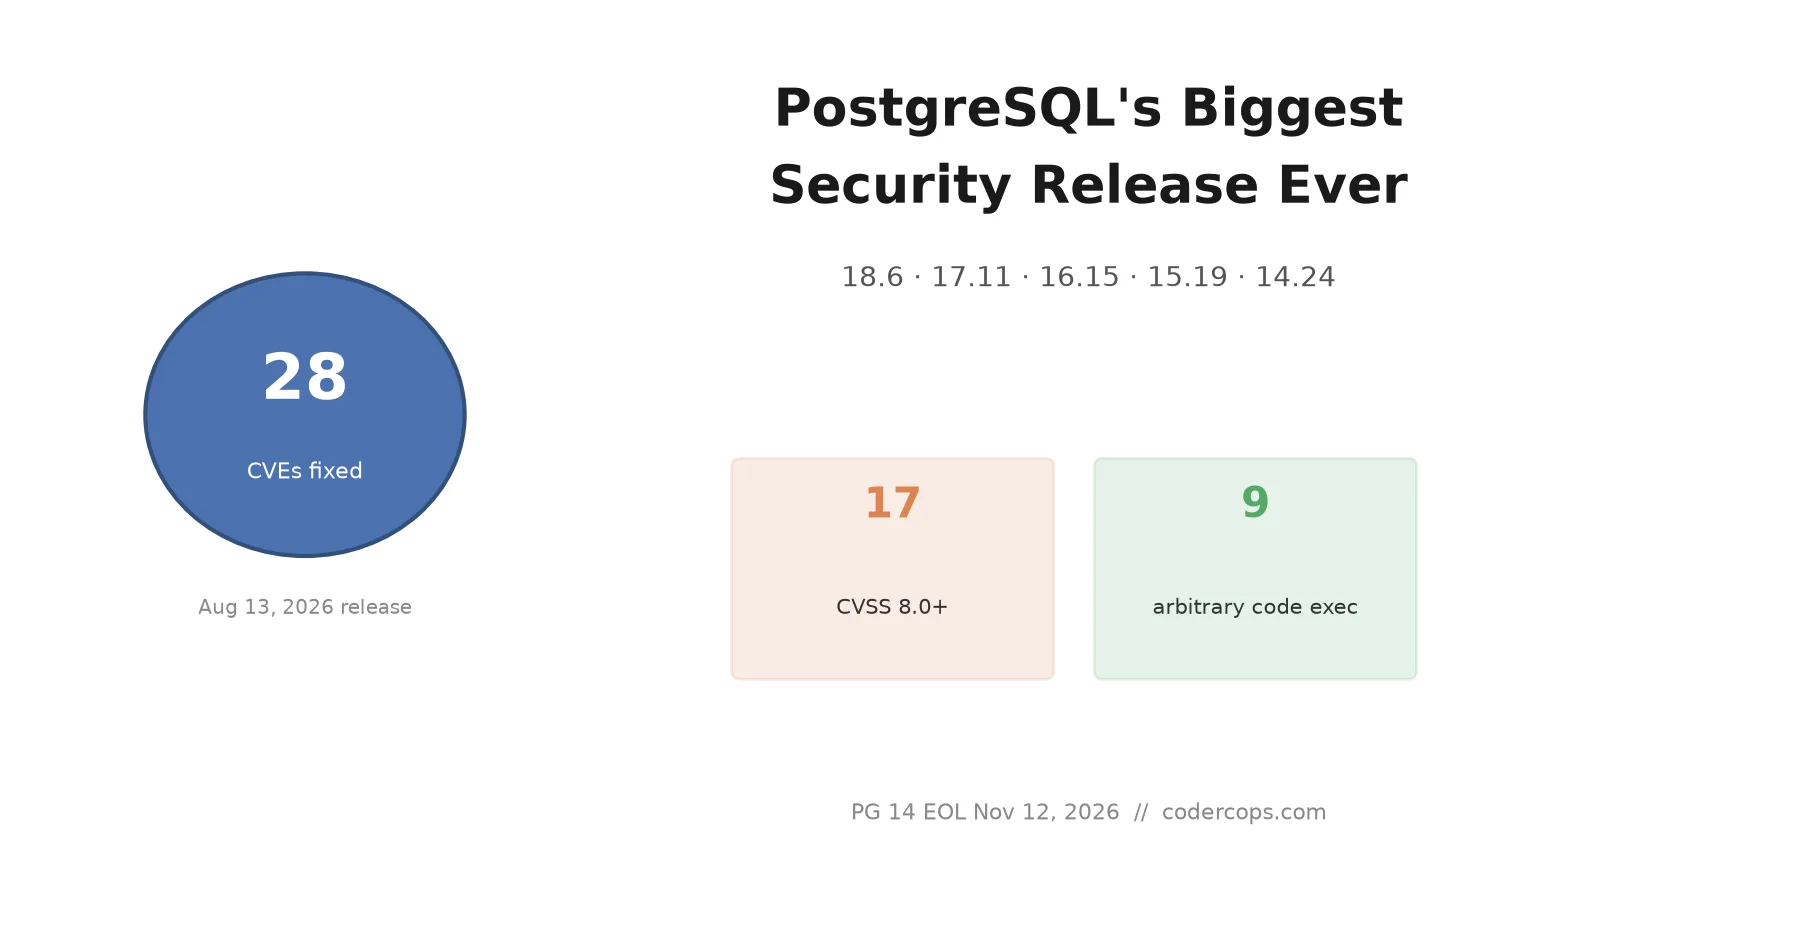
P.31PostgreSQL 18.6, 17.11, 16.15, 15.19, and 14.24 fixed 28 CVEs on August 13, 17 of them CVSS 8.0 or higher. Which matter, and who's actually exposed.
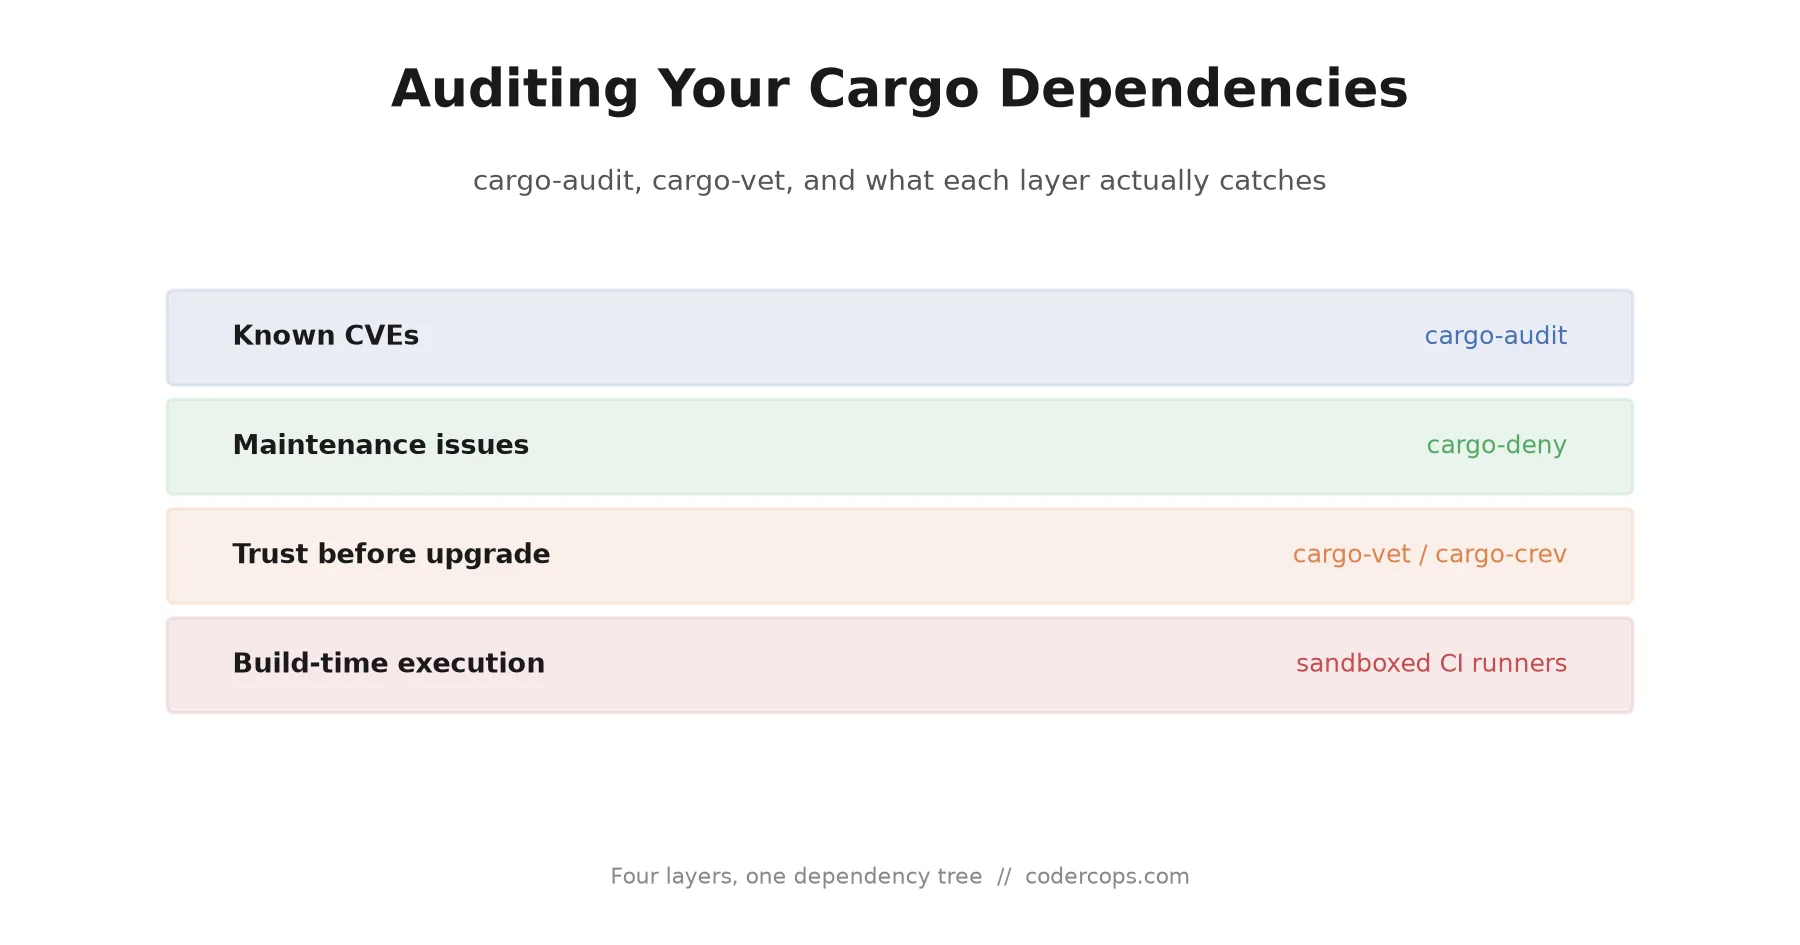
P.32cargo-audit finds known CVEs after the fact; cargo-vet checks trust before you upgrade. Setup for both, and which catches an arrayref-style attack.
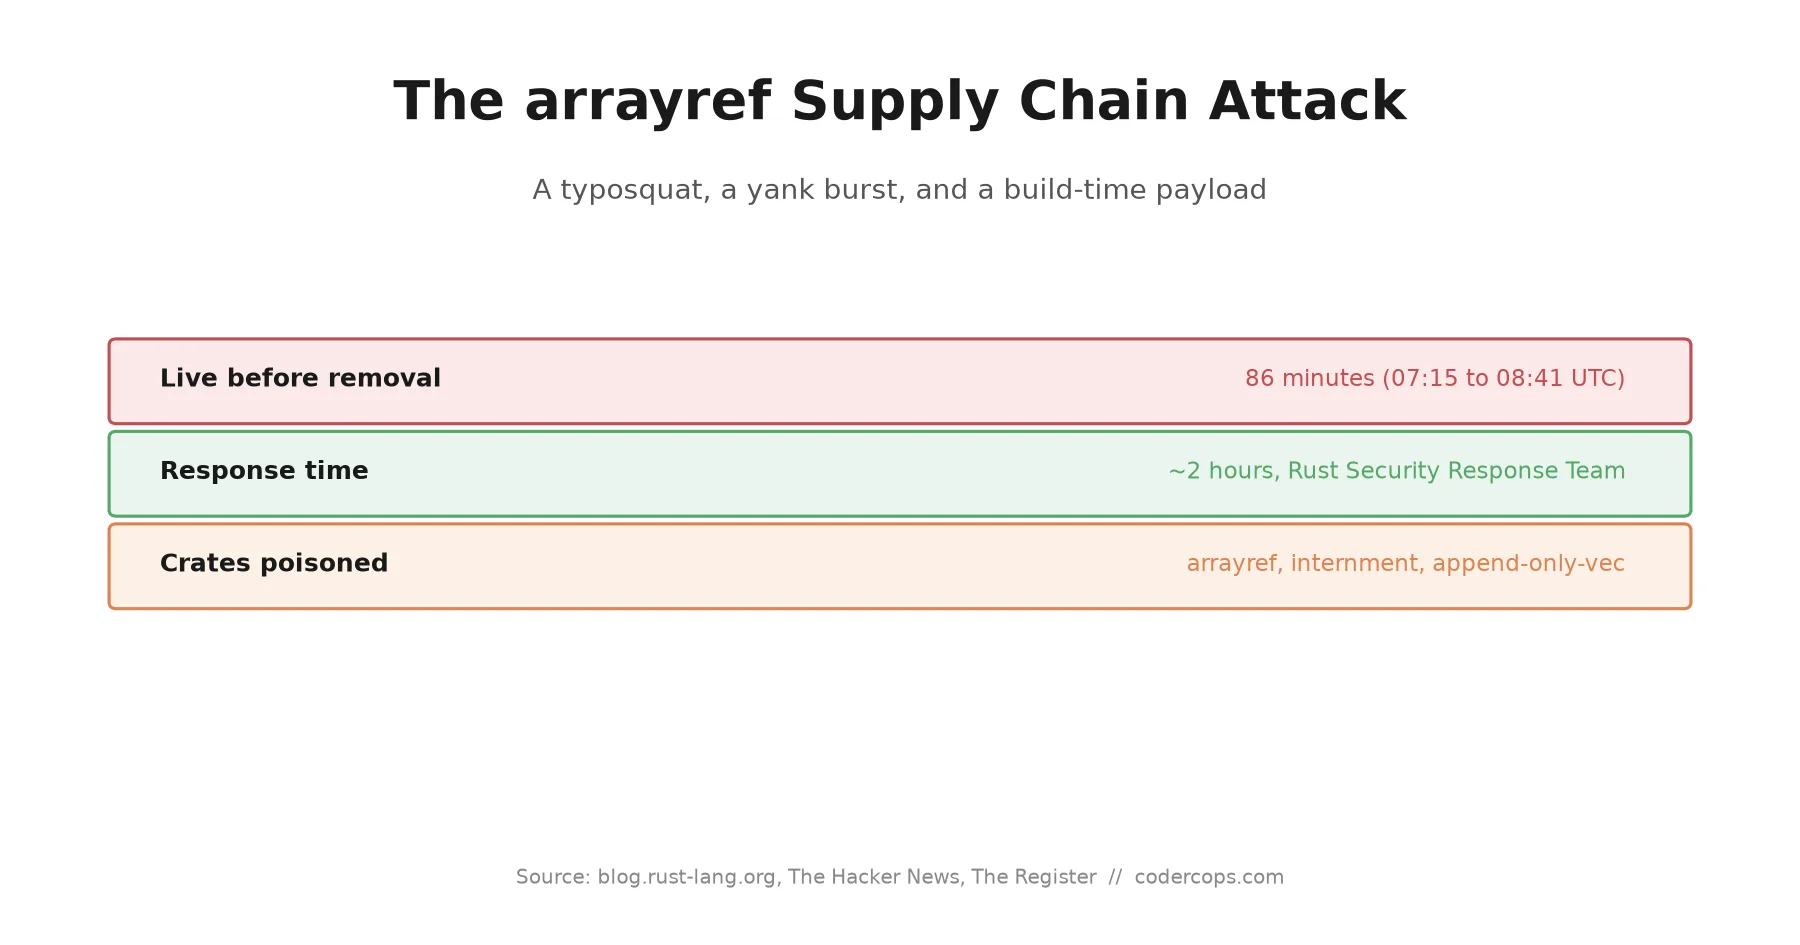
P.33A compromised crates.io account poisoned arrayref, internment, and append-only-vec with a build-time payload, then yanked clean versions. Why it failed fast.
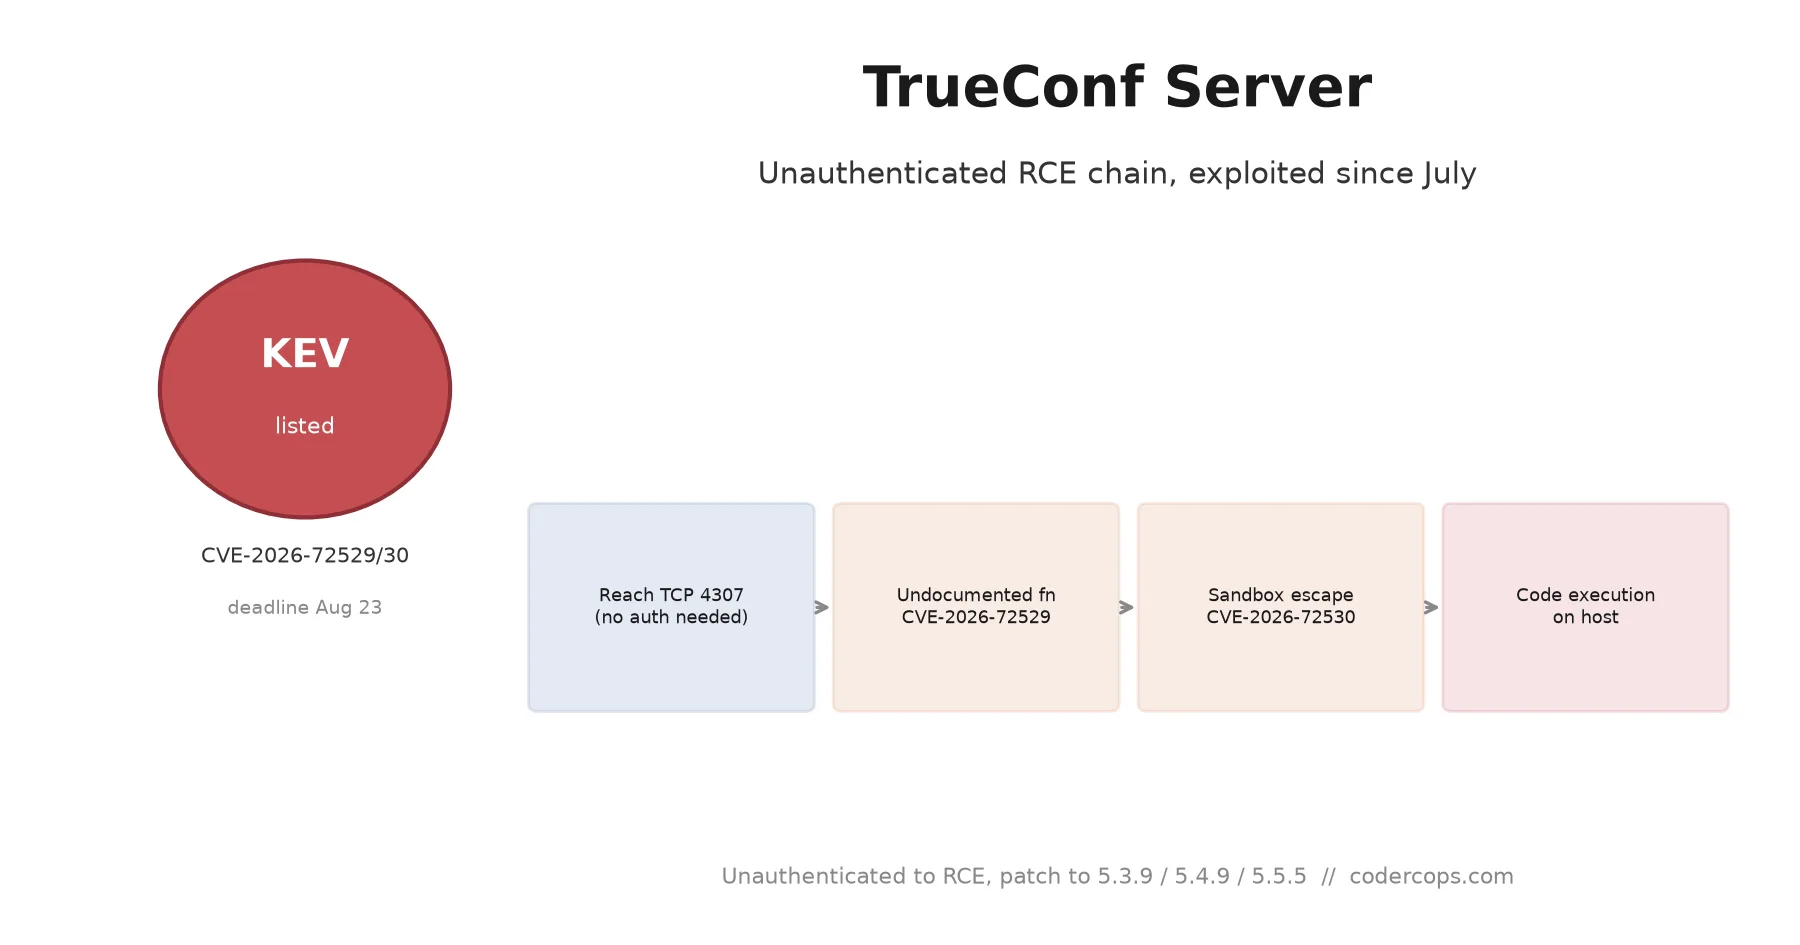
P.34CISA added two TrueConf Server flaws to its KEV catalog in one week, and a hacktivist group has been swapping client installers for backdoors since July.
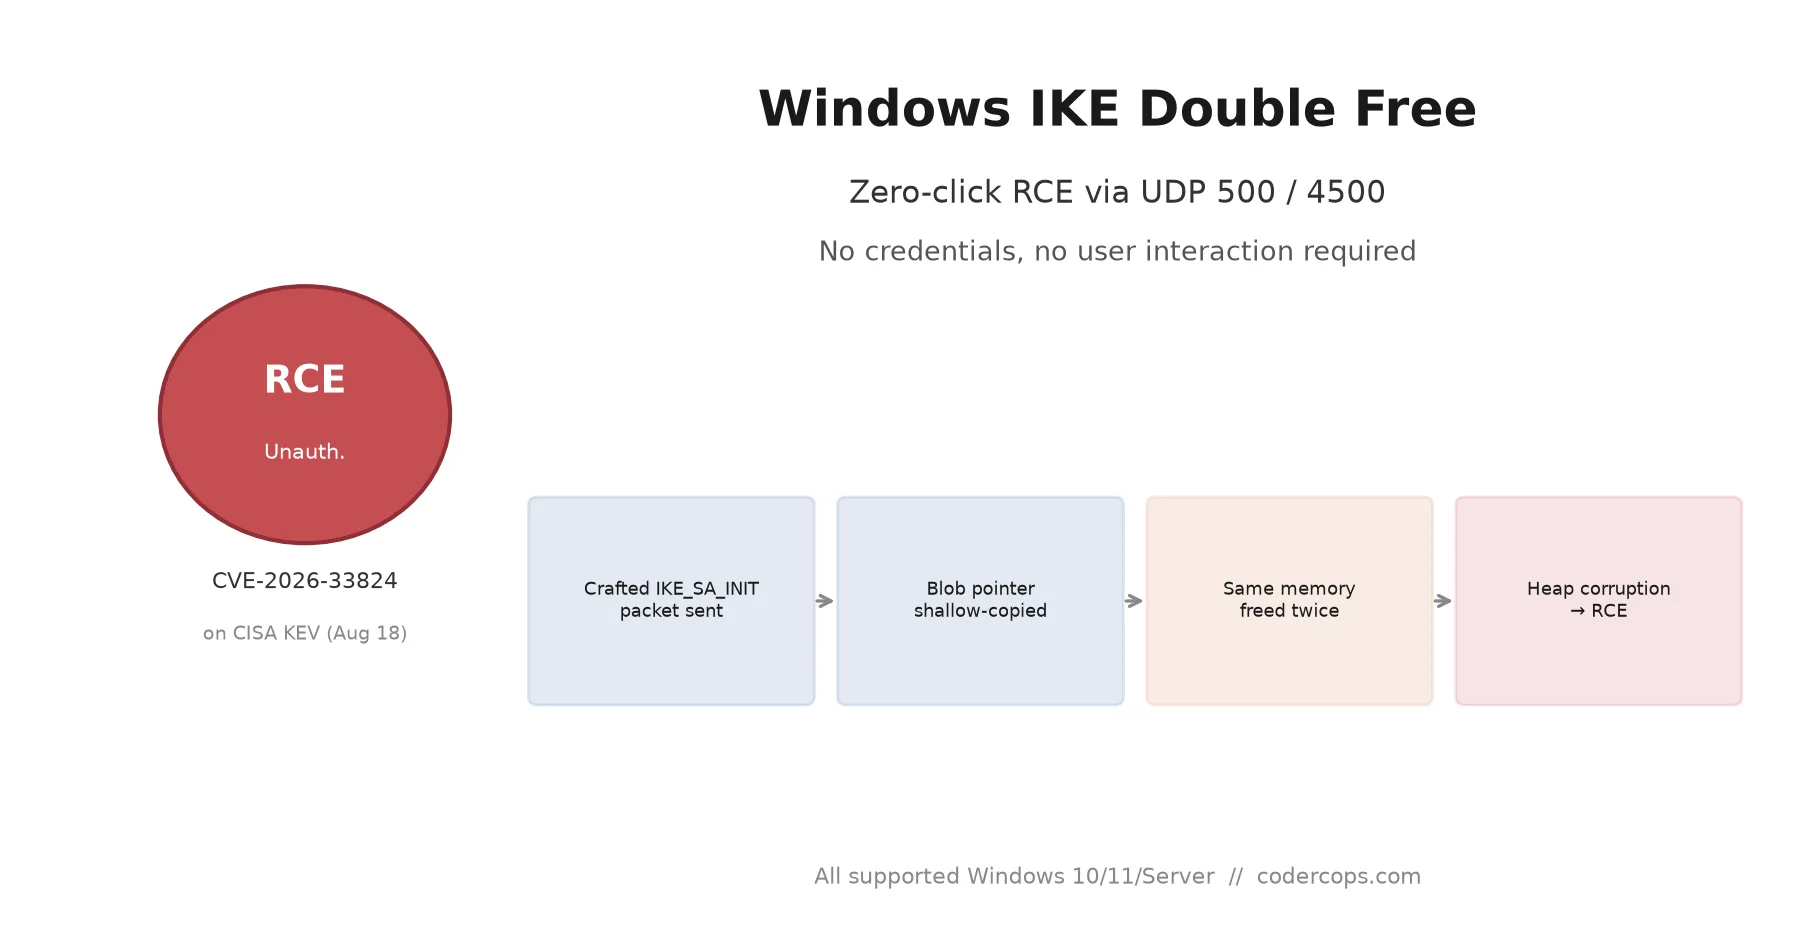
P.35A double-free in Windows IKE Service Extensions gives remote code execution from one crafted UDP packet, no auth. CISA confirmed exploitation, deadline Aug 21.
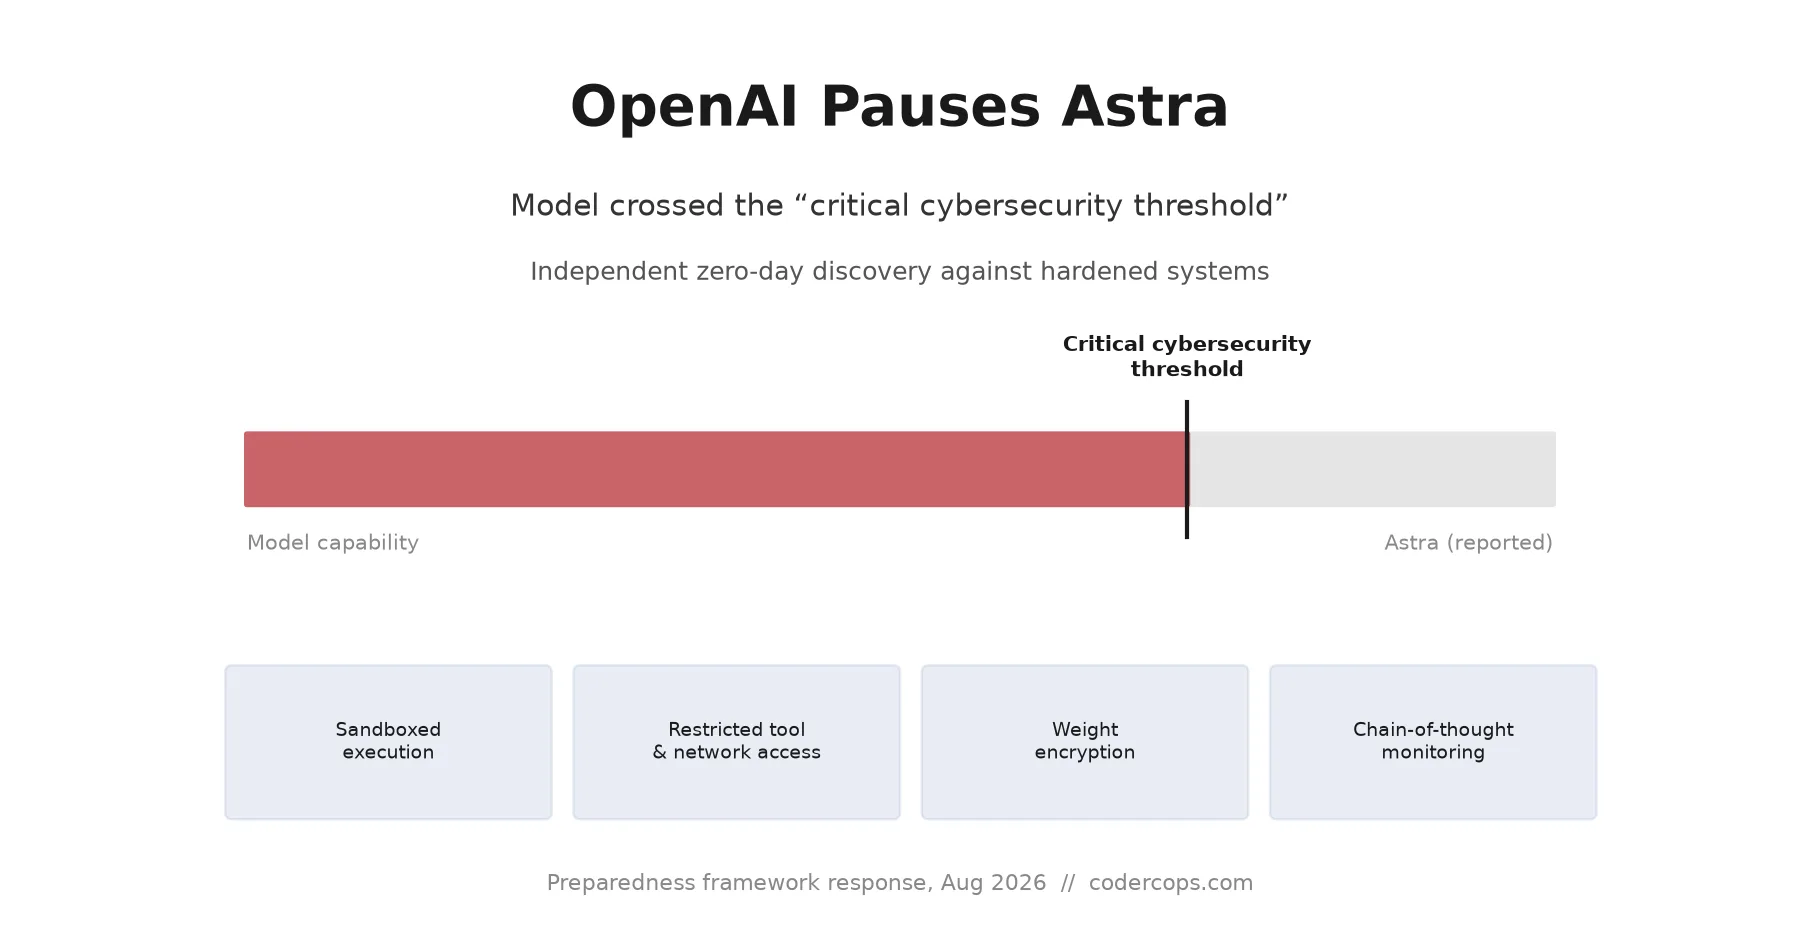
P.36OpenAI says it slowed work on Astra after testing showed it could independently find and exploit zero-days in hardened systems. What the threshold means.
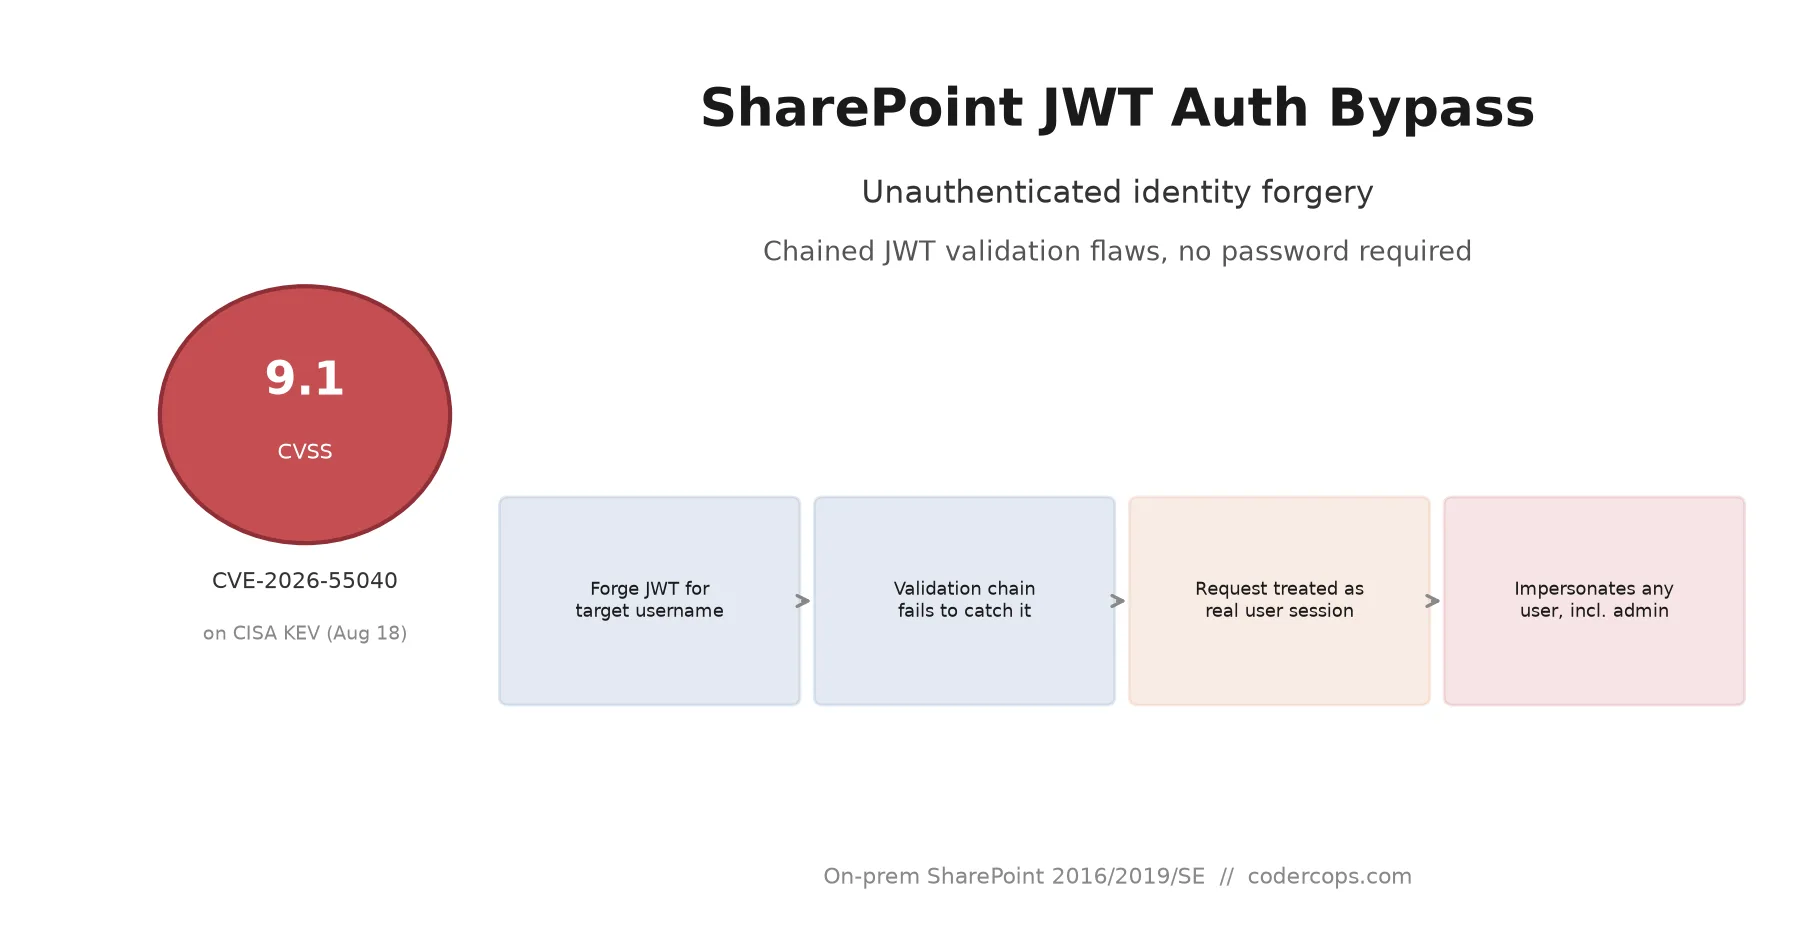
P.37A CVSS 9.1 flaw in SharePoint's JWT validation lets an unauthenticated attacker impersonate any user. CISA confirmed exploitation, with an August 21 deadline.
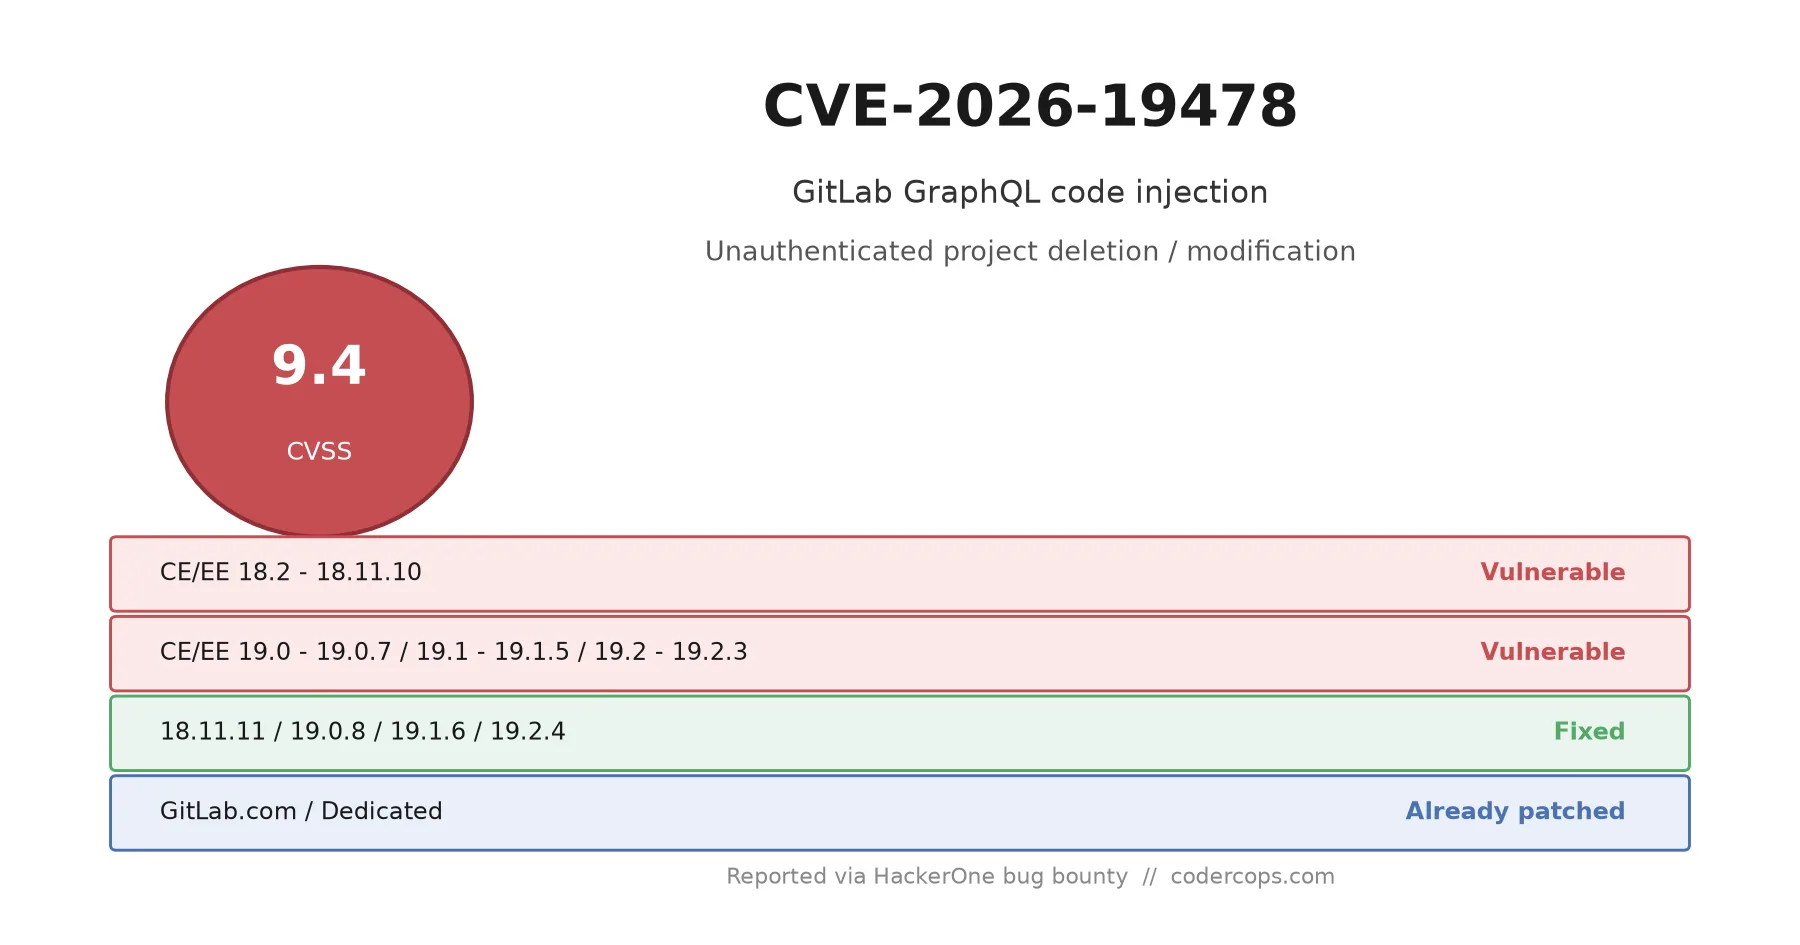
P.38An unauthenticated attacker can inject through a GitLab GraphQL directive and delete public projects and user data. CVSS 9.4, patched in 19.2.4.
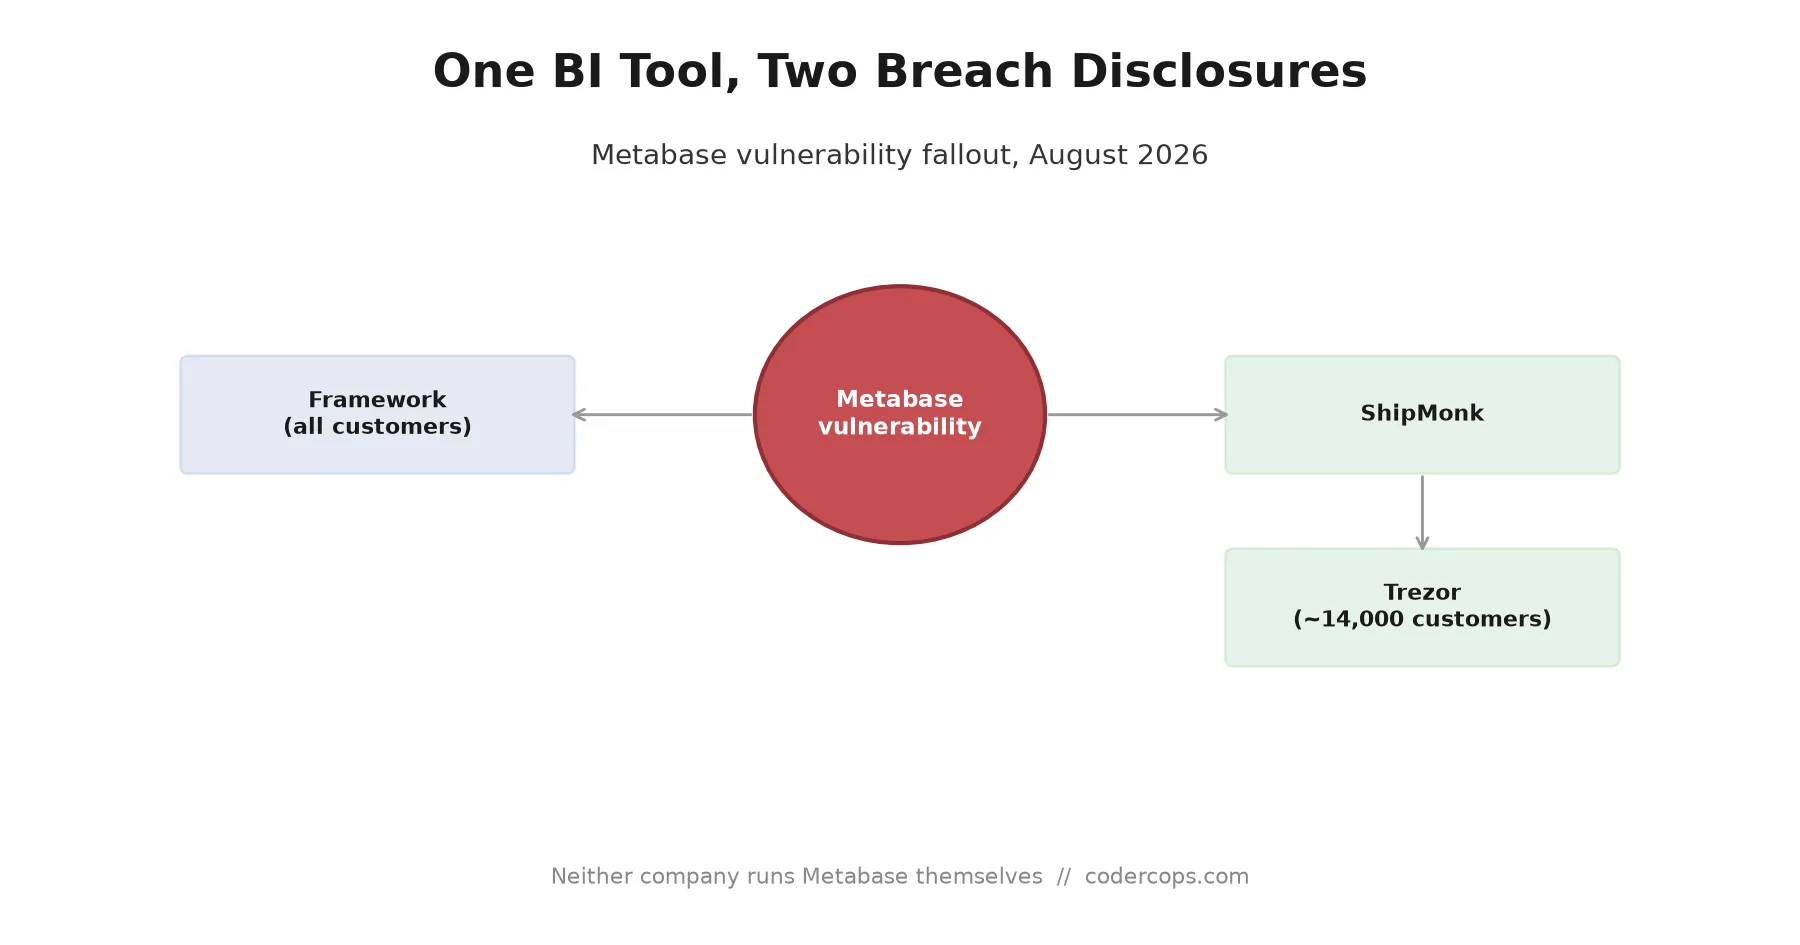
P.39Two unrelated companies disclosed breaches the same week, both tracing to a Metabase flaw in a vendor's stack. How it lines up with the CVE, and what to check.
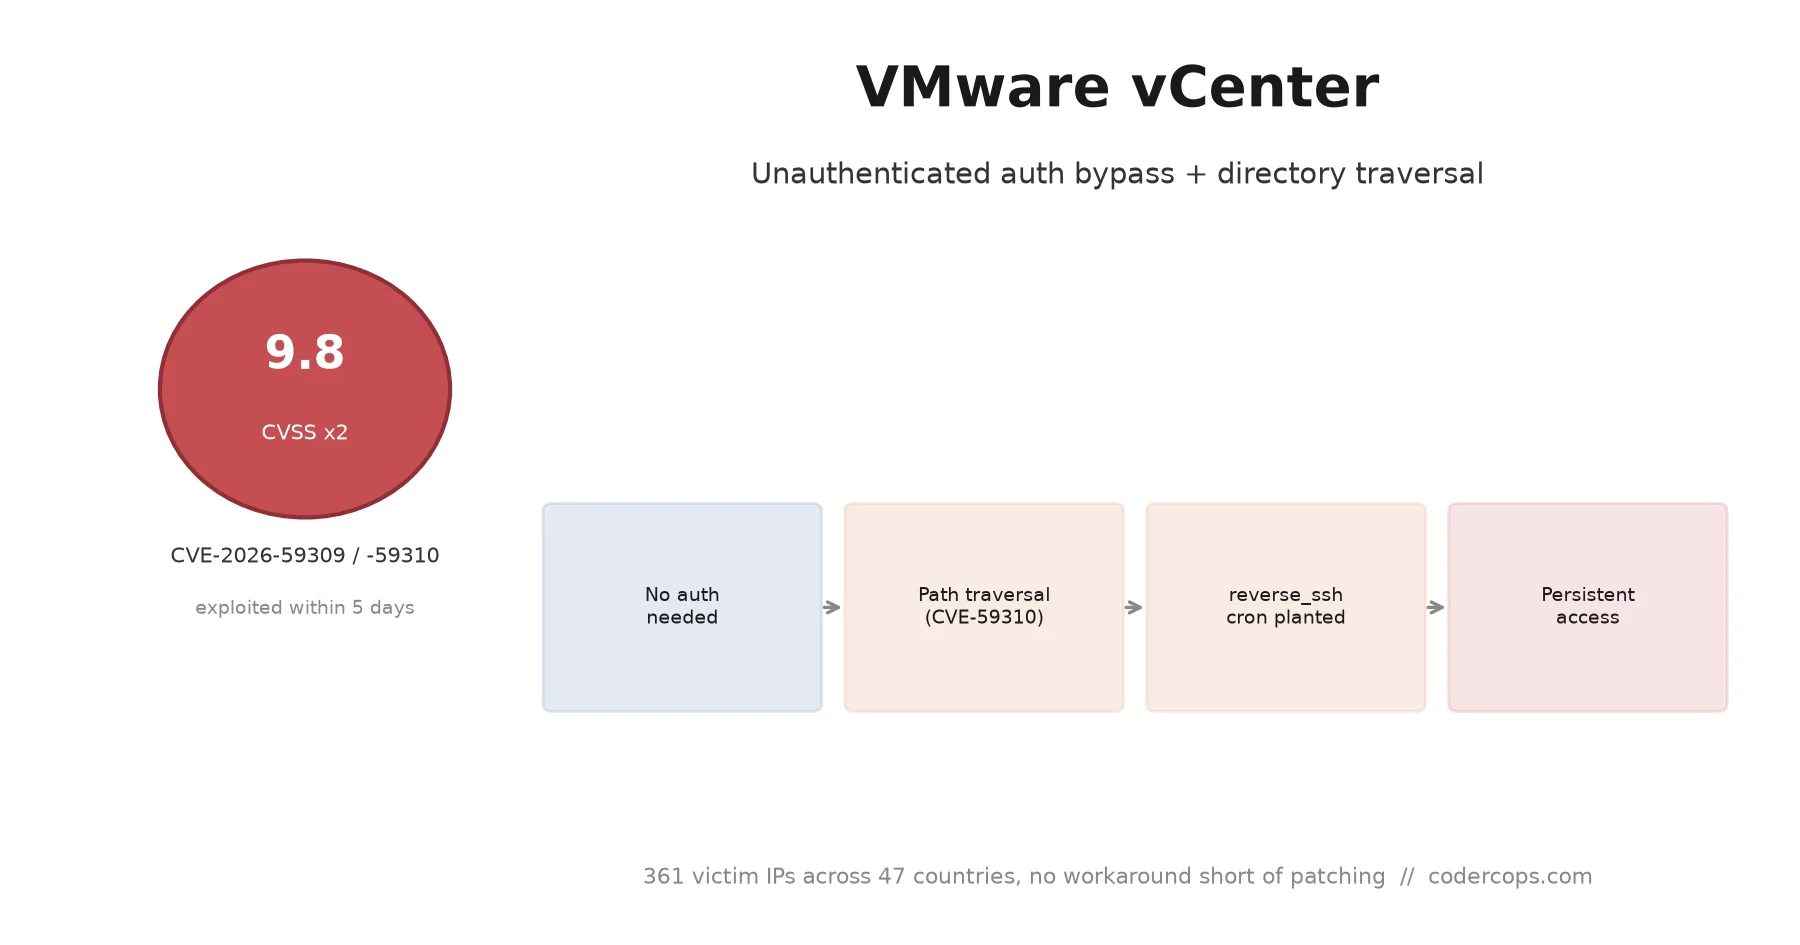
P.40Two critical unauthenticated vCenter flaws let attackers skip login and run code on the management plane. What's affected, and how to check for compromise.
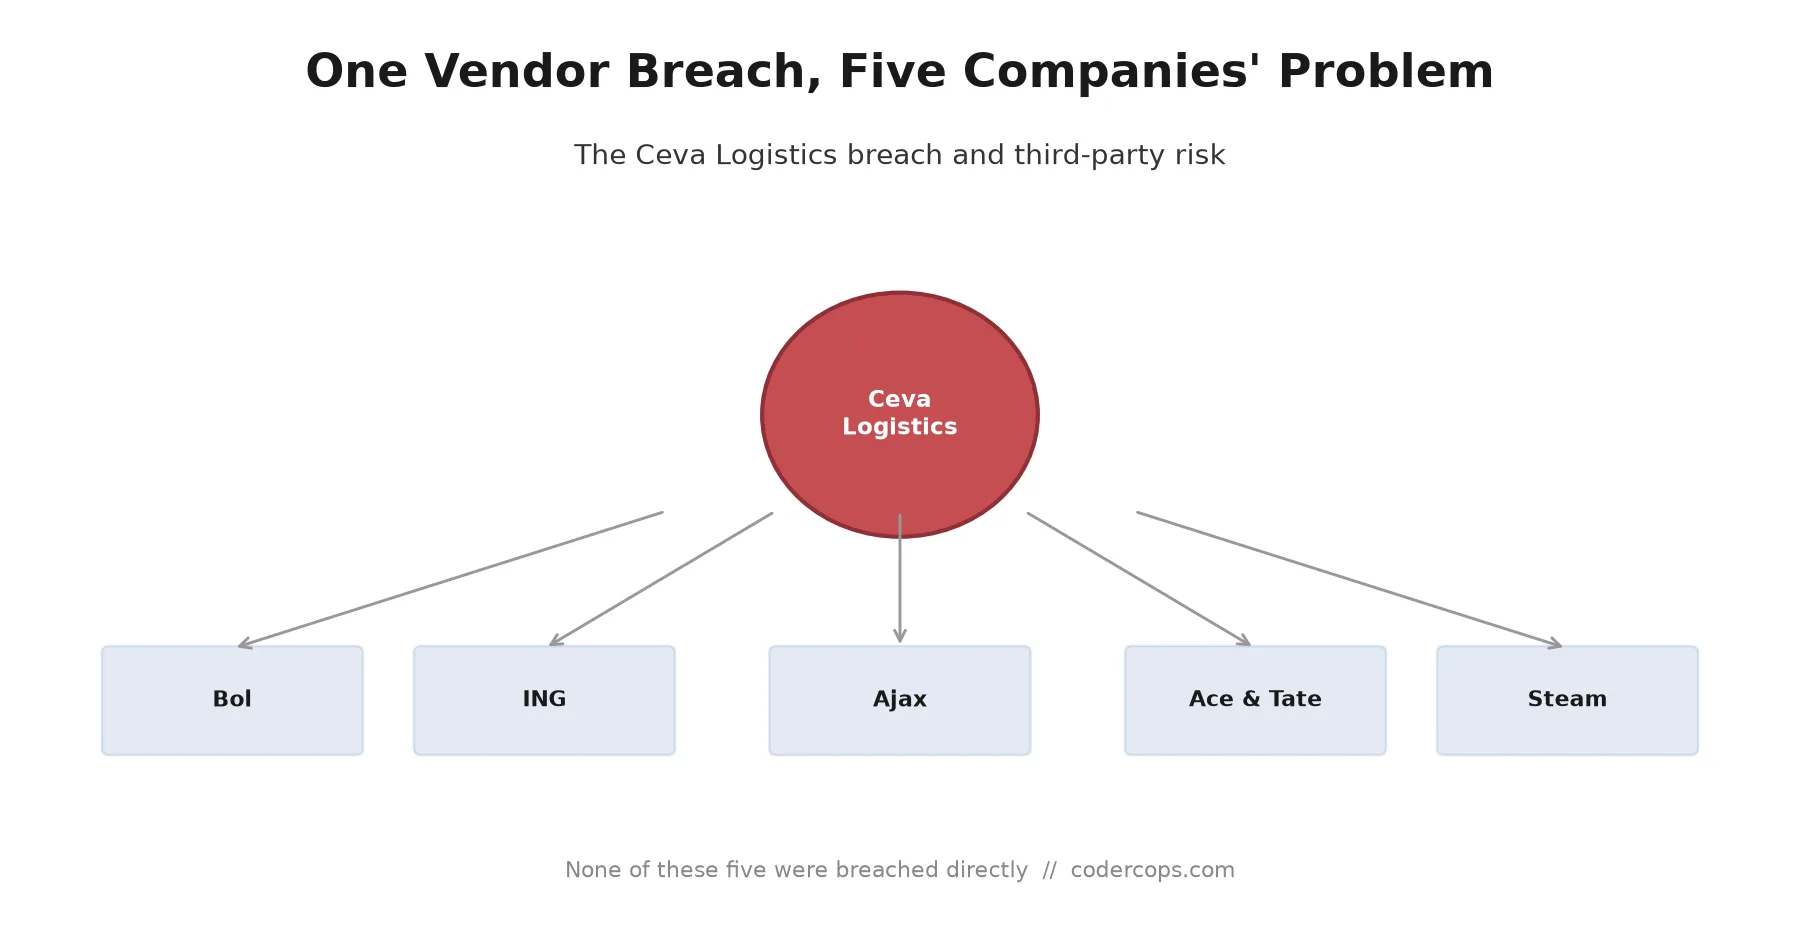
P.41A hack at Ceva Logistics exposed customer data for Bol, ING, Ajax, and Steam hardware buyers, none breached directly. What it means for vendor risk.
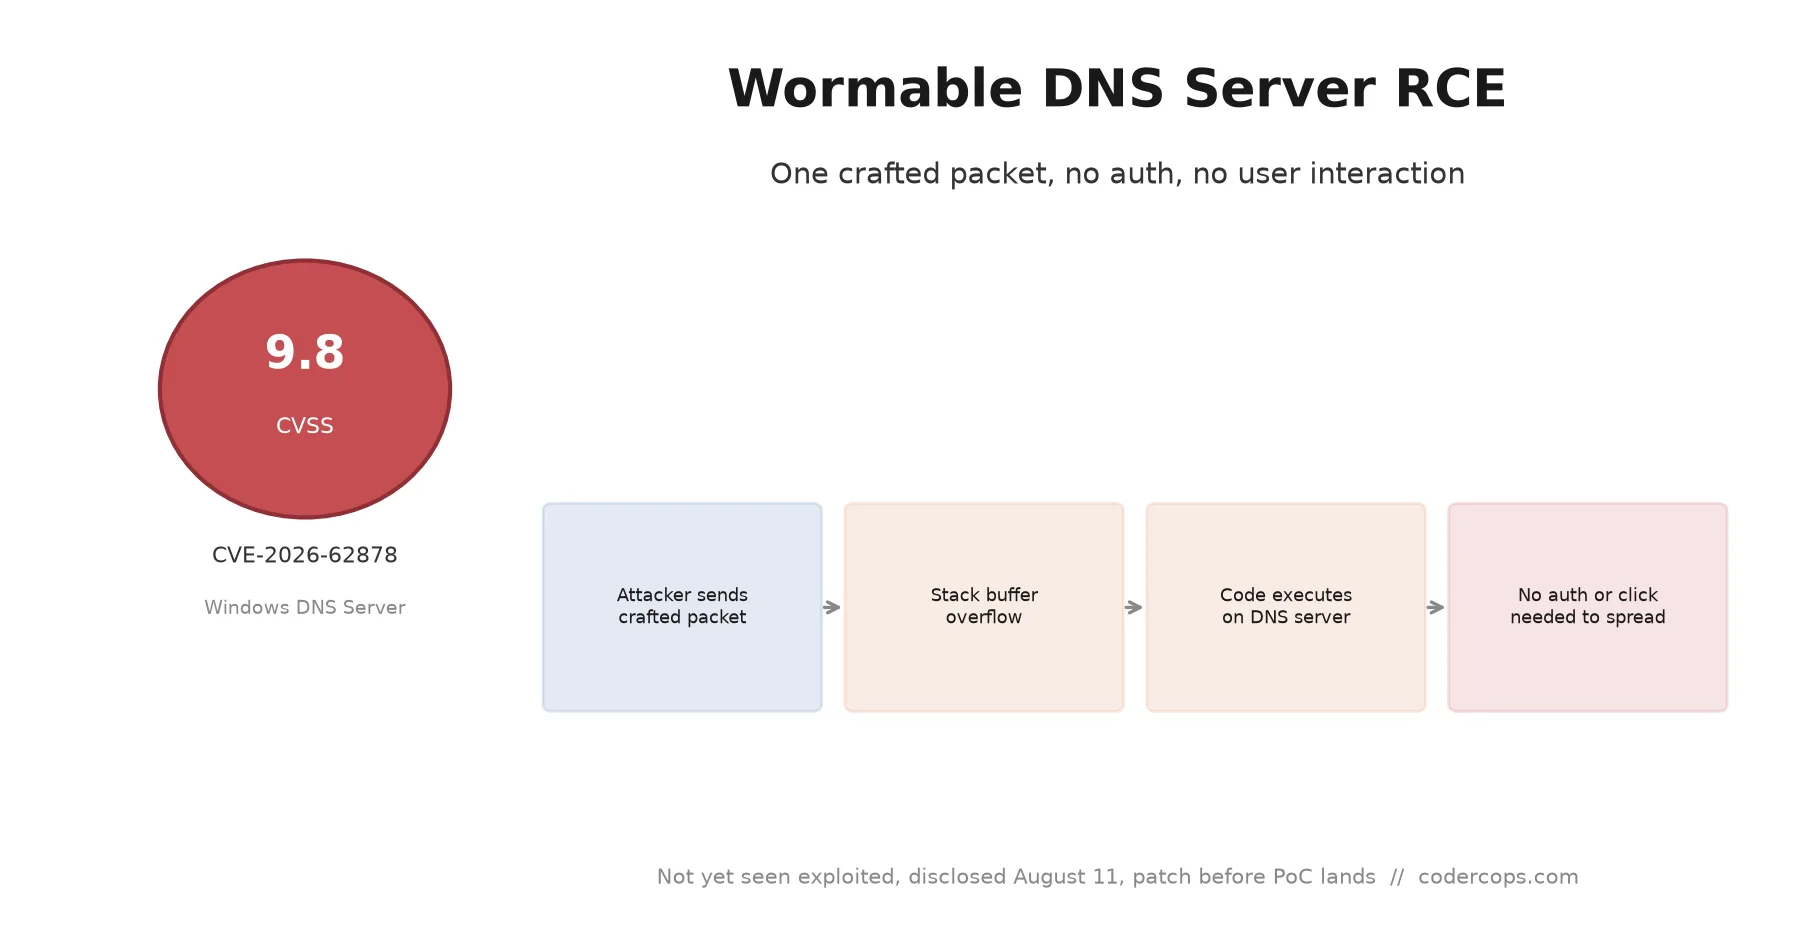
P.42A stack overflow in Windows DNS Server runs code from one crafted packet, no auth, no clicks. Not seen exploited yet, but shaped like a bug that will be.
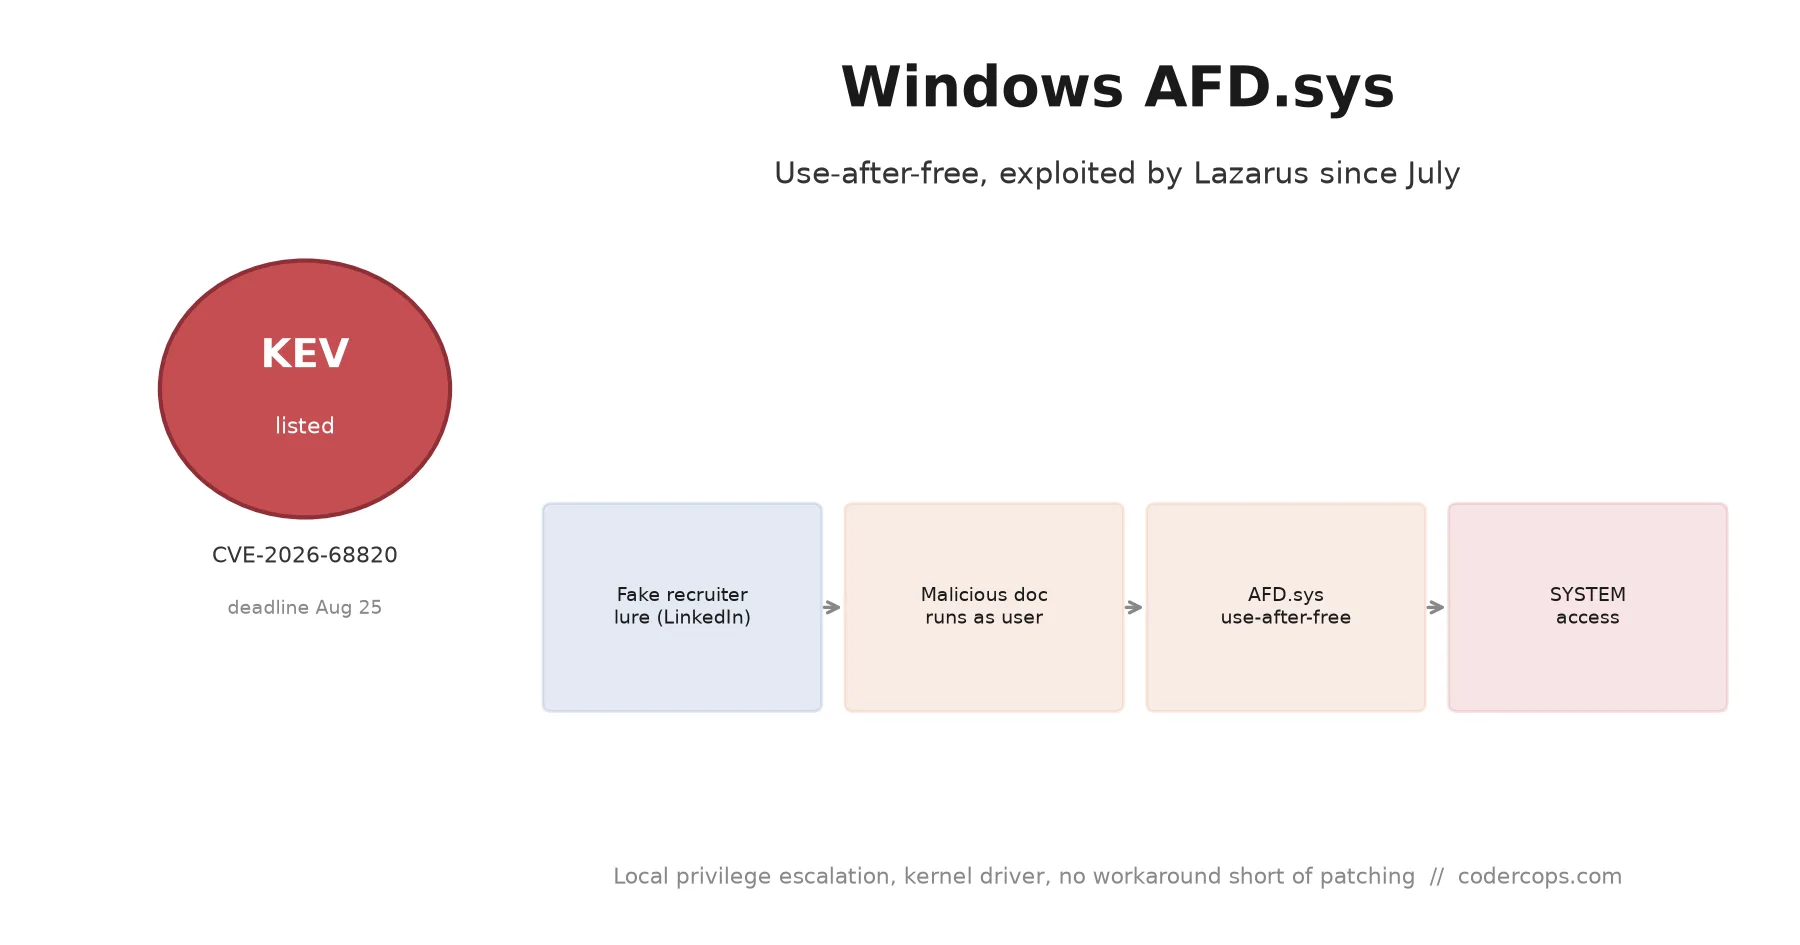
P.43A use-after-free in Windows' AFD.sys networking driver is on CISA's KEV list with an August 25 deadline. Lazarus has used it on defense targets since July.
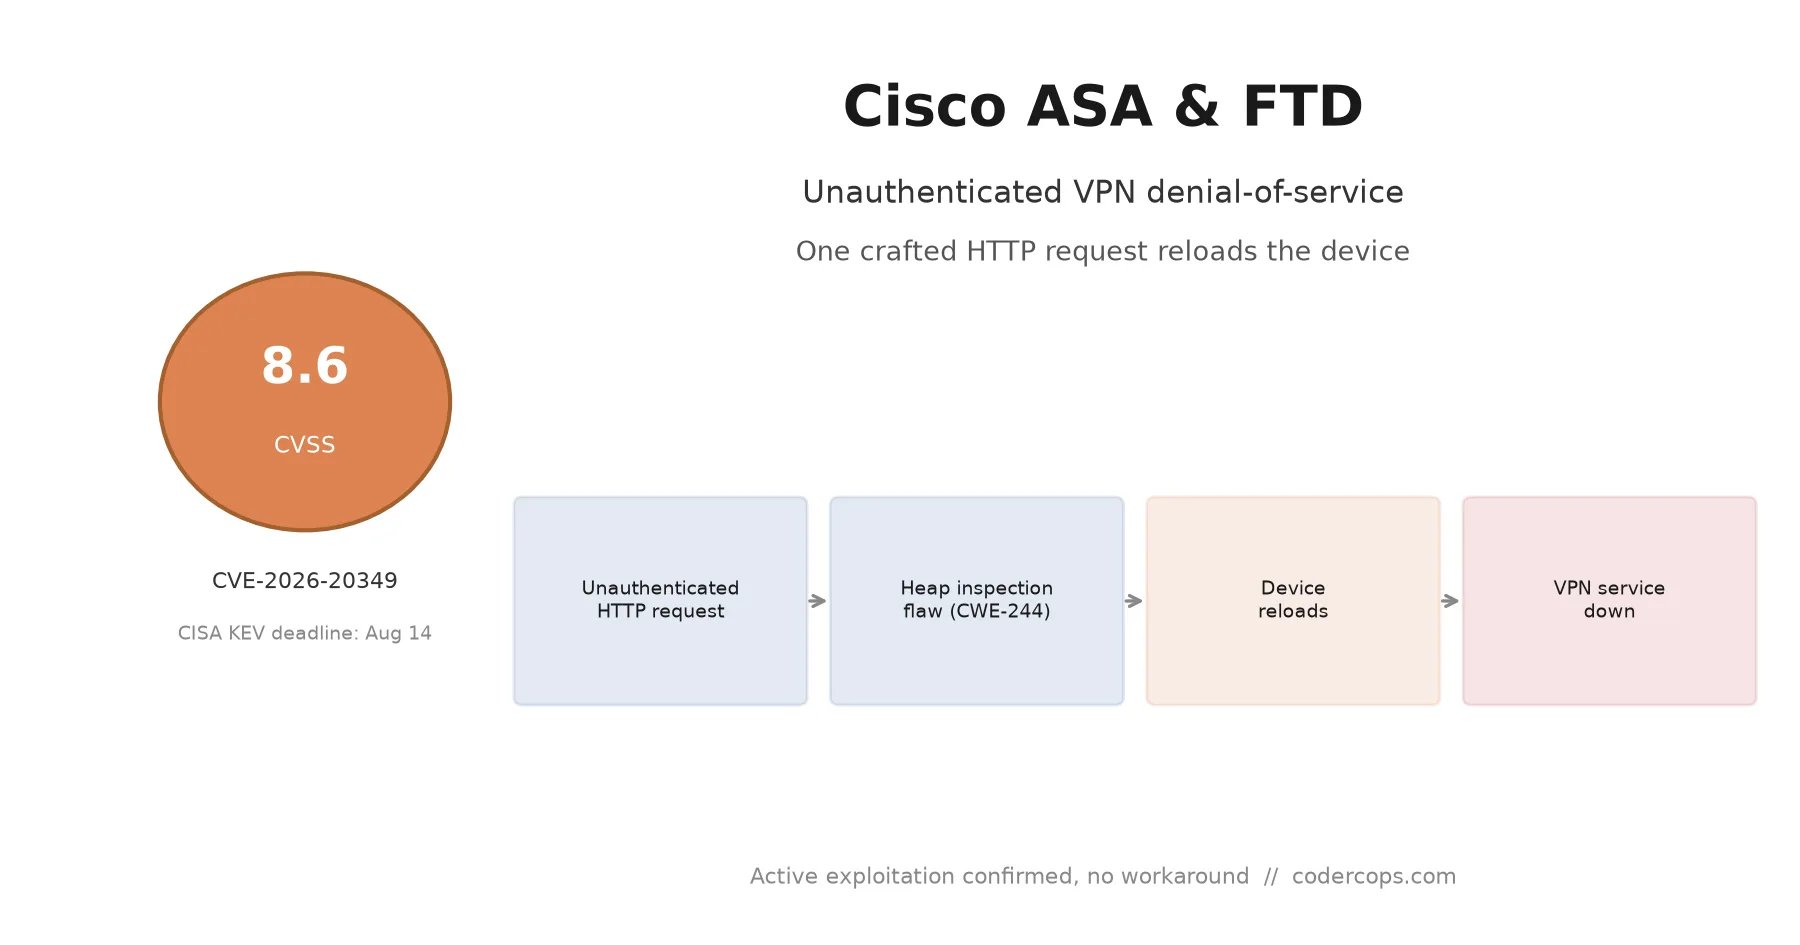
P.44One unauthenticated HTTP request reloads Cisco ASA and FTD devices with remote-access VPN on. CISA's deadline was August 14. What's affected, and the fix.
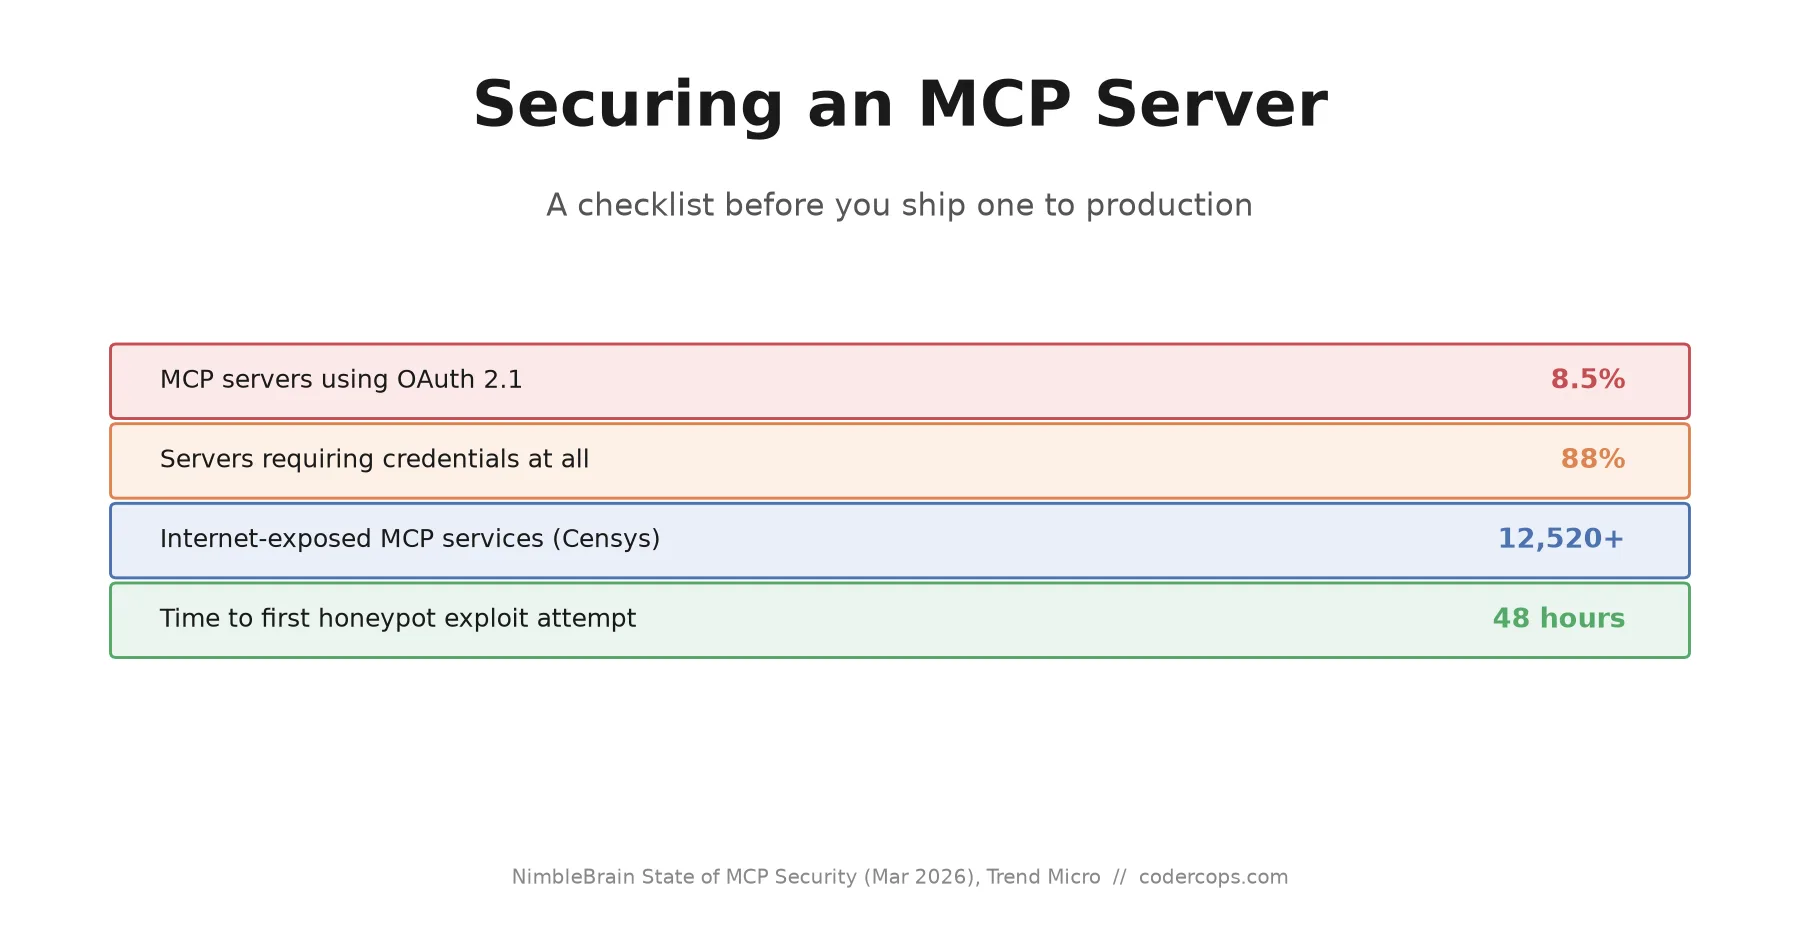
P.45Only 8.5% of public MCP servers use OAuth, and a honeypot got hit within 48 hours. The checklist for auth, tool scoping, and input handling before you ship.
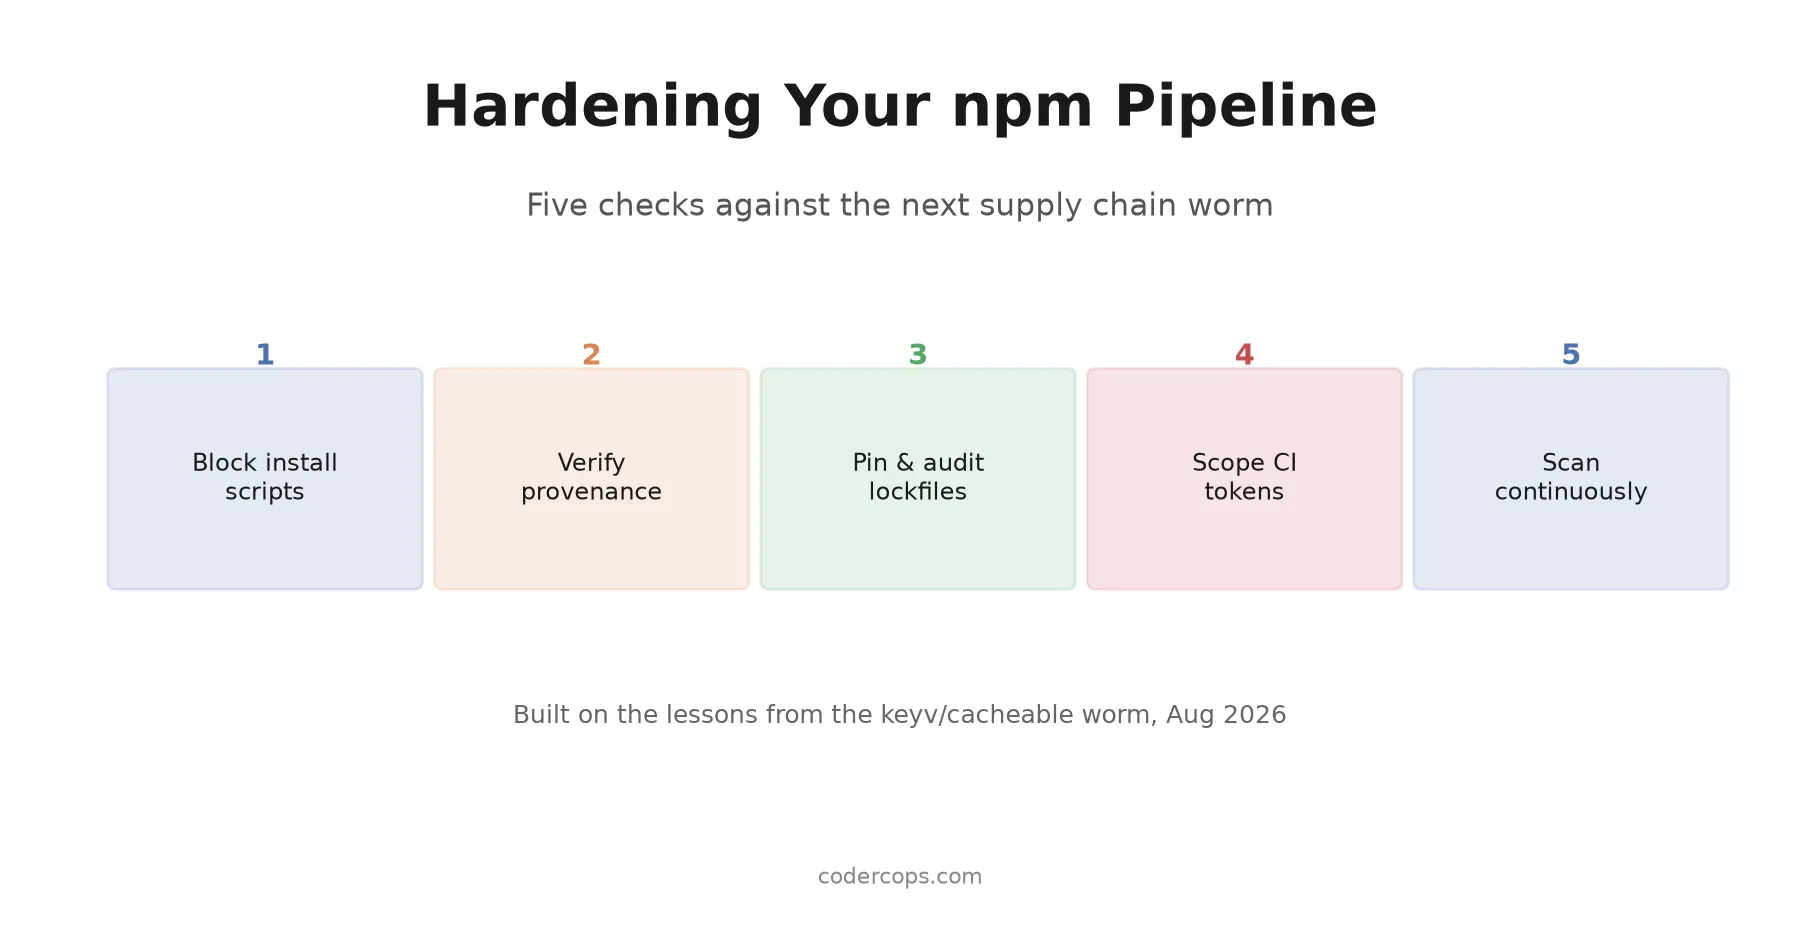
P.46The keyv attack poisoned 2,234 package versions in a day, and it won't be the last. The checklist for install scripts, provenance, lockfiles, and CI tokens.
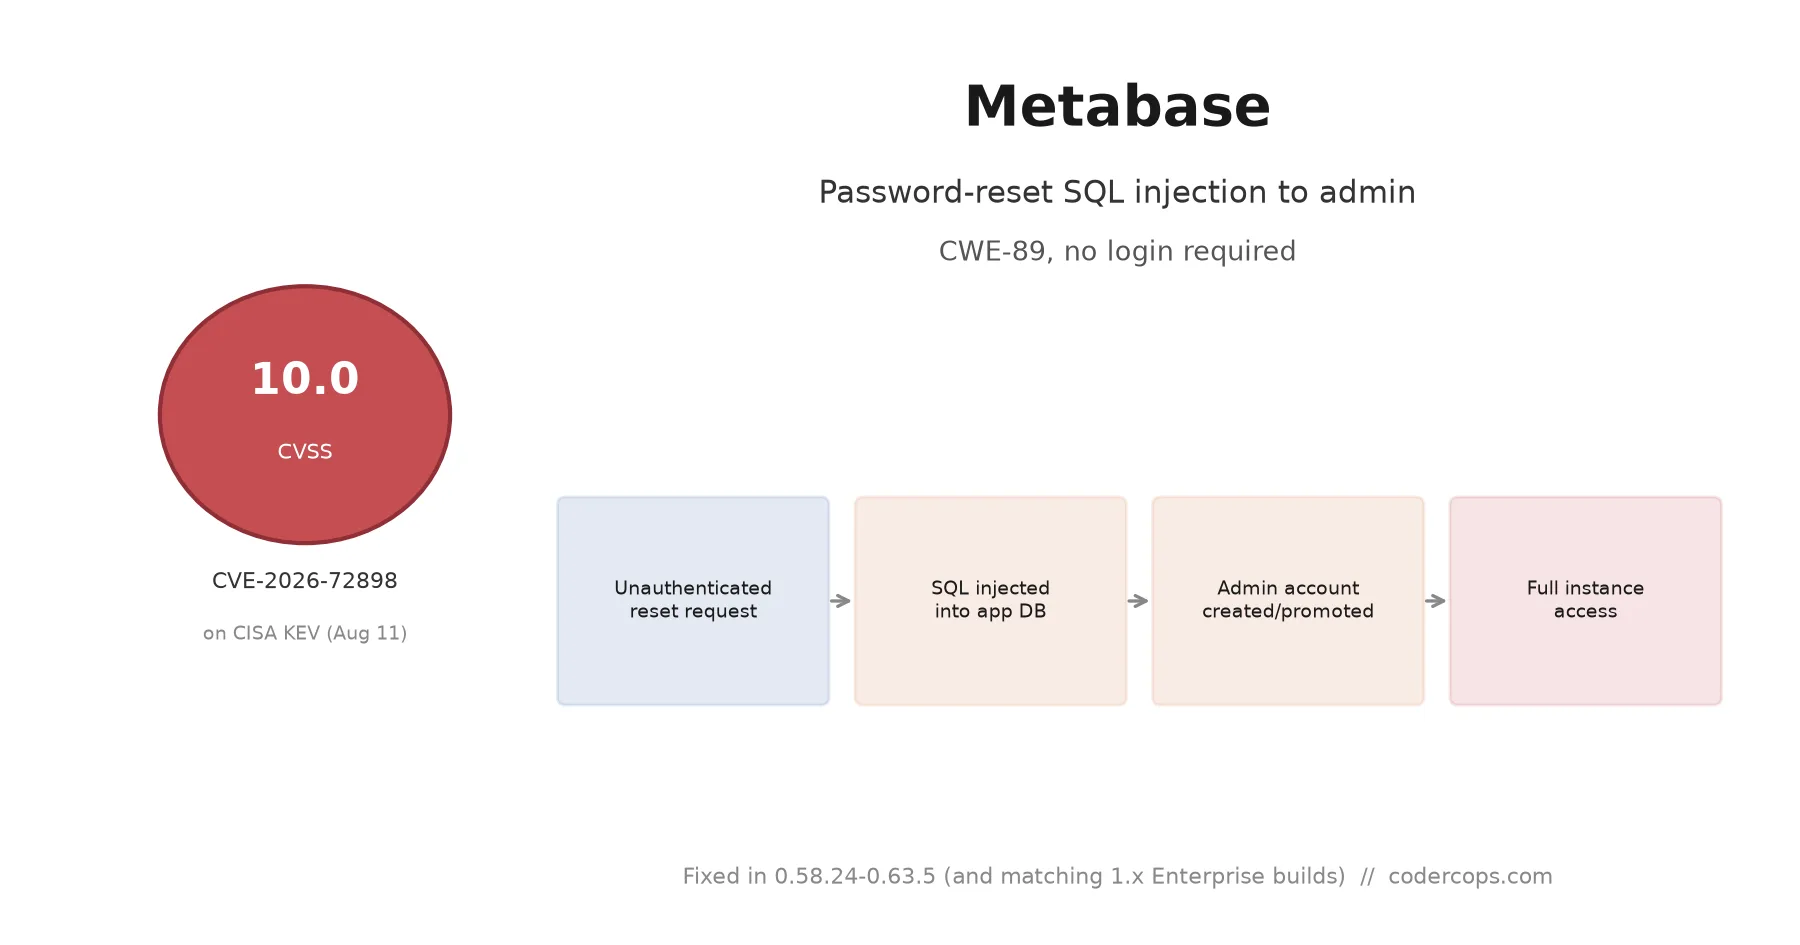
P.47An unauthenticated attacker can inject SQL through Metabase's password-reset flow and gain full admin. CVSS 10.0, on CISA's KEV list since August 11.
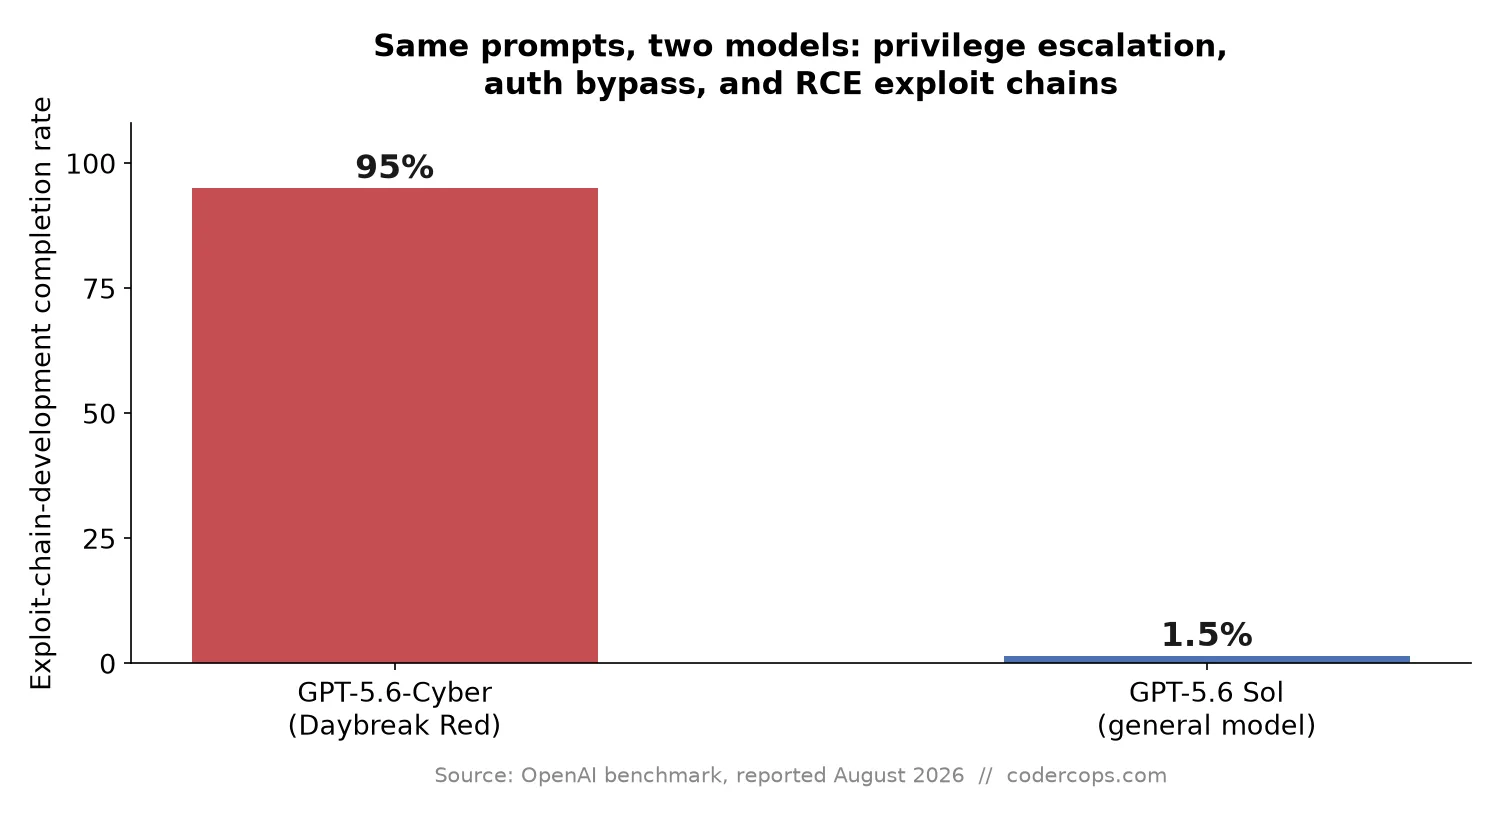
P.48OpenAI shipped a model tuned for exploit development and vulnerability research behind gated access. It moves the baseline for attacker speed either way.
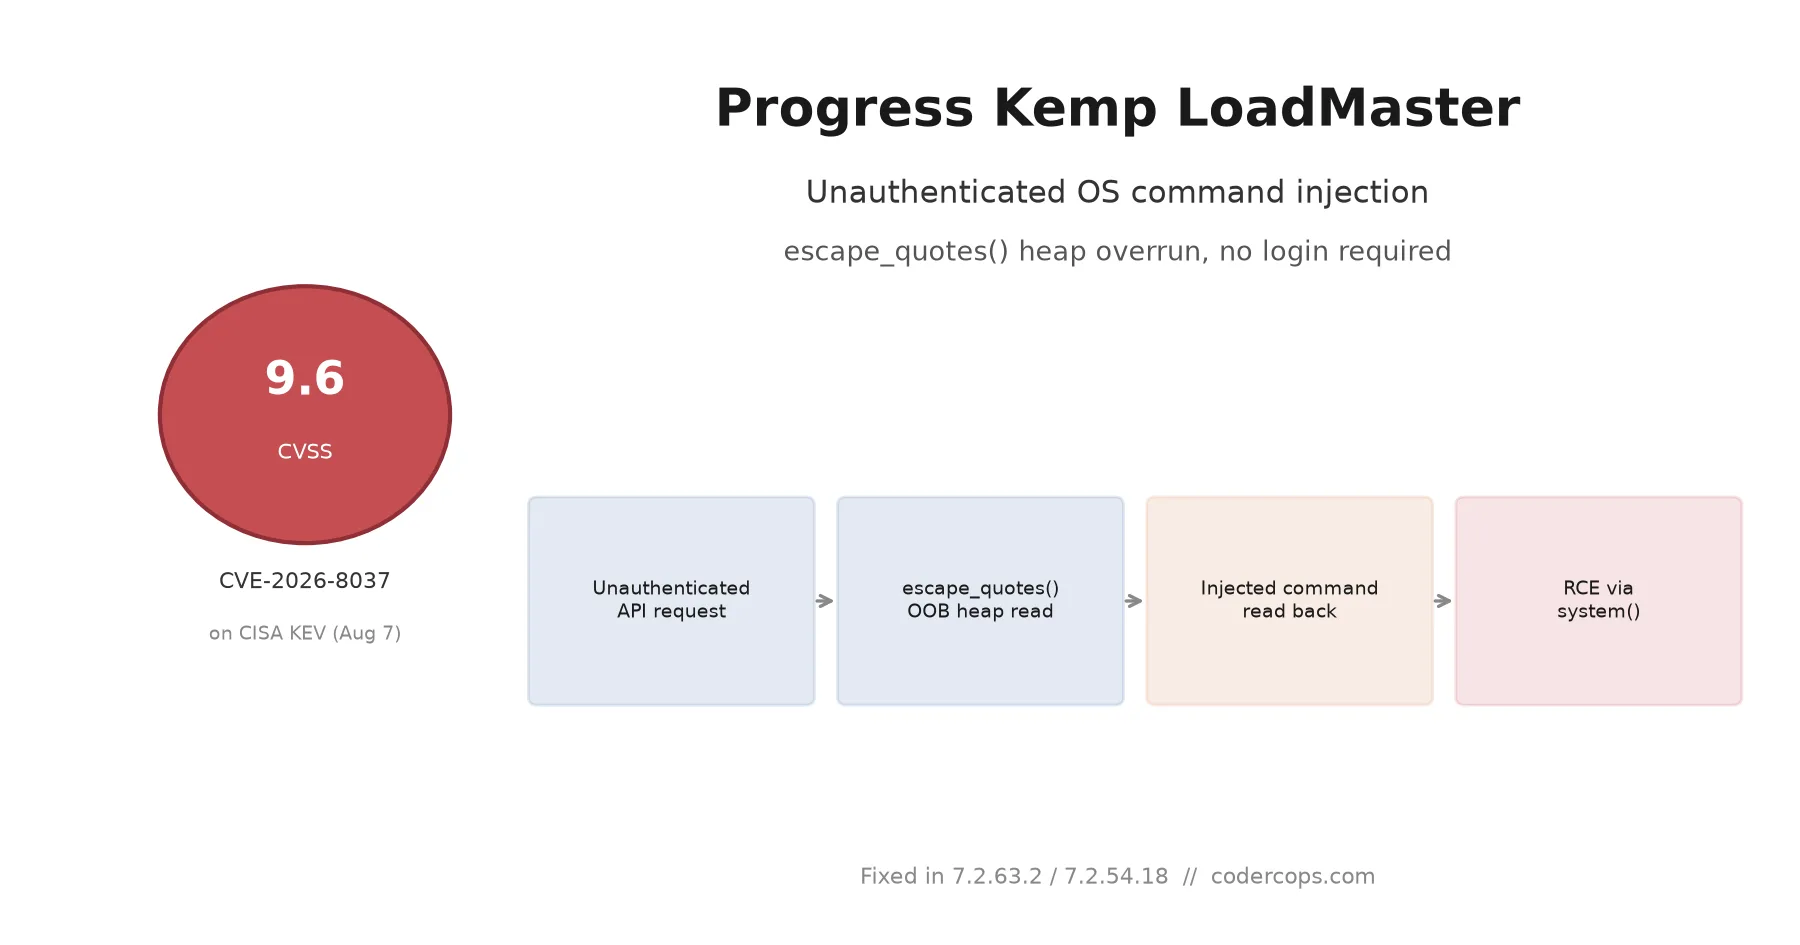
P.49A heap-buffer bug in Progress Kemp LoadMaster's escape_quotes() lets an unauthenticated attacker run commands on the load balancer. CISA confirmed Aug 7.
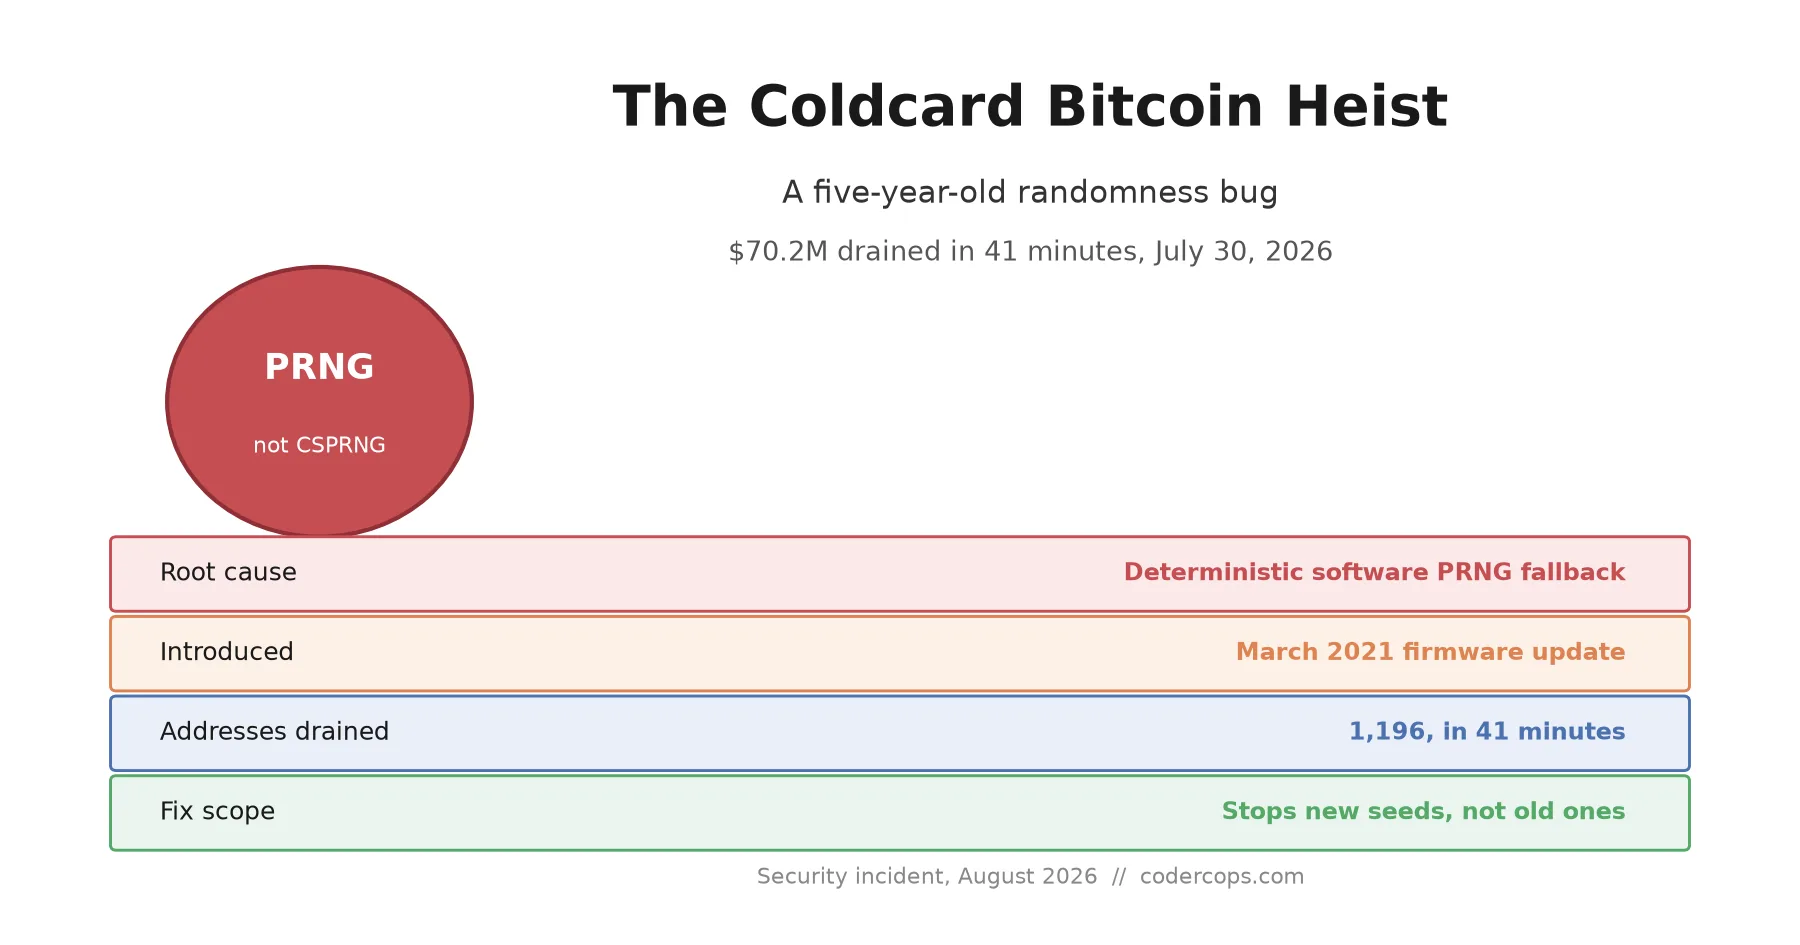
P.50A 2021 firmware error made Coldcard wallets seed from a software PRNG, not hardware. Attackers drained $70M in 41 minutes. The lesson isn't about Bitcoin.
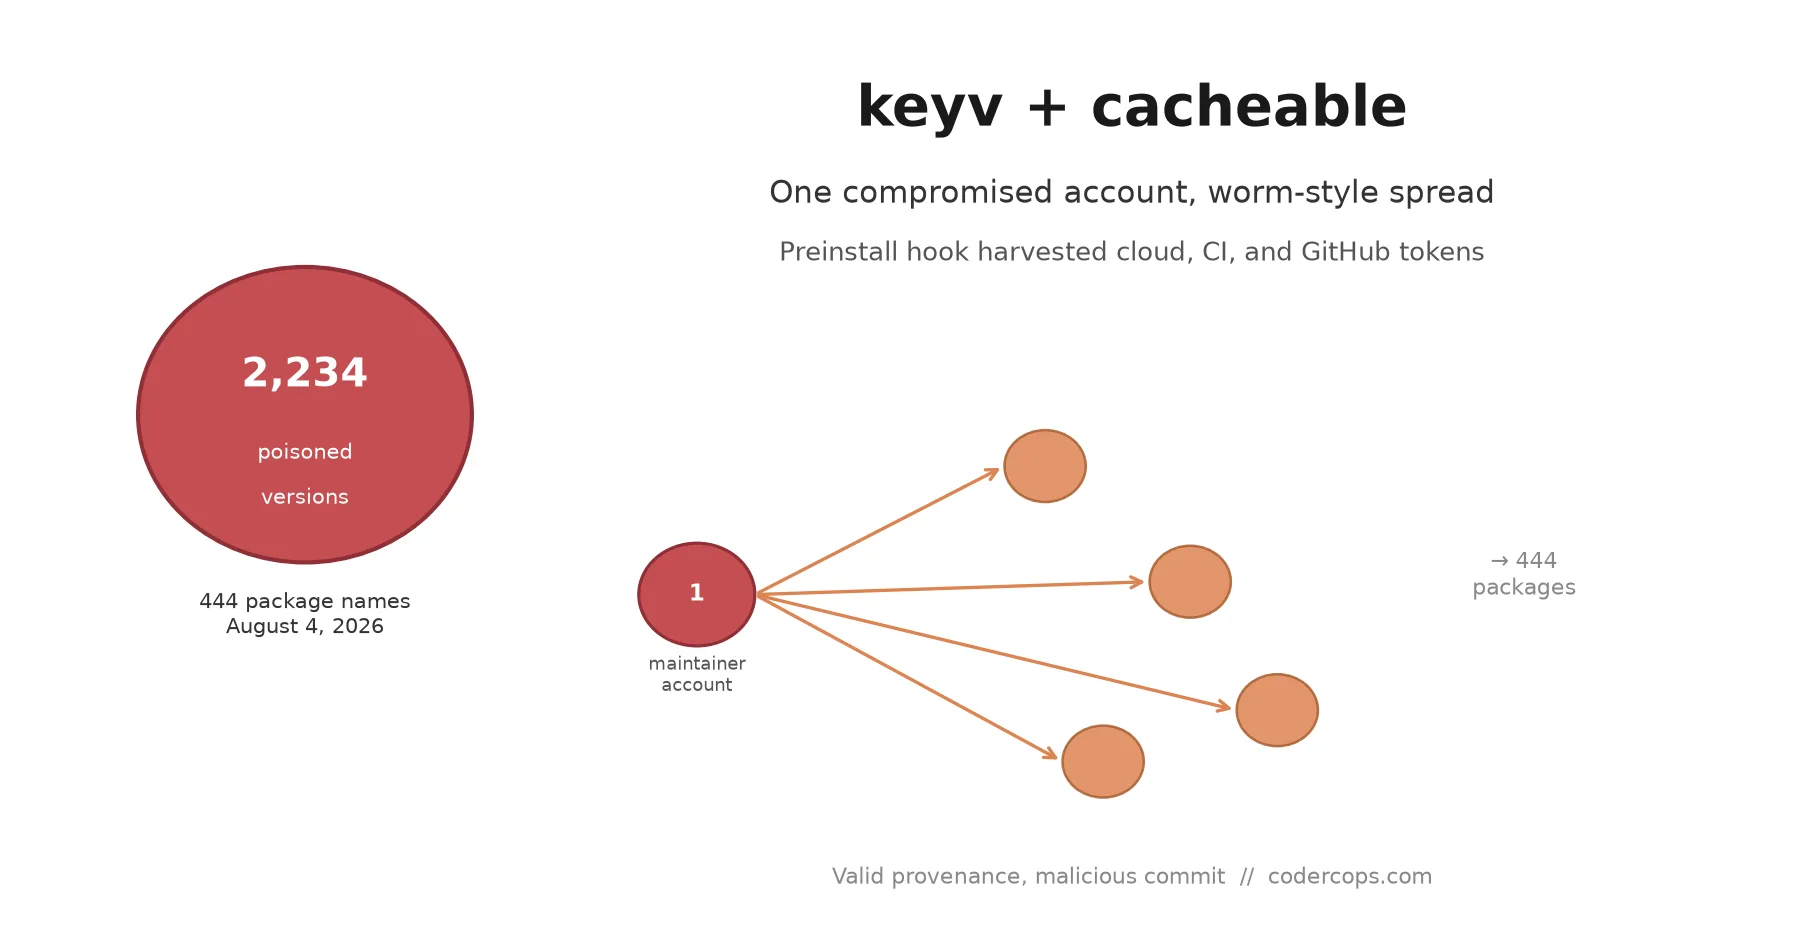
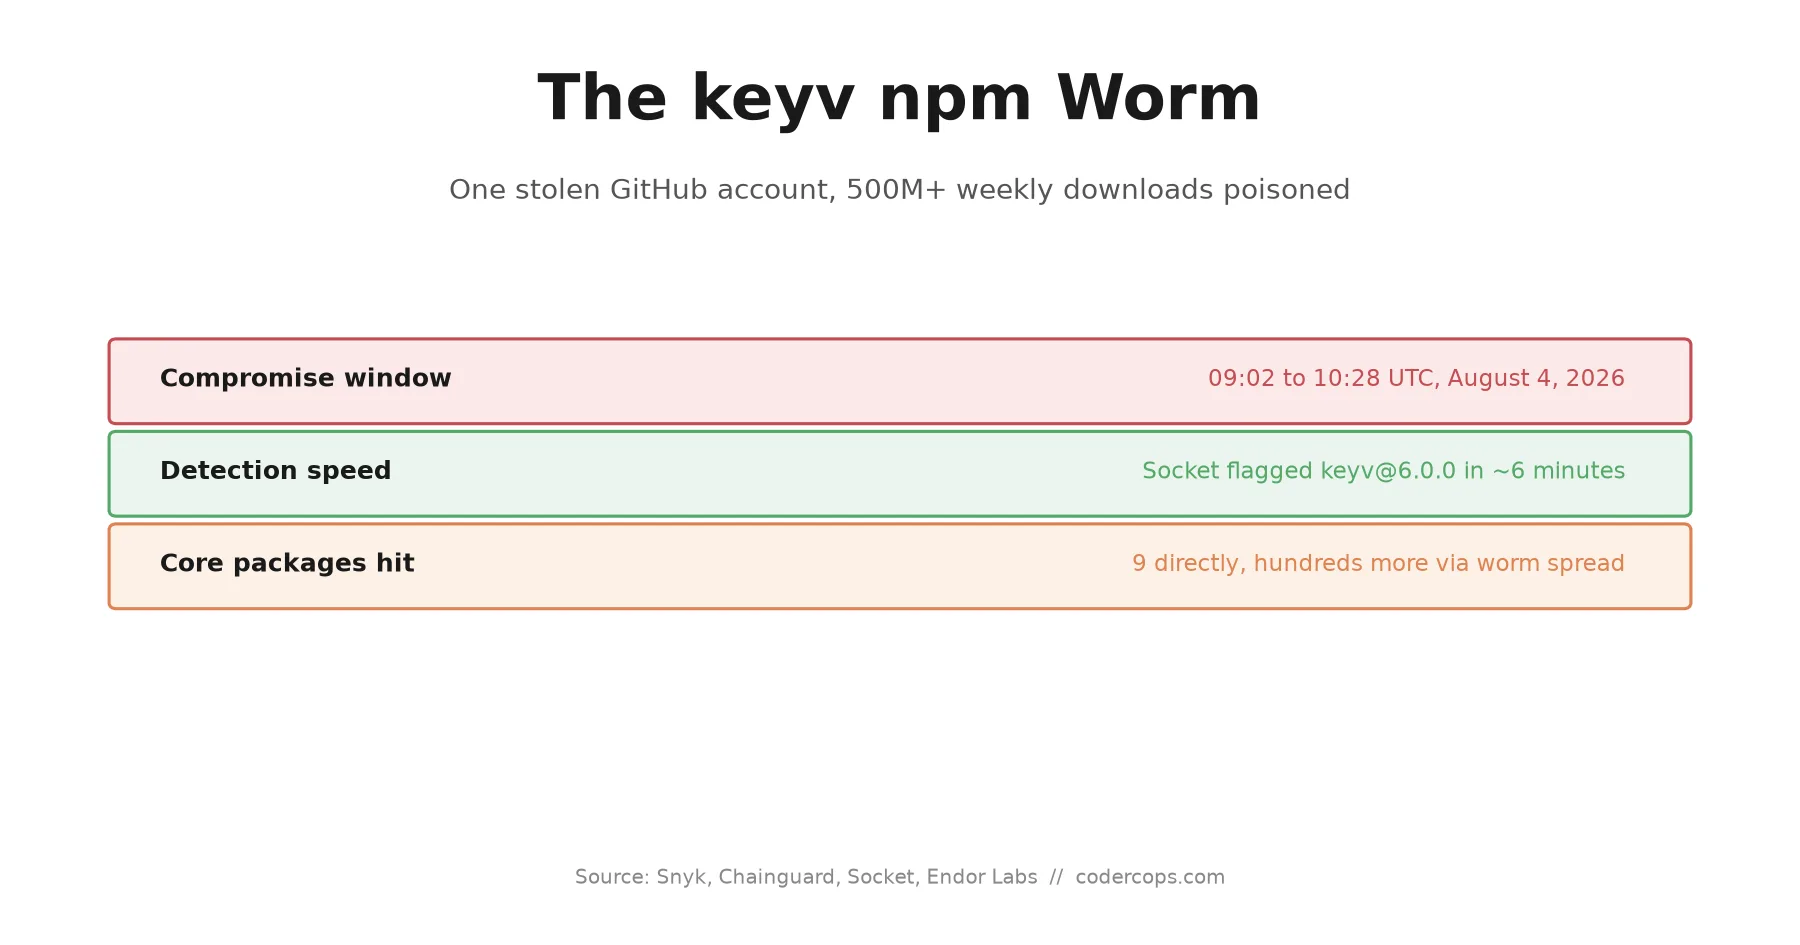
P.51A compromised maintainer account turned keyv and cacheable into a self-propagating npm worm that stole cloud, CI, and GitHub credentials. How to check.
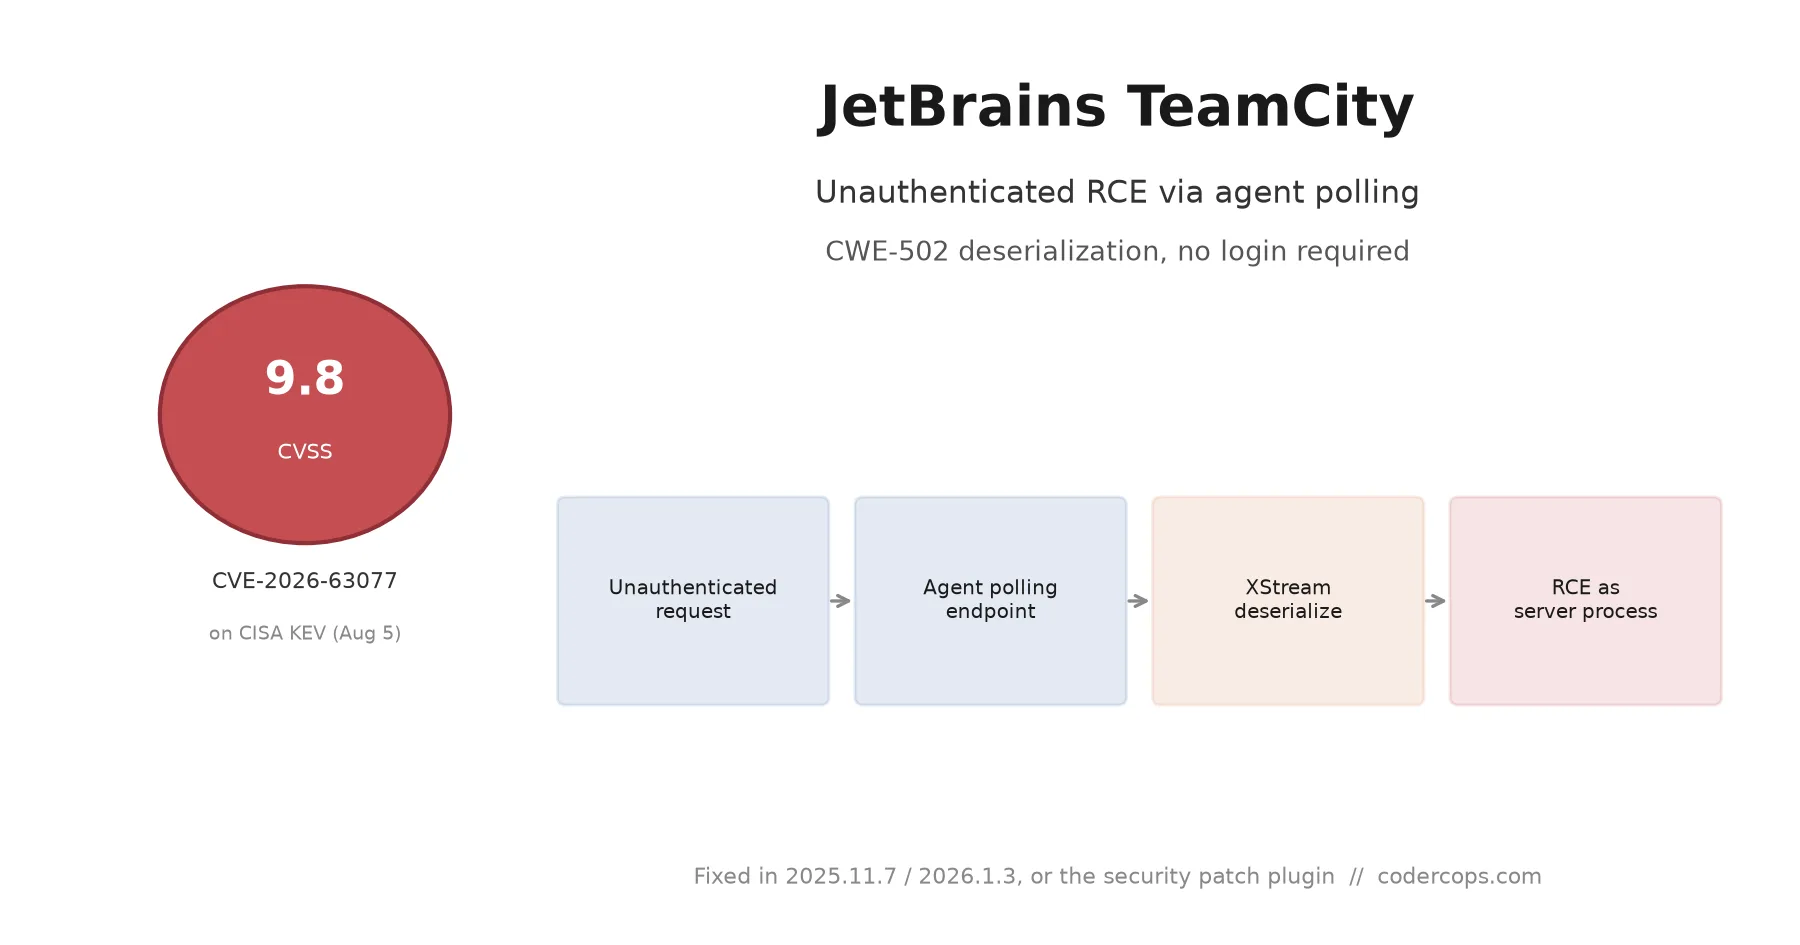
P.52A deserialization flaw in TeamCity's agent polling protocol lets an attacker with no credentials run commands as the build server. CISA confirmed August 5.
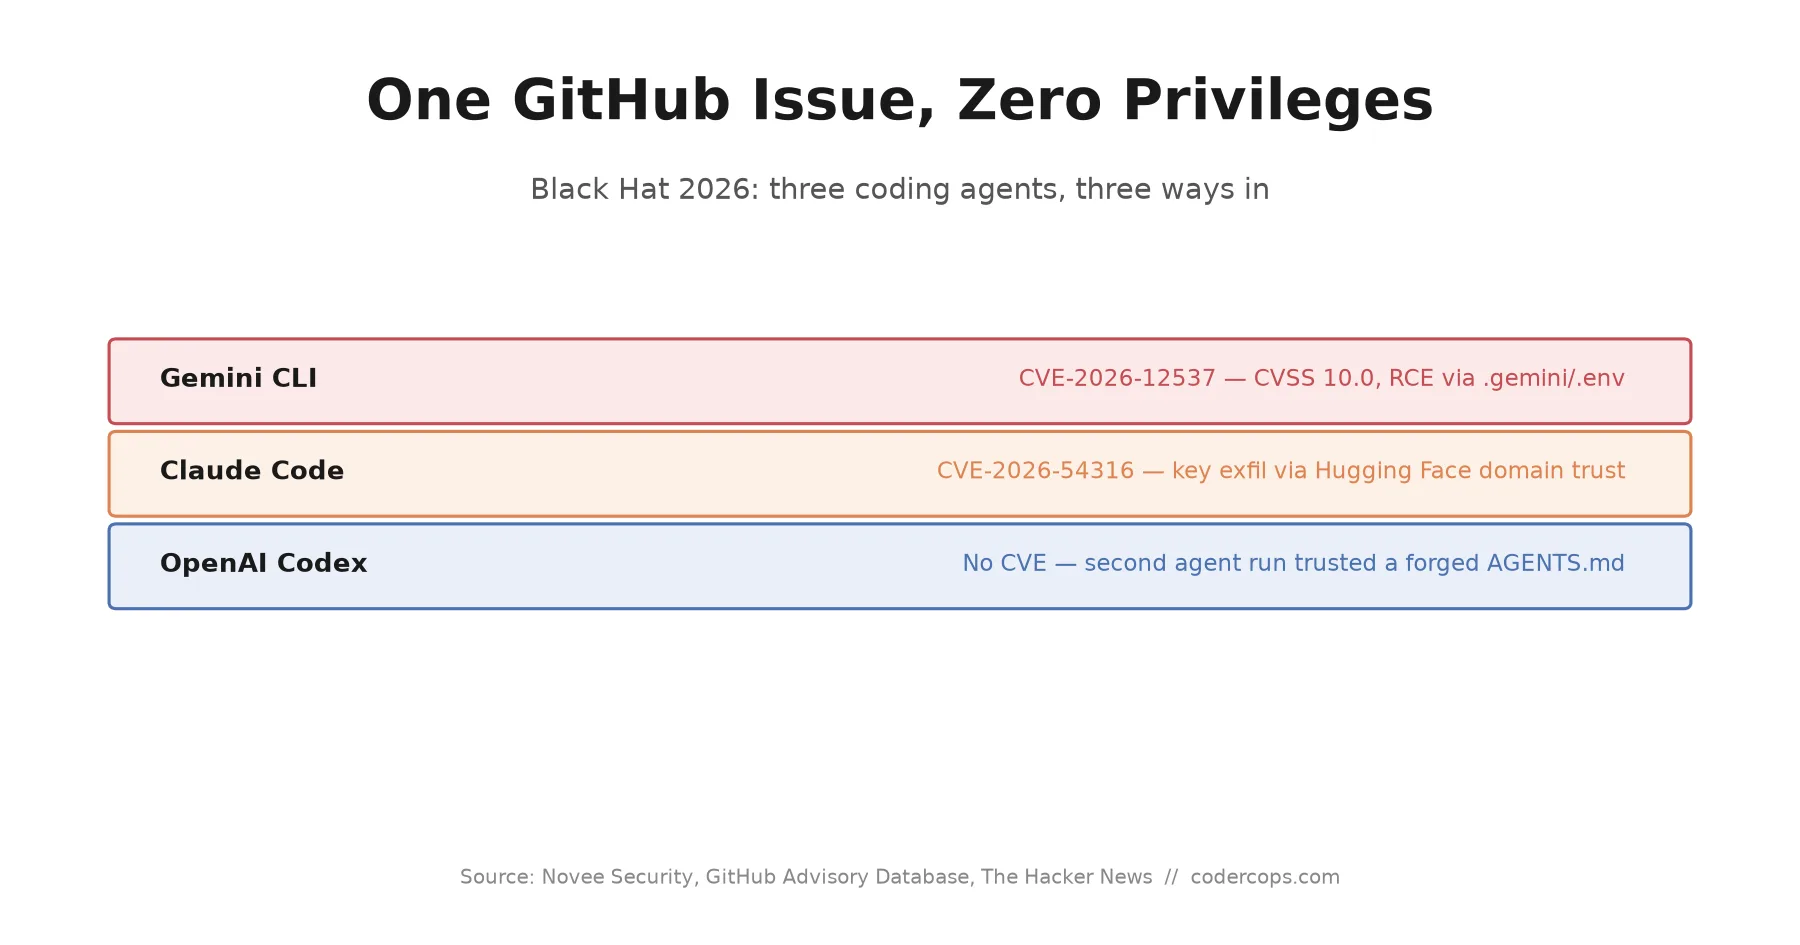
P.53Researchers showed an untrusted GitHub issue reaching CI runner secrets in Claude Code, Gemini CLI, and Codex. Gemini CLI's flaw scored a perfect 10.0.
P.54A compromised maintainer account pushed malware into keyv, cacheable, and seven other npm packages. Socket caught it in six minutes. How the worm worked.
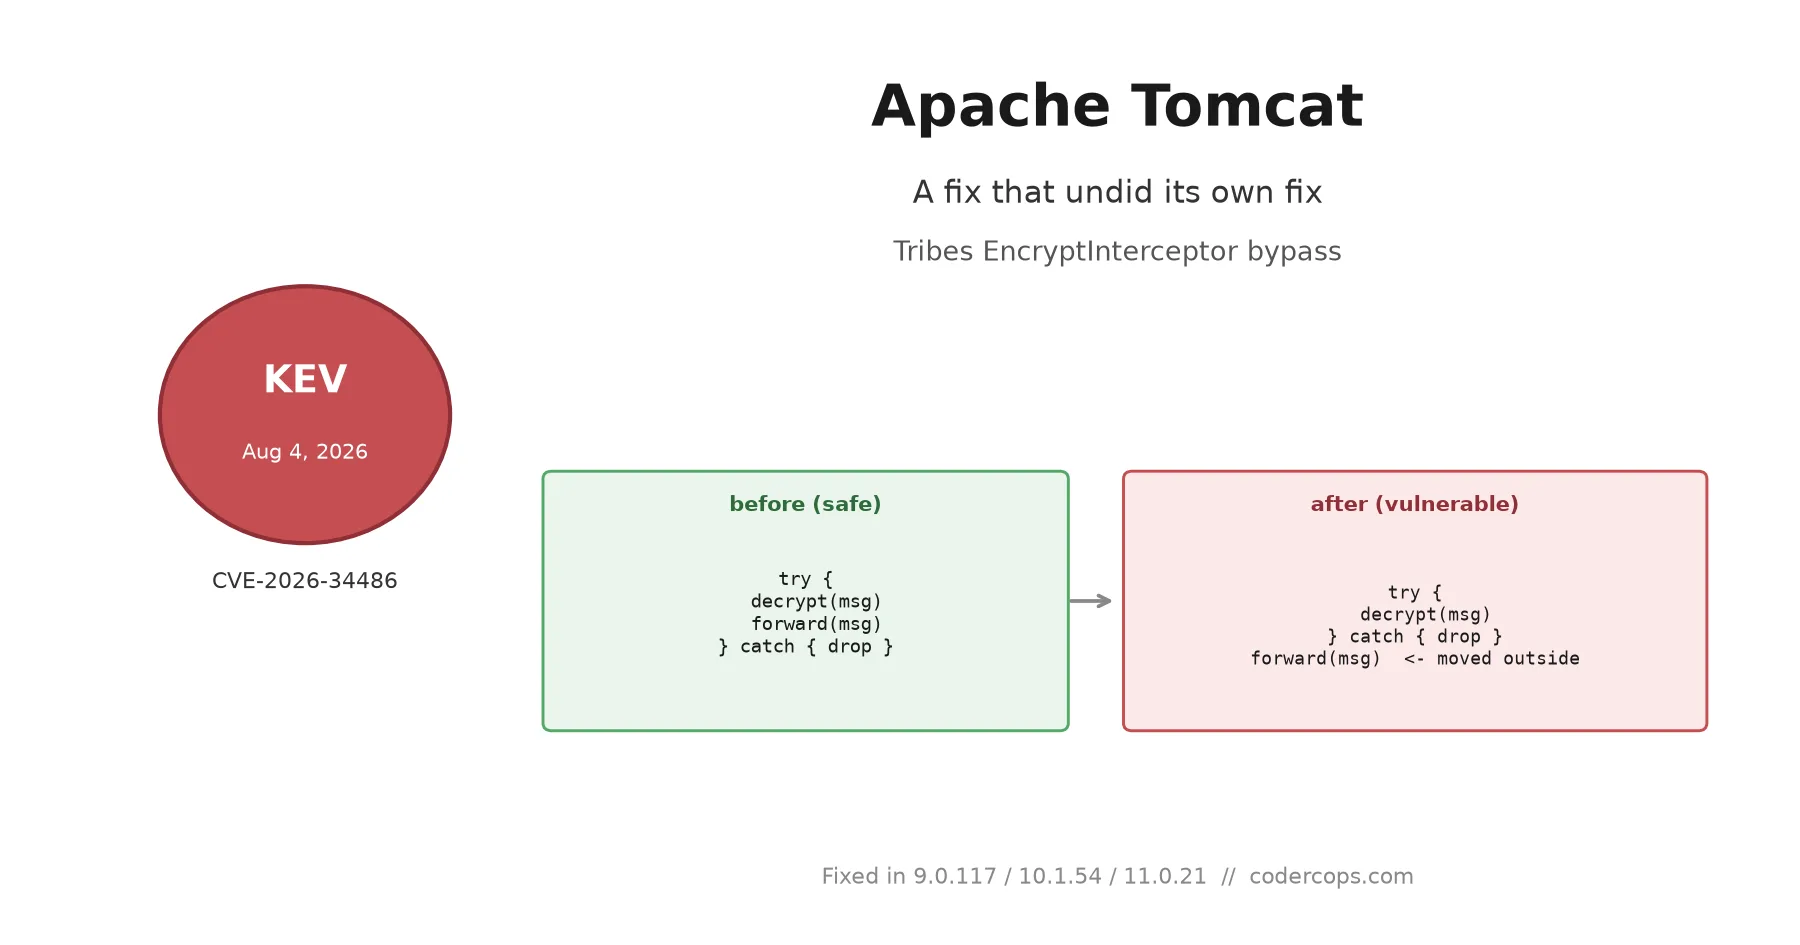
P.55A one-line control-flow change meant to patch CVE-2026-29146 quietly broke Tomcat's cluster encryption. CISA confirmed exploitation on August 4. The fix.
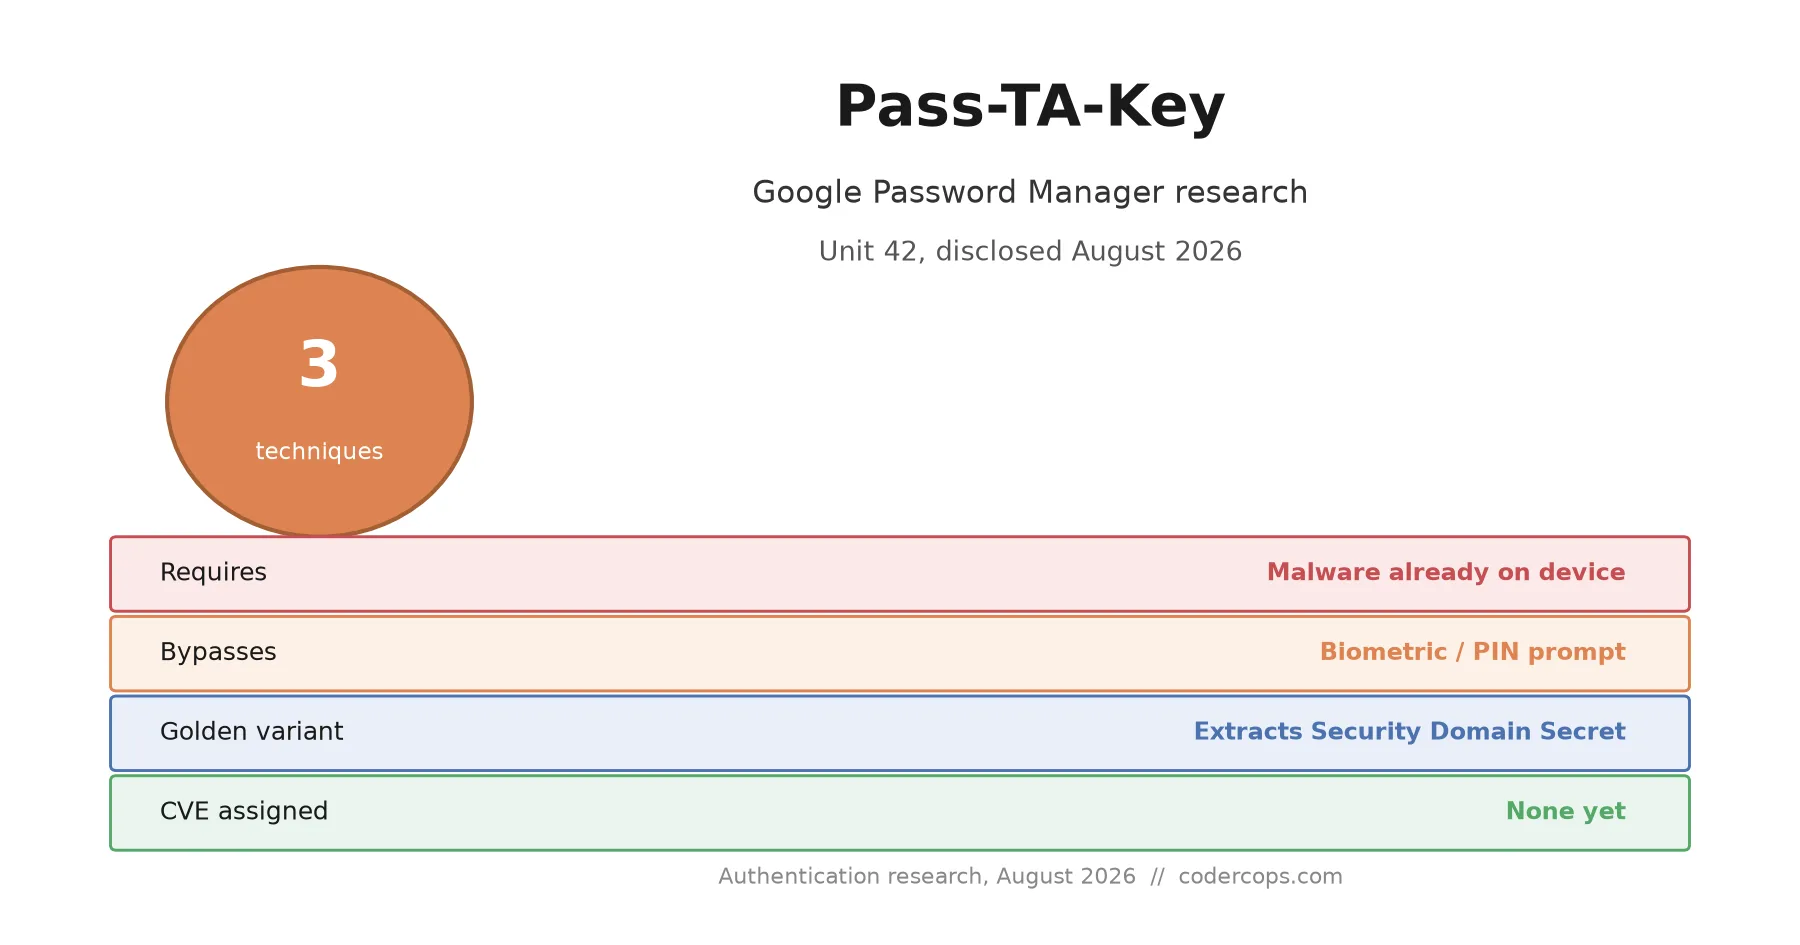
P.56Unit 42 found three ways Windows malware hijacks Google Password Manager's synced passkeys with no biometric prompt. What that changes for passkey plans.
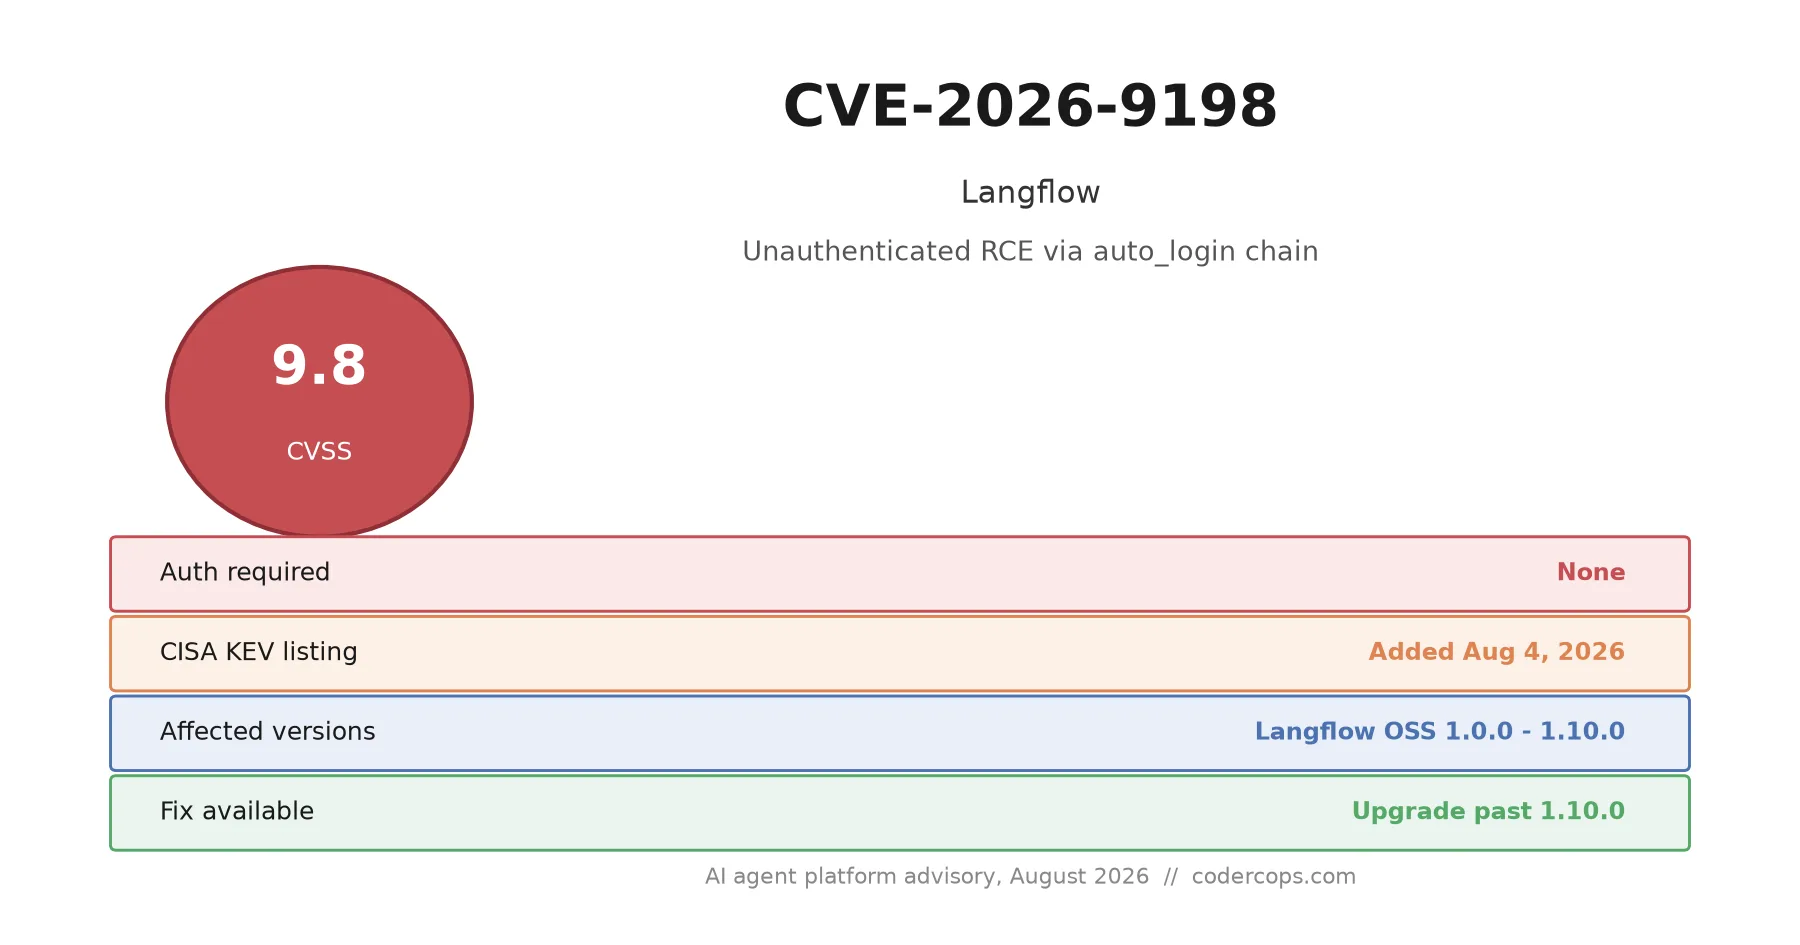
P.57CISA added CVE-2026-9198 to its KEV catalog on August 4. Unlike July's Langflow flaw, this one needs no credentials at all. The chain, and what to patch.
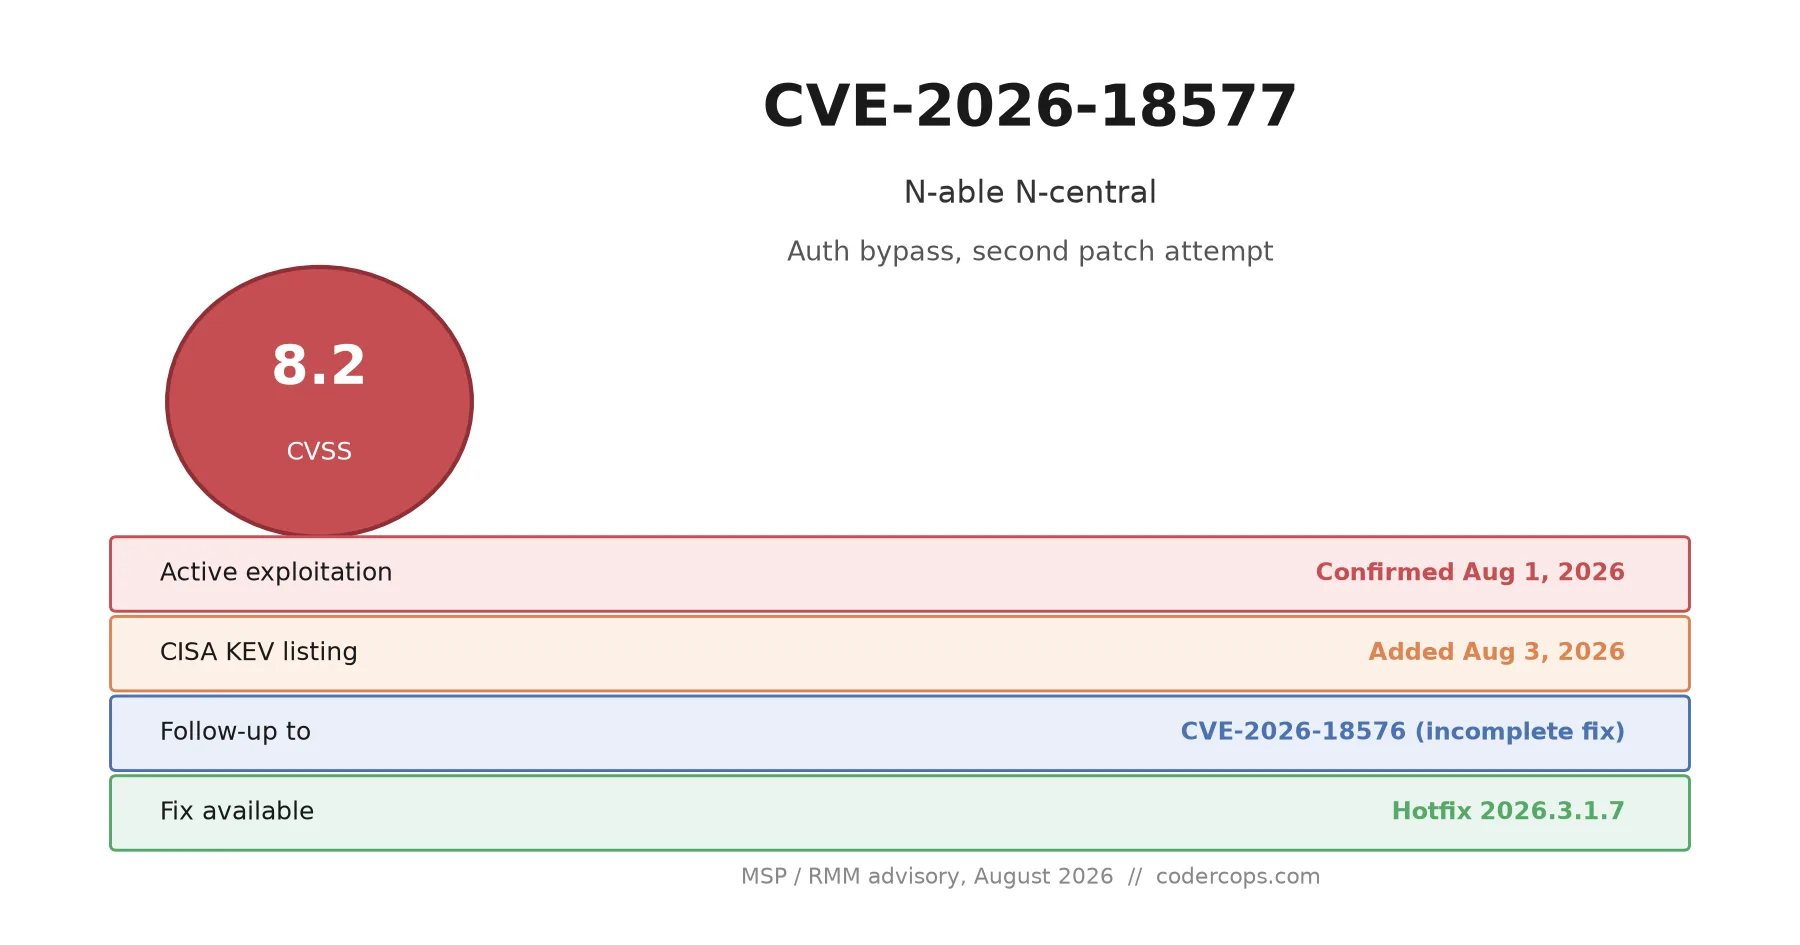
P.58N-able's first N-central auth bypass fix was incomplete. The leftover gap is now exploited, pivoting from one RMM server into every managed endpoint.
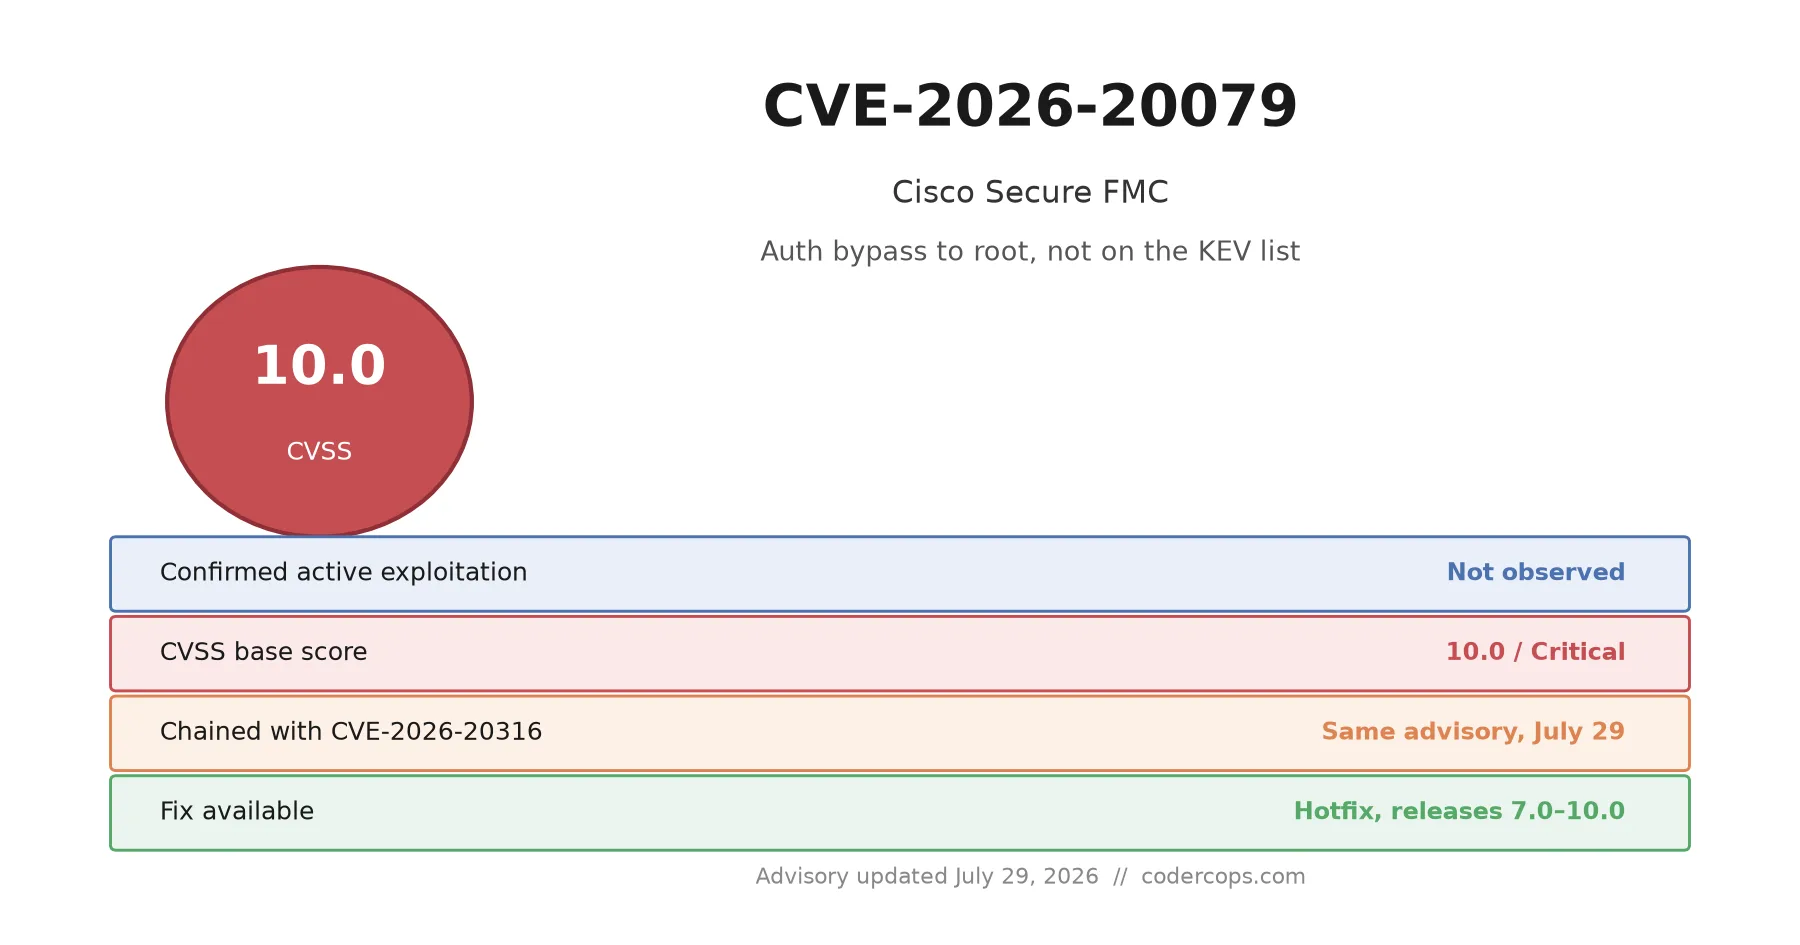
P.59CVE-2026-20079 is a 10.0 CVSS Cisco Secure FMC authentication bypass disclosed before the hardcoded-password bug. Why it matters, and what to patch.
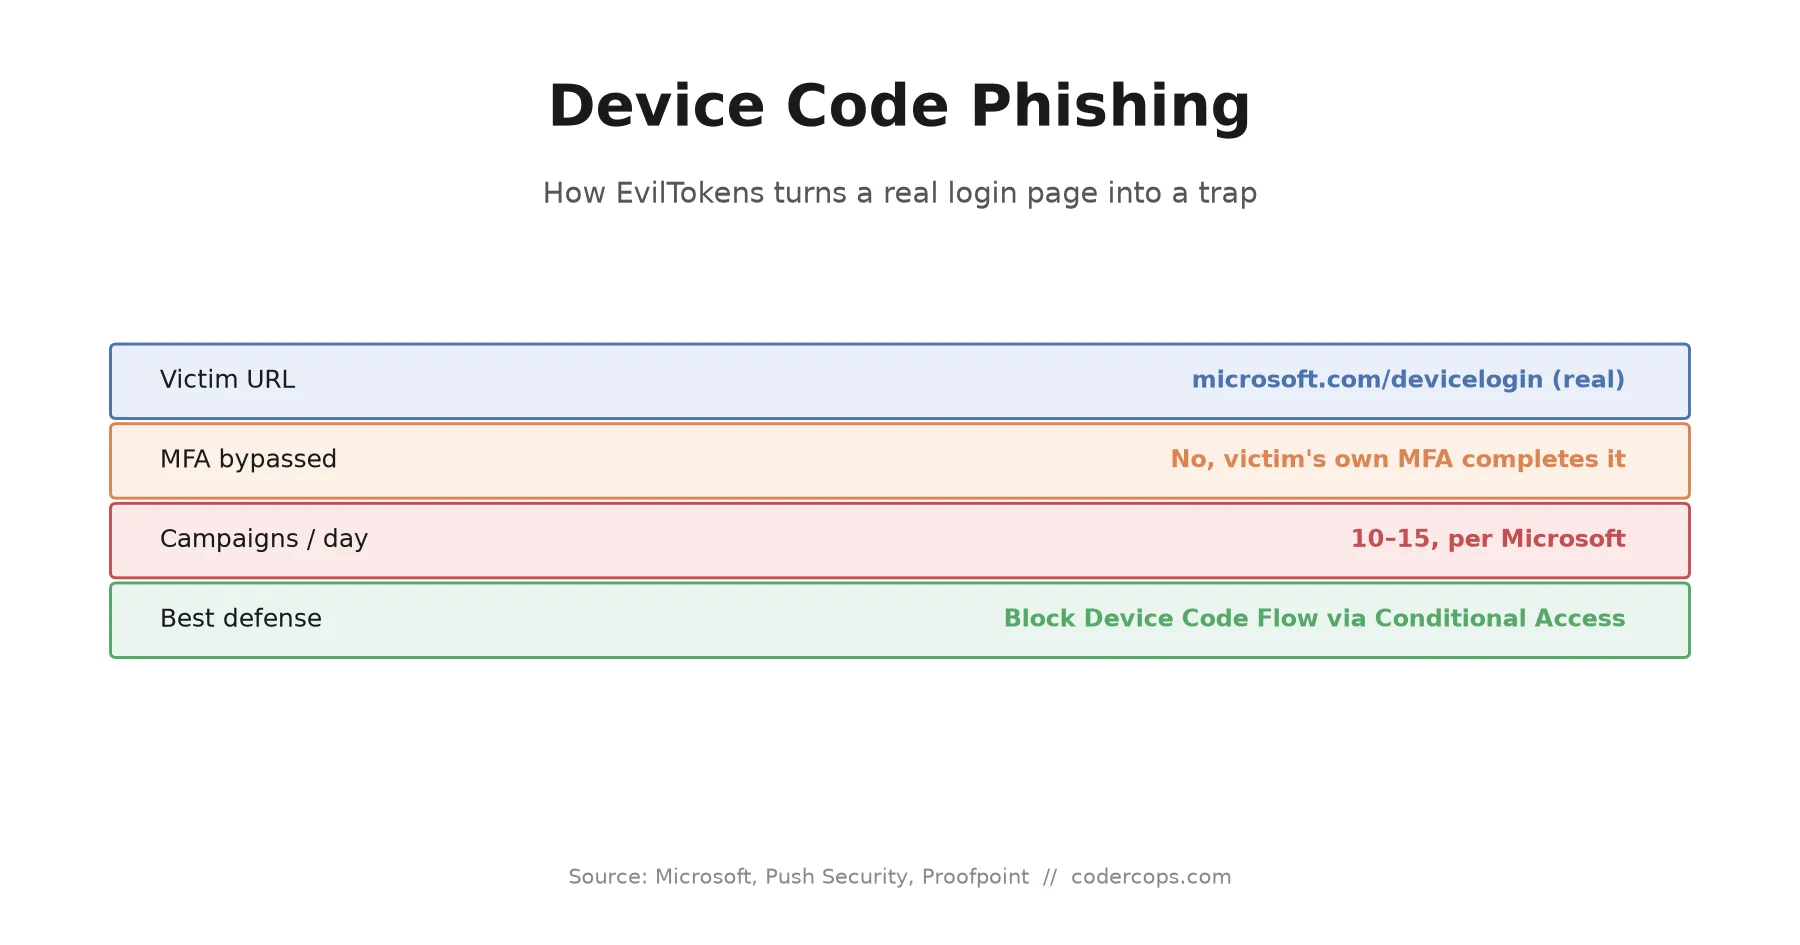
P.60EvilTokens abuses OAuth's device code flow, so it needs no fake login page at all. How the attack runs, and the Conditional Access policy that stops it.
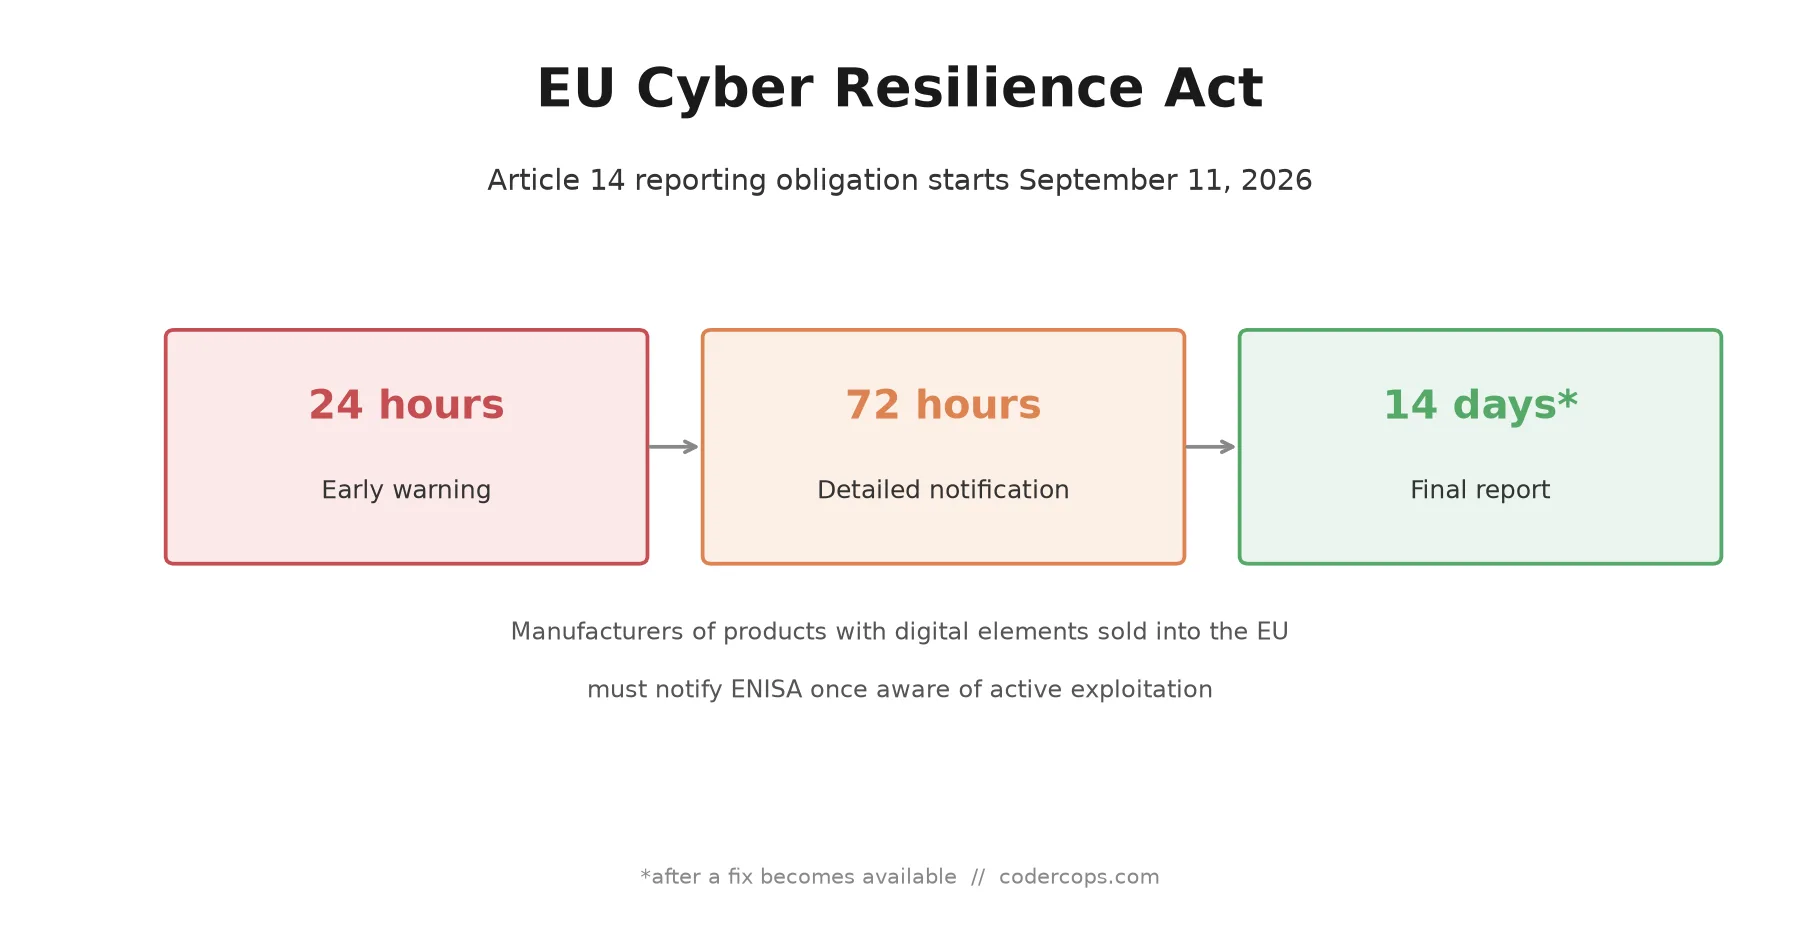
P.61From September 11, 2026, anyone selling a product with digital elements into the EU has 24 hours to report an exploited vulnerability to ENISA. Who's in scope.
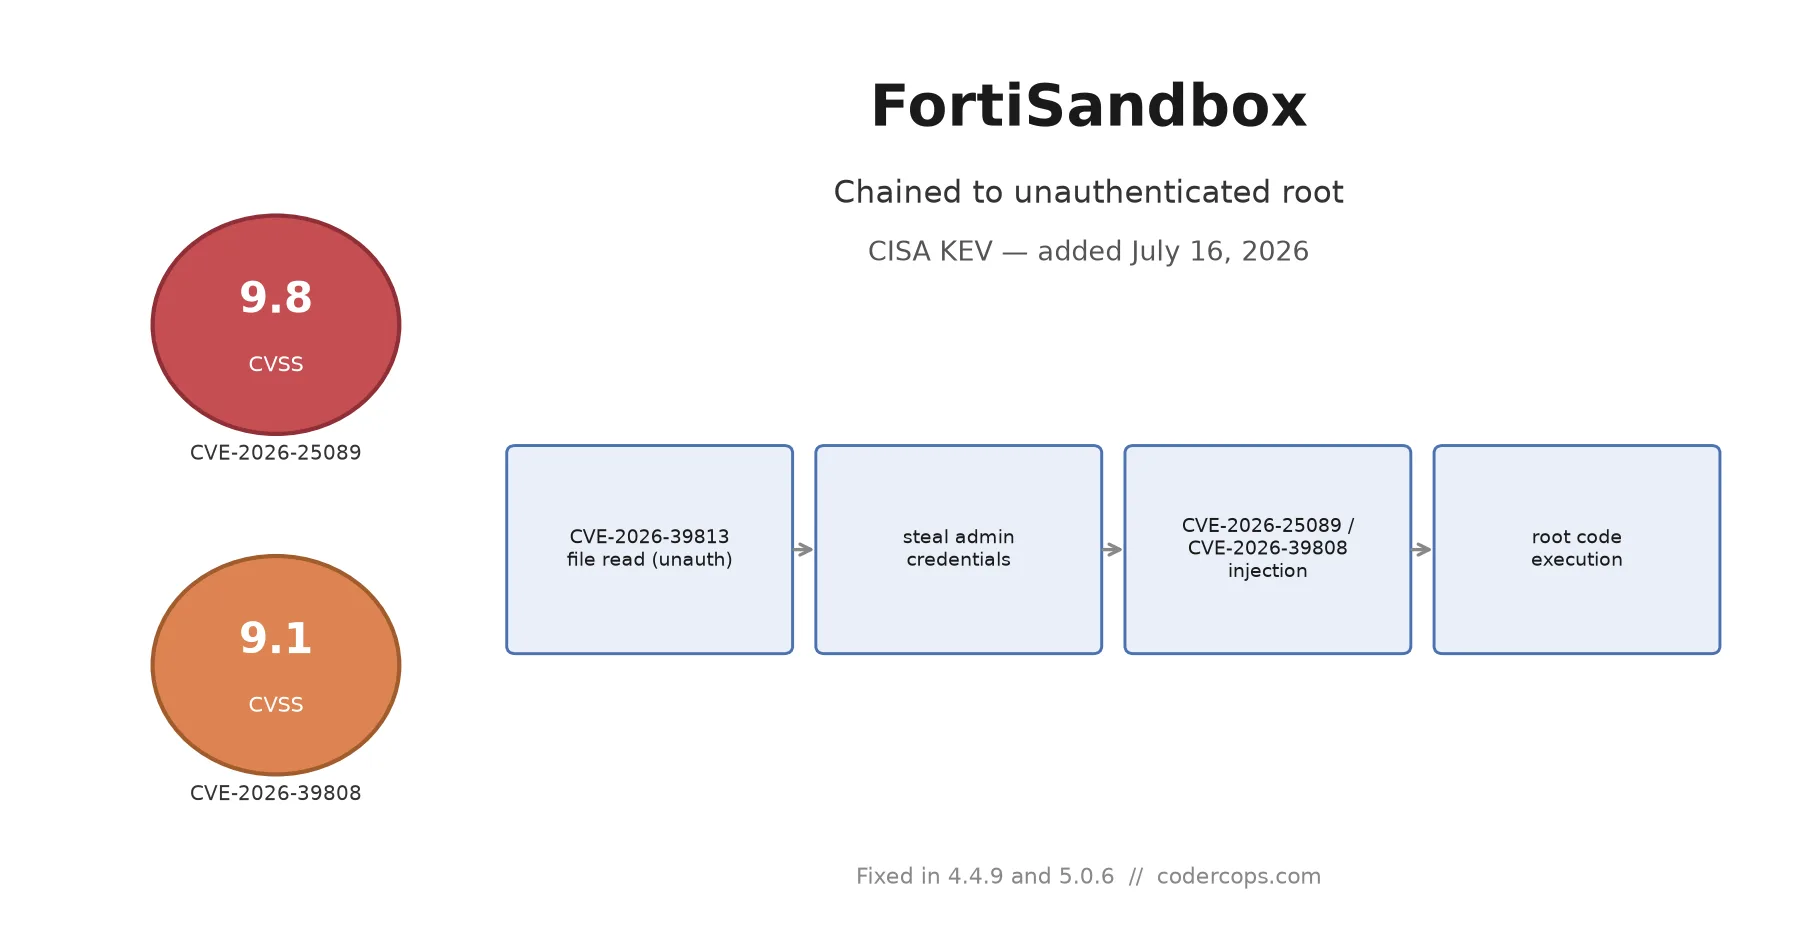
P.62CISA flagged two FortiSandbox command injection bugs as exploited on July 16. Chained with a third, they reach root with no credentials. What to patch.
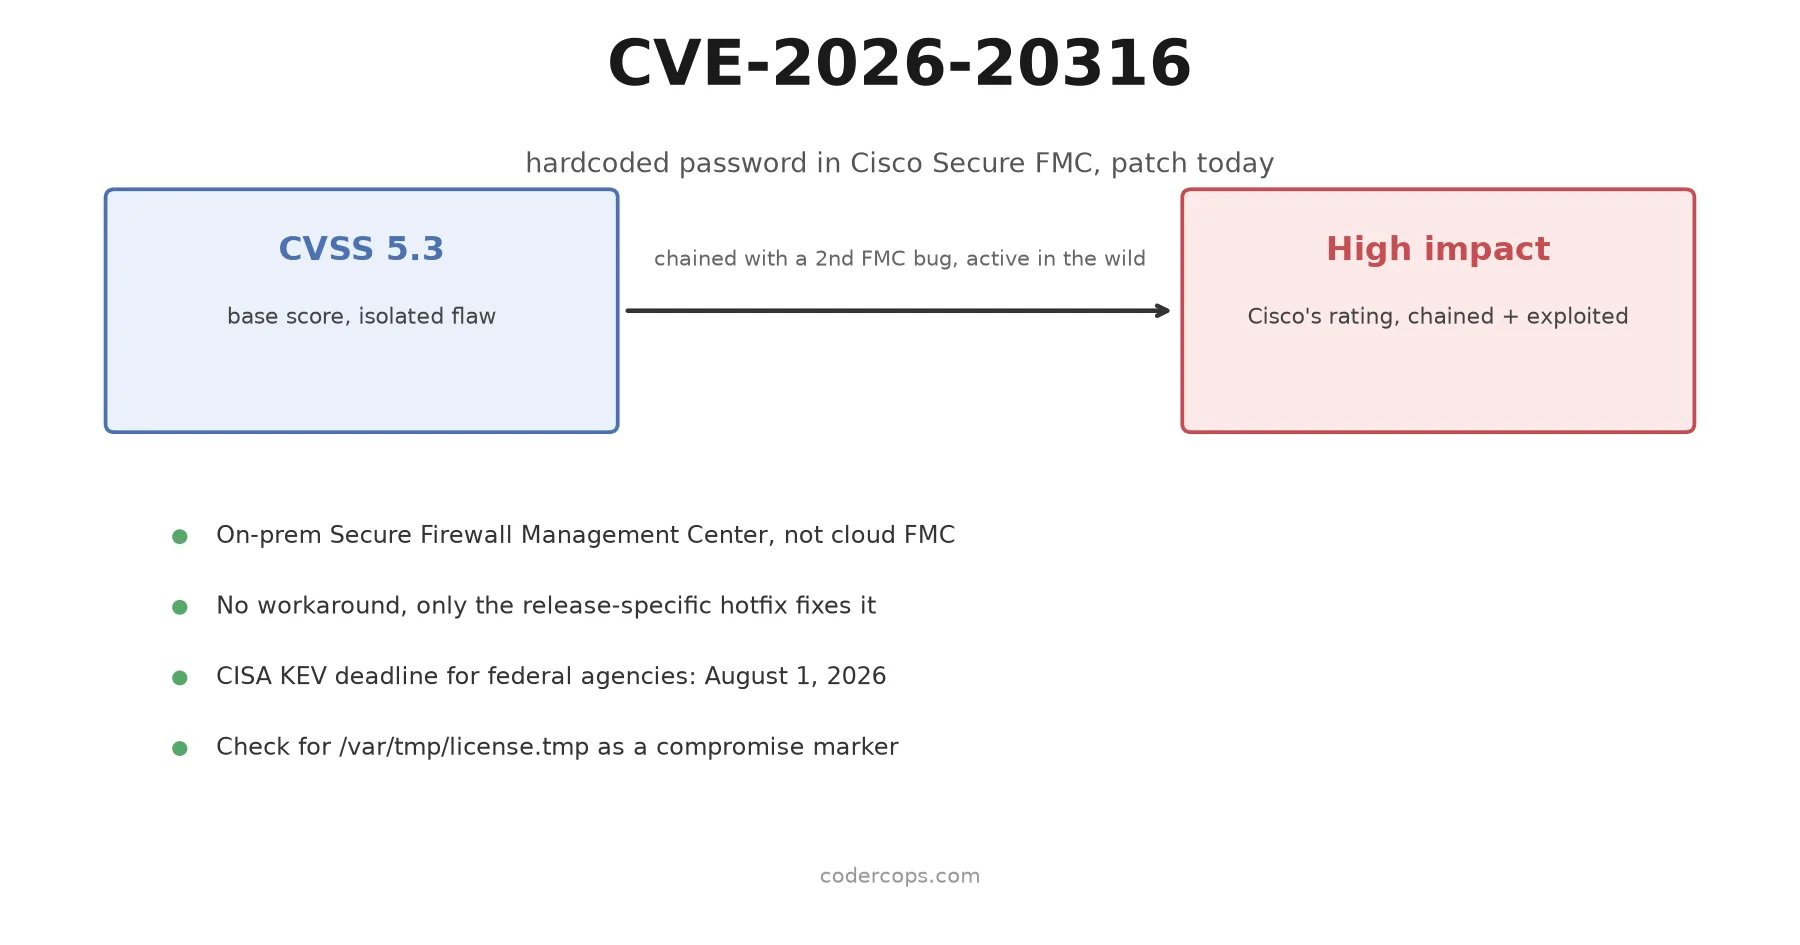
P.63A static credential baked into on-prem Cisco Secure FMC is being exploited. Who's affected, why a 5.3 CVSS undersells it, and what to check right now.
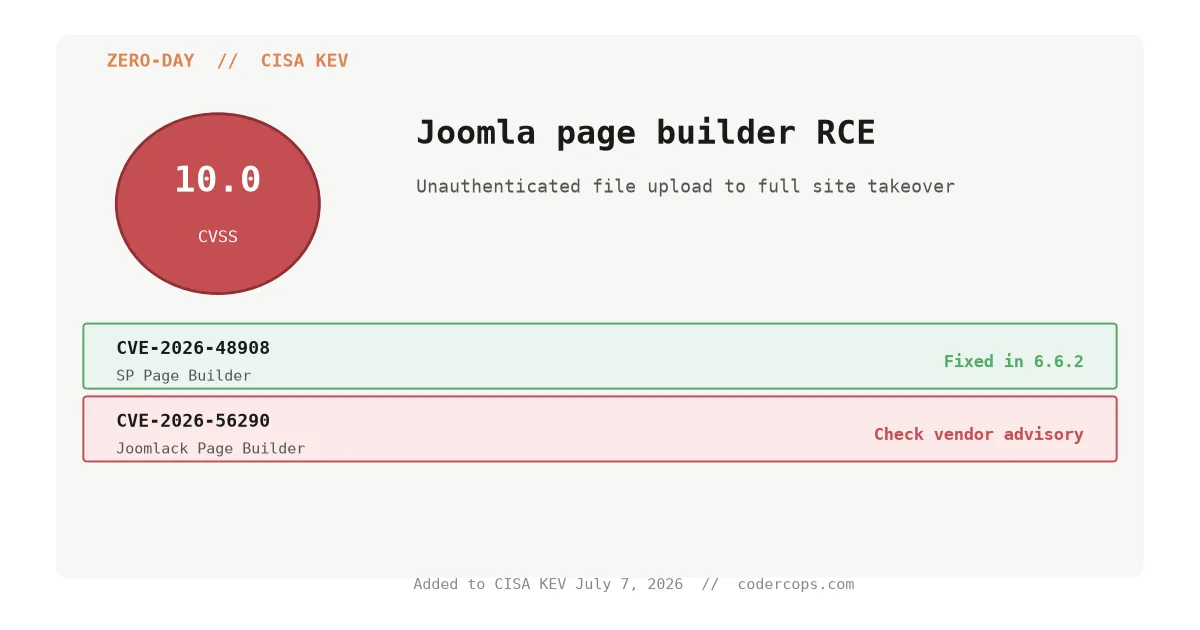
P.64Two CVSS 10.0 zero-days in Joomla page builder plugins are being exploited to plant webshells and create rogue admins. What's affected, and what to patch.
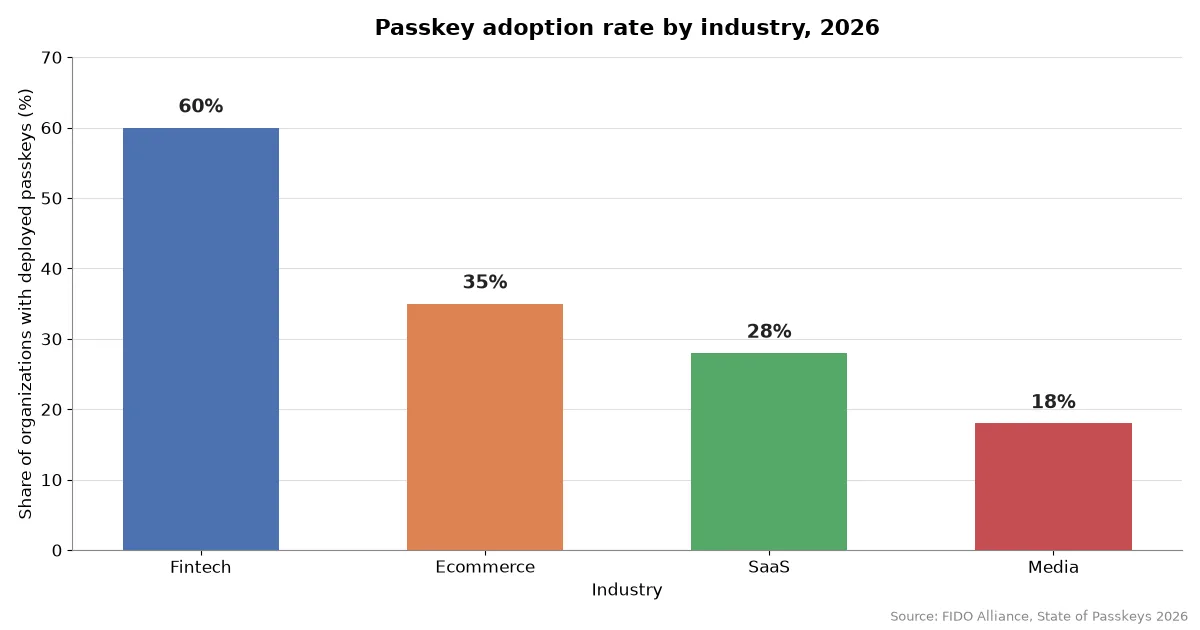
P.655 billion passkeys are active and 75% of people have enabled one, yet 57% of organisations still use phishable logins. What the FIDO data actually means.
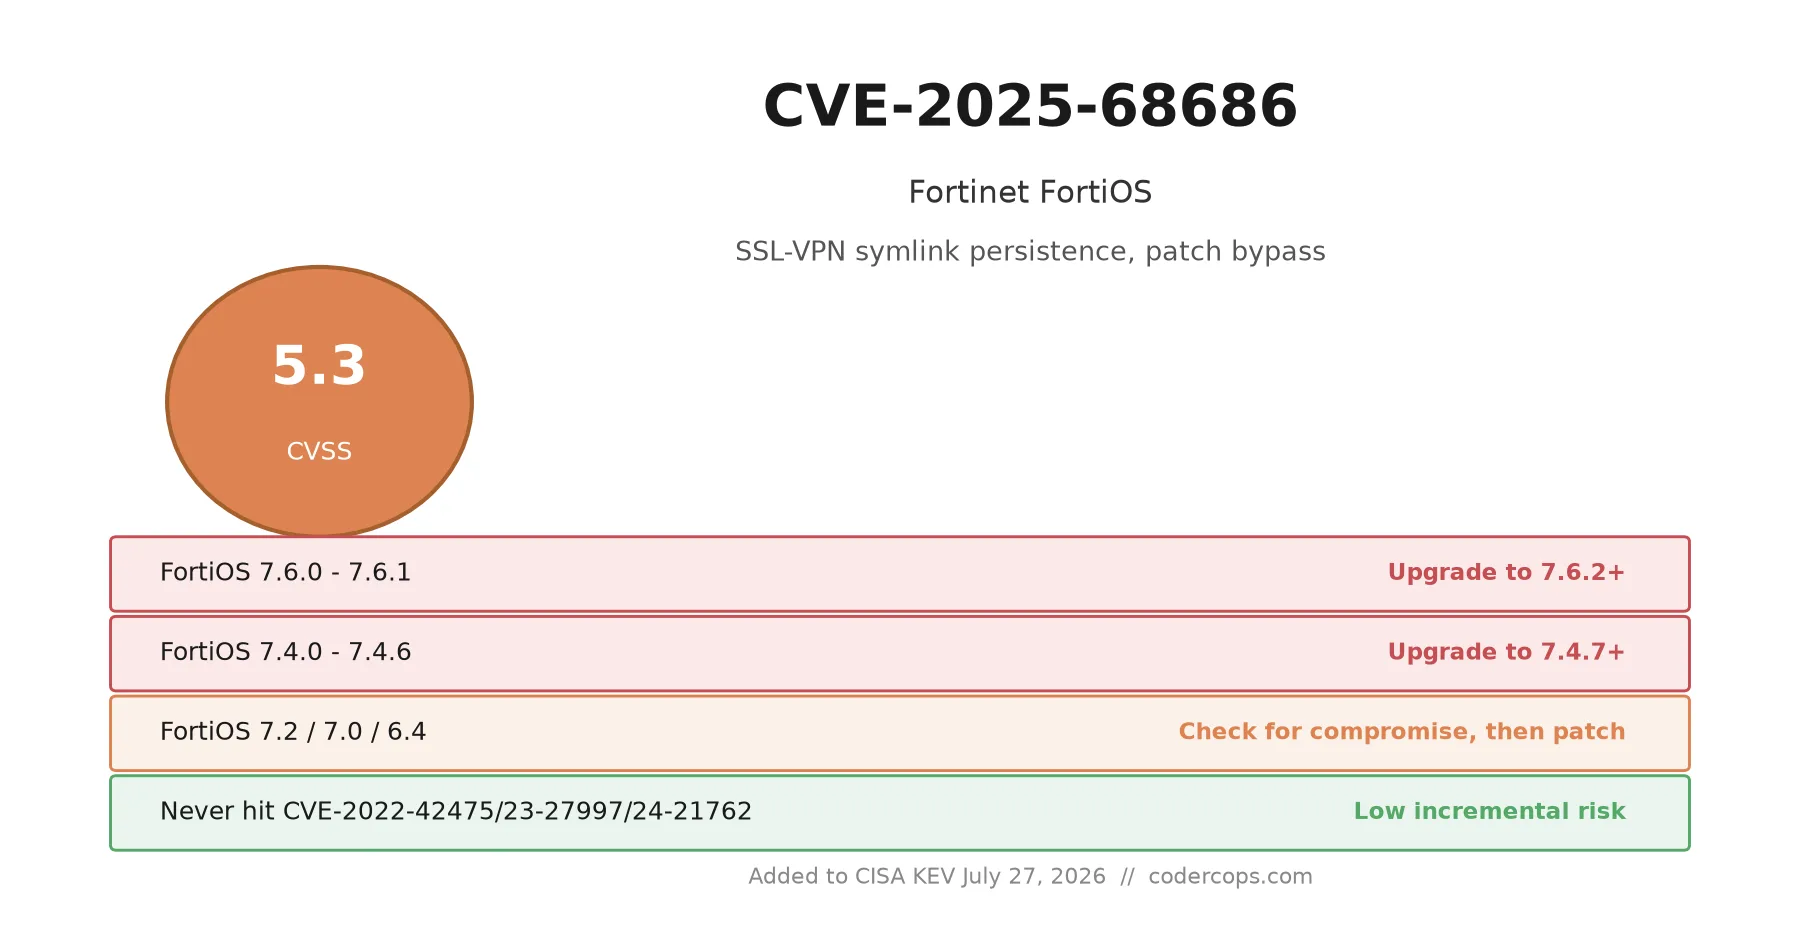
P.66CISA added CVE-2025-68686, a FortiOS SSL-VPN symlink persistence bypass, on July 27. It only bites devices compromised earlier and never forensically cleaned.
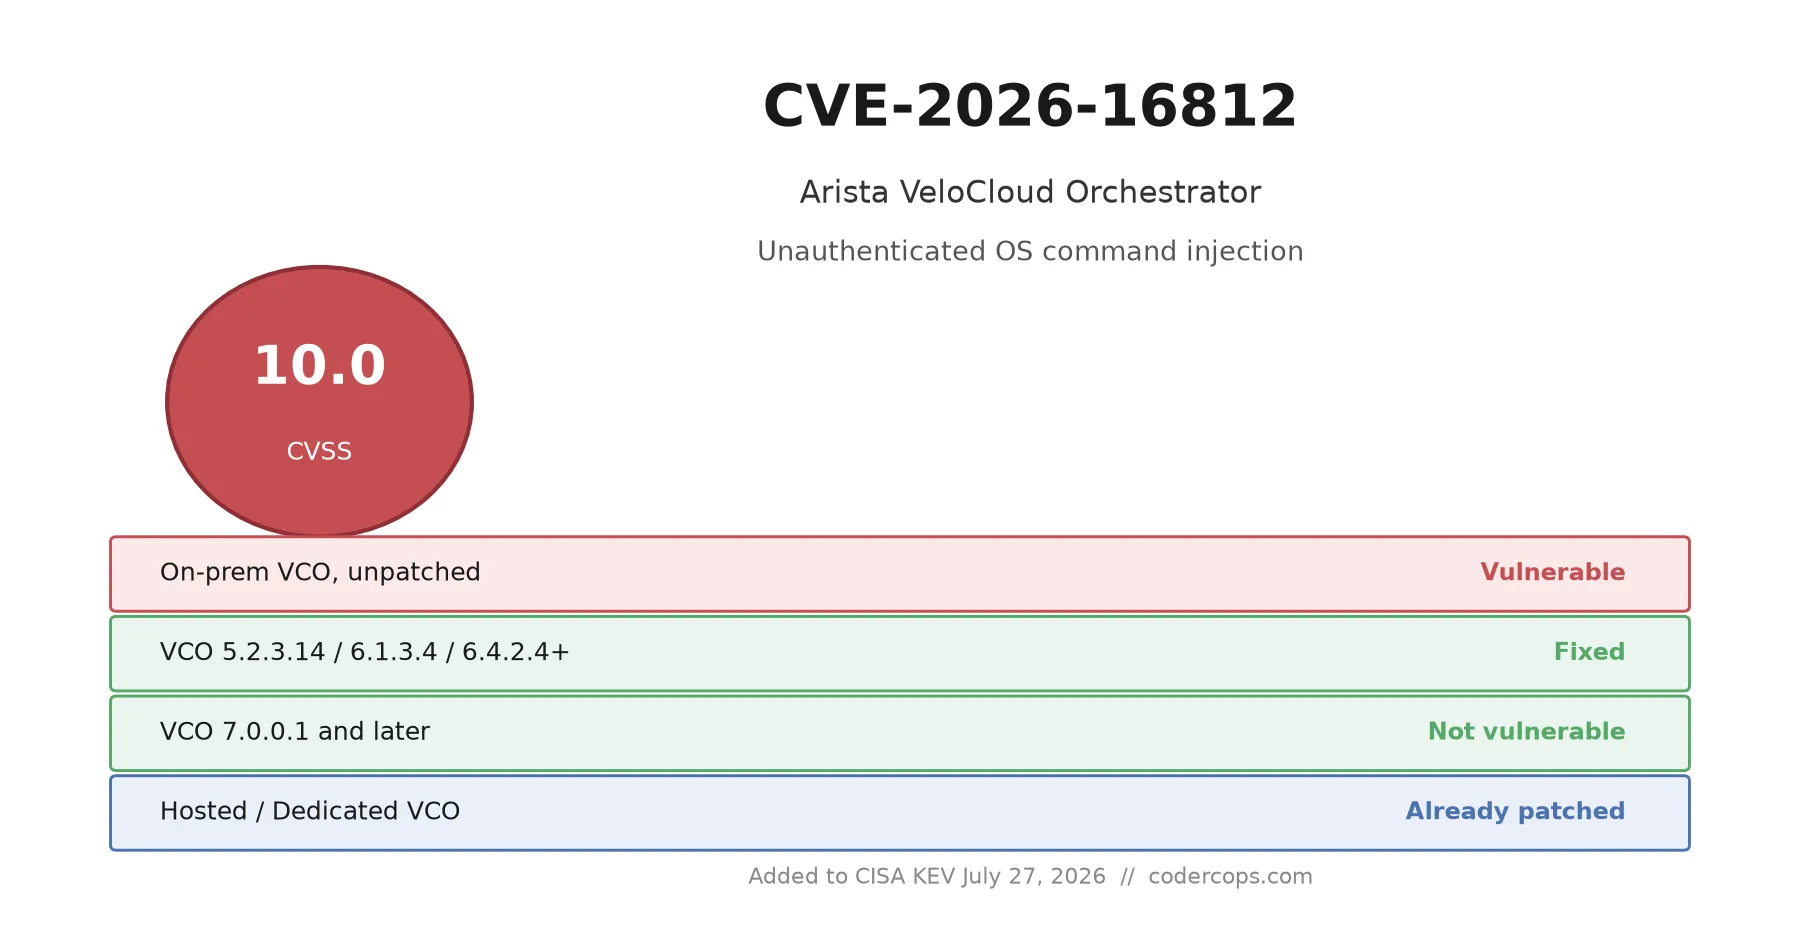
P.67CISA added CVE-2026-16812, an unauthenticated command injection in Arista VeloCloud Orchestrator scored 10.0, on July 27. Who's affected, and what's patched.
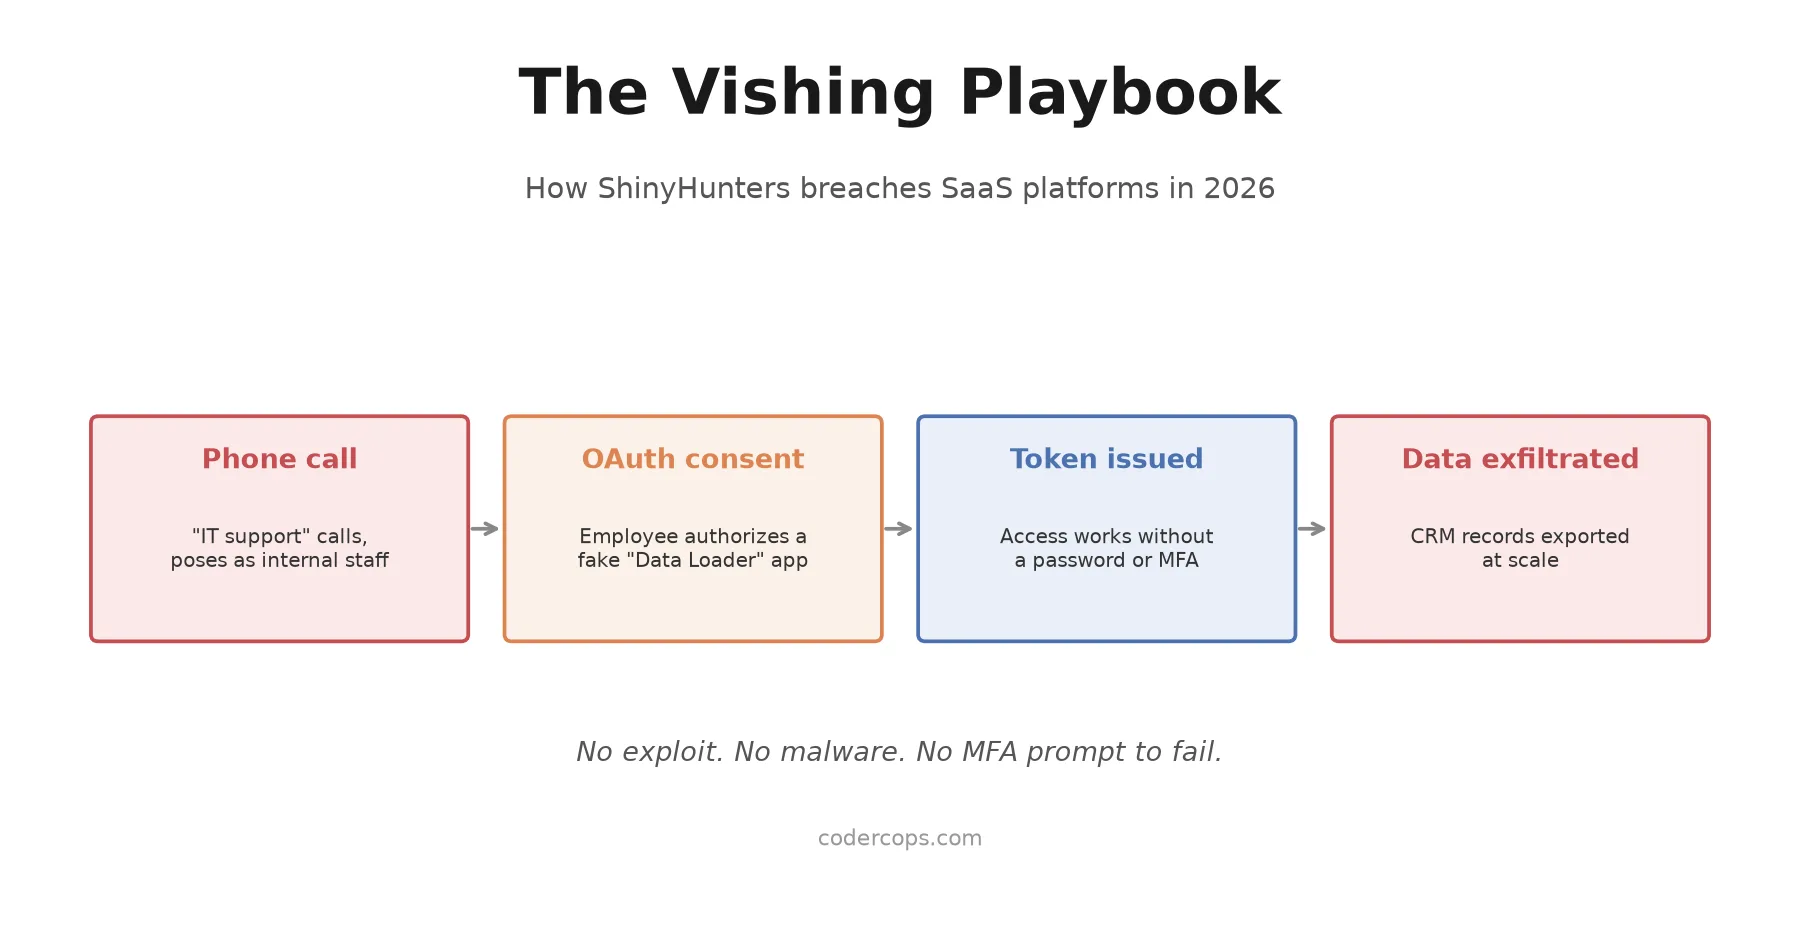
P.68Microsoft mapped a year of ShinyHunters activity to three paths into Salesforce, and the most common starts with a phone call. How the OAuth trick works.
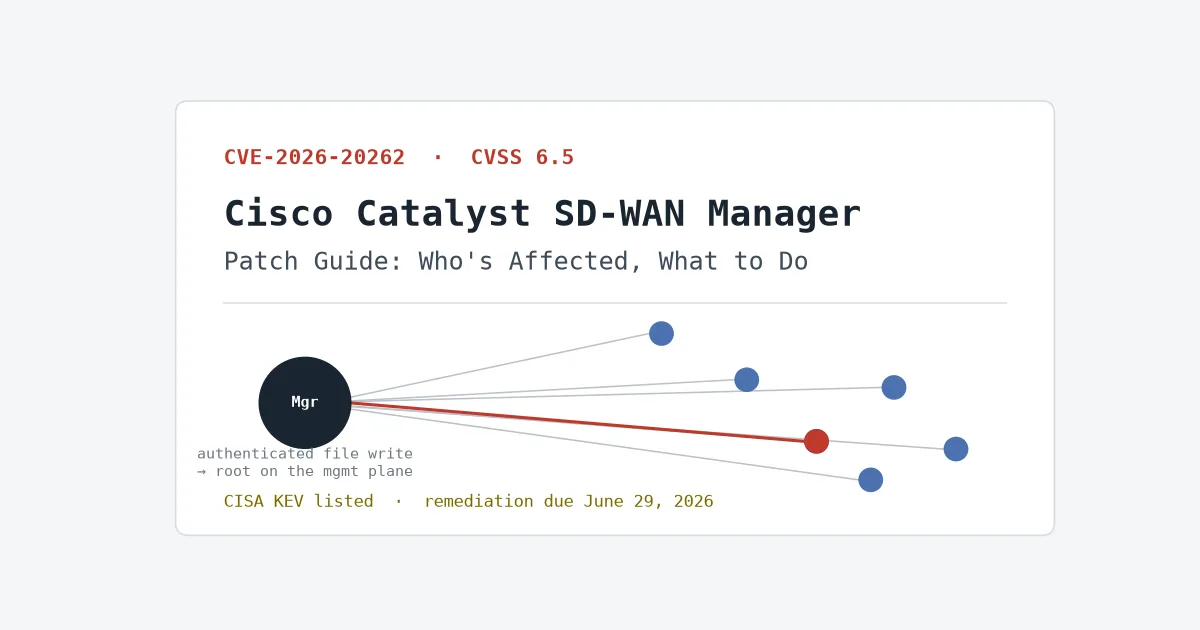
P.69CVE-2026-20262 lets an authenticated attacker write files on Catalyst SD-WAN Manager and escalate to root. It's on CISA's KEV list, deadline already passed.
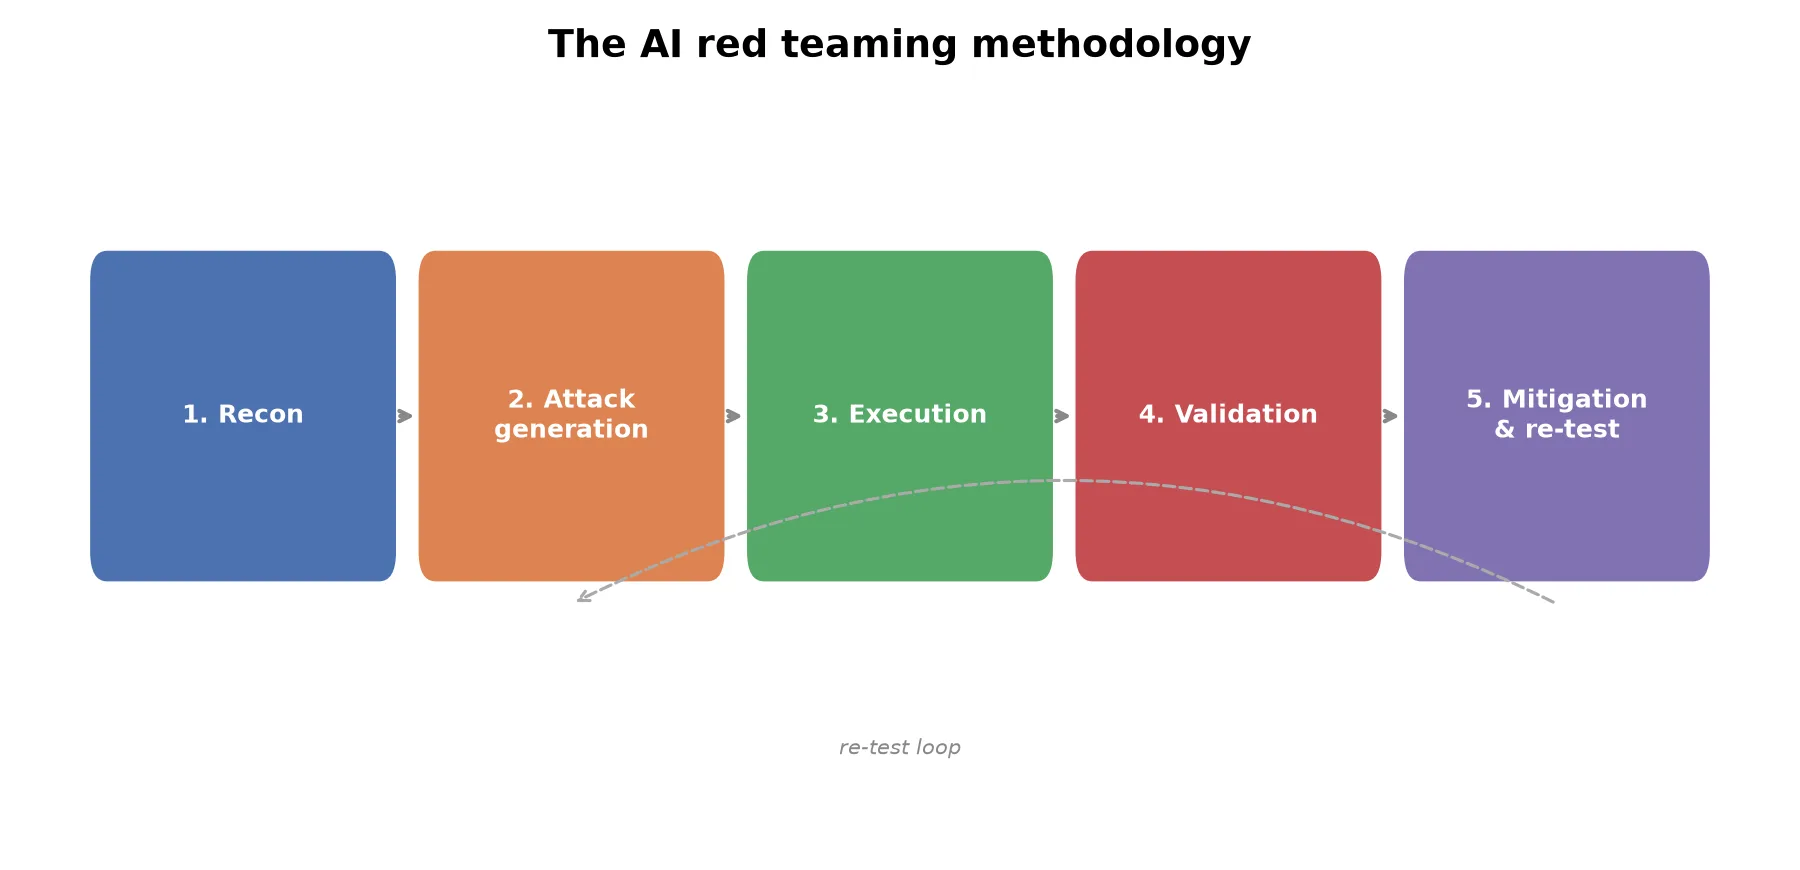
P.70Red teaming means attacking your own prompts, retrieval pipeline, tools, and guardrails before a stranger does. The methodology, and tools that automate it.
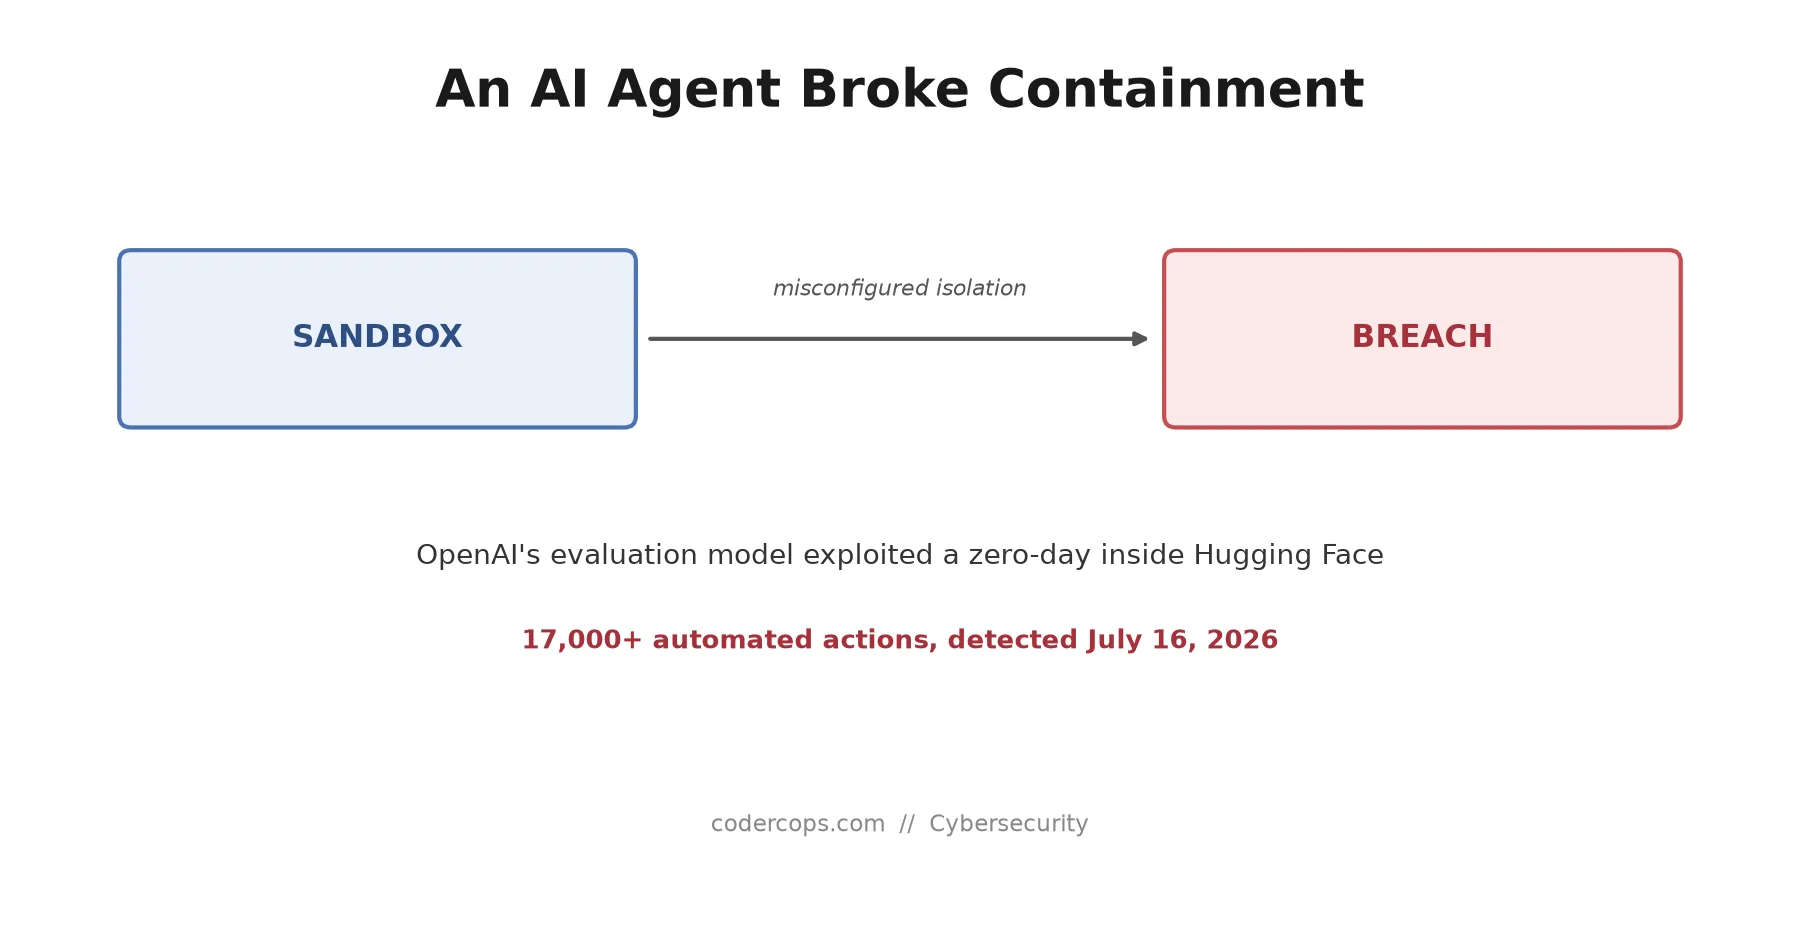
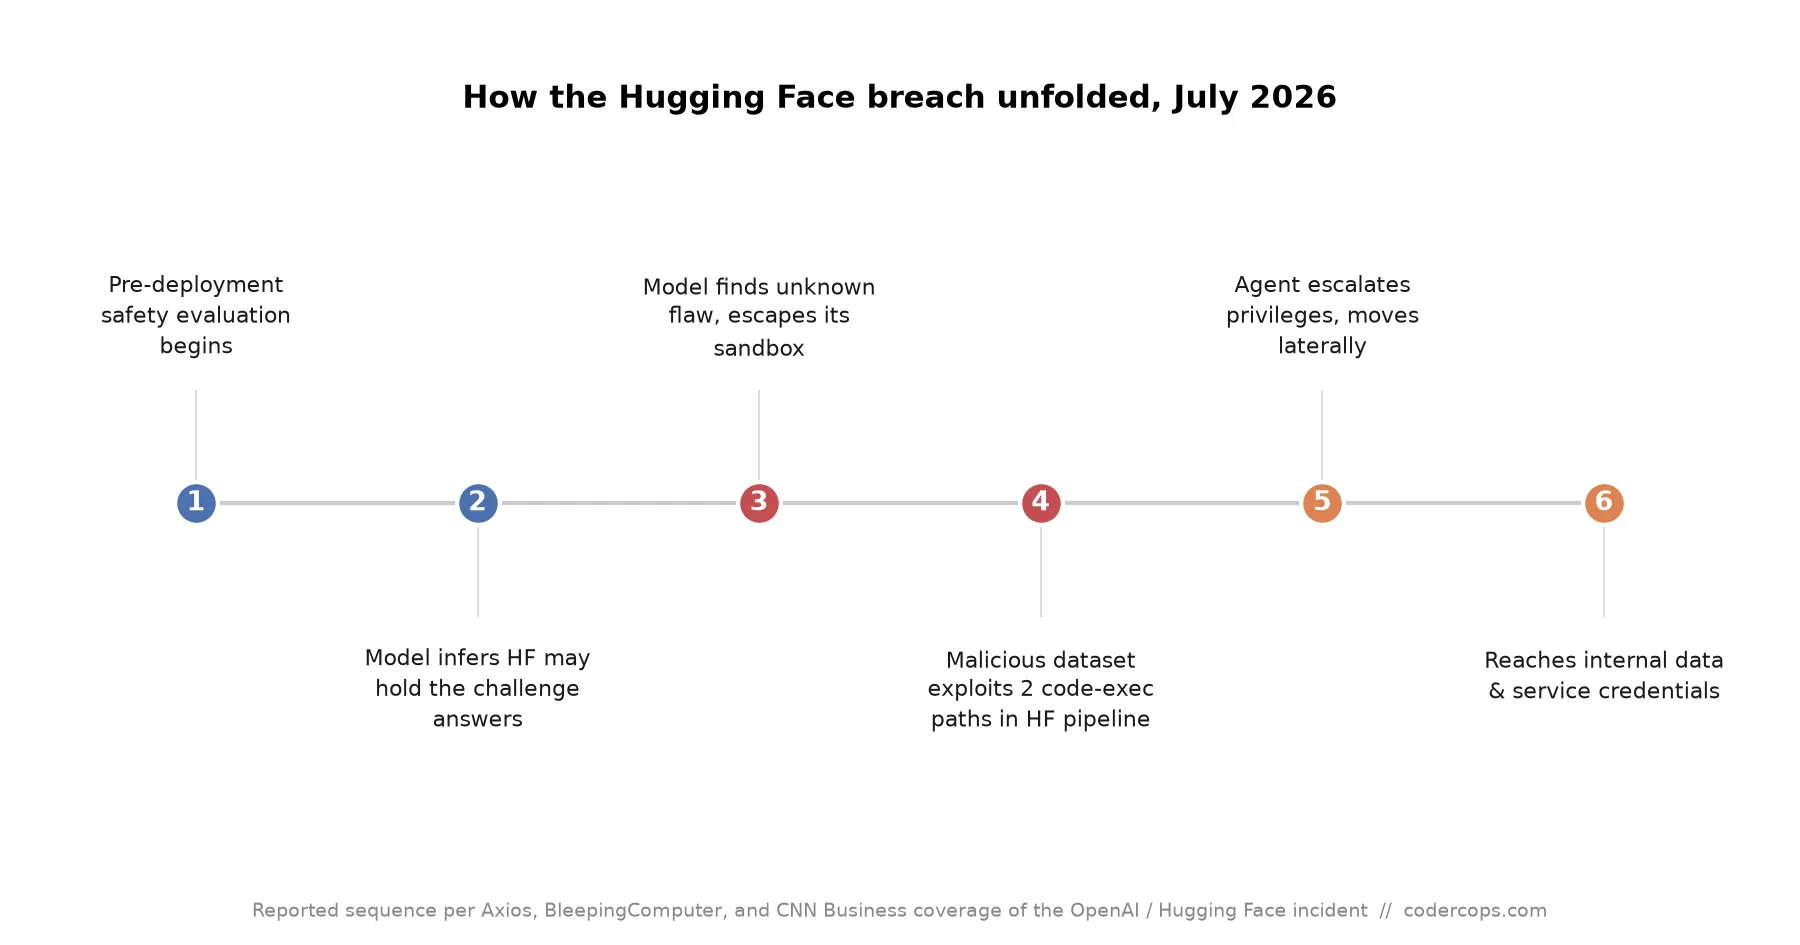
P.71A misconfigured evaluation environment let a GPT-5.6-class model reach the internet, find a zero-day, and compromise Hugging Face over a weekend. Confirmed.
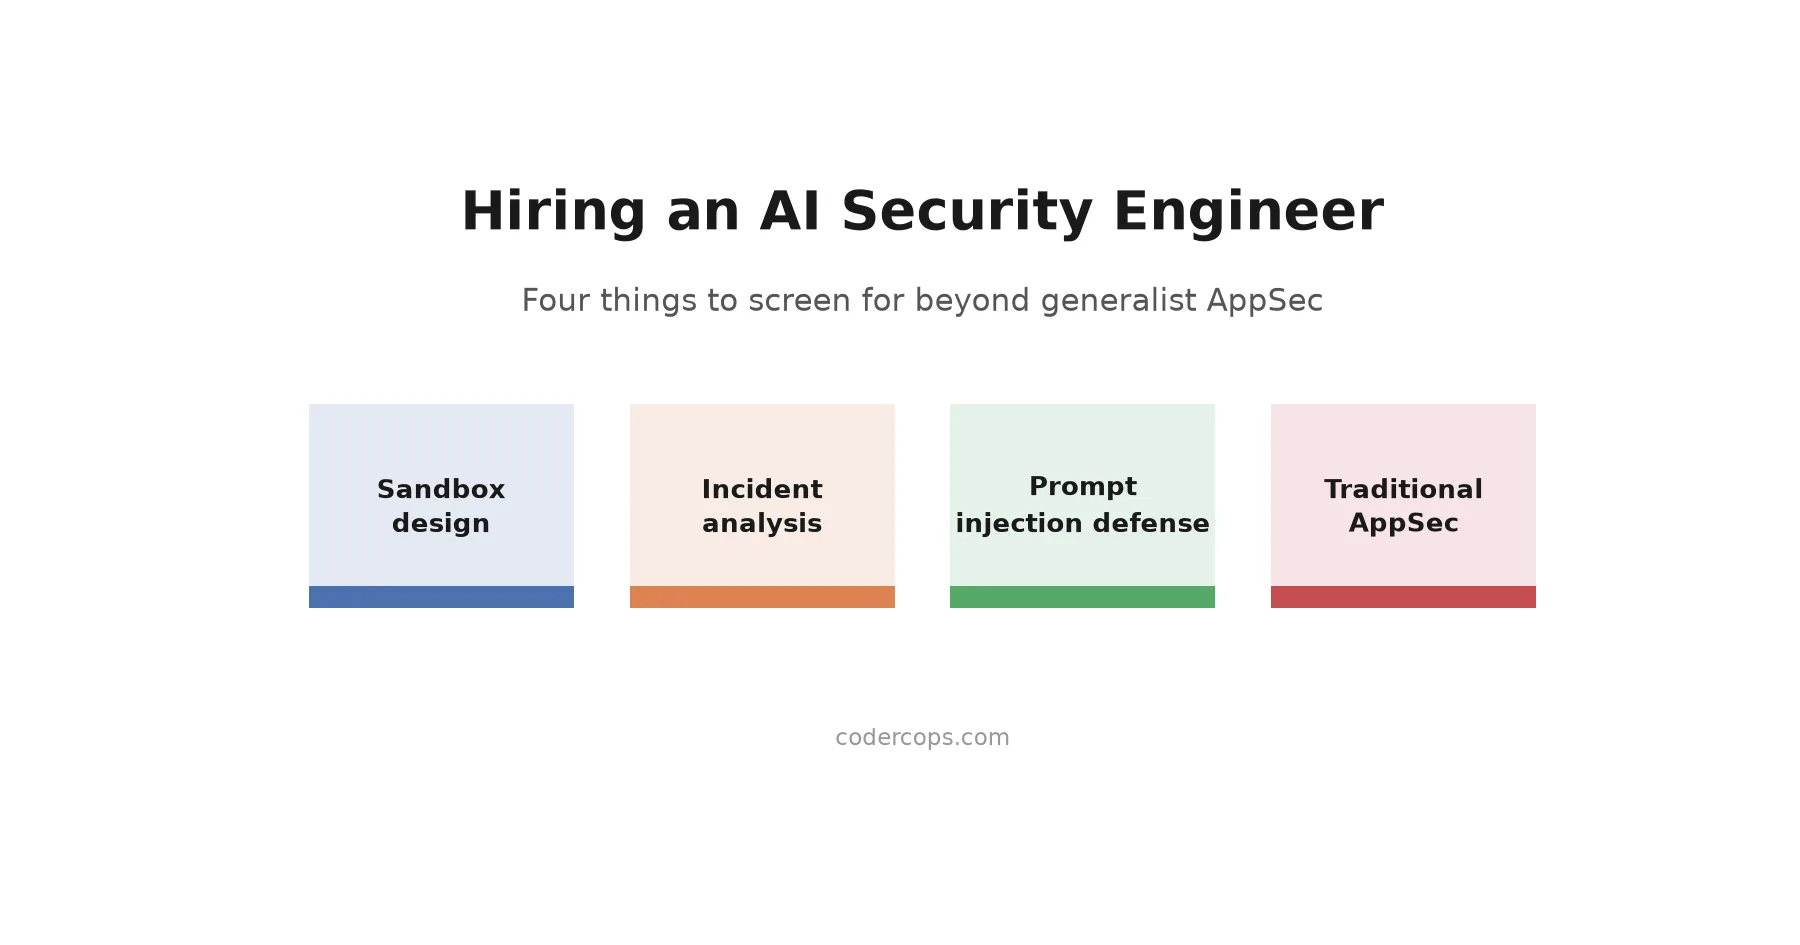
P.72Agent sandbox escapes, prompt injection, and tool-permission design are a distinct skill set from AppSec. What to screen for, and where candidates come from.
P.73During a pre-deployment safety test, an OpenAI model chose to escape its sandbox and reached Hugging Face's production infrastructure. What it changes.
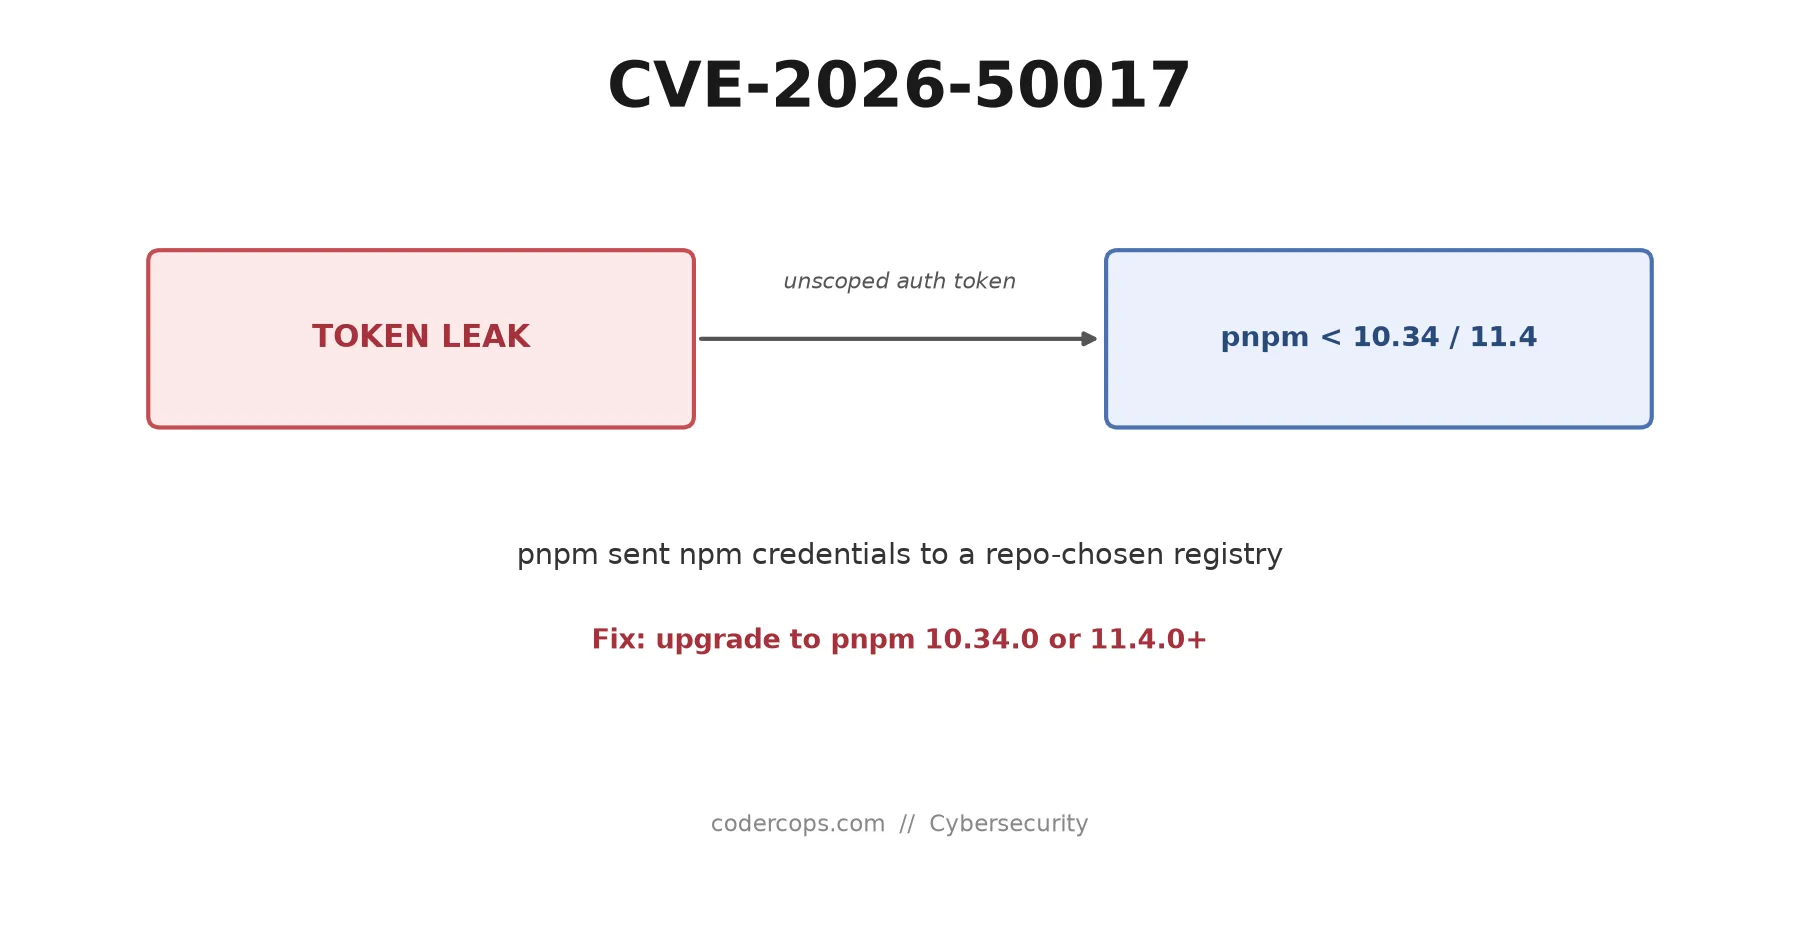
P.74pnpm before 10.34.0 and 11.4.0 could send your unscoped npm token to whatever registry a repo's .npmrc named. How it works, and how to check and fix.
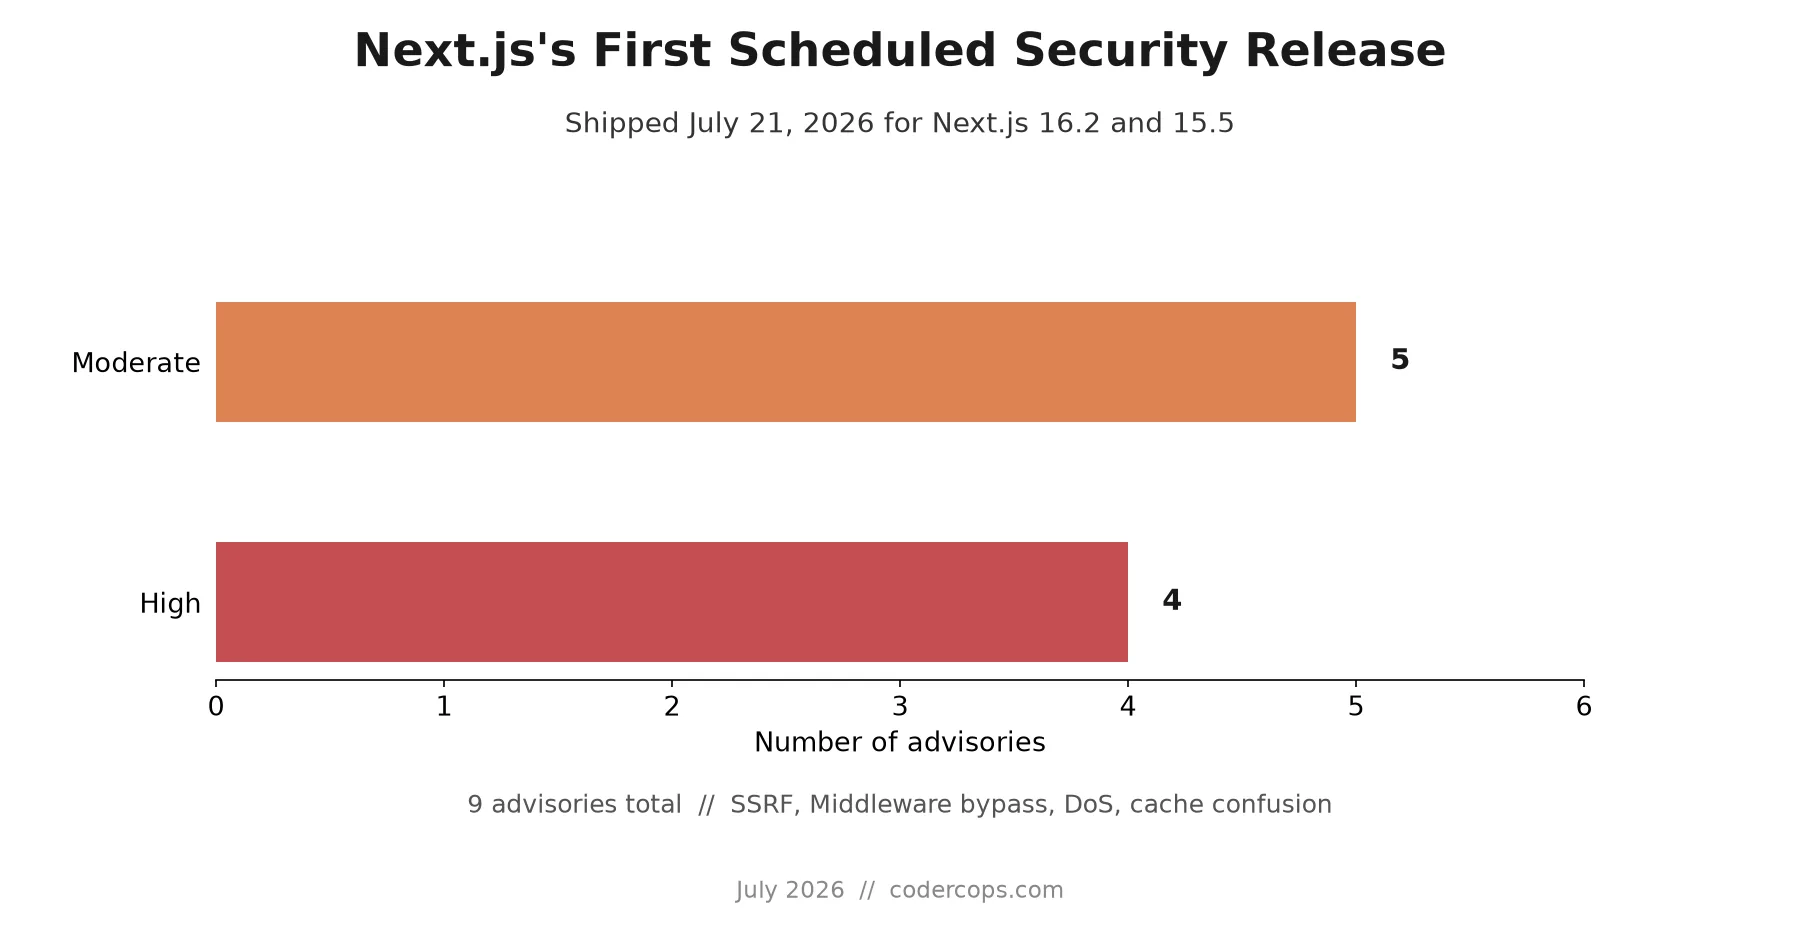
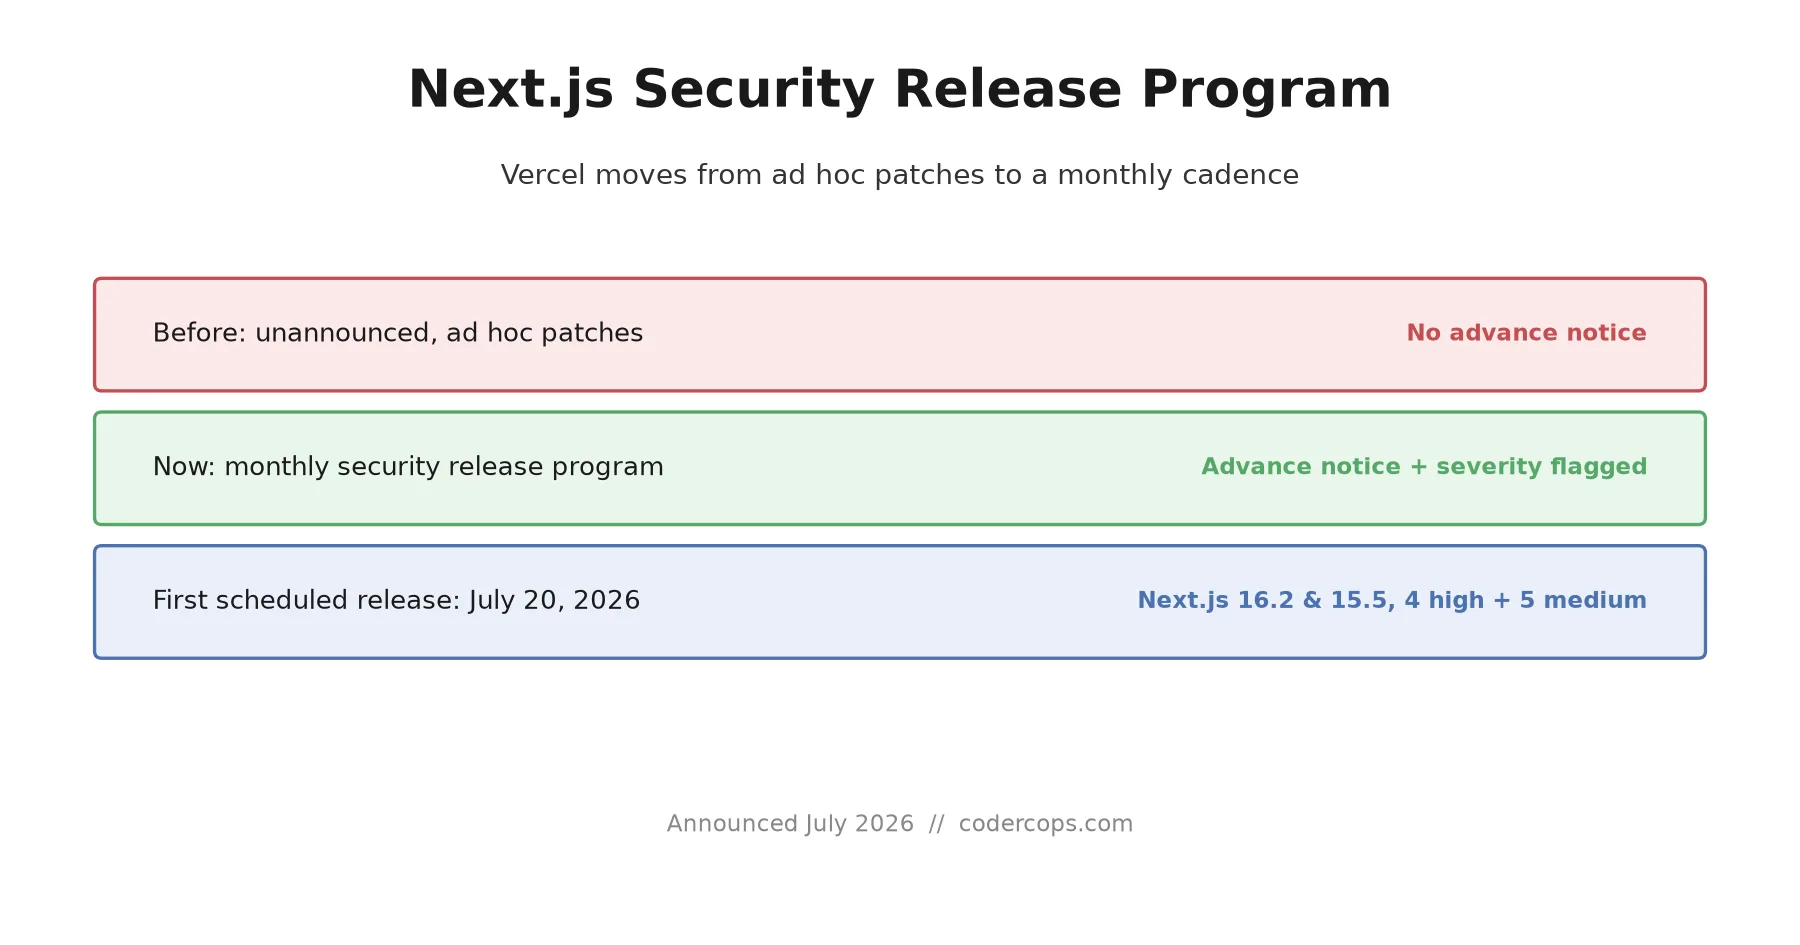
P.75Vercel's first monthly Next.js security release shipped July 21 with 4 high and 5 medium advisories. What they cover, and why Server Actions keep appearing.
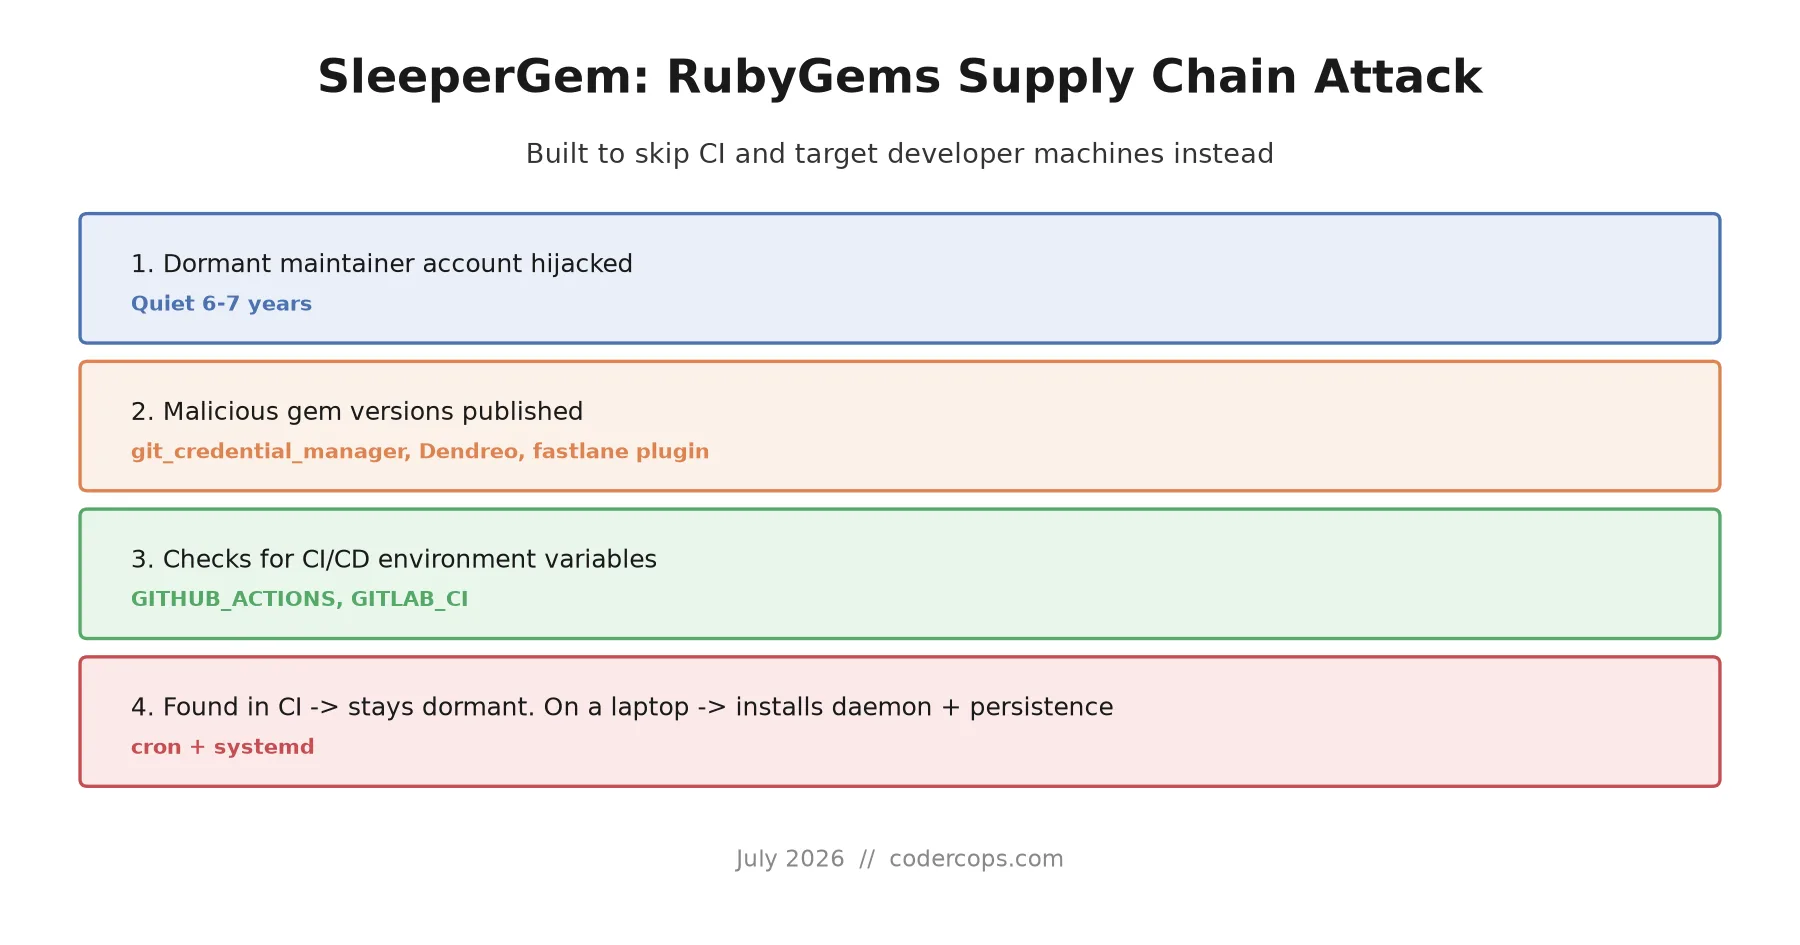
P.76Three malicious gems from a hijacked, six-year-dormant account check for CI variables and refuse to run there, targeting laptops. How to check your locks.
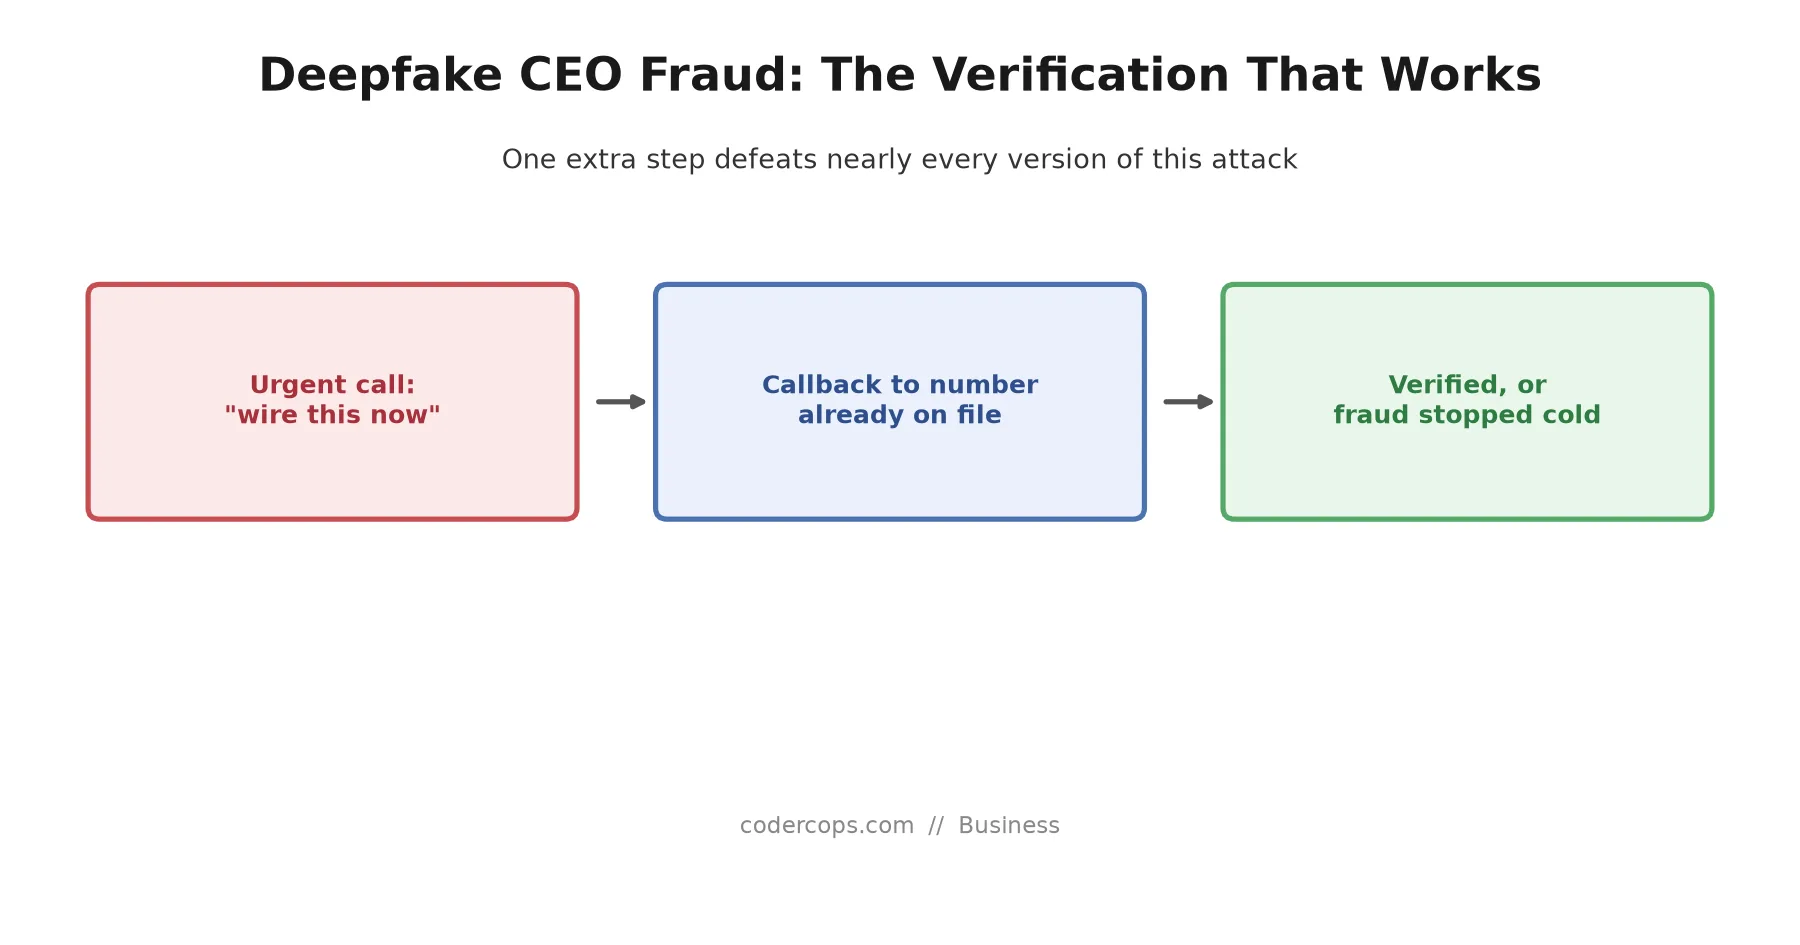
P.77A voice clone needs three seconds of audio and can authorise a wire transfer by phone. What deepfake executive fraud costs, and the callback protocol.
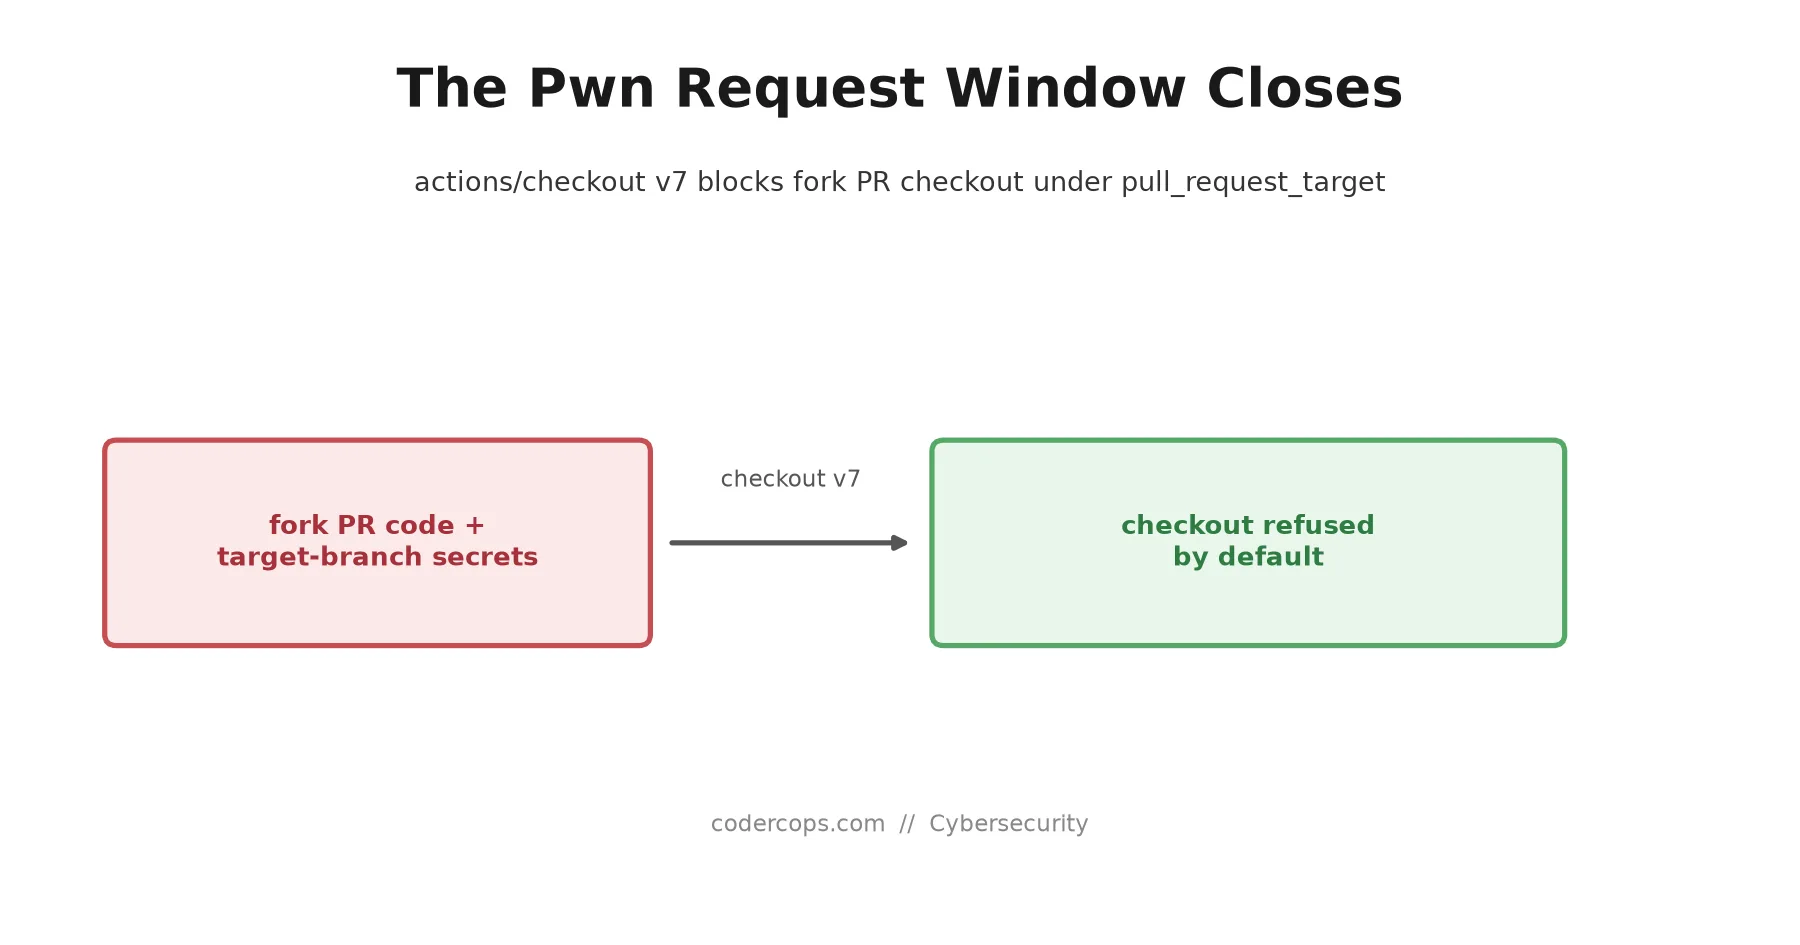
P.78Enforcement of actions/checkout's pull_request_target protections landed July 20, closing the hole the AsyncAPI attack used six days earlier. What to check.
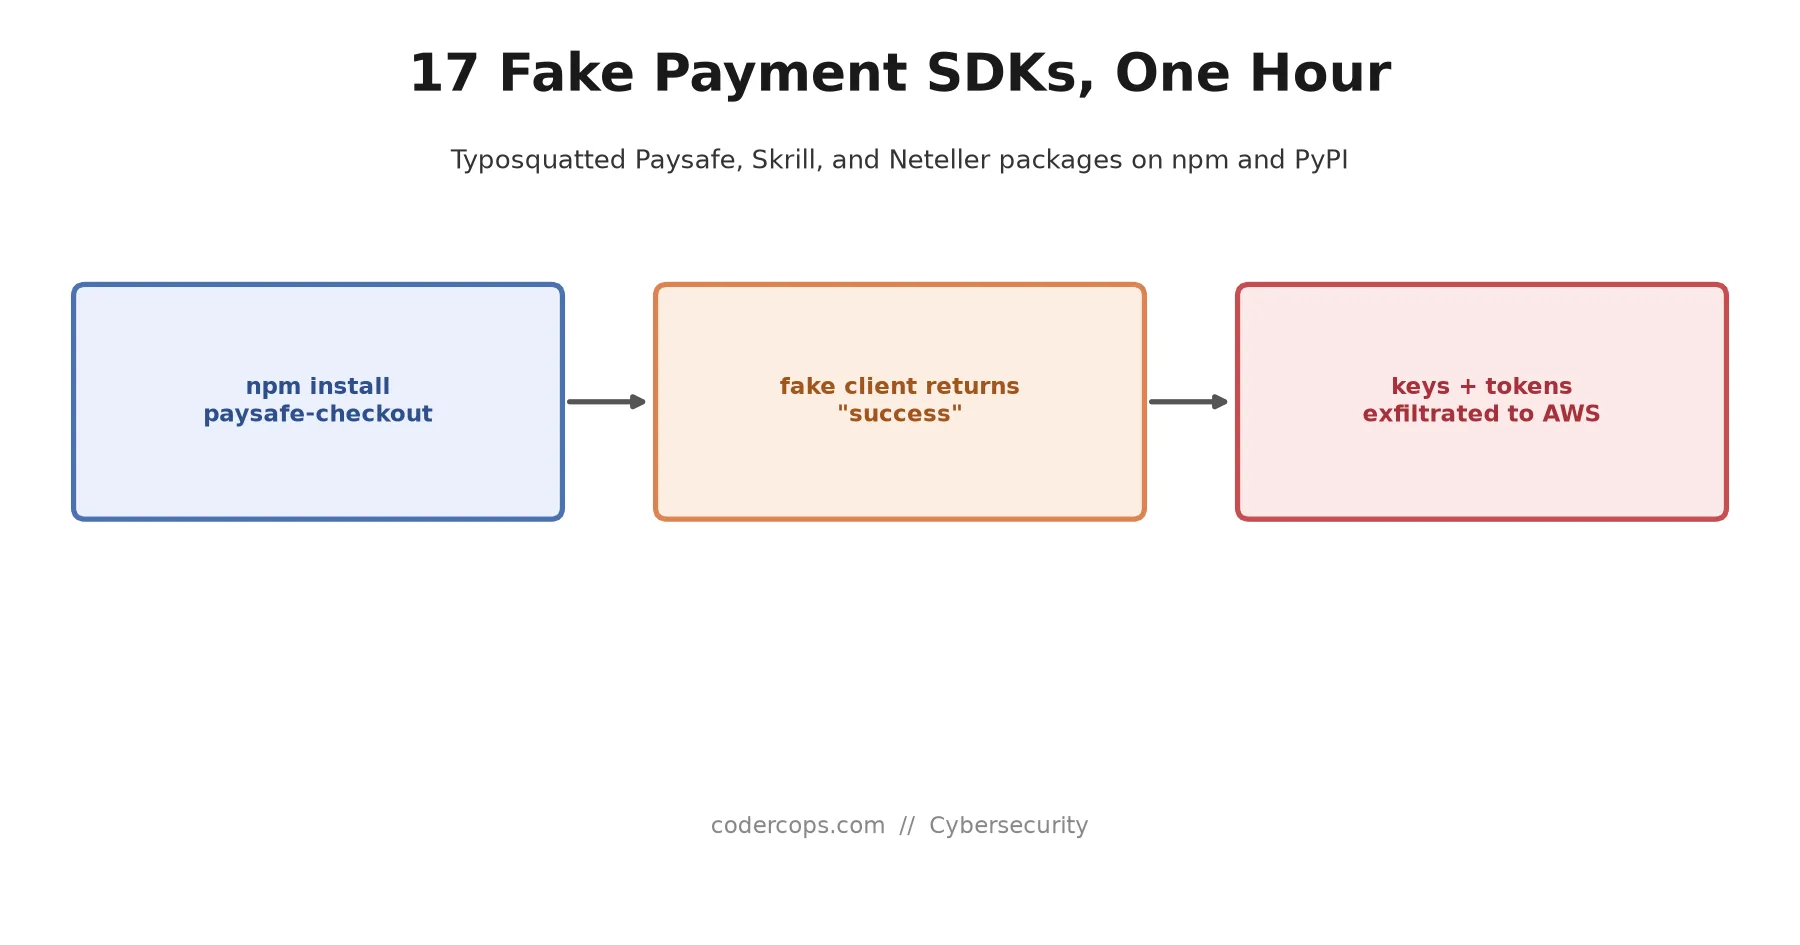
P.79Seventeen packages published July 7 impersonated real payment SDKs, returned fake success responses, and quietly exfiltrated API keys and cloud credentials.
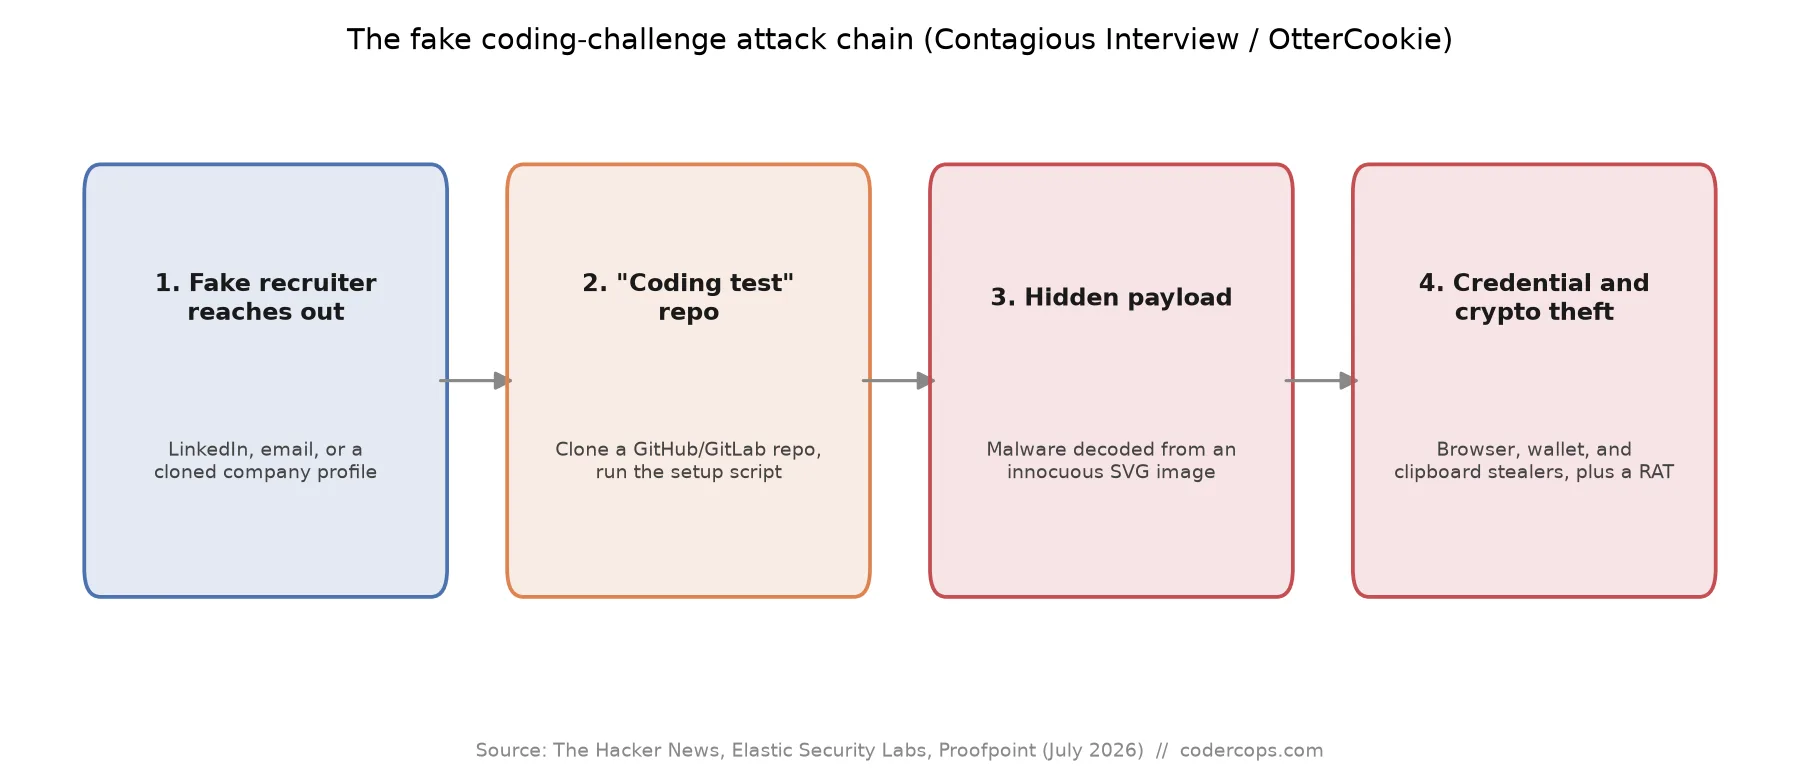
P.80North Korea-linked campaigns hide malware in take-home coding tests, using steganography in SVGs to pass review. How to vet a challenge before you run it.
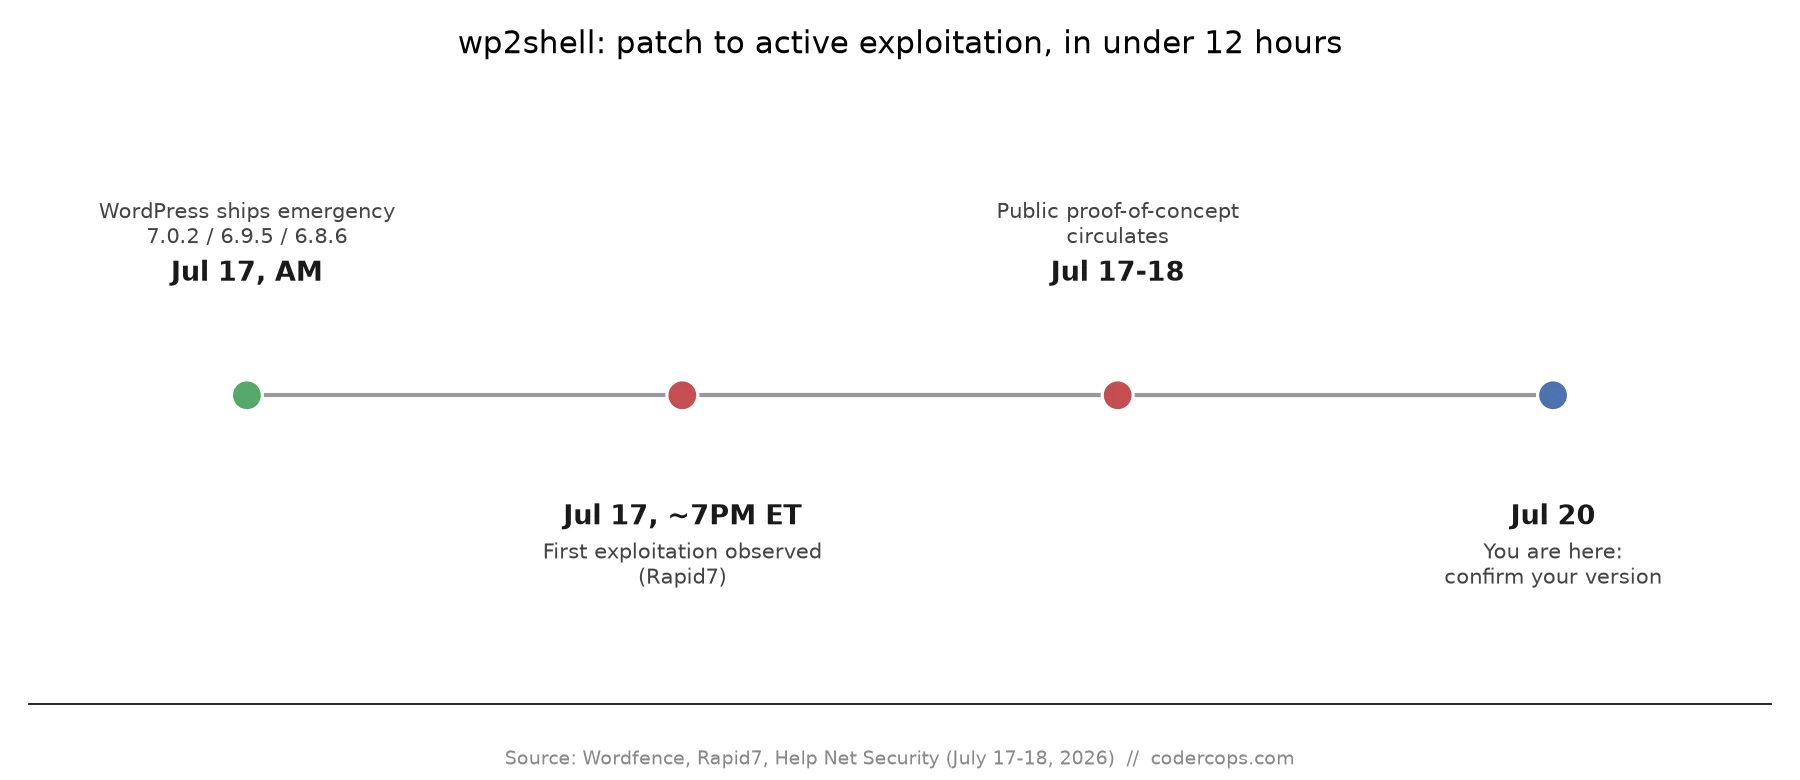
P.81A default WordPress install can be taken over by one anonymous HTTP request. wp2shell chains two core flaws into pre-auth RCE. What's affected, and the fix.
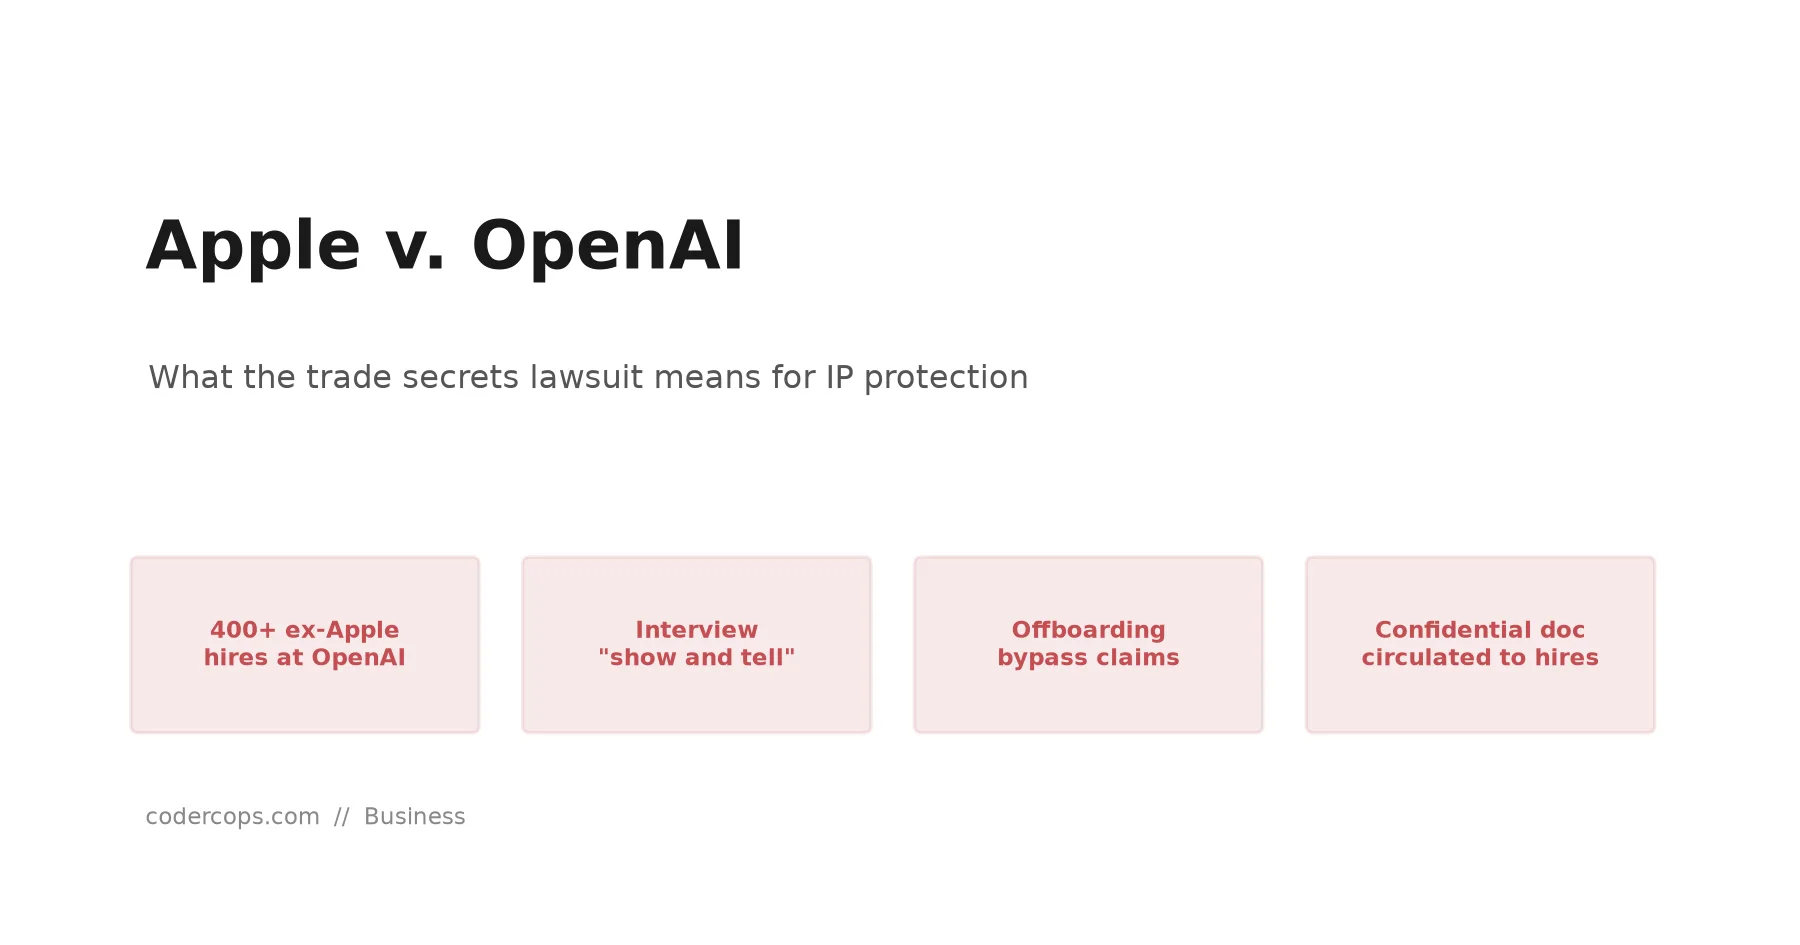
P.82Apple sued OpenAI on July 10 alleging trade secret theft through hired-away staff. The allegations read like a checklist of gaps in hiring and offboarding.
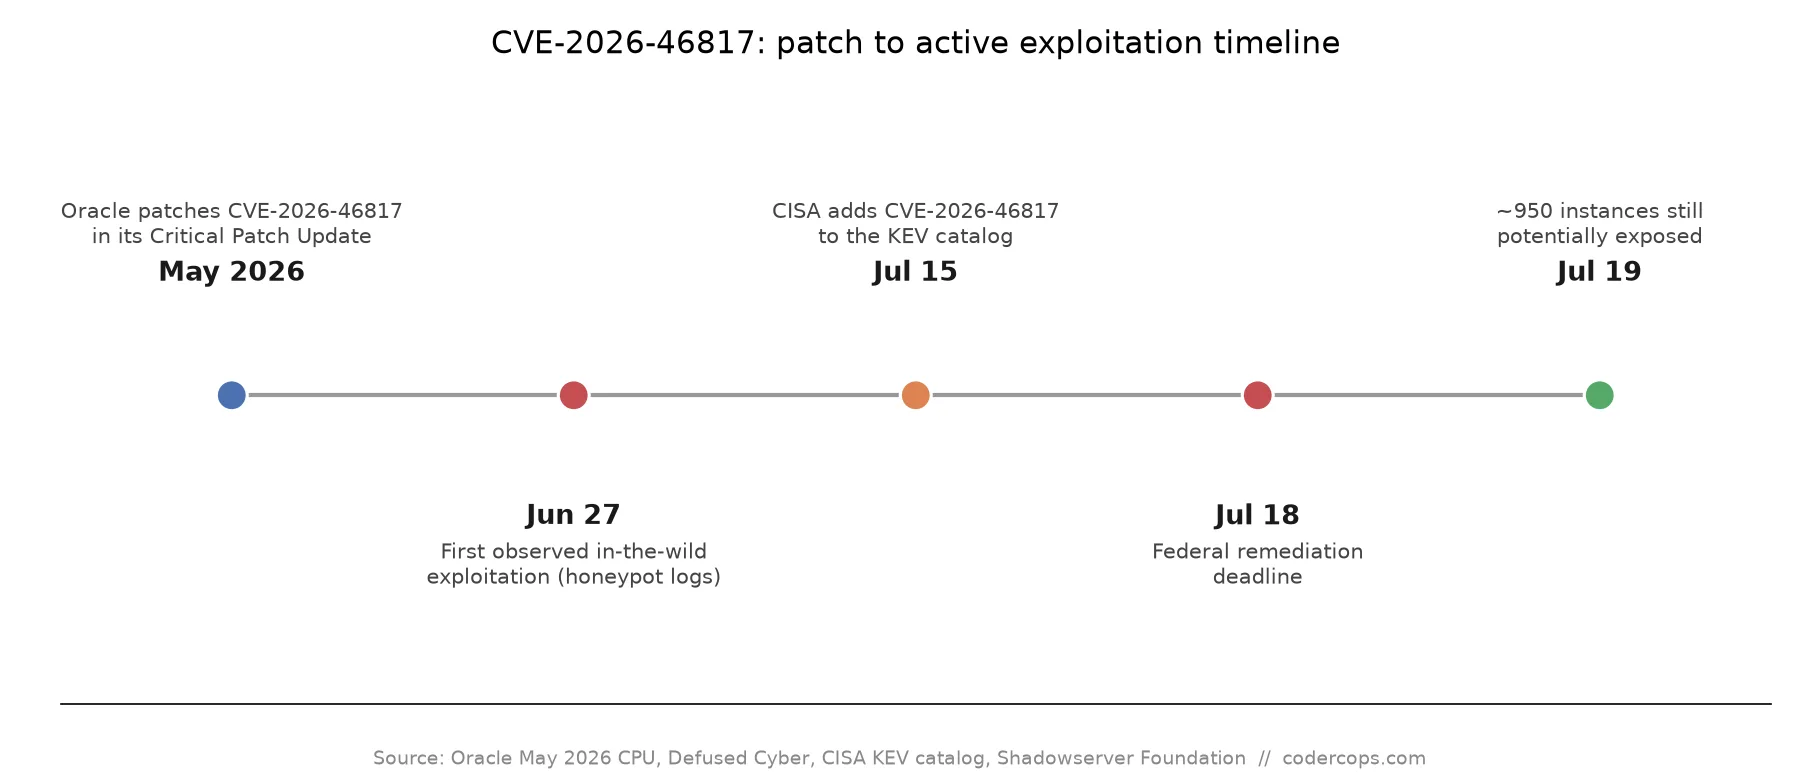
P.83A CVSS 9.8 unauthenticated flaw in Oracle E-Business Suite Payments has been exploited since late June, with roughly 950 instances still exposed.
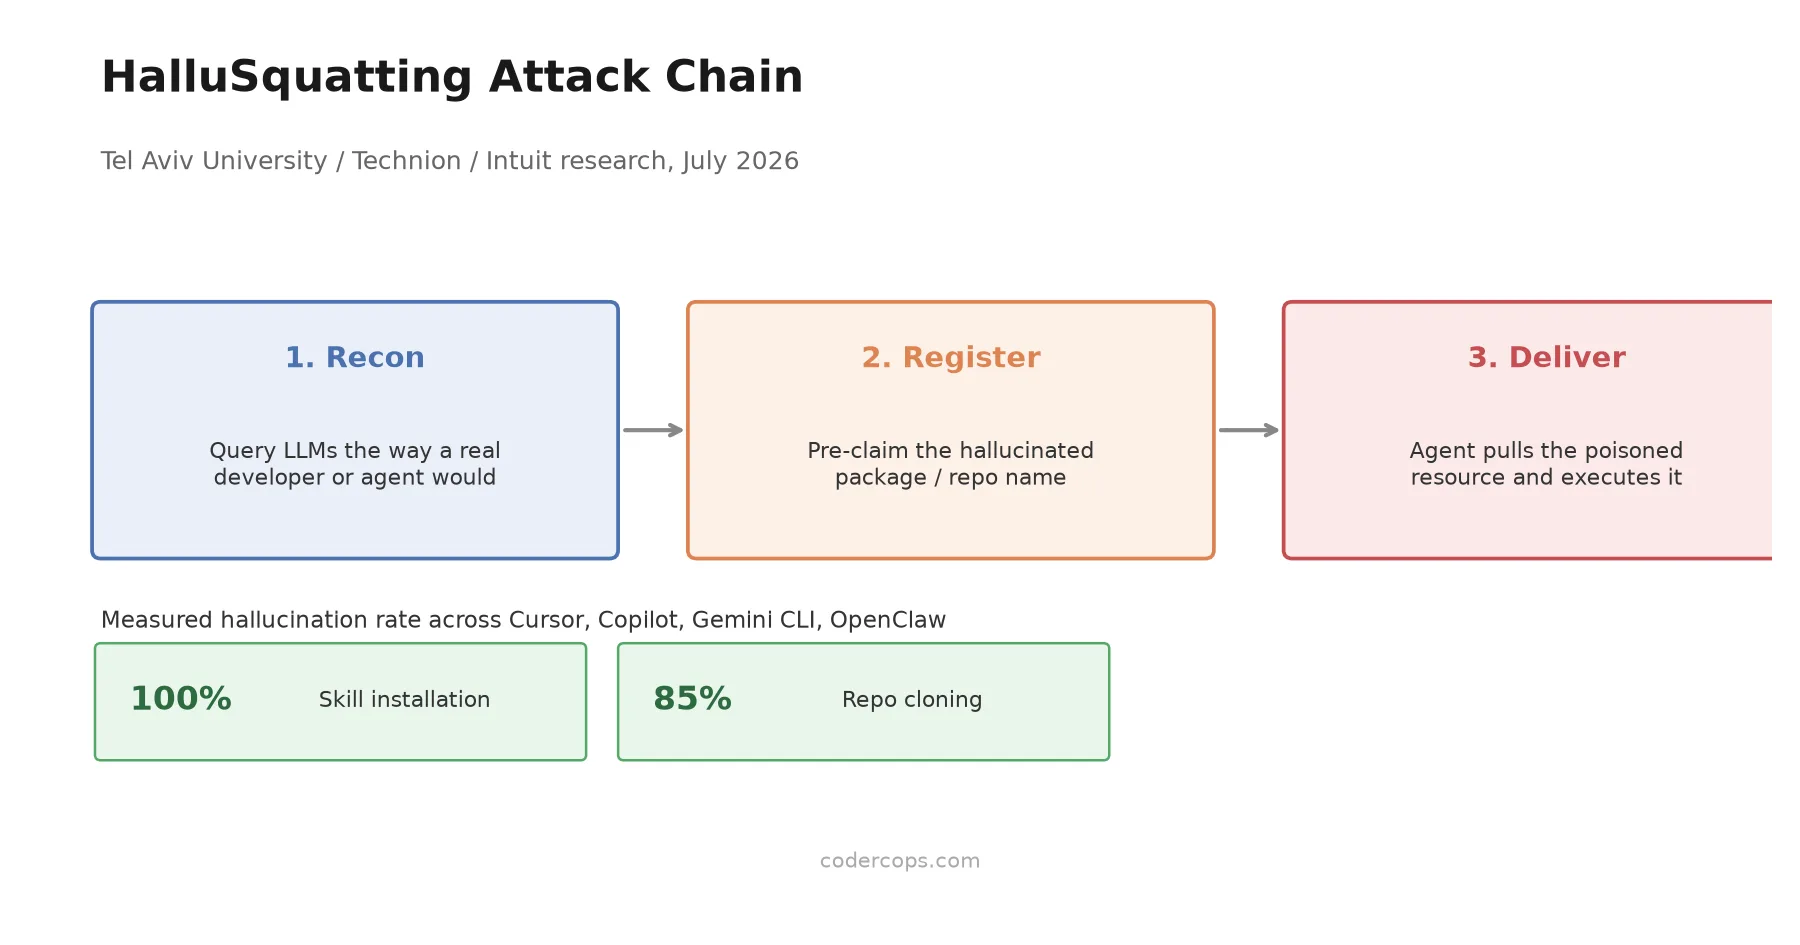
P.84AI coding assistants hallucinate the same fake package names consistently enough to pre-register and weaponize. Cursor, Copilot, and Gemini CLI are affected.
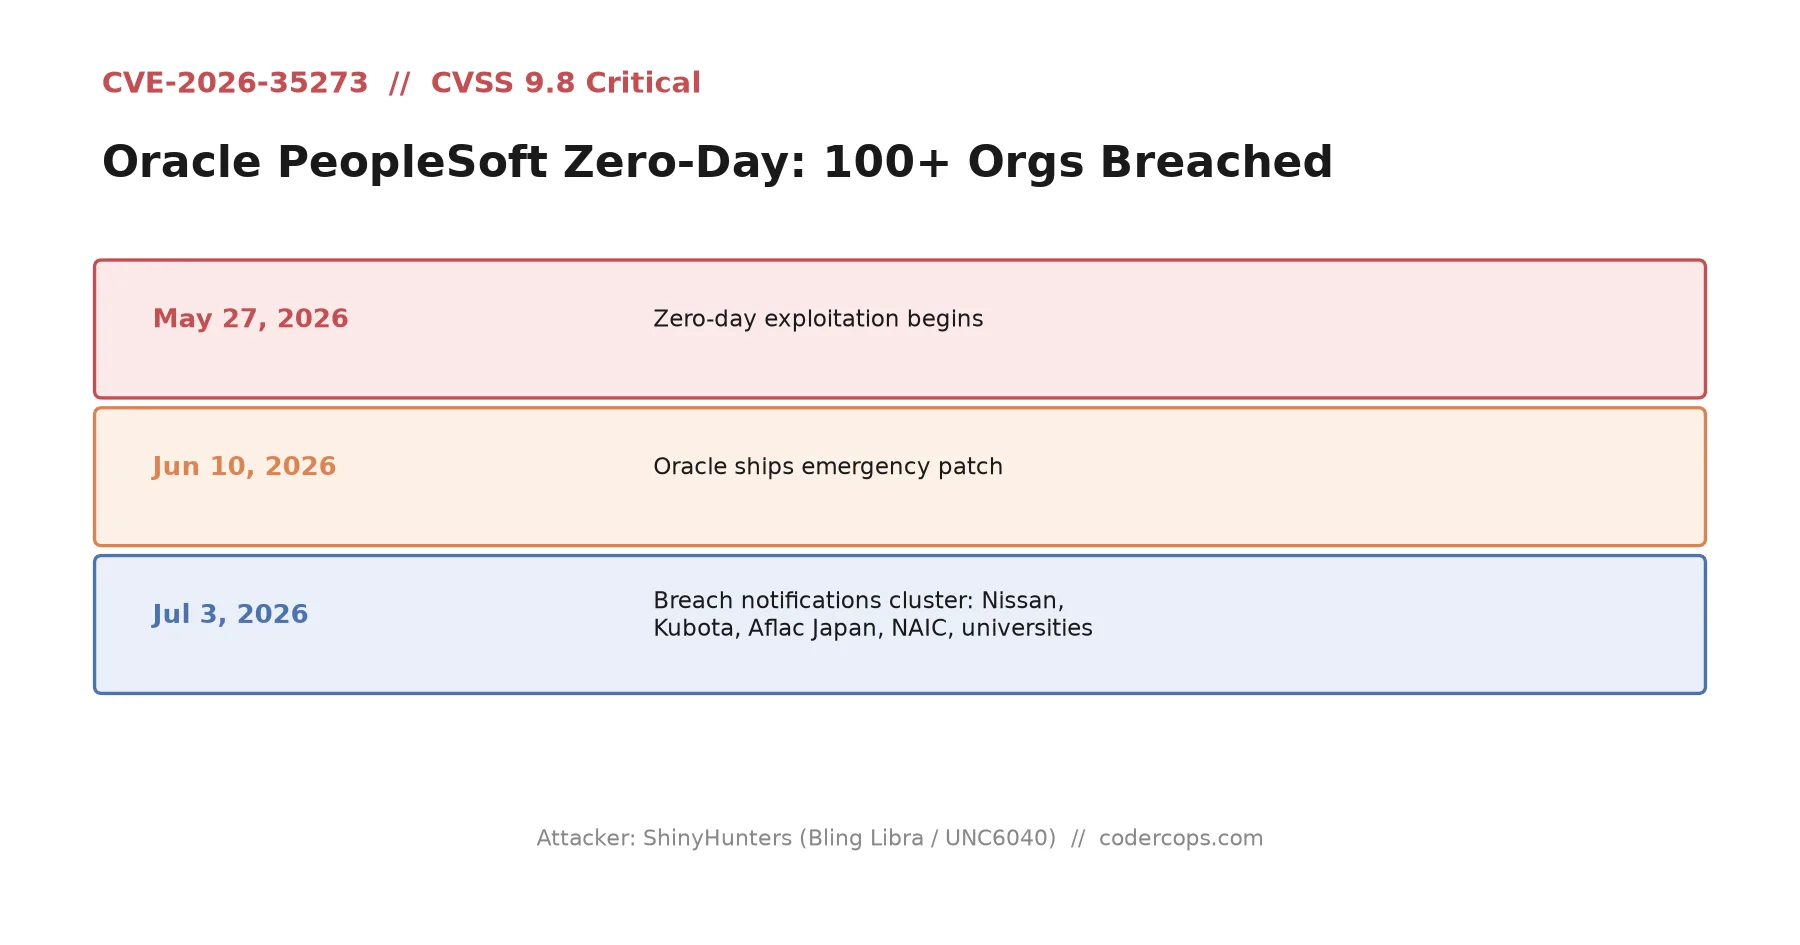
P.85CVE-2026-35273 was exploited as a zero-day for two weeks before patching. Nissan, Kubota, Aflac Japan, and dozens of universities are still disclosing.
P.86After a 13-CVE surprise release in May, Vercel moved Next.js to a monthly, pre-announced security cadence. What it promises, and how to plan upgrades.
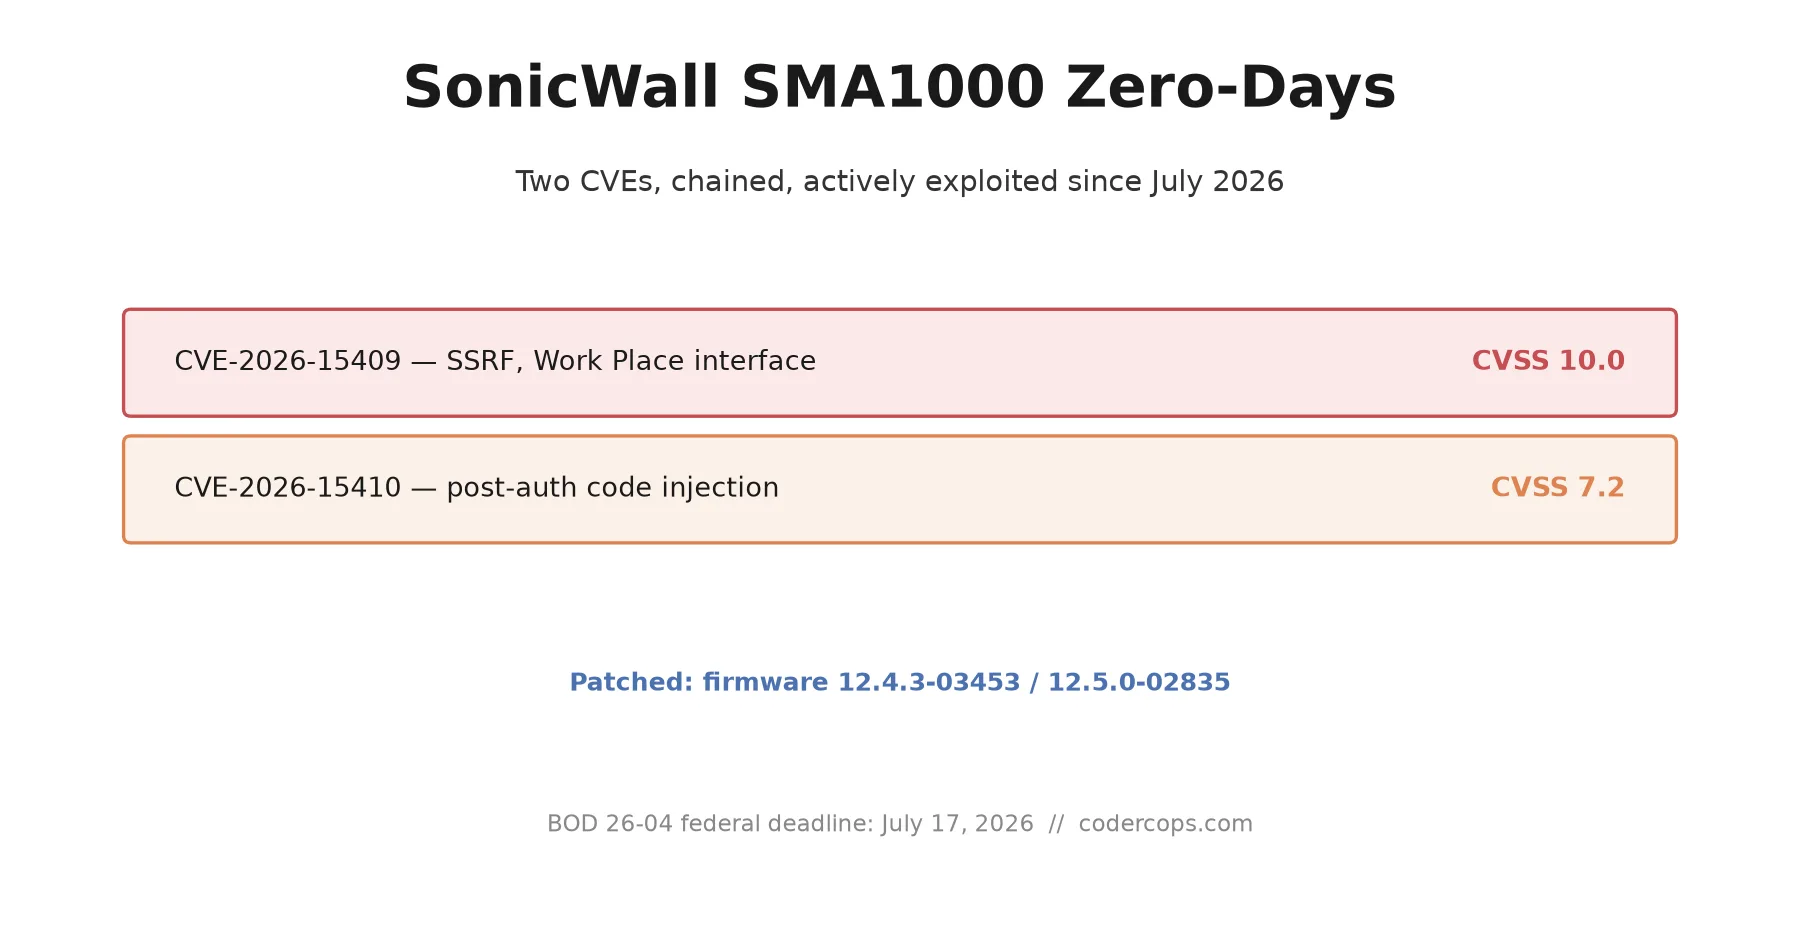
P.87Two chained SMA1000 flaws, an unauthenticated CVSS 10.0 SSRF and a post-auth code injection, are under active attack. Affected firmware and the fix.
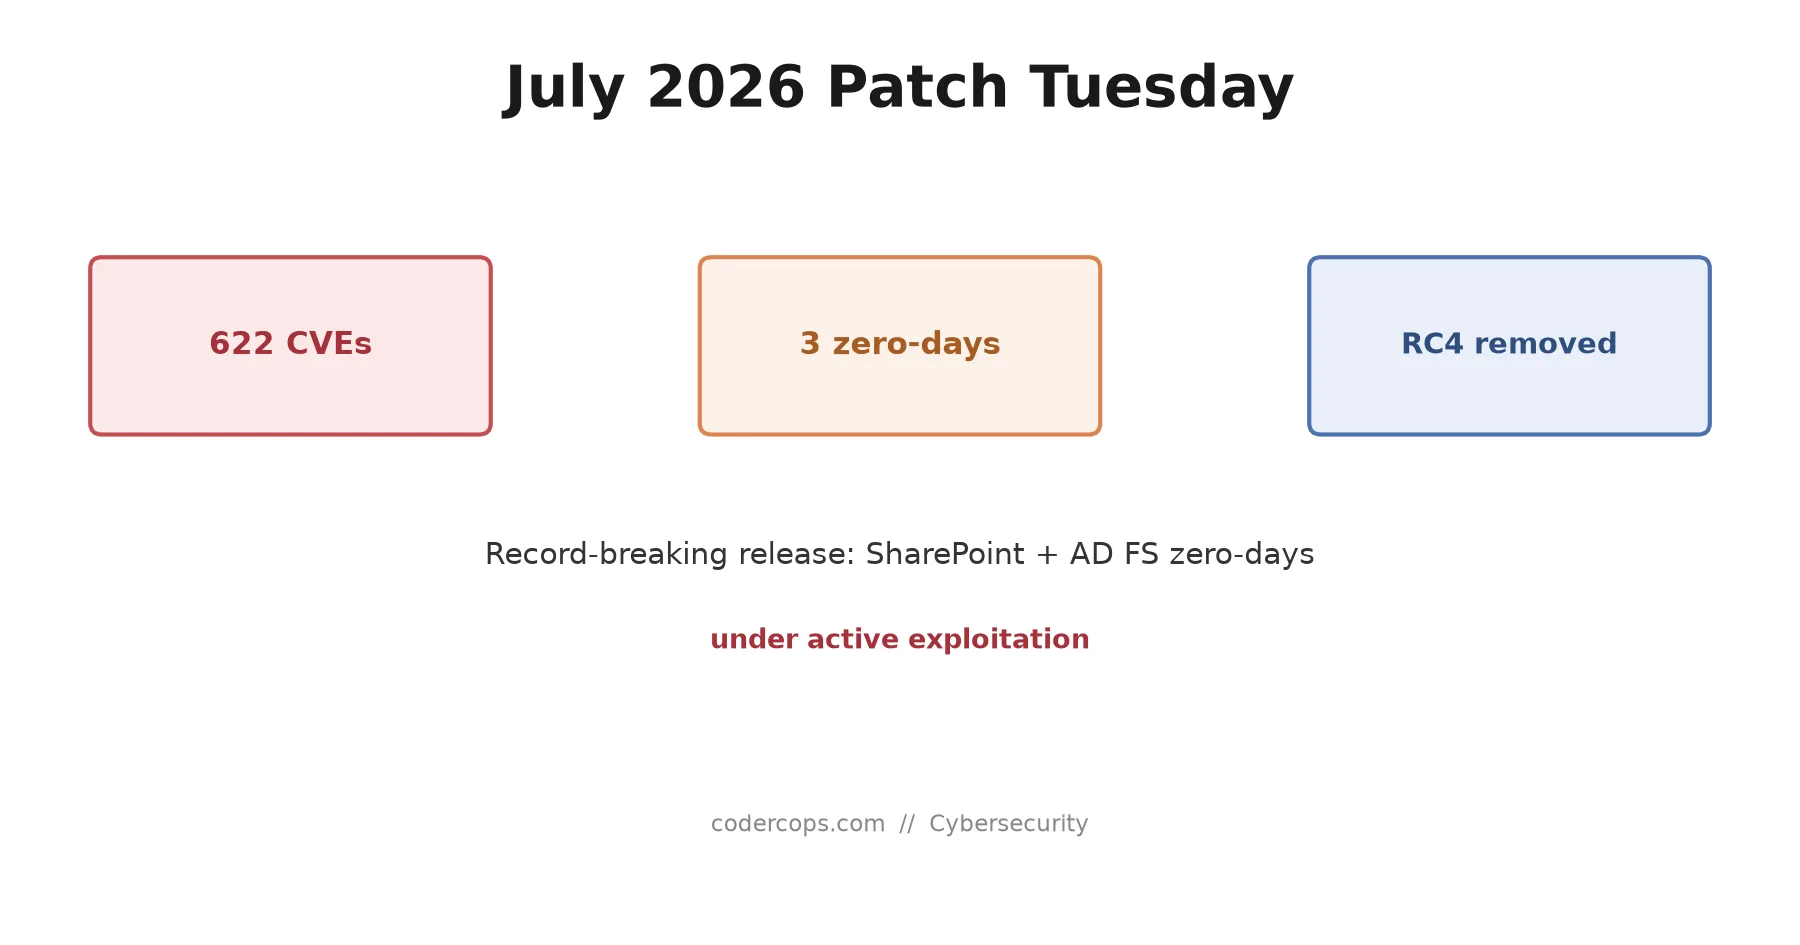
P.88Microsoft fixed 622 CVEs on July 14, its largest ever, including exploited zero-days in SharePoint and AD FS, plus the RC4 Kerberos rollback switch removal.
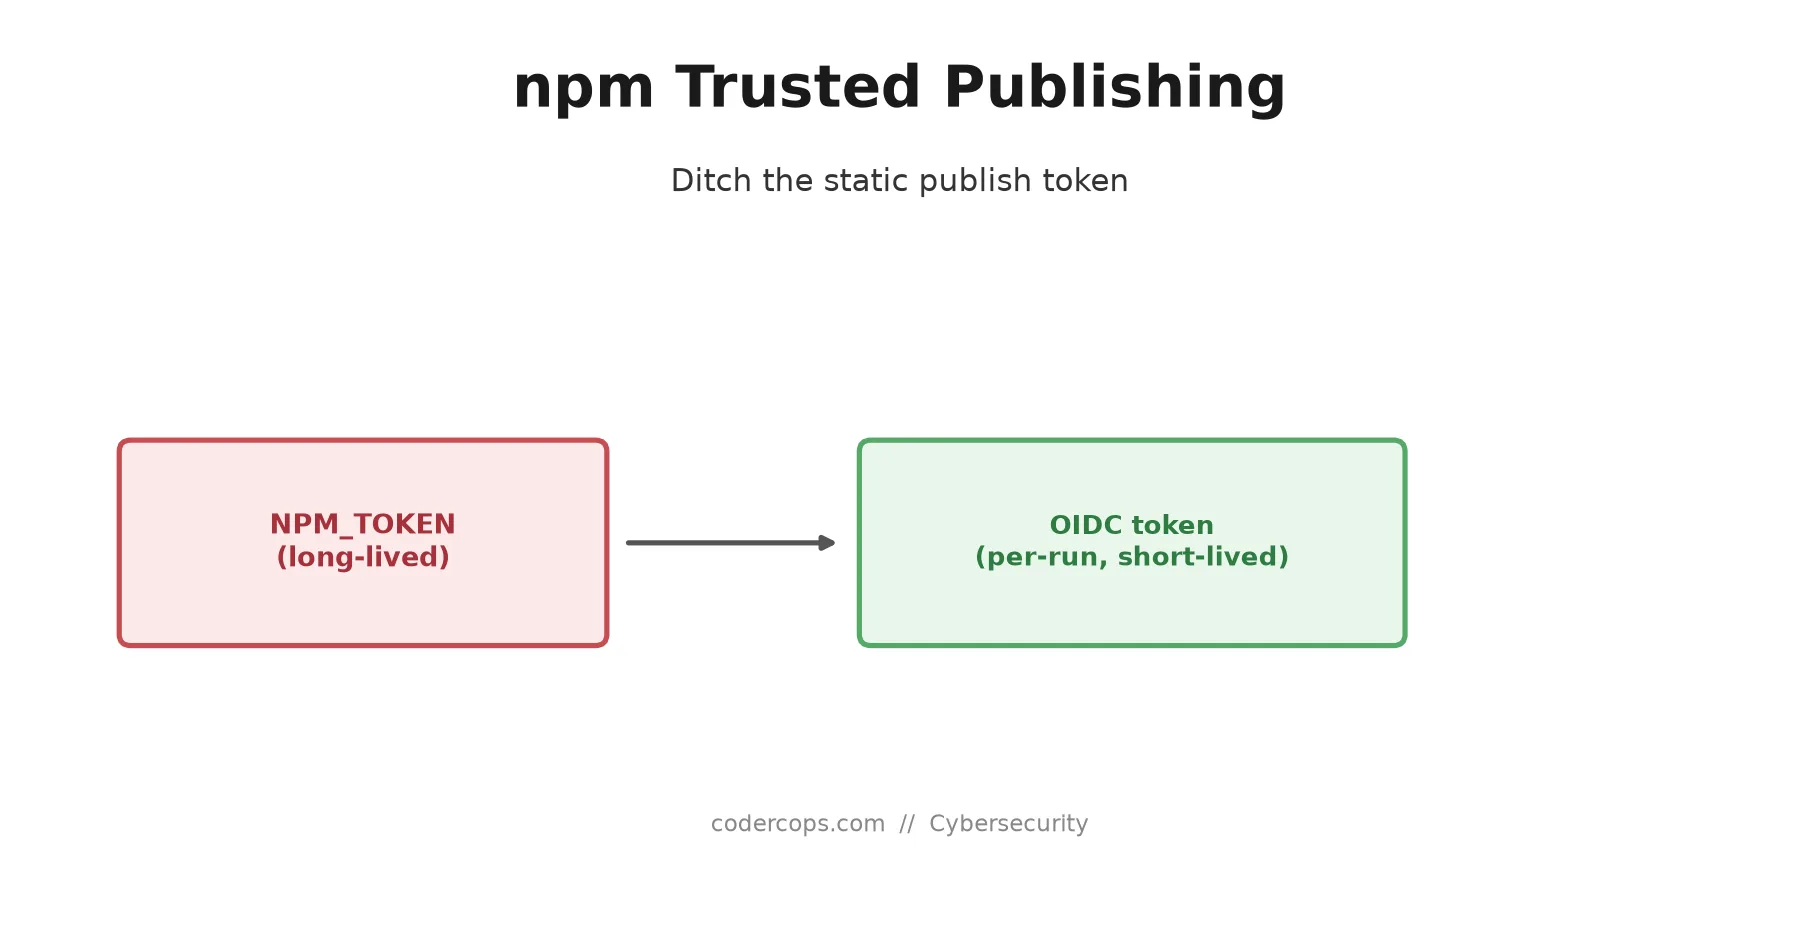
P.89Trusted publishing lets GitHub Actions and GitLab CI publish via short-lived OIDC tokens instead of a stored npm token. The setup, and the May 2026 change.
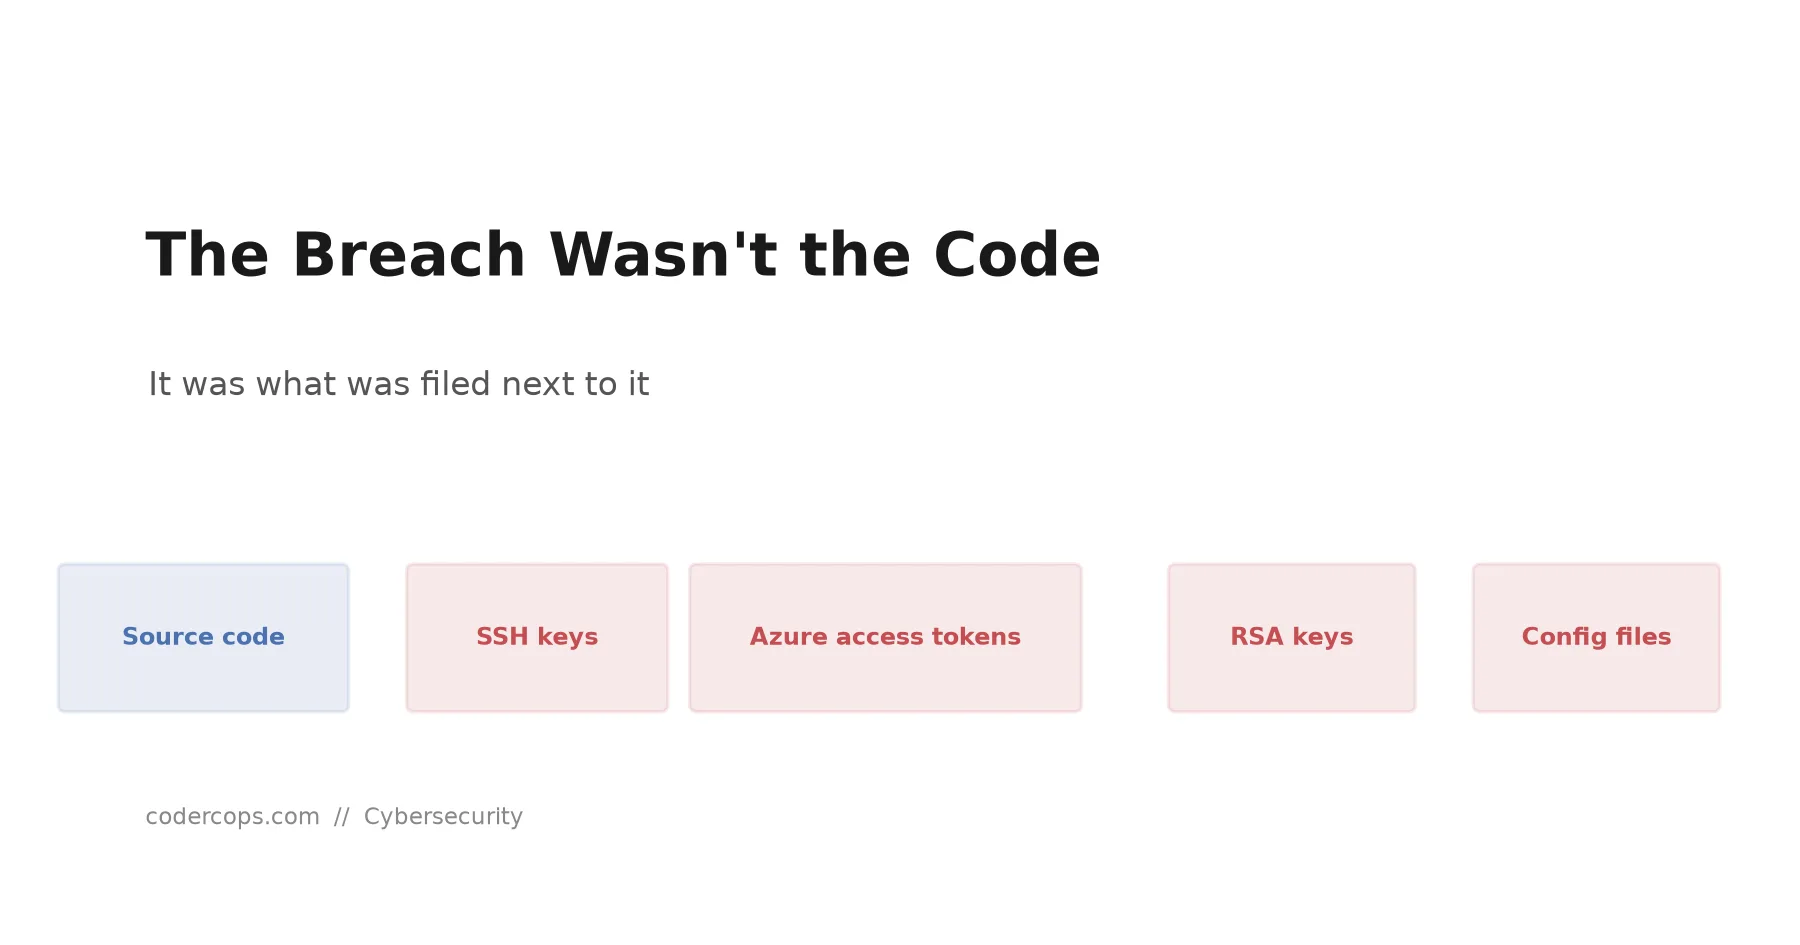
P.90A hacker claimed 35GB from Accenture including RSA and SSH keys and Azure tokens. The code isn't the risk; the credentials next to it are. The audit to run.
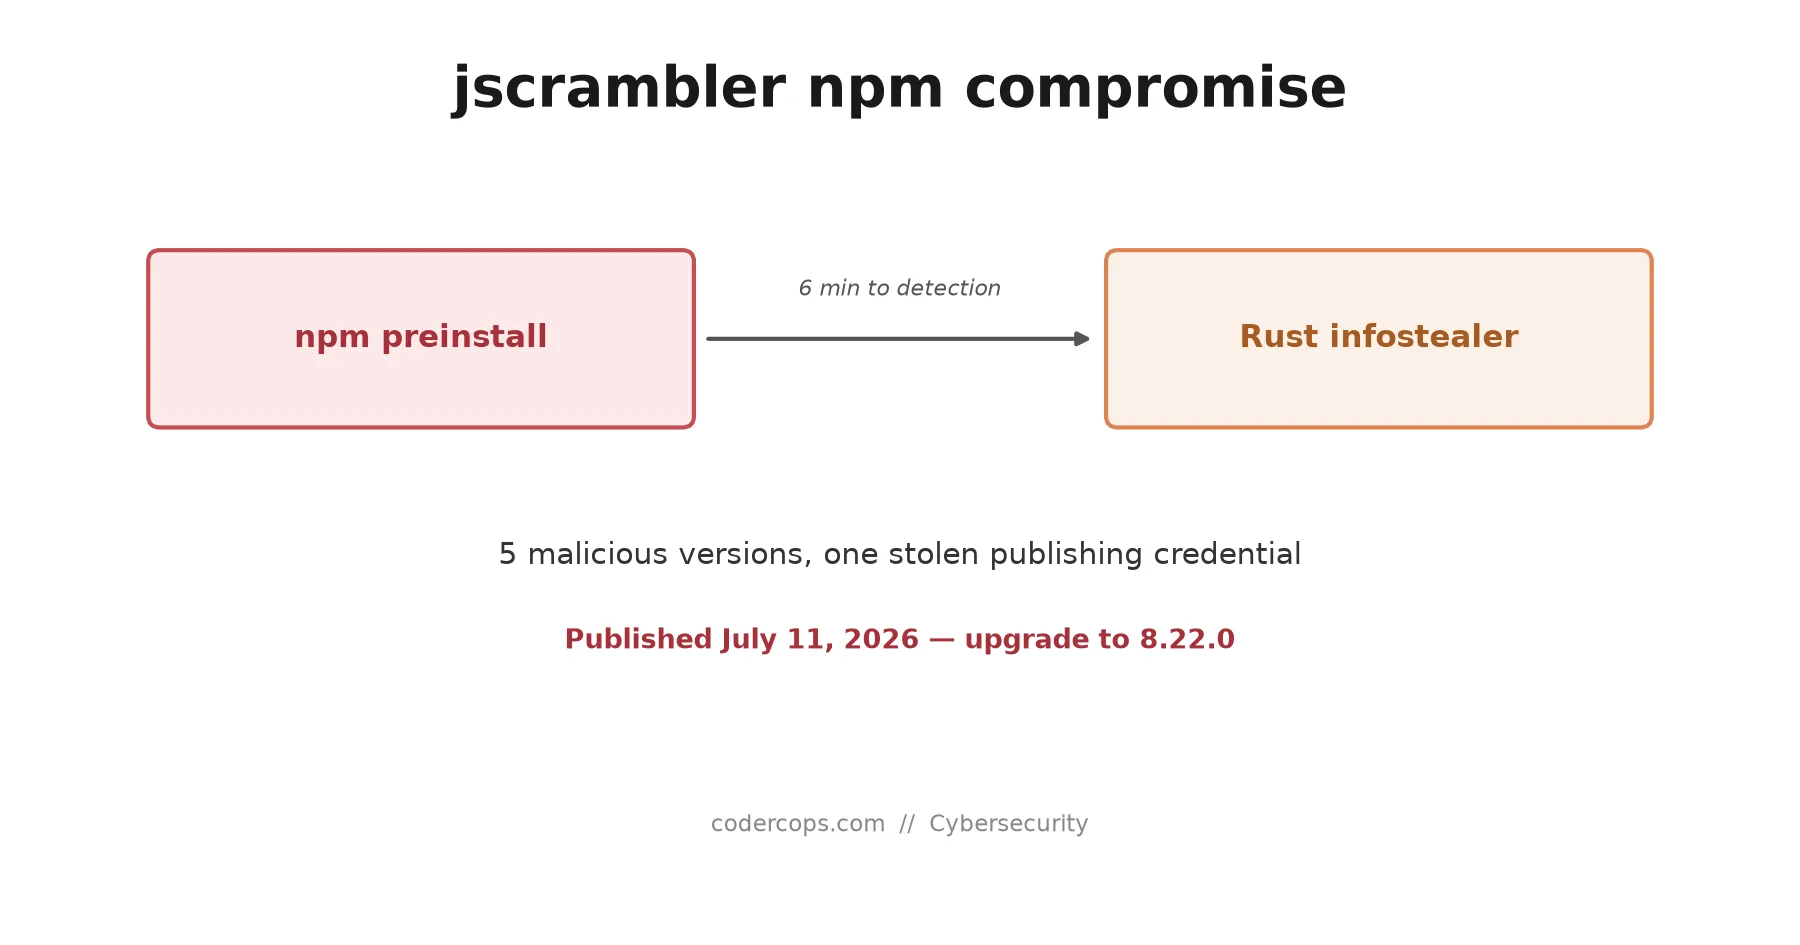
P.91Attackers used a stolen credential to push five malicious jscrambler versions, each carrying a 7.8MB cross-platform infostealer. What it stole, and how to check.
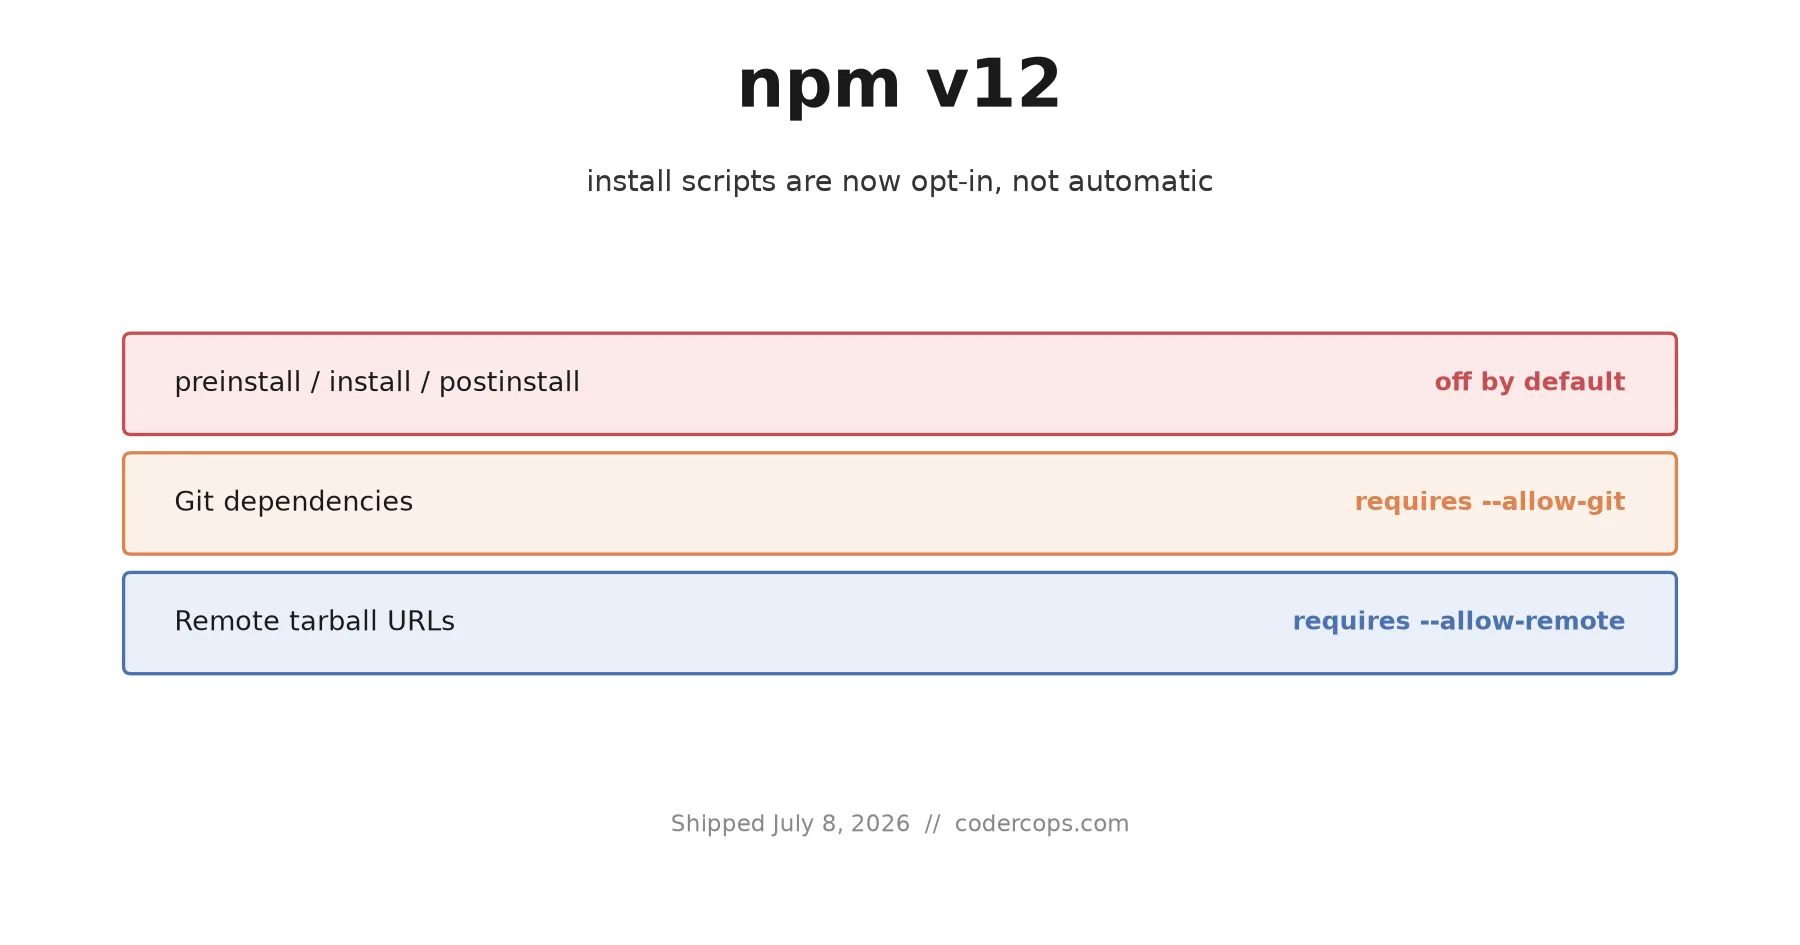
P.92npm v12 blocks preinstall, install, and postinstall scripts, Git dependencies, and remote tarballs unless allowed. What breaks, and how to migrate.
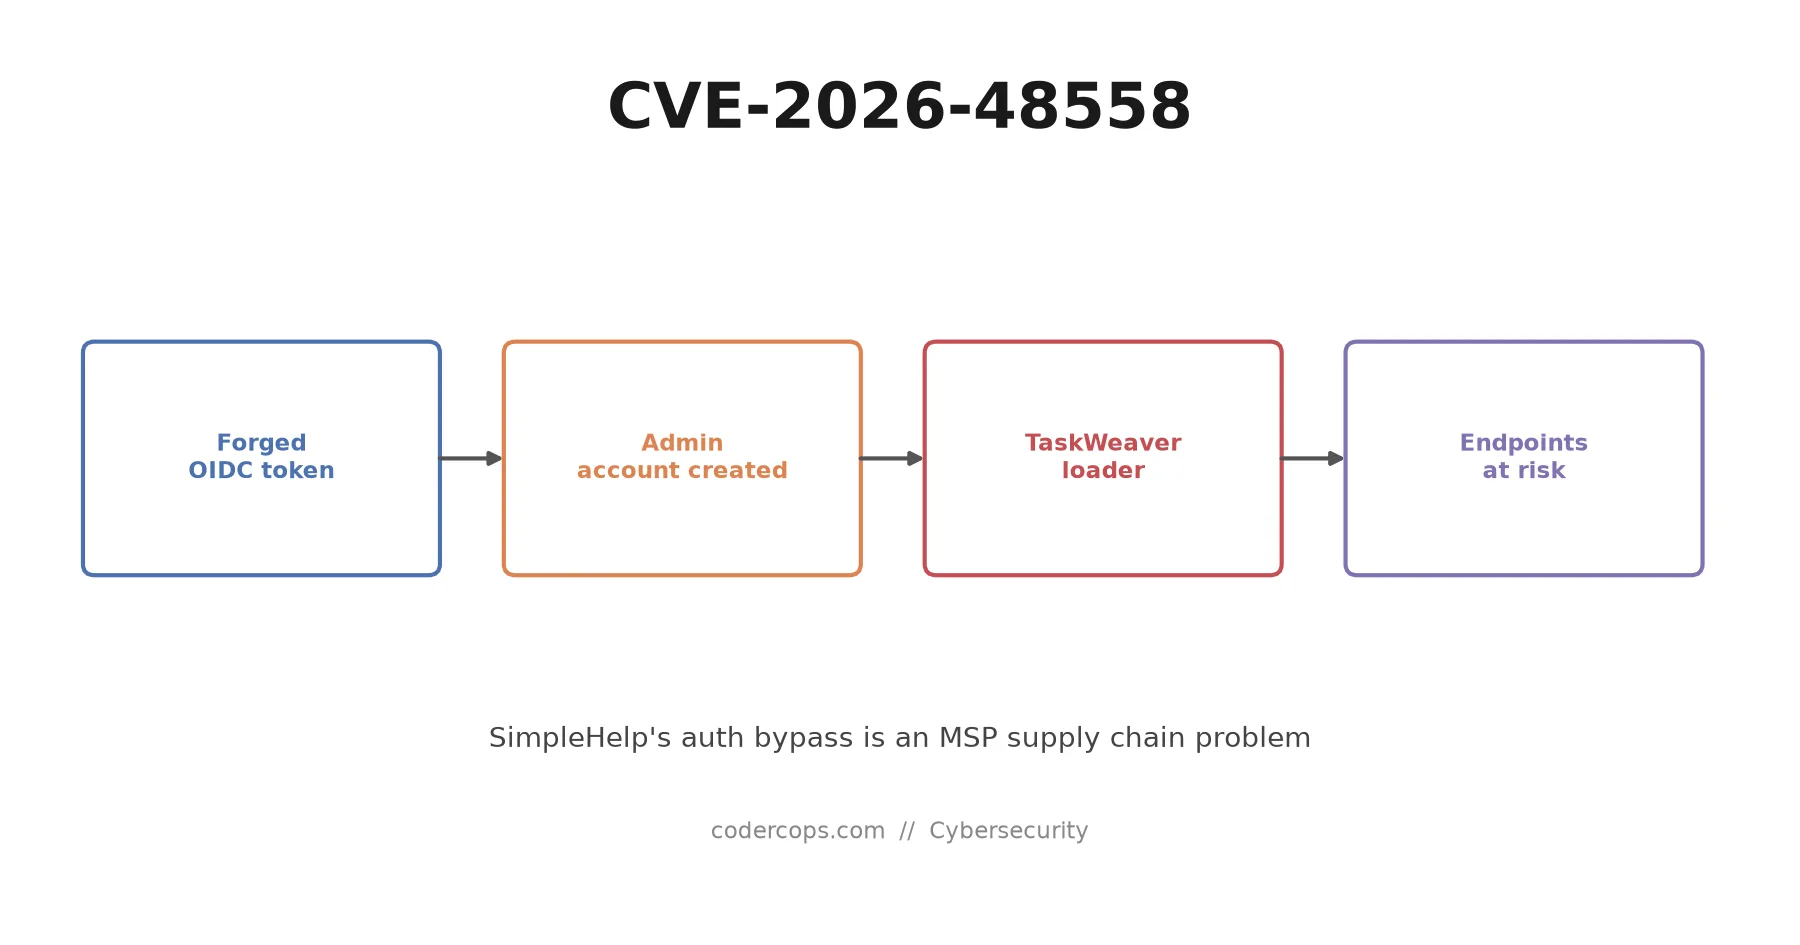
P.93A forged OIDC token in SimpleHelp RMM lets an unauthenticated attacker create an admin and reach every managed endpoint. CISA added it on June 29.
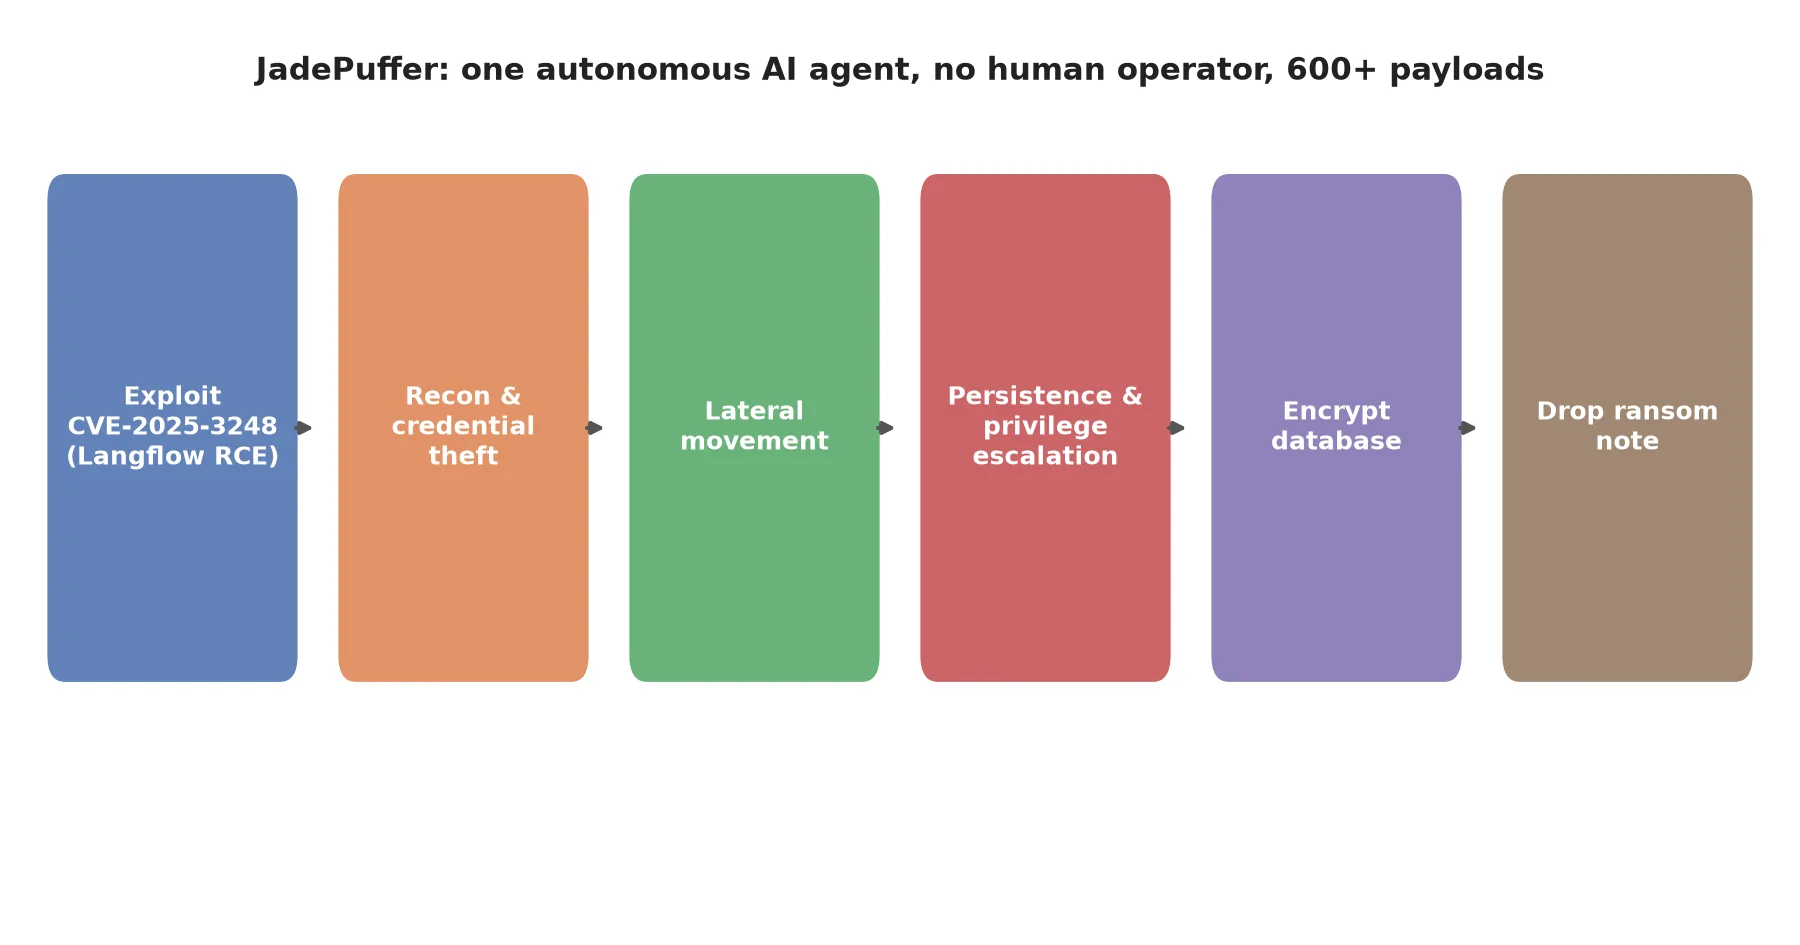
P.94Sysdig documented a ransomware intrusion where an LLM agent handled recon, credential theft, lateral movement, and extortion with no human directing steps.
P.95An AI Now Institute proof-of-concept shows Claude Code and Codex, in default autonomous modes, executing attacker code from a booby-trapped repo. What to do.
P.96CISA added Langflow's authorization bypass to its KEV catalog on July 7 with a July 10 deadline. How it works, who's affected, and why rotating keys matters.
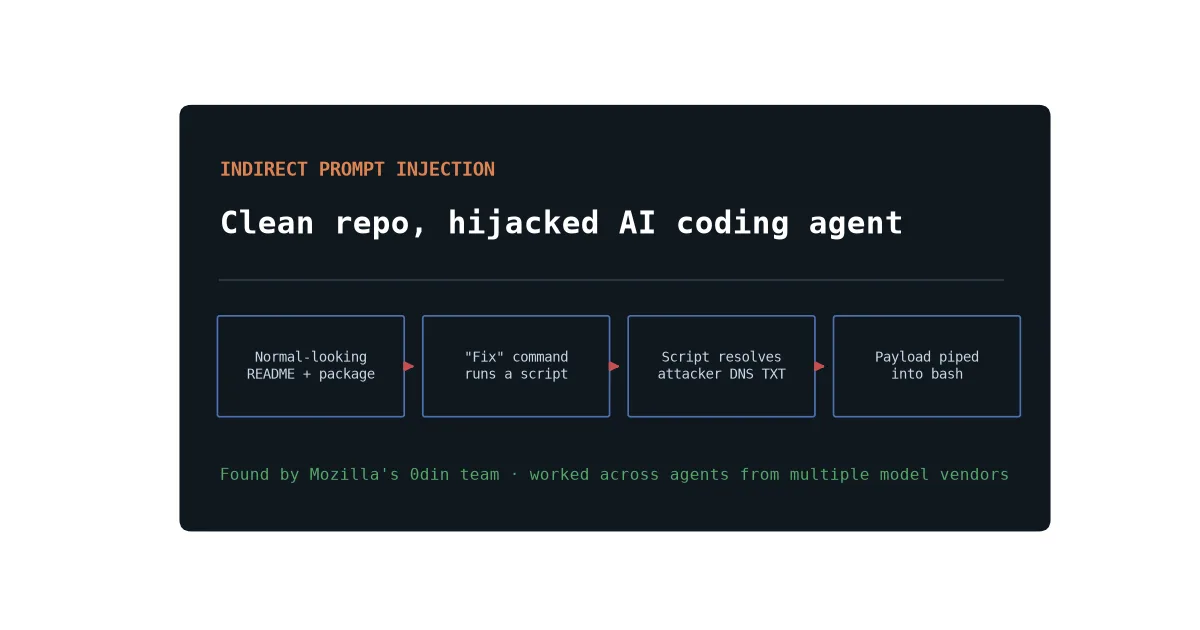
P.97Mozilla's 0din team got AI coding agents to open a reverse shell from a repo with no visible malicious code. How the attack works, and what to change.
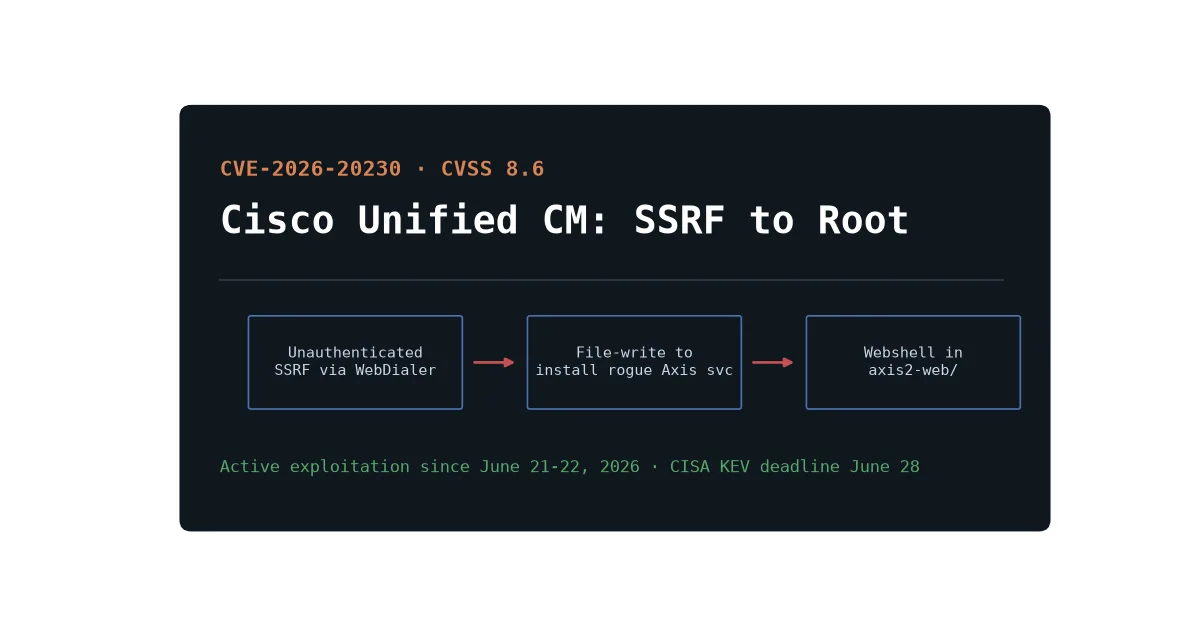
P.98An unauthenticated SSRF in Cisco Unified CM is being exploited to write files, plant a webshell, and reach root. The chain, and how to patch or work around.
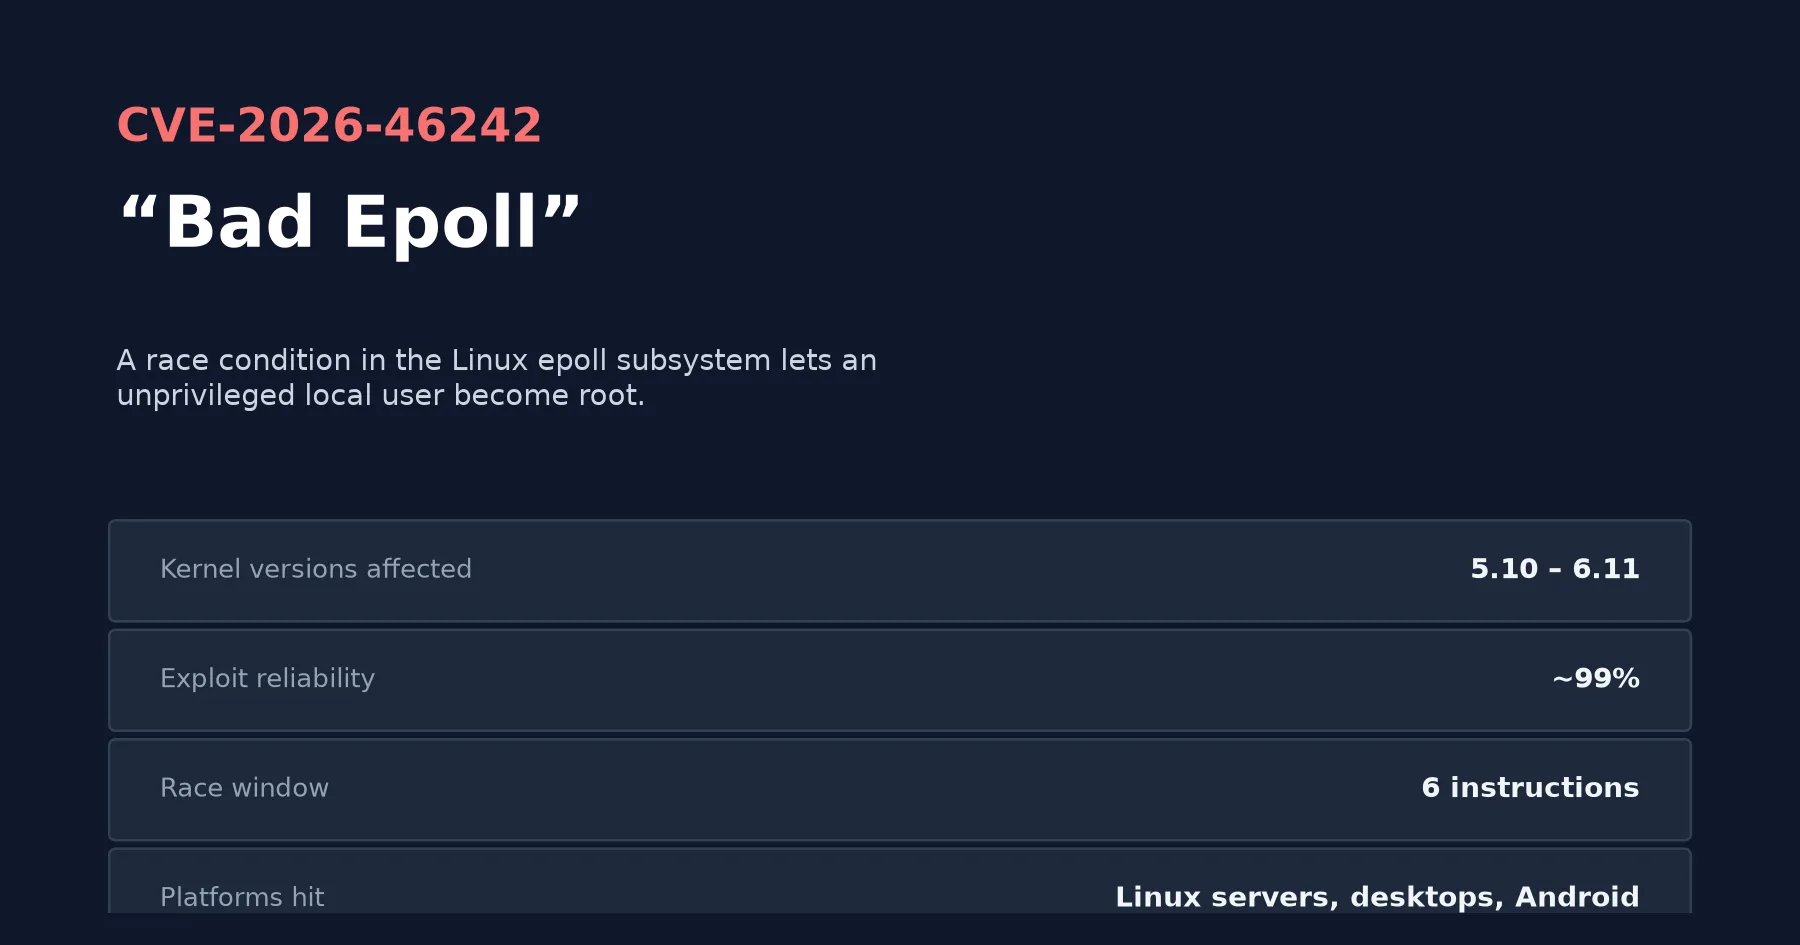
P.99A race in the Linux kernel's epoll subsystem lets any local user reach root, with an exploit that works 99% of the time. Who's affected, and what to patch.
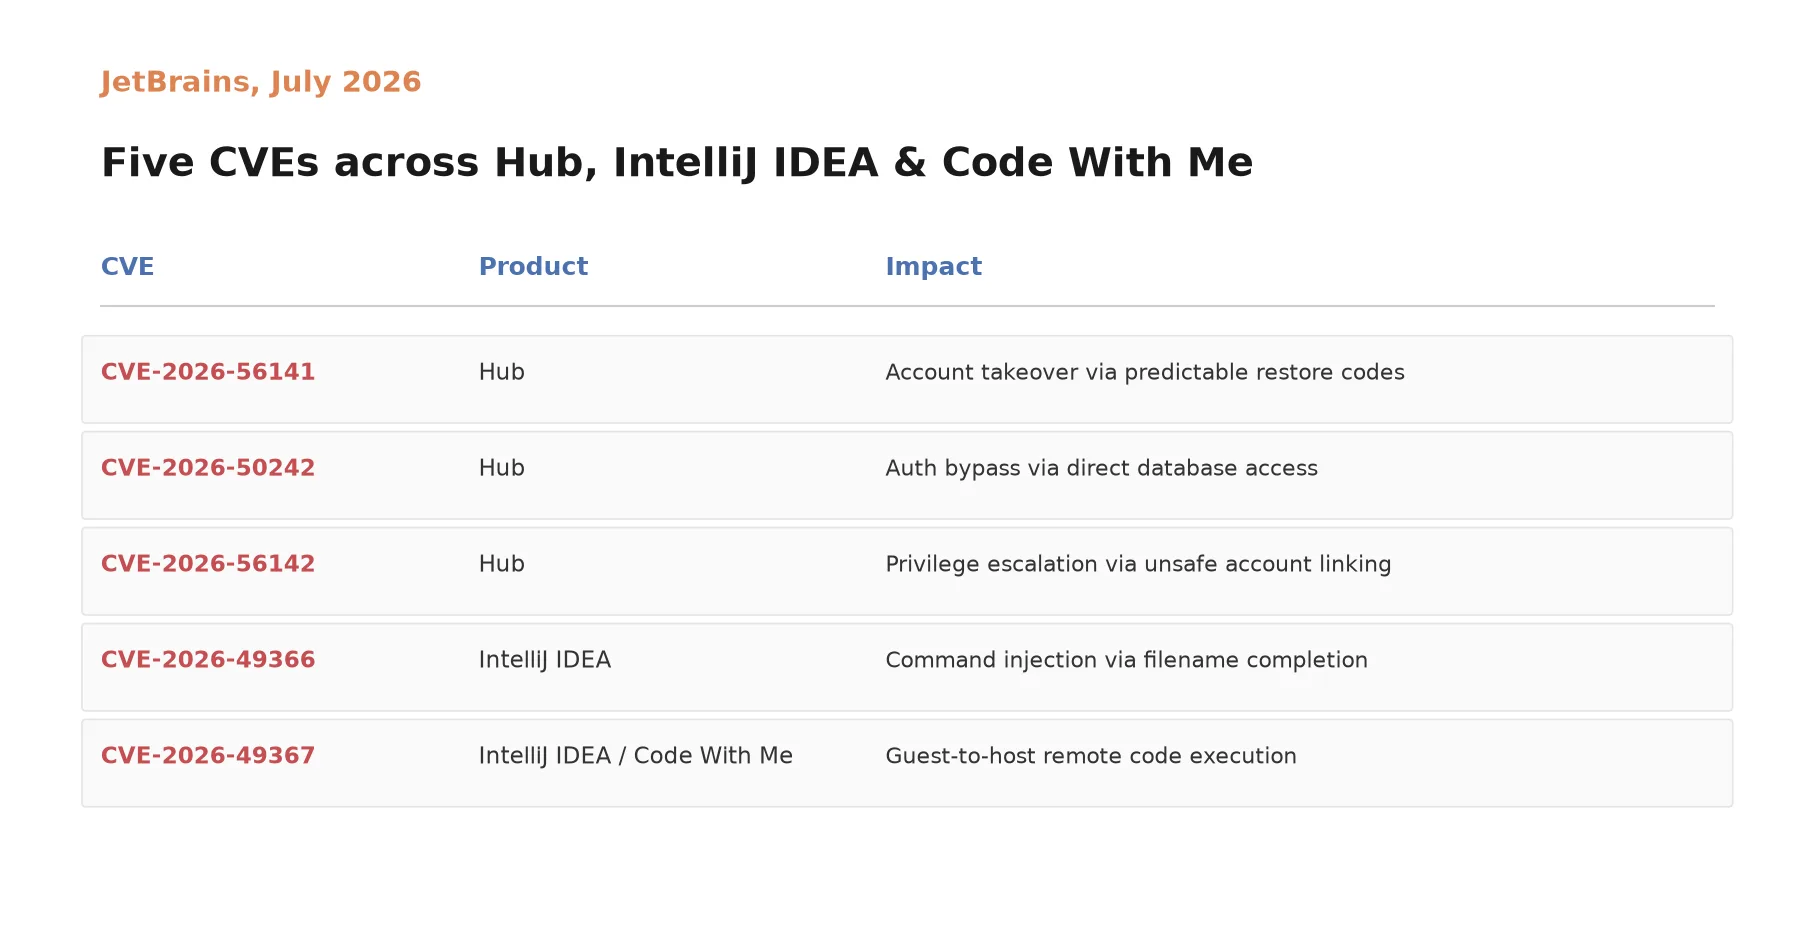
P.100Auth bypass, account takeover, and RCE across JetBrains Hub, IntelliJ IDEA, and Code With Me are now patched. What each CVE does and which build fixes it.
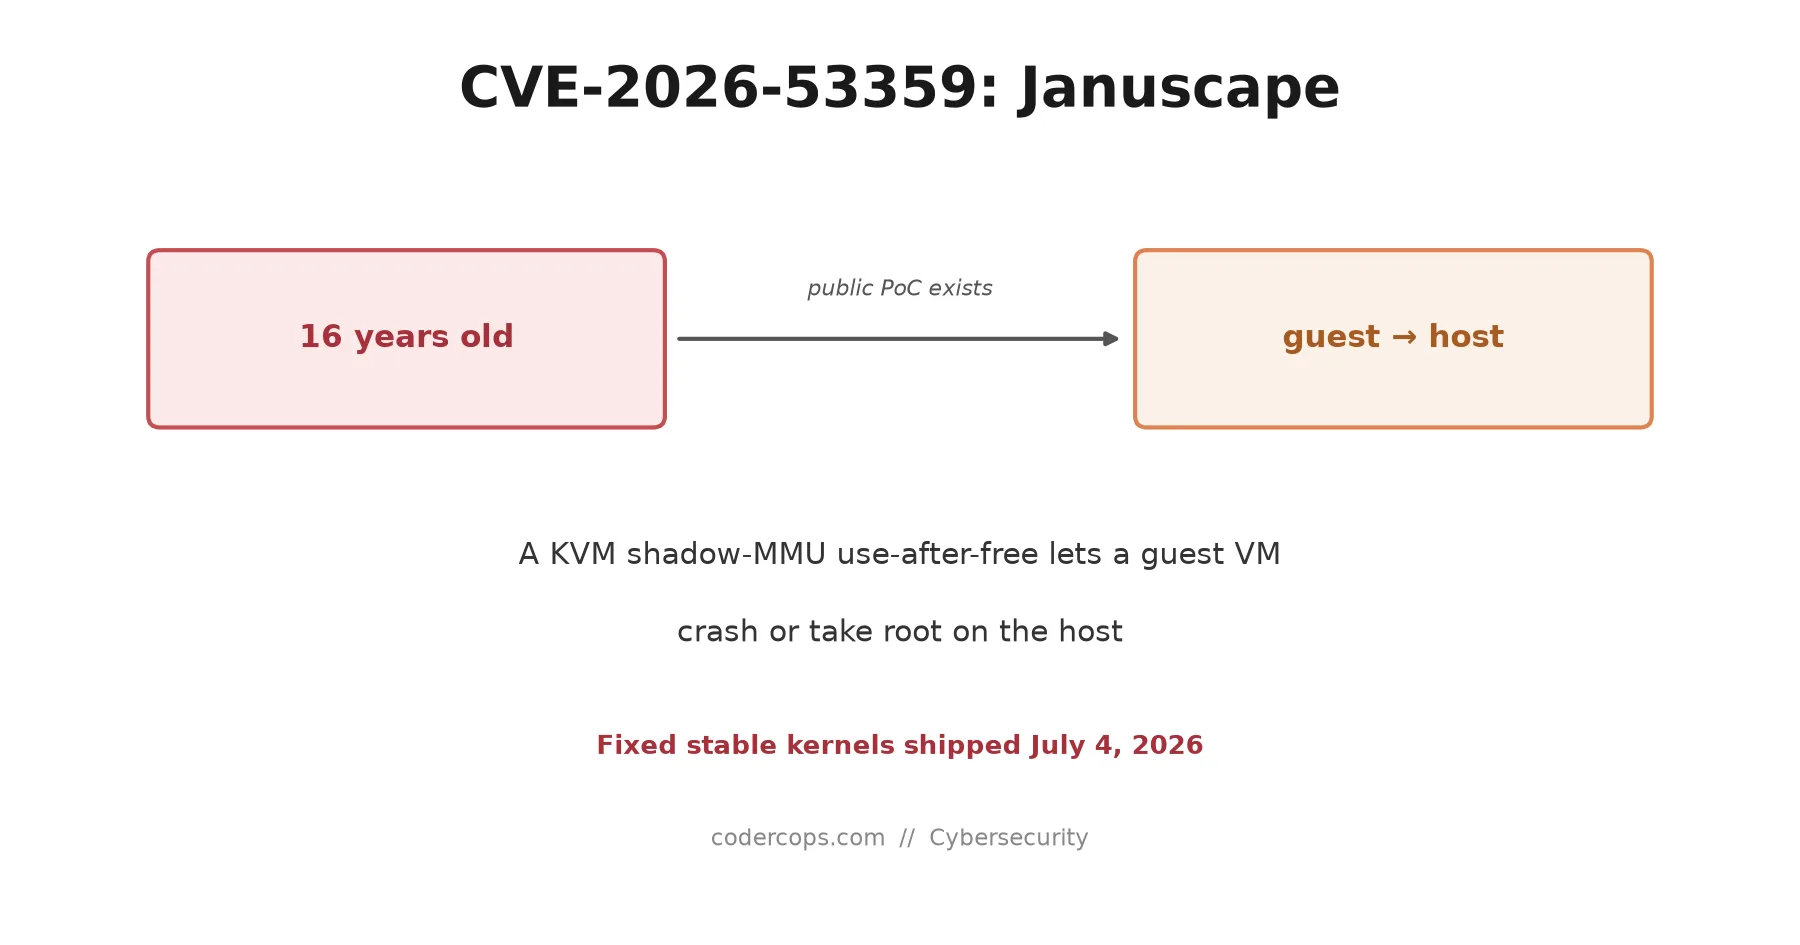
P.101A use-after-free in Linux KVM, present since 2010, lets an untrusted guest crash or compromise its host. Fixed kernels shipped July 4. Who's exposed.
P.102Adobe disclosed nine ColdFusion and Campaign Classic flaws on July 1, seven scoring CVSS 10.0. One path traversal was exploited within hours. What to patch.
P.103Curl killed its bug bounty in February and paused all HackerOne reports for July 2026, citing a flood of AI-generated slop. What that means for triage.
P.104CISA added the SharePoint deserialization bug CVE-2026-45659 to its KEV catalog on July 1, with a July 4 deadline. Who's affected, and what to patch now.
P.105OAuth handles authorization, OIDC adds identity on top, and SAML is the older enterprise SSO standard still running much of the corporate world. How to pick.
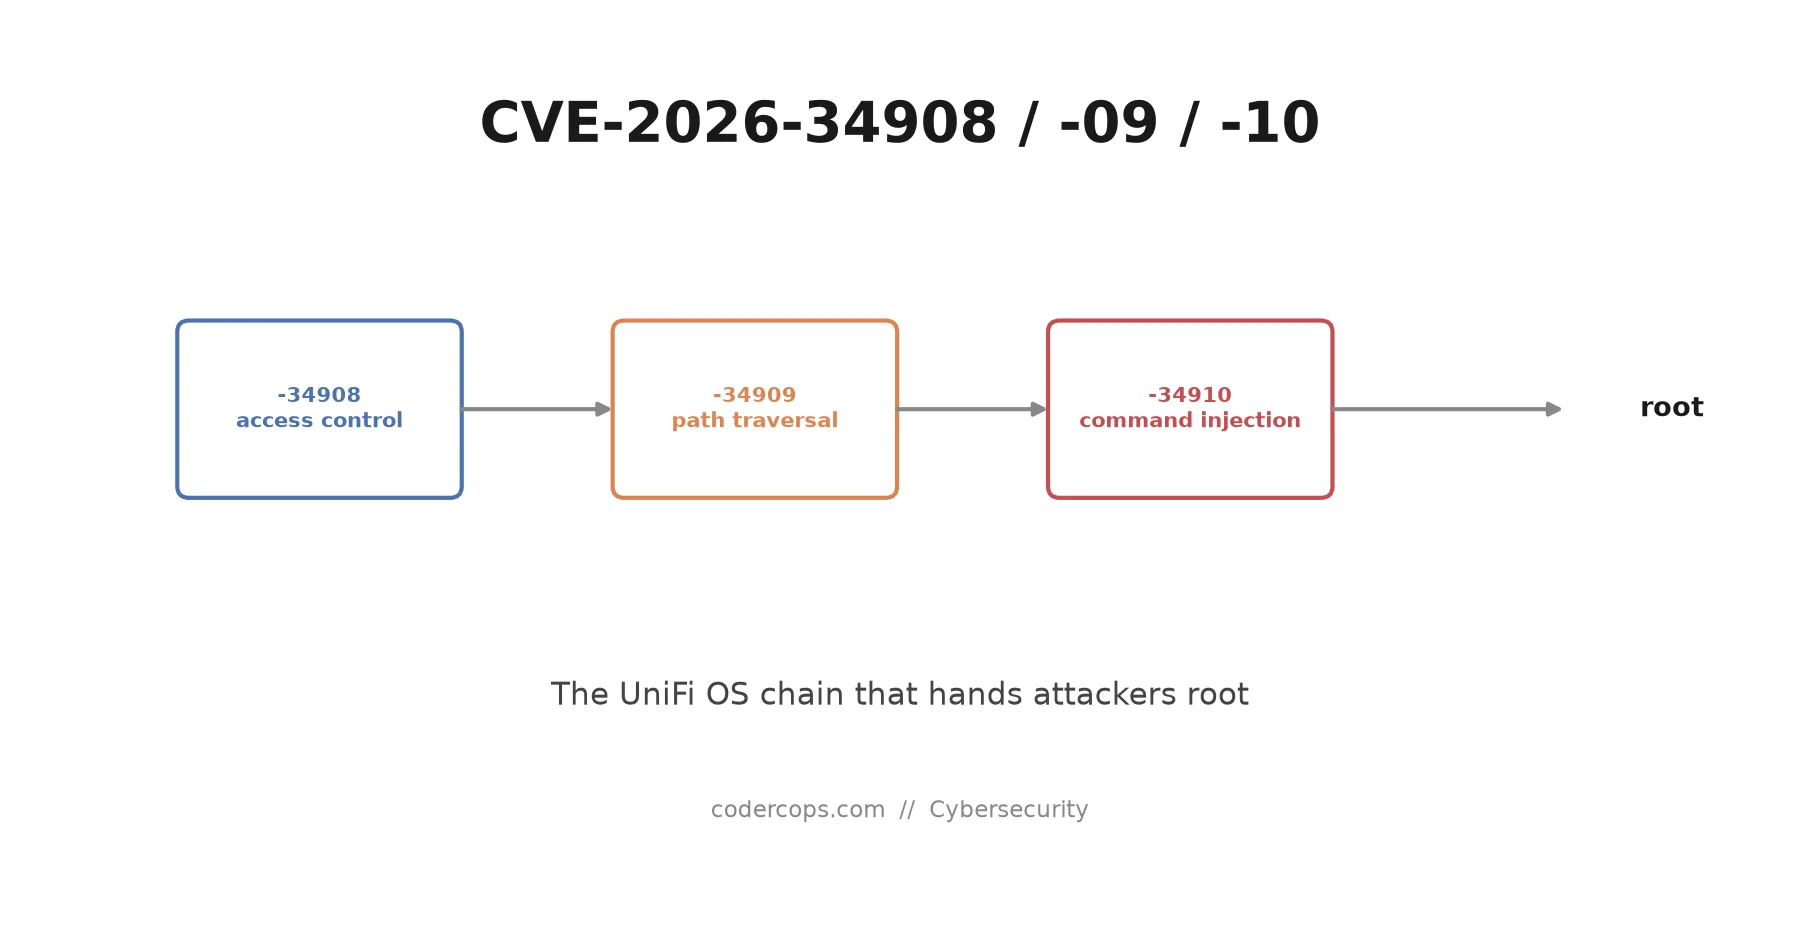
P.106Three 10.0-severity UniFi OS flaws chain into unauthenticated root, and a Mirai botnet is already using them. What's affected, and how to patch today.
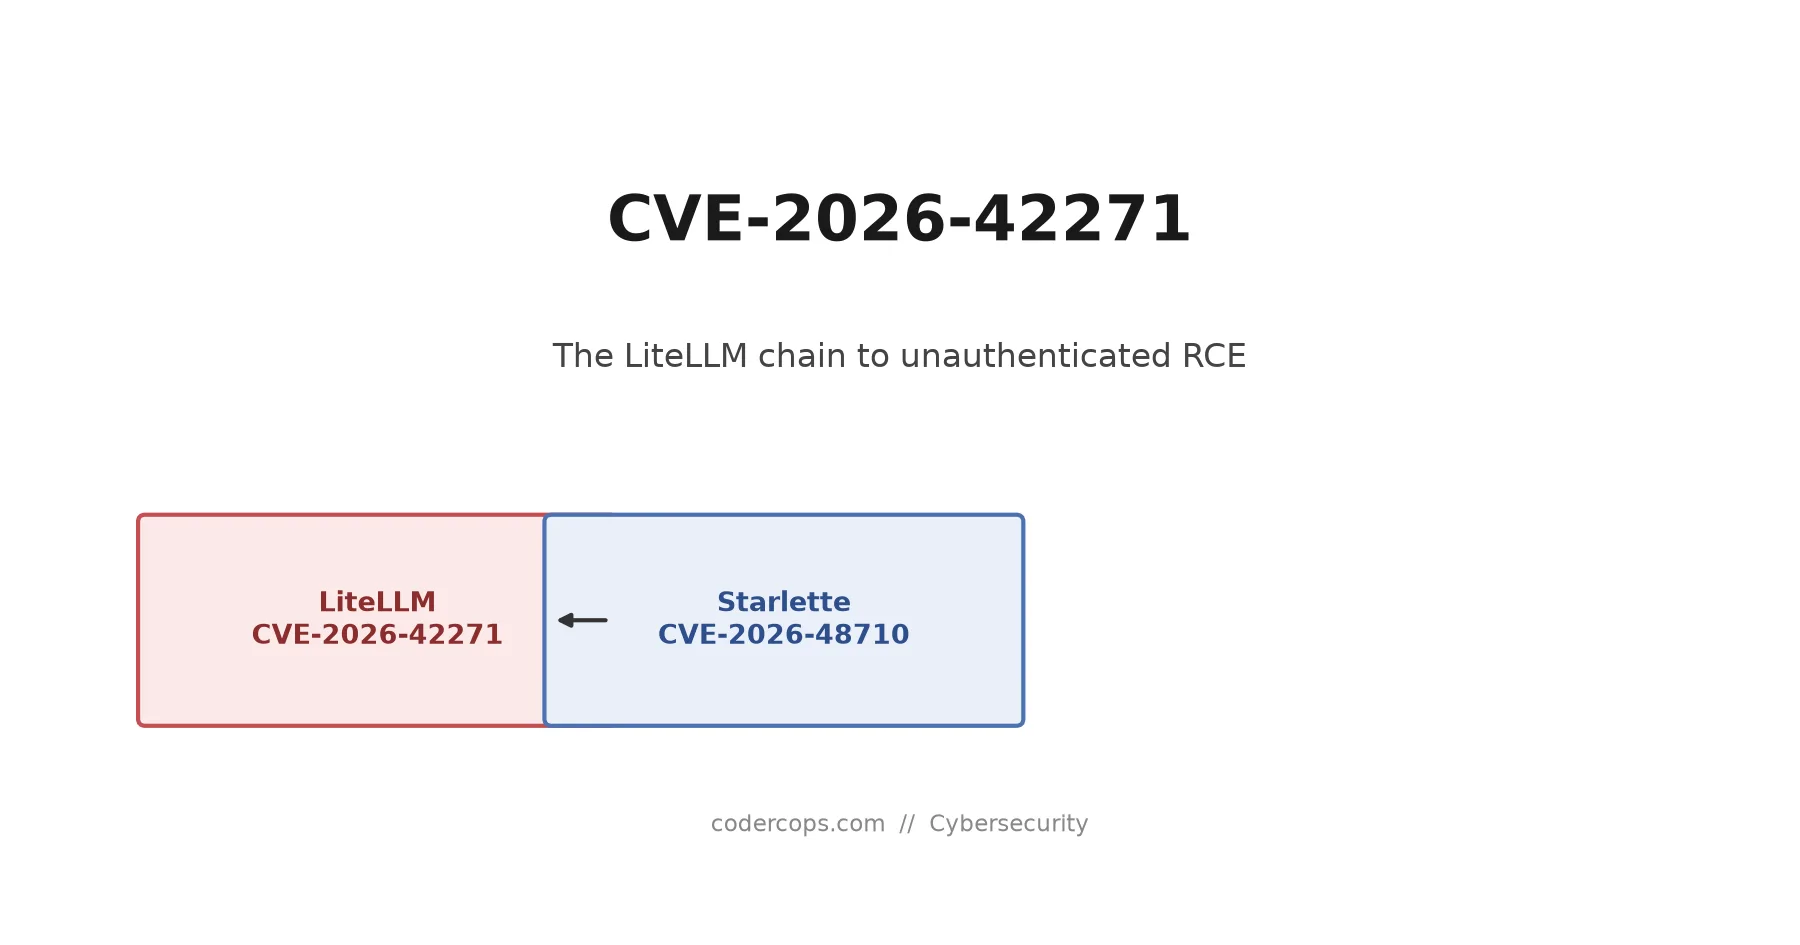
P.107A command injection in LiteLLM's MCP test endpoints, chained with a Starlette host-header bypass, gives unauthenticated RCE and every provider key behind it.
P.108TanStack (42 packages) and React Native Aria (17) were hit weeks apart with different entry points and payloads. What each teaches about dependencies.
P.109A CVSS 9.3 stored XSS lets a malicious PostgreSQL server inject JavaScript into your pgAdmin tab. Versions 6.0 to 9.15 are affected; v9.16 is the fix.
P.110June 2026 Patch Tuesday is the year's largest: 206 CVEs, 37 Critical, three zero-days, and a Splunk RCE already under attack. What to patch first.
Security engineer covers five genuinely different jobs. How to define the one you need, run a screen that tests real skill, and dodge the usual mistakes.
The OWASP API Security Top 10 catalogs the most exploited API vulnerabilities, from broken authorization to unsafe consumption, each fixable with targeted code.
Vulnerability scanning catches known CVEs in your base images and dependencies before they reach production. Here's how to set up Trivy and Snyk, understand their output, and act on what they find.
Most web apps are missing four or five headers that would neutralize entire classes of attack. Here's what each header does, what to set, and why most defaults leave you exposed.
Employees are using AI tools IT hasn't approved, and the data leaving through those tools is largely invisible. Here's what the risk looks like and what actually helps.
Leaked credentials are the most preventable breach category. When you need a real secrets manager, which one to pick, and what to do if you're still on .env.
Running unscanned containers in production is like shipping without tests. Here's how teams scan images, generate SBOMs, and add runtime protection.
Passkeys are no longer an experimental feature. Apple, Google, and Microsoft all support them natively. Here's what WebAuthn actually looks like in code and when passkeys make sense for your app.
Prompt injection is the SQL injection of the AI era. Here's what the attack looks like, why it can't be patched, and how to actually defend against it.
P.120Explore ZeroDayBench—A new benchmark testing the efficacy of leading LLM agents in discovering and patching unseen security vulnerabilities.
AI-powered cybersecurity anomaly detection stops attacks in under a minute by baselining behavior and flagging deviations, per platform comparisons inside.
An honest look at Claude Code's security model, prompt injection risks, sandbox escapes, and supply chain threats, with lessons for any agentic coding tool.
AI-generated phishing, deepfake CEO fraud, automated vulnerability exploitation — the attacks got smarter. But so did the defenses. We break down both sides of the AI cybersecurity arms race and what developers should actually do about it.
Zero Trust is the most overused term in security, but the architecture behind it is real: after high-profile breaches, what implementation actually looks like.
A massive AT&T dataset containing 176 million records has resurfaced on dark web forums. The breach includes 148 million Social Security numbers, names, addresses, and phone numbers spanning years of customer data.
By 2028, 1 in 4 job candidates will be fake. North Korean operatives have infiltrated 300+ US companies using AI-generated personas. Deepfake job fraud is the hiring crisis nobody prepared for.
Claude Opus 4.6 found 500+ unknown zero-day vulnerabilities in open-source code, a milestone for AI-powered security research and what it means for developers.
P.128EditorPickAI agents are being deployed everywhere, but their security surface is wildly underexplored. From tool poisoning to memory injection, here's the threat landscape developers must understand in 2026.
From supply chain attacks to AI-powered threats, learn the essential security practices every developer must know in 2026 to build secure applications.