P.01CVE-2026-88062: OmniRoute's Unauthenticated RCE
A single unauthenticated request can run code inside OmniRoute, the 58k-star AI gateway. Patch status is contested, so verify your build yourself.
Tag
12 articles tagged #CVE.
P.01A single unauthenticated request can run code inside OmniRoute, the 58k-star AI gateway. Patch status is contested, so verify your build yourself.
P.02MikroTik patched three RouterOS bugs after CISA confirmed active exploitation of two: which CVEs to prioritize and how to check your router for compromise.
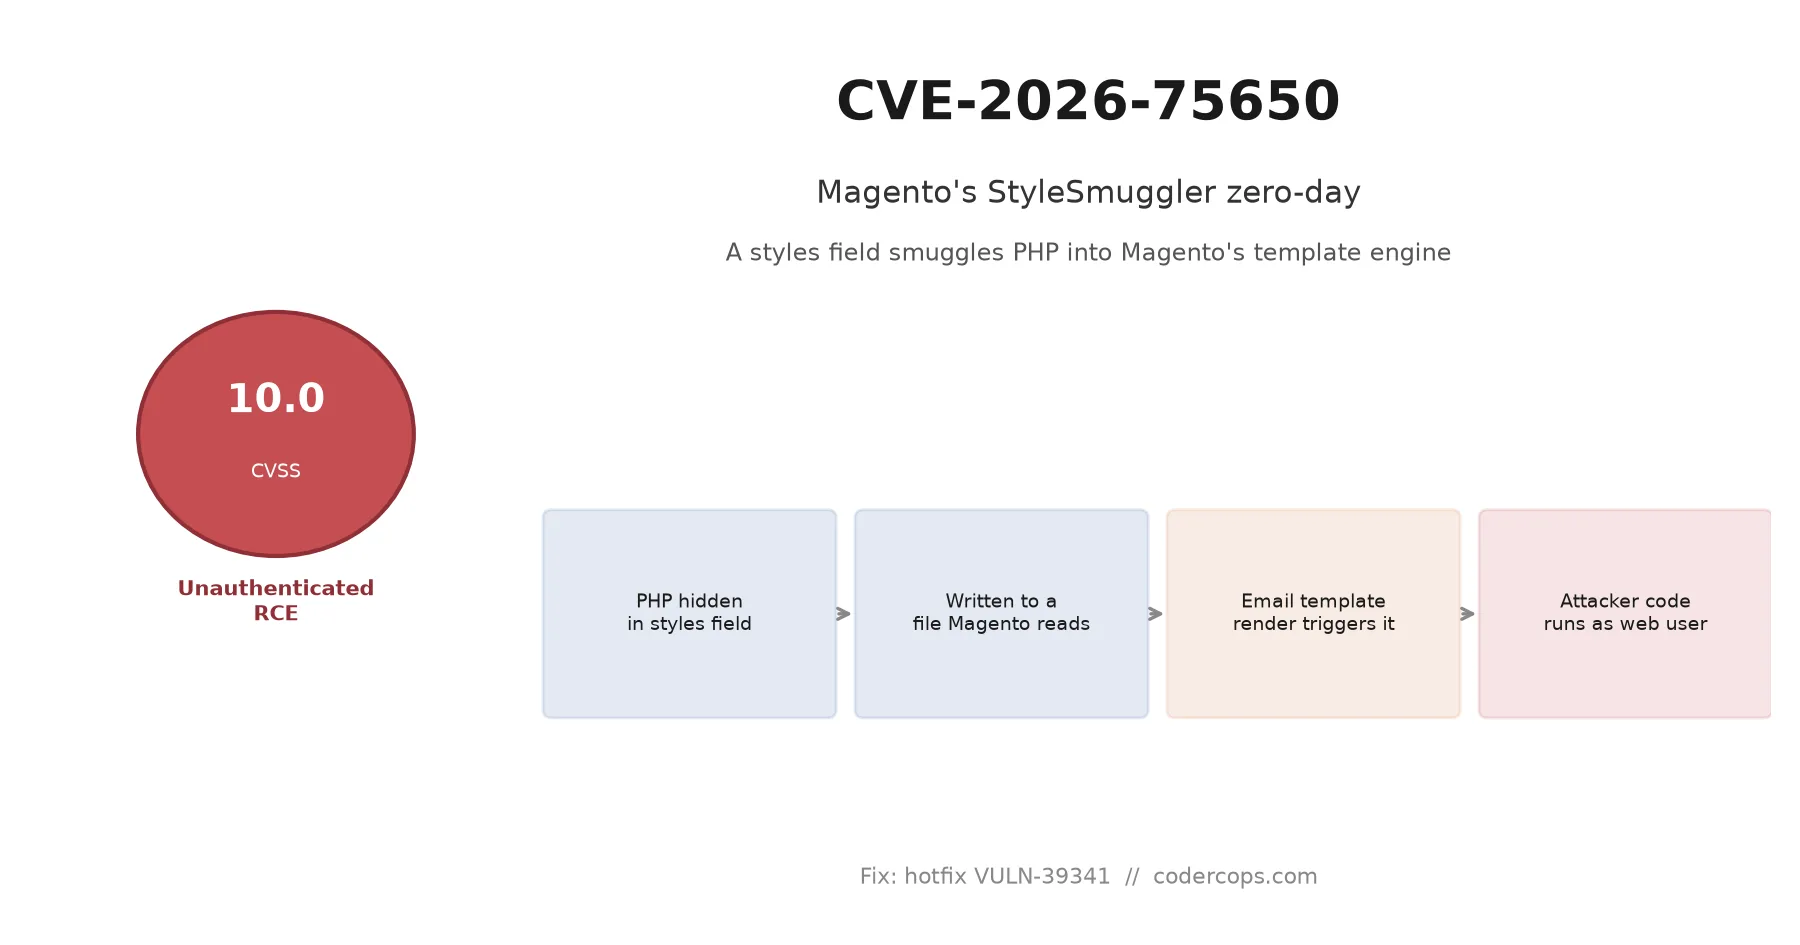
P.03CVE-2026-75650 lets anyone run code on unpatched Magento and Adobe Commerce stores. Sansec found it deploying a Rust backdoor before Adobe even patched.
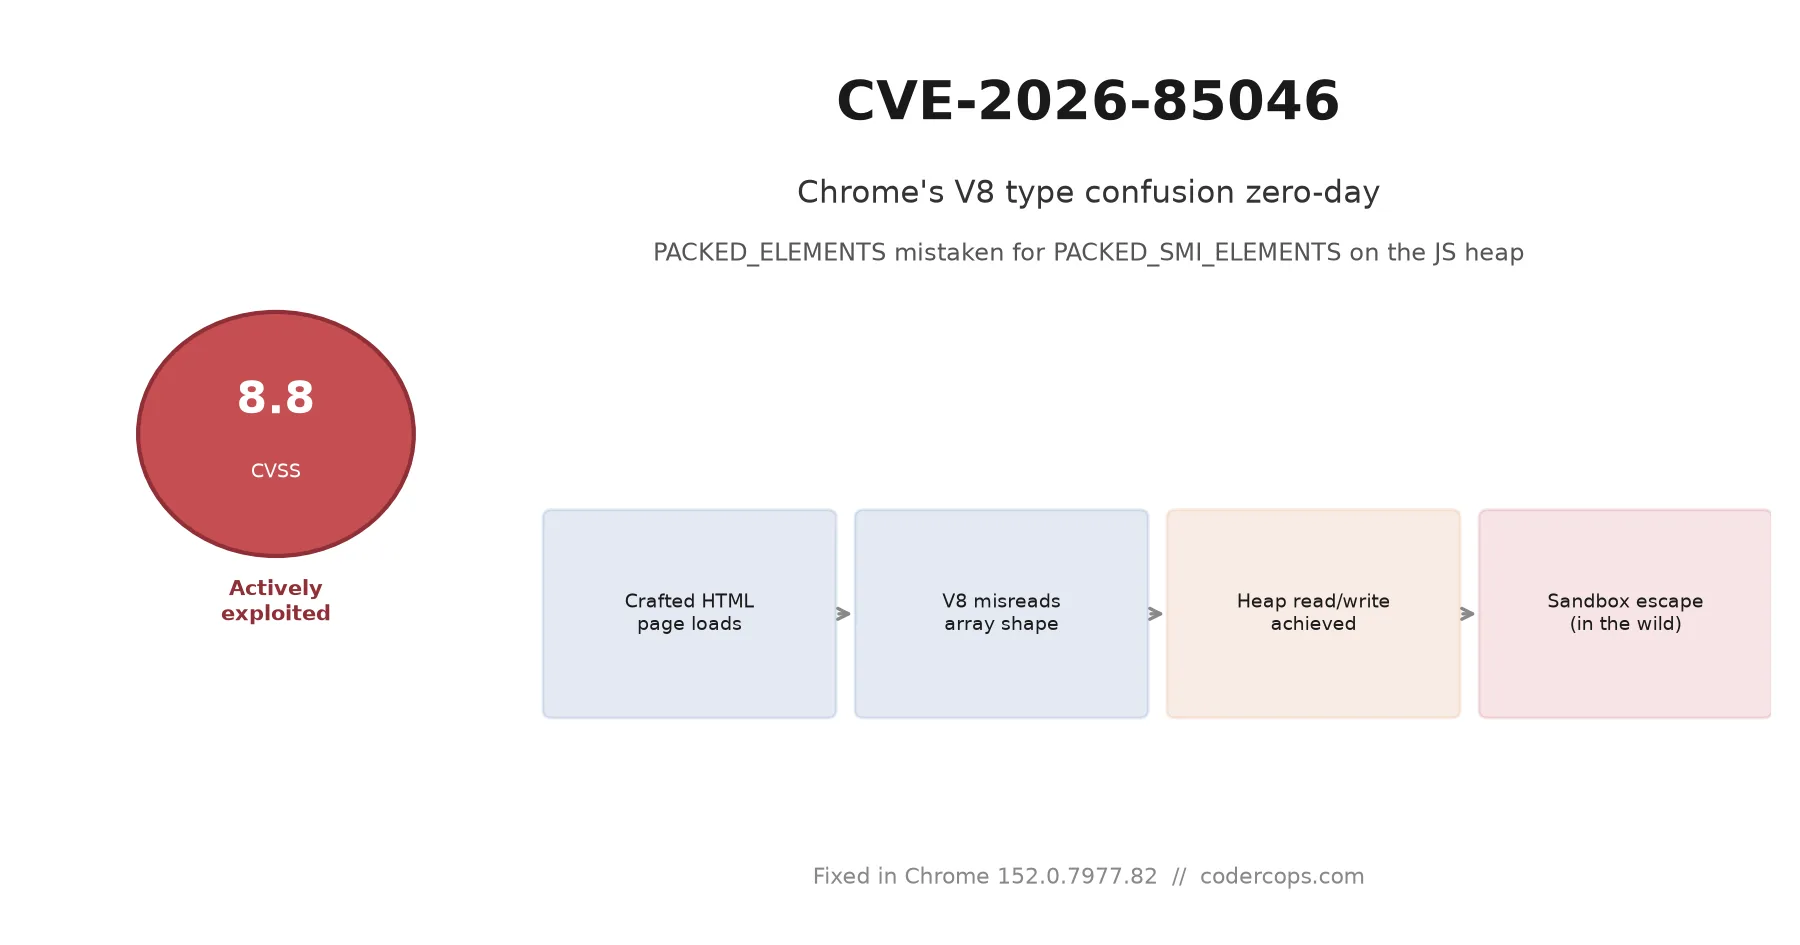
P.04CVE-2026-85046 is a Chrome V8 type confusion bug already exploited in the wild. Here's who's affected, what version fixes it, and how fast to move.
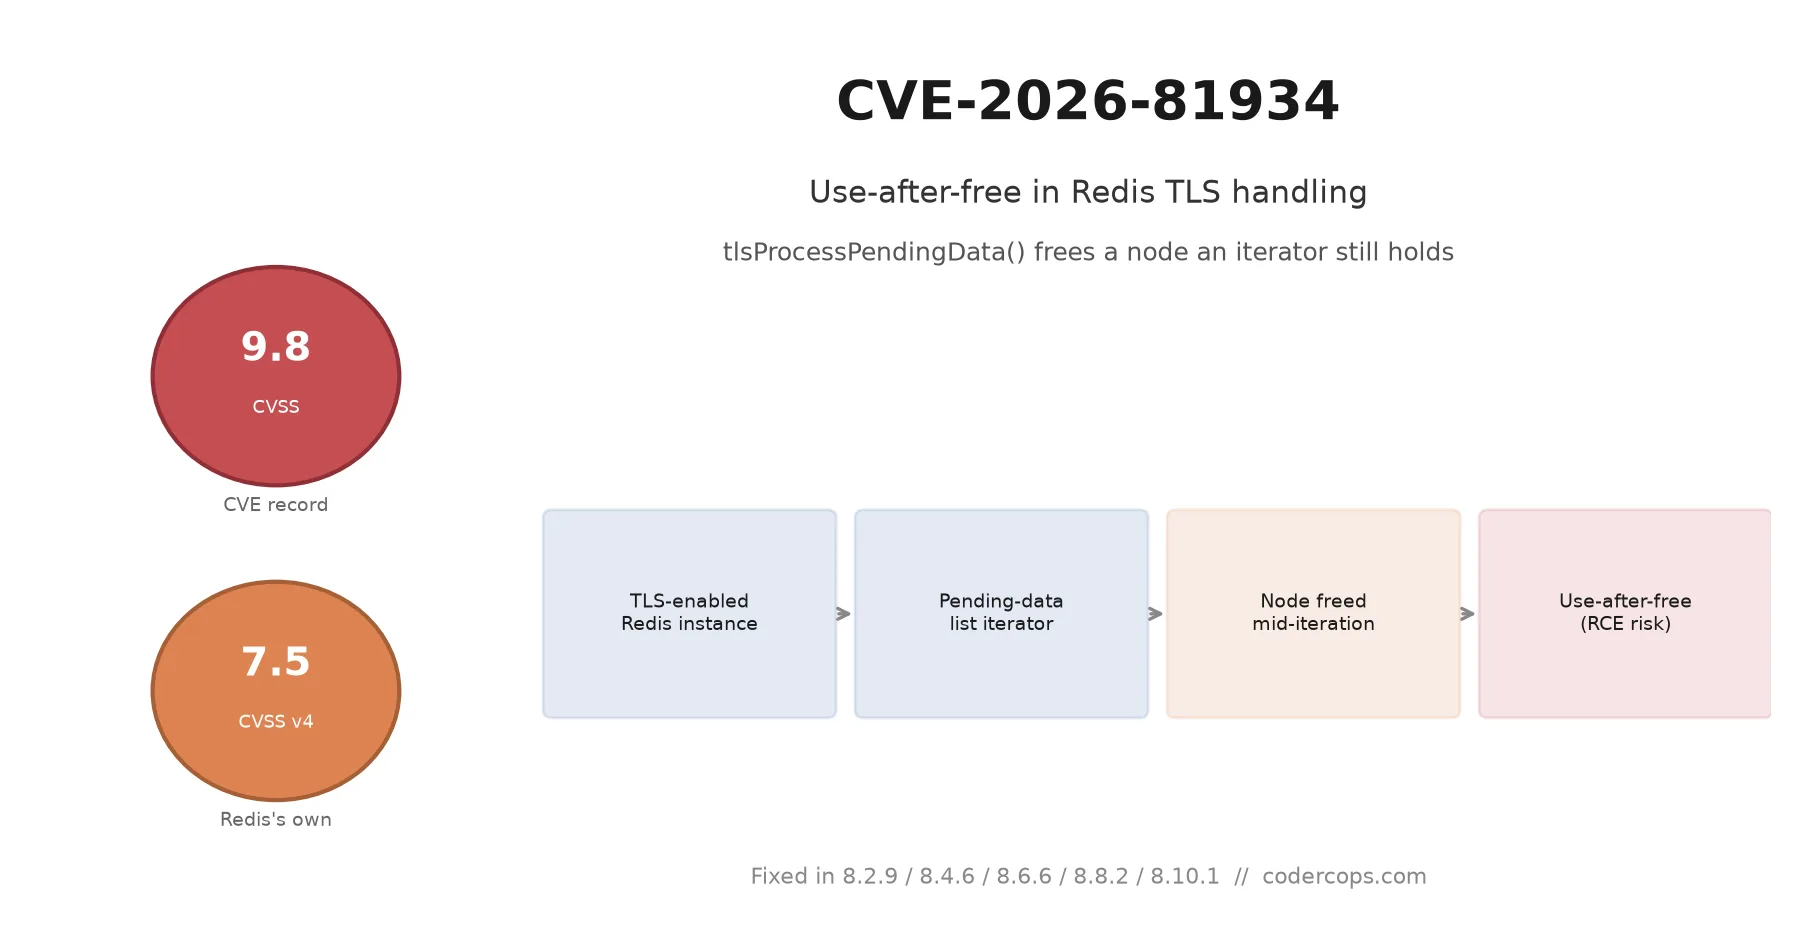
P.05CVE-2026-81934 is a use-after-free in Redis's TLS pending-data handling, with a public PoC. If you don't terminate TLS inside Redis, it mostly passes you by.
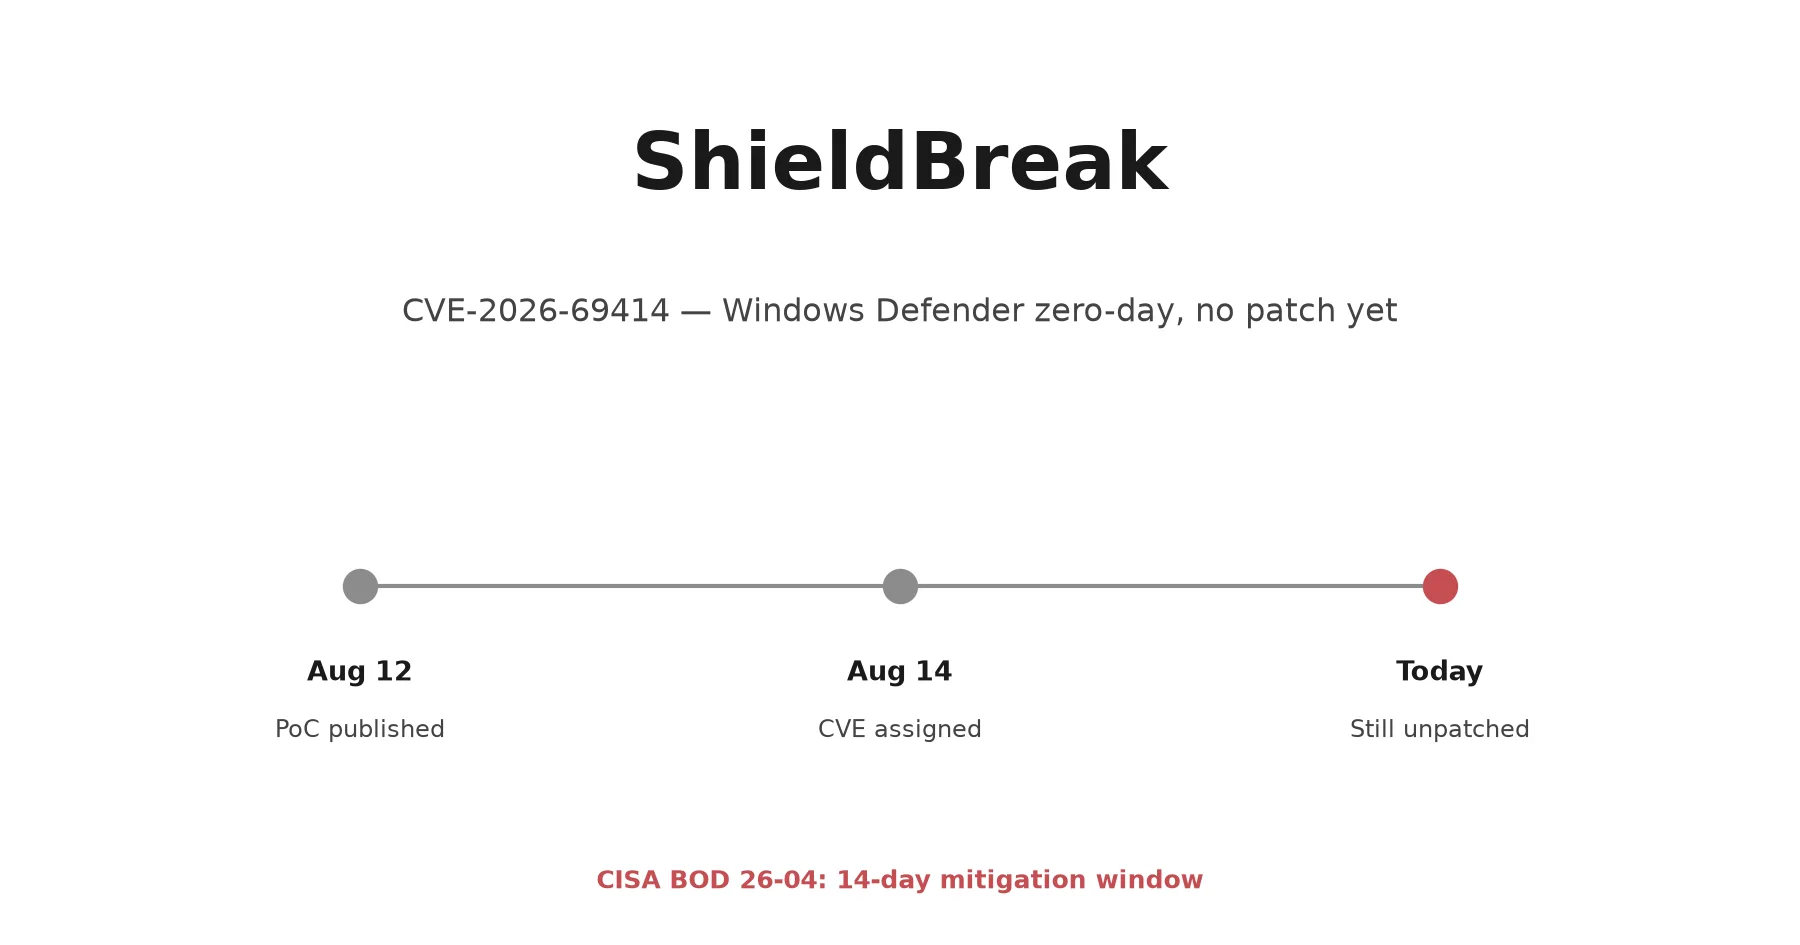
P.06A public proof-of-concept for a Windows Defender privilege-escalation flaw has circulated since August 12 with no fix shipped. What to do about it now.
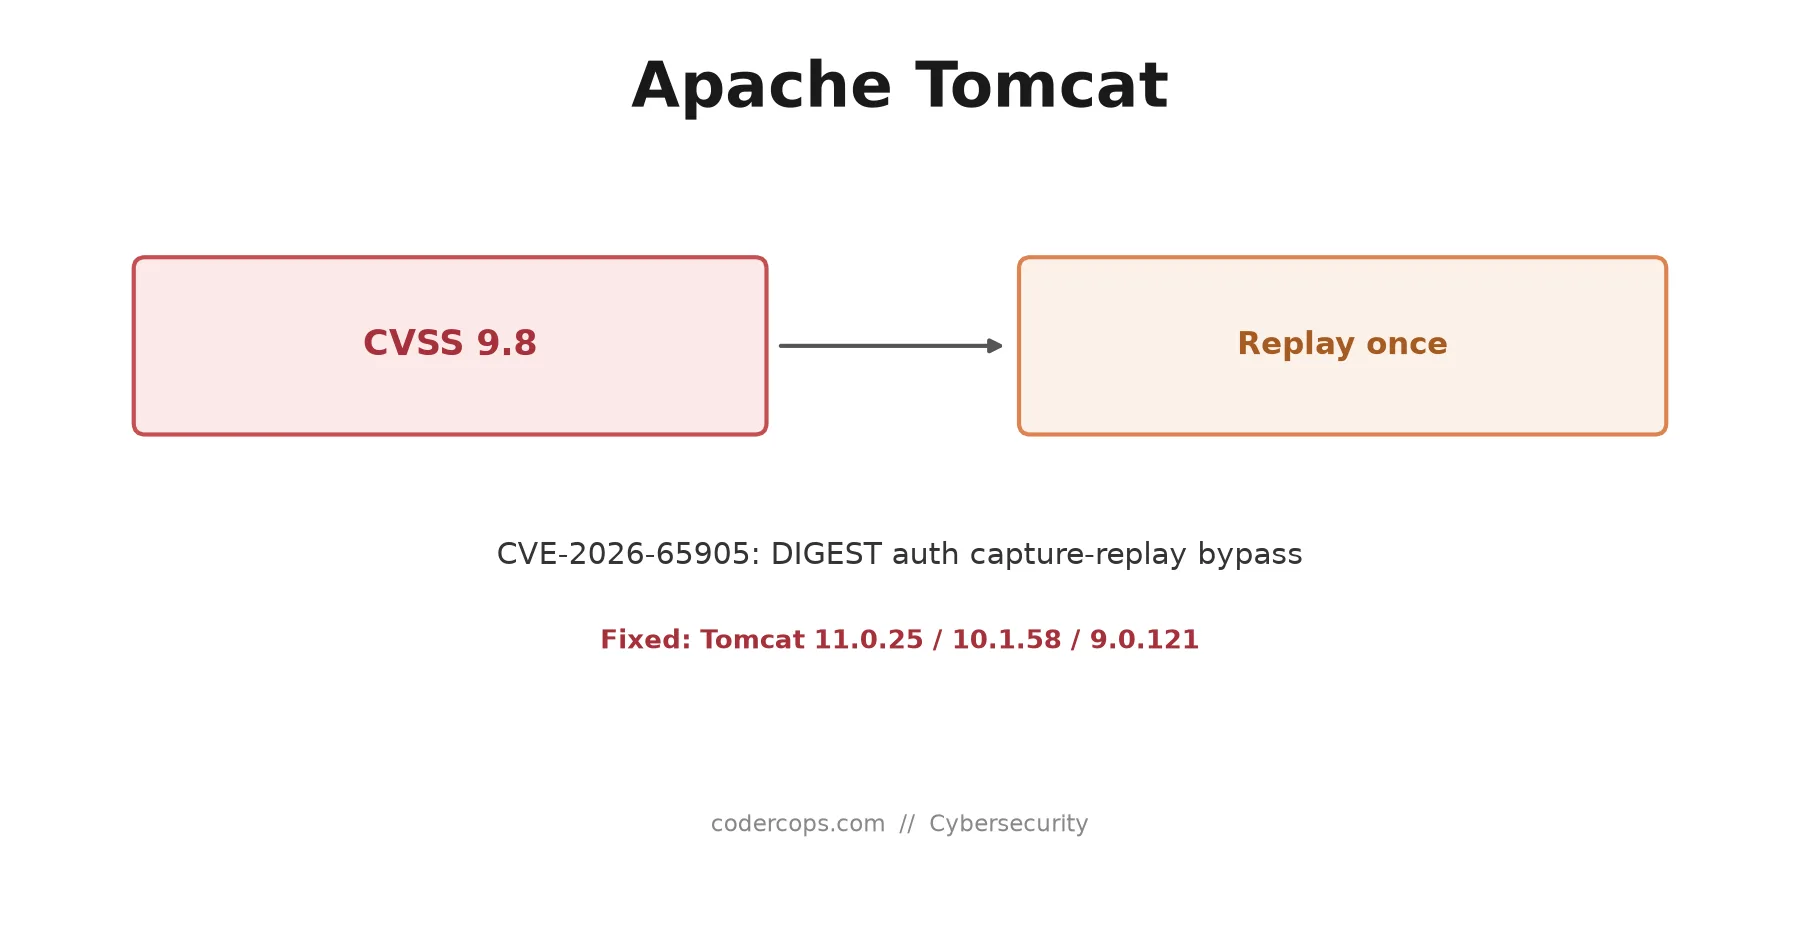
P.07A capture-replay flaw in Tomcat's DIGEST authenticator lets an intercepted request be replayed once inside the nonce window. Critical, but narrow.
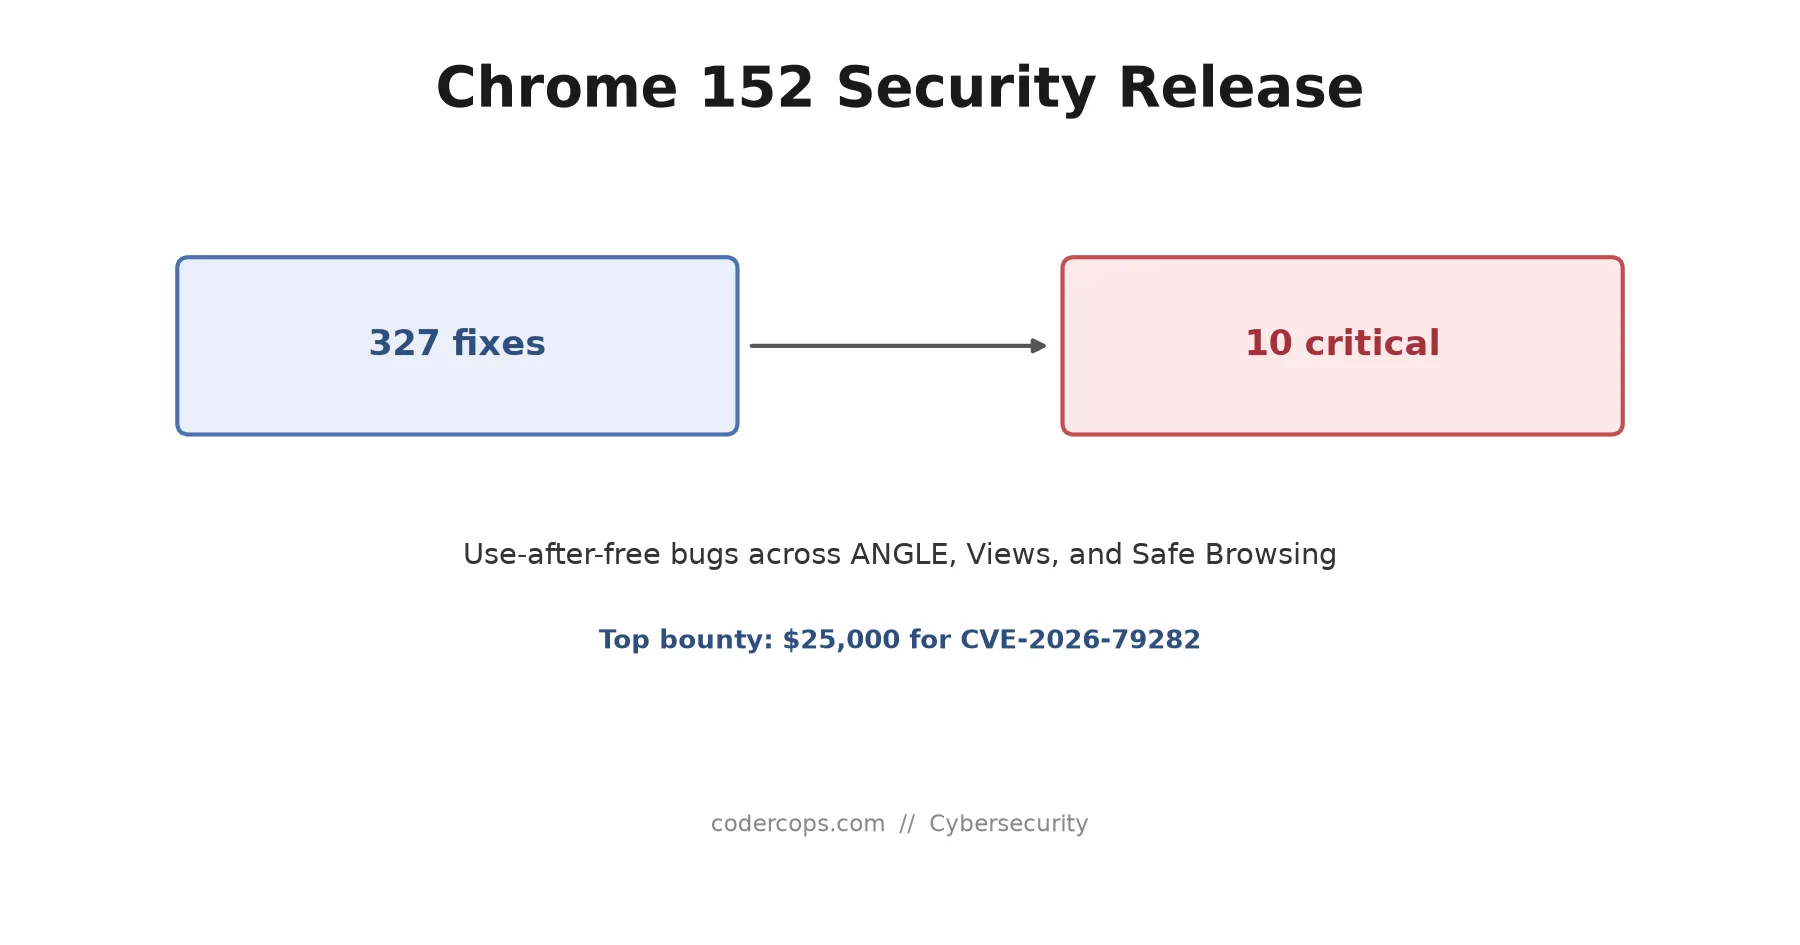
P.08Chrome 152 landed 327 security fixes, 10 of them critical use-after-free bugs in ANGLE, Views, and Safe Browsing. Why not-exploited isn't the same as safe.
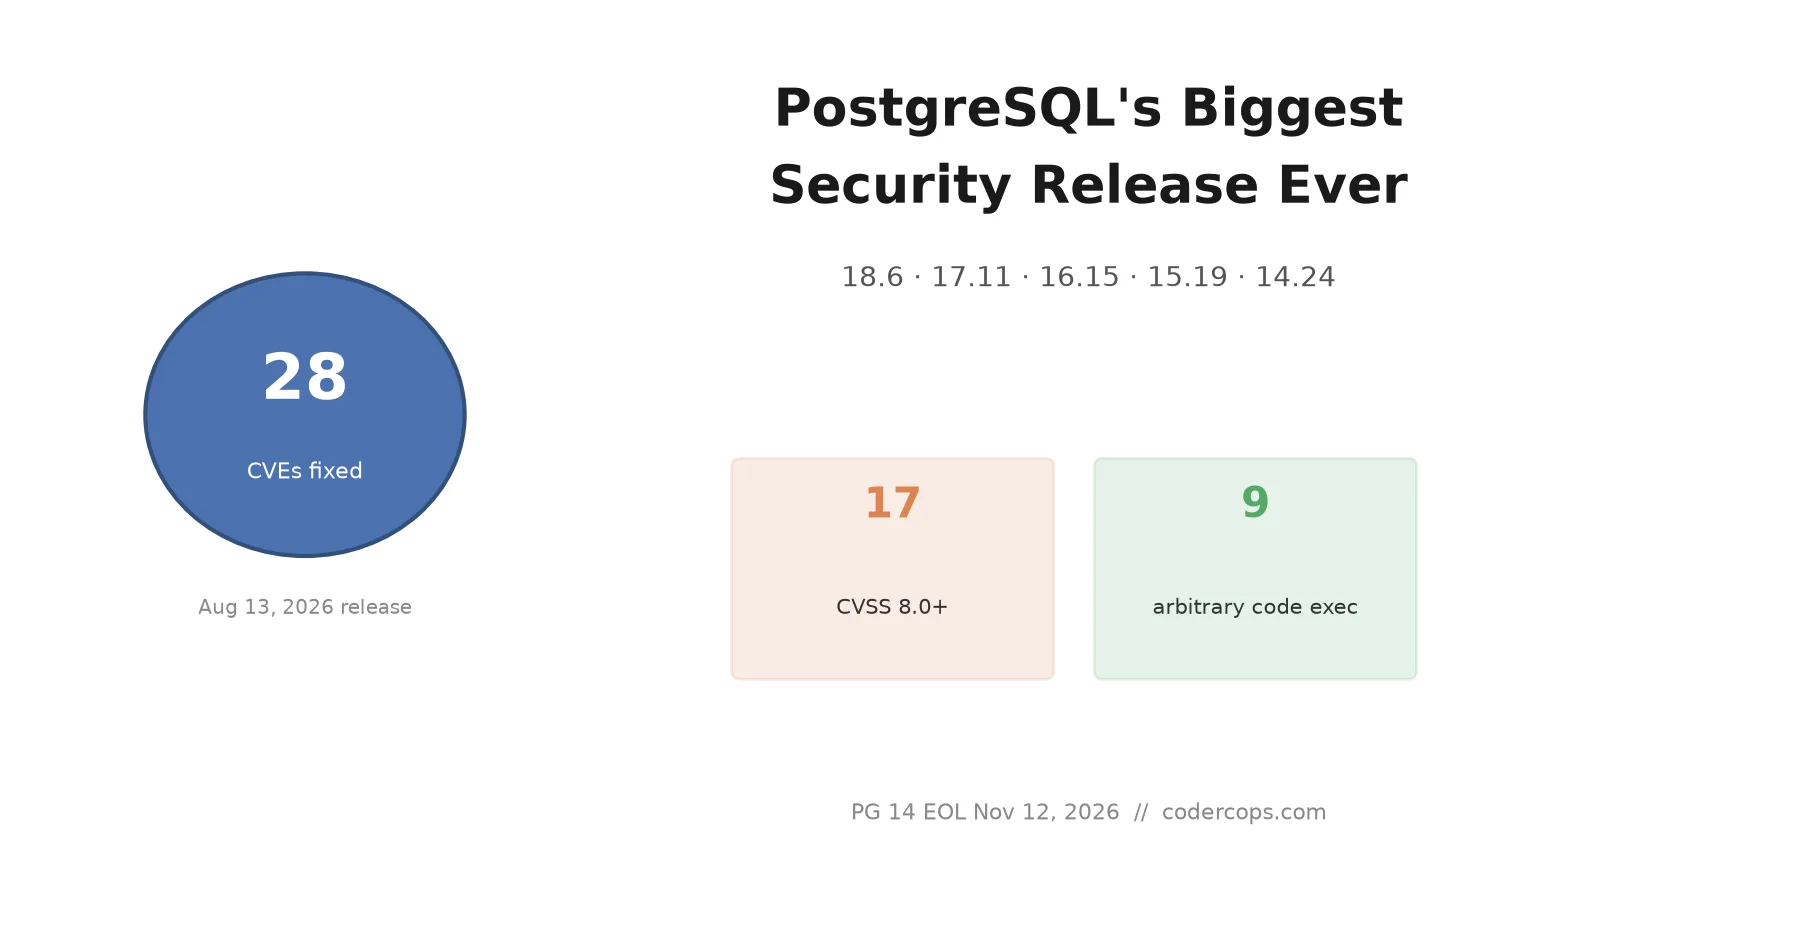
P.09PostgreSQL 18.6, 17.11, 16.15, 15.19, and 14.24 fixed 28 CVEs on August 13, 17 of them CVSS 8.0 or higher. Which matter, and who's actually exposed.
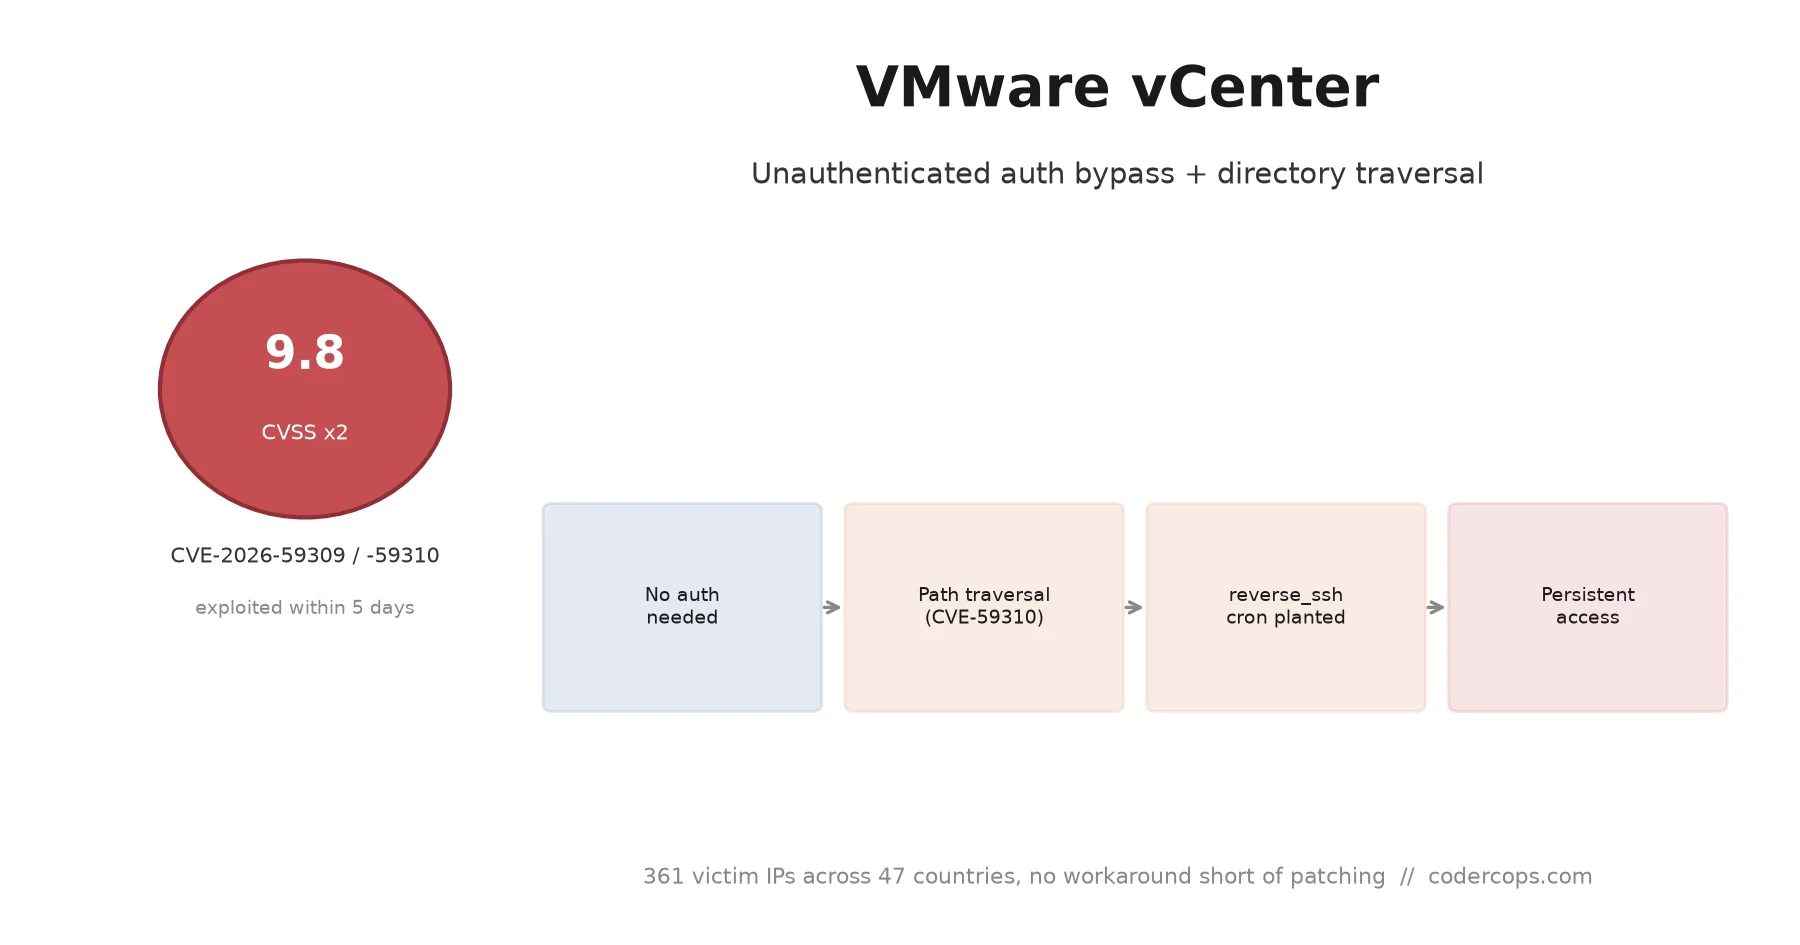
P.10Two critical unauthenticated vCenter flaws let attackers skip login and run code on the management plane. What's affected, and how to check for compromise.
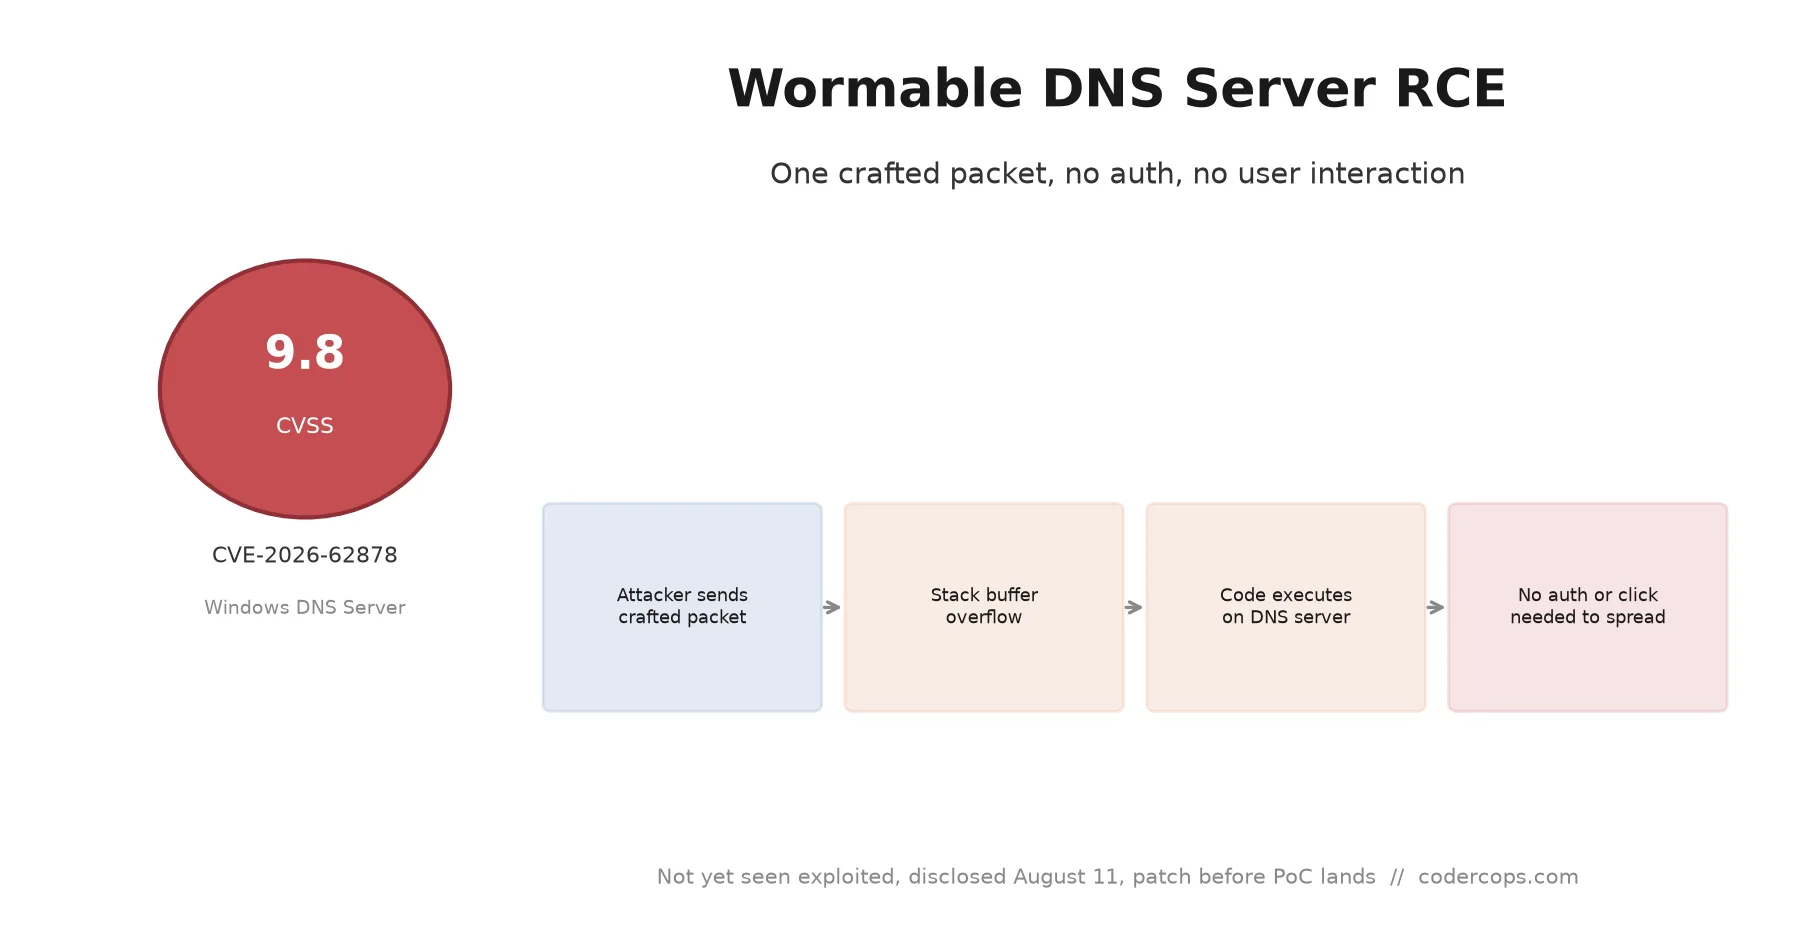
P.11A stack overflow in Windows DNS Server runs code from one crafted packet, no auth, no clicks. Not seen exploited yet, but shaped like a bug that will be.
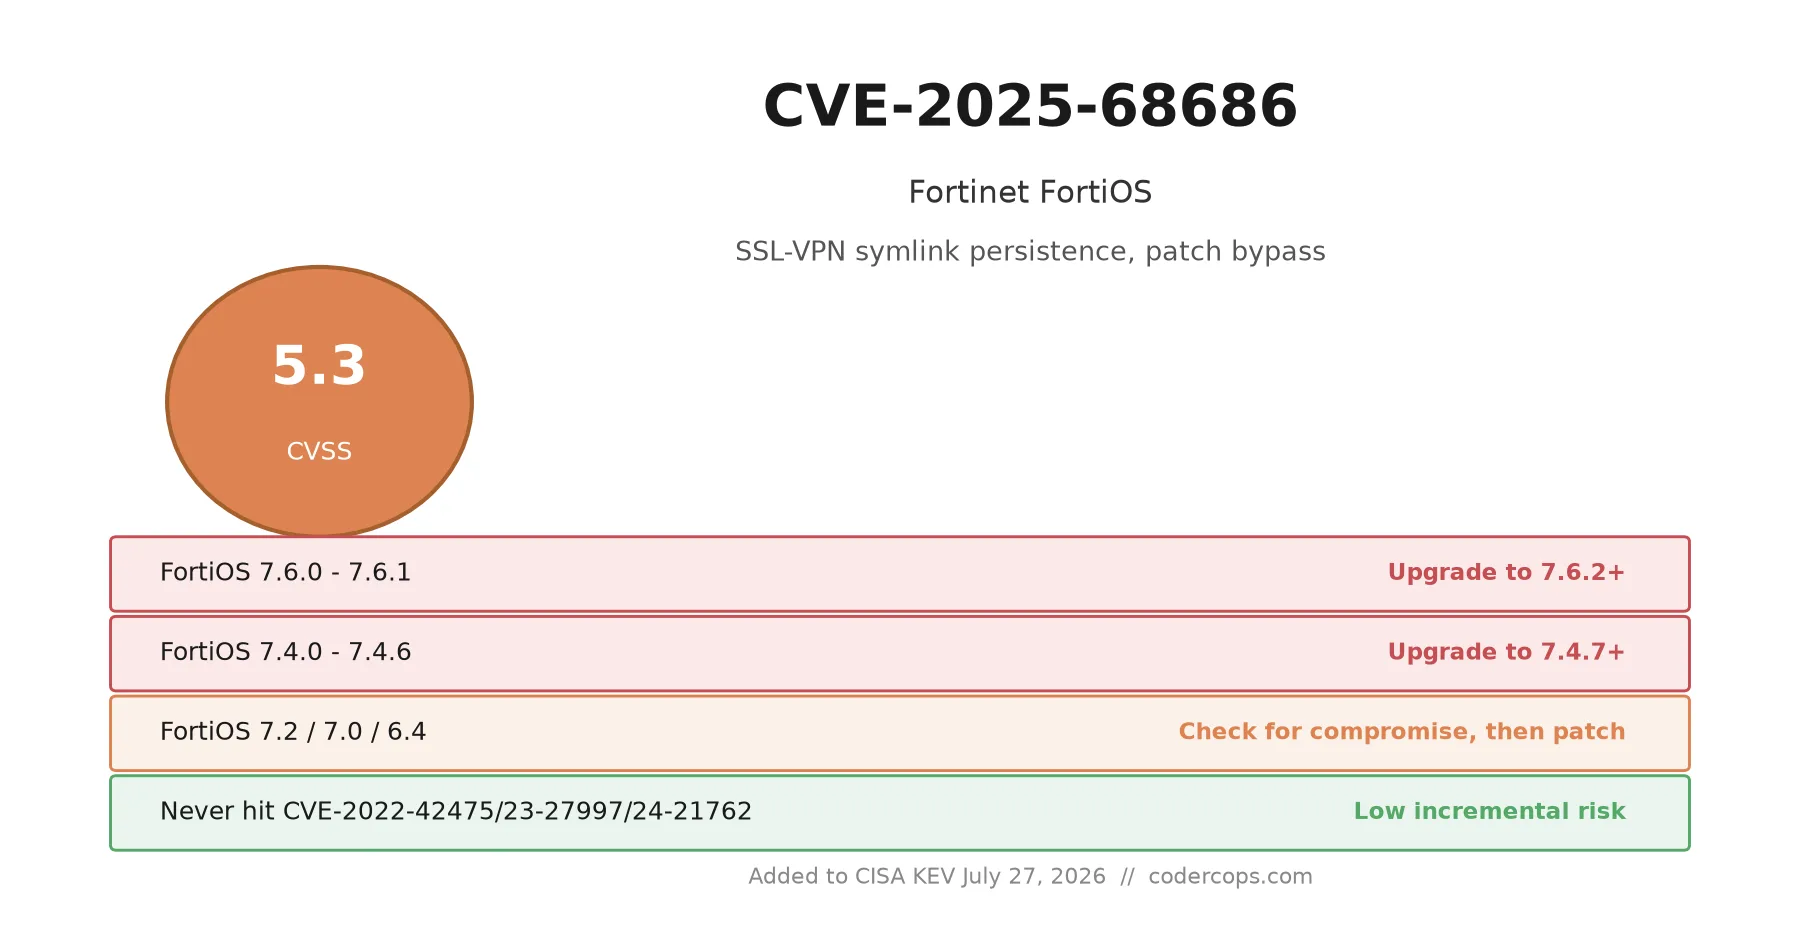
P.12CISA added CVE-2025-68686, a FortiOS SSL-VPN symlink persistence bypass, on July 27. It only bites devices compromised earlier and never forensically cleaned.